
Skip to content
KitploitKITPLOIT
ツールエクスプロイトブログ
Log in
提出
ツールエクスプロイトブログ
提出

ハッキング、侵入テスト、サイバーセキュリティツールをあなたのセキュリティアーセナルに!

Kitploitはハッキング、サイバーセキュリティ、ペネトレーションテストのツールディレクトリです。最新のプロジェクトアップデートを見つけて、脆弱性の発見、システム分析、テストの自動化、セキュリティの強化を行いましょう。

フィードお問い合わせプライバシー© 2026 Kitploit

ツールディレクトリ

カテゴリ

すべてのカテゴリを見る
Loading categories
CVE-2026-11645 — Advisory repository documenting CVE-2026-11645, a Chrome V8 out-of-bounds memory corruption zero-day enabling RCE, with affected versions, detection indicators, and patch guidance. | Kitploit
ツール/GitHubGitHub/ashrafzaryouh/cve-2026-11645
Vulnerability AnalysisWeb SecurityThreat IntelligenceLearning & Education
GitHubashrafzaryouh/cve-2026-11645

CVE-2026-11645

Advisory repository documenting CVE-2026-11645, a Chrome V8 out-of-bounds memory corruption zero-day enabling RCE, with affected versions, detection indicators, and patch guidance.

リポジトリを見る
15ヶ月前未レビュー
共有
要求された言語のコンテンツは利用できません。英語版を表示しています。

🚨 CVE-2026-11645 🚨

🌐 Google Chrome V8 Zero-Day Memory Corruption Vulnerability

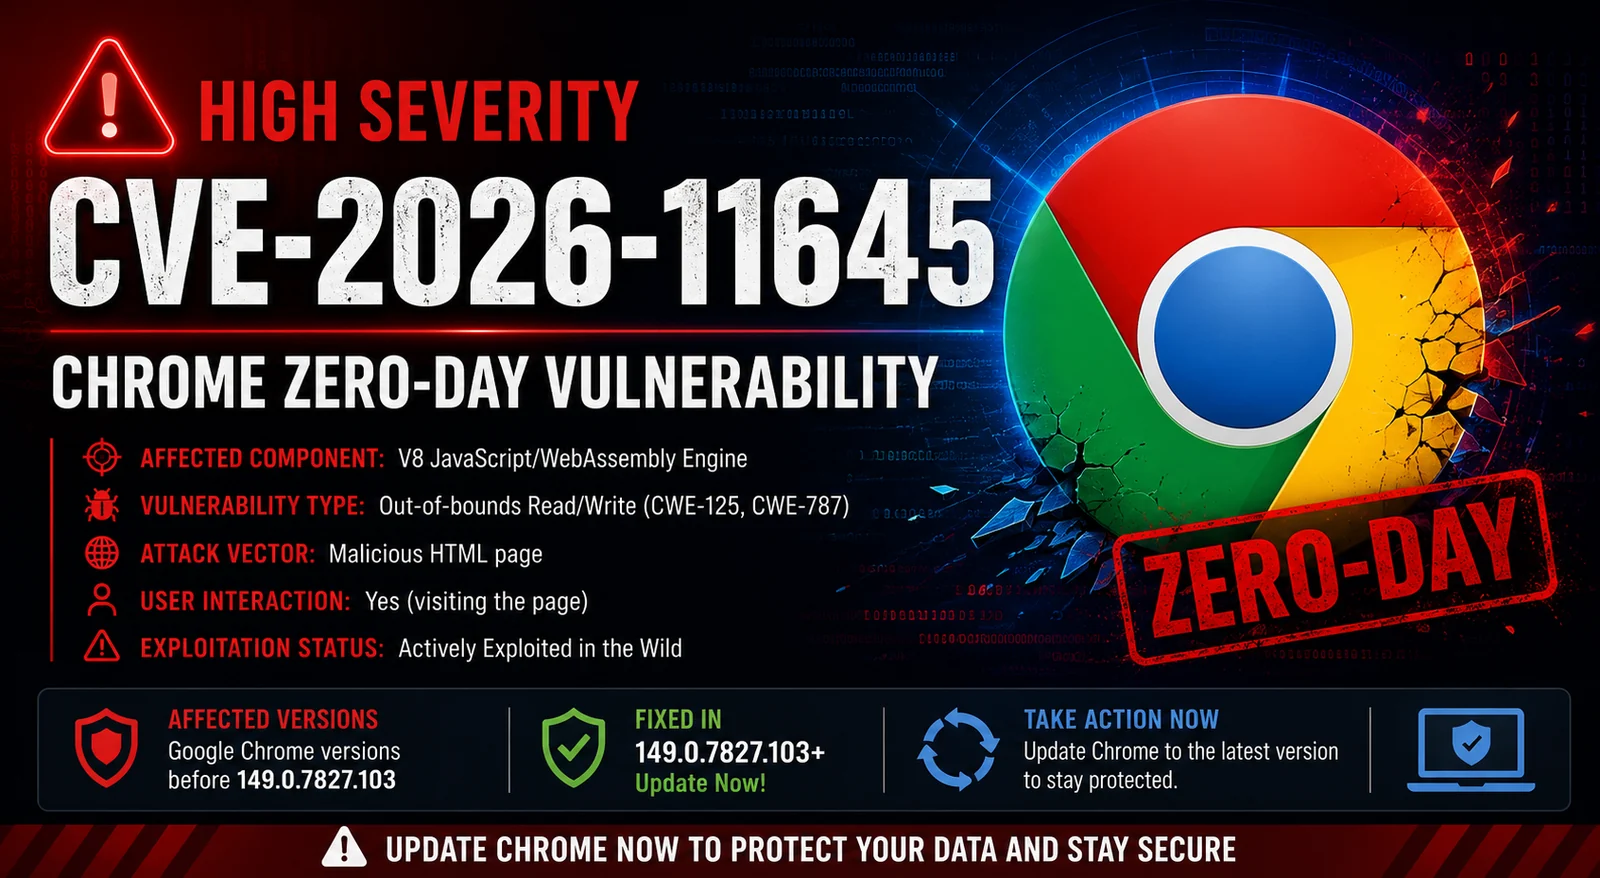
ChatGPT Image Jun 11, 2026, 04_25_47 PM

Severity CVSS Status Chrome

🔥 Actively Exploited Zero-Day

⚡ V8 Engine Memory Corruption

🛡️ Patch Immediately


📖 Overview

⚠️ CVE-2026-11645 is a high-severity zero-day vulnerability affecting the Google Chrome V8 JavaScript engine. The flaw allows attackers to trigger an Out-of-Bounds Read/Write condition that may lead to Remote Code Execution (RCE).


🎯 Vulnerability Information

🏷️ Field📋 Value
CVECVE-2026-11645
🔥 SeverityHigh
📊 CVSS8.8
🏢 VendorGoogle
🌐 ProductChrome
🧩 ComponentV8 Engine
💥 TypeOut-of-Bounds Read/Write
⚠️ ExploitedYes
🎯 ImpactRemote Code Execution

🧠 Technical Summary

The vulnerability exists within Chrome's V8 JavaScript engine.

An attacker can craft a malicious webpage that:

  • 🎯 Triggers memory corruption
  • 📖 Reads unintended memory regions
  • ✍️ Writes outside allocated boundaries
  • 💻 Executes arbitrary code
  • 🔓 Assists exploitation chains
  • 🚨 Causes browser crashes

⚔️ Attack Chain

🌐 Victim Opens Malicious Website
                │
                ▼
📜 Crafted JavaScript Payload
                │
                ▼
🧩 V8 Engine Vulnerability Triggered
                │
                ▼
💥 Out-of-Bounds Memory Access
                │
                ▼
⚡ Remote Code Execution
                │
                ▼
🚨 Browser Compromise

🎯 Affected Versions

❌ Vulnerable

Chrome < 149.0.7827.103
CVE-2026-11645

✅ Fixed

🪟 Windows : 149.0.7827.102+
🍎 macOS   : 149.0.7827.103+
🐧 Linux   : 149.0.7827.102+

💥 Potential Impact

ImpactRisk
⚡ Remote Code Execution🔴 High
🔍 Information Disclosure🔴 High
💣 Browser Crash🟠 Medium
🔗 Exploit Chaining🟠 Medium
🏢 Enterprise Risk🔴 High

🔎 Detection Opportunities

Monitor for:

🚨 Indicators:
  - Unexpected browser crashes
  - Suspicious JavaScript activity
  - Exploit-kit traffic
  - Malicious domain visits
  - Unusual Chrome child processes
  - Browser memory anomalies

🛡️ Mitigation

🚀 Immediate Actions

chrome://settings/help

✅ Recommendations

  • 🔄 Update Chrome immediately
  • 🛡️ Enable automatic updates
  • 🔒 Restrict untrusted extensions
  • 📡 Monitor browser telemetry
  • 🚨 Review EDR alerts
  • 📊 Track threat intelligence feeds

📈 Risk Assessment

Likelihood  : ██████████  HIGH
Impact      : ██████████  HIGH
Overall     : 🚨 CRITICAL 🚨

📚 References

  • 🌐 Google Chrome Security Advisory
  • 🏛️ NIST National Vulnerability Database
  • 🔬 Chromium Security Updates

⚠️ Disclaimer

This repository is provided for:

  • 🎓 Security Education
  • 🔍 Vulnerability Research
  • 🛡️ Defensive Security
  • 📊 Patch Management

❌ No exploit code is included.


⭐ Stay Updated • Patch Early • Hunt Smart ⭐

🚀 Cyber Threat Intelligence Repository 🚀

ツールをダウンロード

人気

すべて見る →

コミュニティで最も使われているツールを見つけましょう。

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 究極のOSINTツールキット:調査グラフ、信頼度スコアリング、エイリアスファミリー、マップ、タイムライン、レポート。49個のモジュール、400以上のサイト、APIキー不要。

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock ワンタップ実行アプリ(CVE-2026-43499)

    628
  • 3

    looking-glass

    anonghosty/looking-glass

    ShadowserverレポートをMongoDBに取り込み、インタラクティブなマップ、分析、調査結果、アドバイザリ、エグゼクティブダッシュボードとして再生するCSIRTプラットフォーム。

    413
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServerは、オープンソースの特権アクセス管理(PAM)プラットフォームであり、DevOps および IT チームに対し、Webブラウザを介してSSH、RDP、Kubernetes、データベース、RemoteAppエンドポイントへのオンデマンドで安全なアクセスを提供します。

    366
  • 5

    ARTEX

    baarai/artex

    プランナー/ワーカーエージェント、資産グラフと探索グラフ、MITMトラフィック記録、脆弱性の再テストを備えたLLMマルチエージェント自律ペネトレーションテストプラットフォーム。

    329
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    ウェブ全体で7,700以上のソーシャルメディア上の身元を発見・マッピングするAI搭載OSINTエンジン

    287

すべてのツールを探索

ツールコレクションを閲覧

すべてのツールを見る →