
 #1
ブルーチーム、防御的セキュリティ、脅威保護のためのツール。
Kitploit おすすめ

 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 azure/azure-sentinel
企業全体のインテリジェントなセキュリティ分析のためのクラウドネイティブSIEM。
 beenuar/aisoc
Self-hostable AI SOC that fuses security alerts, auto-triages via agentic AI, runs MITRE ATT&CK investigations, and logs every agent decision in a…
 anthropics/oss-scanner
登録されたオープンソースリポジトリを分離されたオフラインVMでビルドし、セキュリティ脆弱性をスキャンして、再現手順と提案されたパッチを含む検出結果をメールで通知するサービス。
 bekkaze/abusebox
Self-hosted mail server monitoring: checks 24 DNS blacklists, AbuseIPDB reputation, SSL and domain expiry, SPF/DKIM/DMARC grades and uptime, with…
 shuffle/shuffle
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Linuxカーネルゼロデイ攻撃に対するゼロダウンタイム防御のケーススタディ。自動化CLIとデュアルウィットネス公証フレームワークについては、mc493/kshieldを参照してください。
 agentrust-io/cmcp
cMCP: 機密MCPゲートウェイ。MCPツール呼び出しに対するハードウェア認証によるポリシー強制。
 hotcakex/harden-windows-security
Windowsを公式サポートされたMicrosoftの手法を用いて安全かつ確実に堅牢化 | 常に最新版のWindowsに対応 | 個人、企業、政府、軍事レベルのセキュリティ向けツールとガイドを提供 | 安全な開発・ビルドプロセスに対応したSLSA Level 3準拠 | MS…
 matijamiki/ranwhat
Audit log and secret scanner for AI coding agents: see what Claude Code, Codex, Gemini CLI and 27 more ran on your machine, and find API keys leaked…
 xalgorix/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…

 daveyd347/secrets-scanner
ソースコードとgit履歴から漏洩したAPIキー、トークン、秘密鍵を検出する依存関係不要のシークレットスキャナー。出力は秘匿化され、GitLab CIジョブとしてそのまま組み込めます。
 qubesos/qubes-core-admin
Python管理APIを介してQubes OSドメインのコアライフサイクルを管理し、Xenによる安全なコンパートメント化を処理するとともに、自動化のためのイベントシステムを公開します。
 cisagov/kev-data
CISAのKnown Exploited Vulnerabilities(KEV)カタログをCSVおよびJSON(JSONスキーマ付き)としてミラーリングし、KEV更新へのプログラムによるアクセスとコミット履歴の追跡を可能にします。
 nzymeorg/nzyme
WiFi、Bluetooth、Ethernetの脅威検出。
 lolbas-project/lolbas
ローカル環境に存在するバイナリとスクリプト - (LOLBins および LOLScripts)
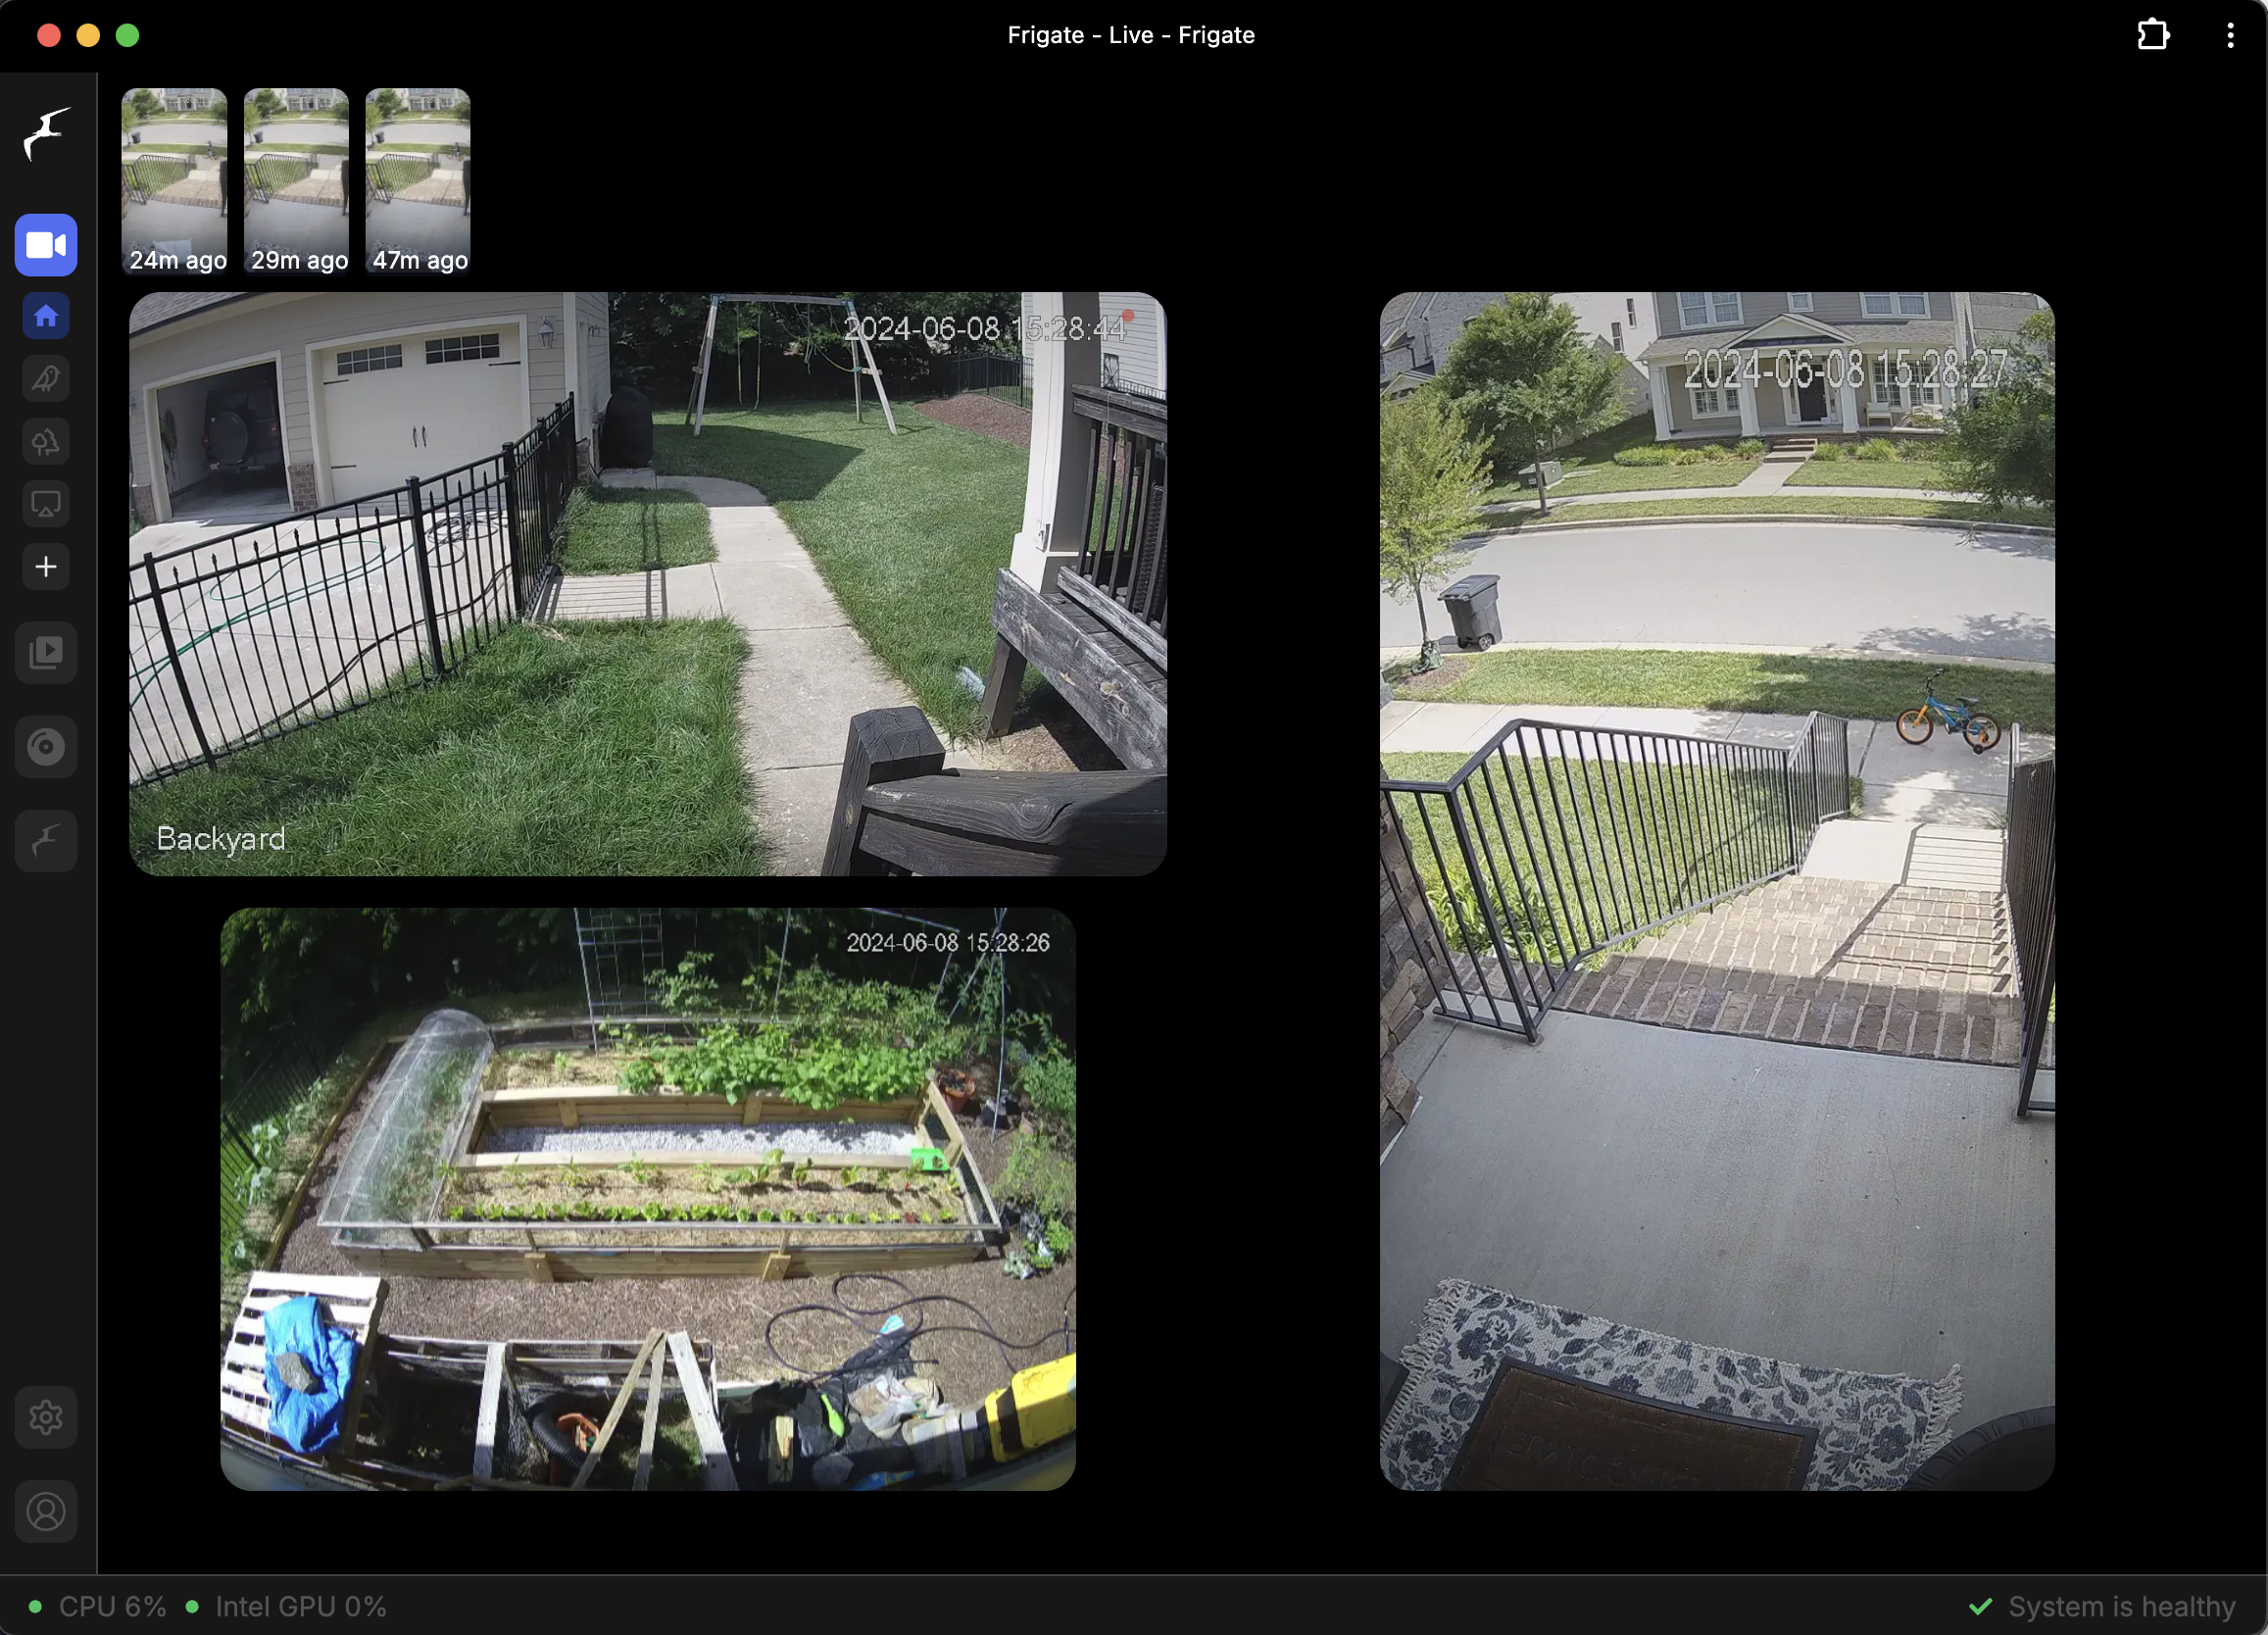 blakeblackshear/frigate
IPカメラ向けリアルタイムローカル物体検出を備えたNVR








