 tylous/sourcepoint
Cobalt Strike के लिए Polymorphic C2 प्रोफ़ाइल जनरेटर जो HTTP, DNS और process injection के लिए यादृच्छिक विकल्पों के साथ evasive बीकन कॉन्फ़िगरेशन के निर्माण को स्वचालित करता है ताकि detection को कम किया जा सके।

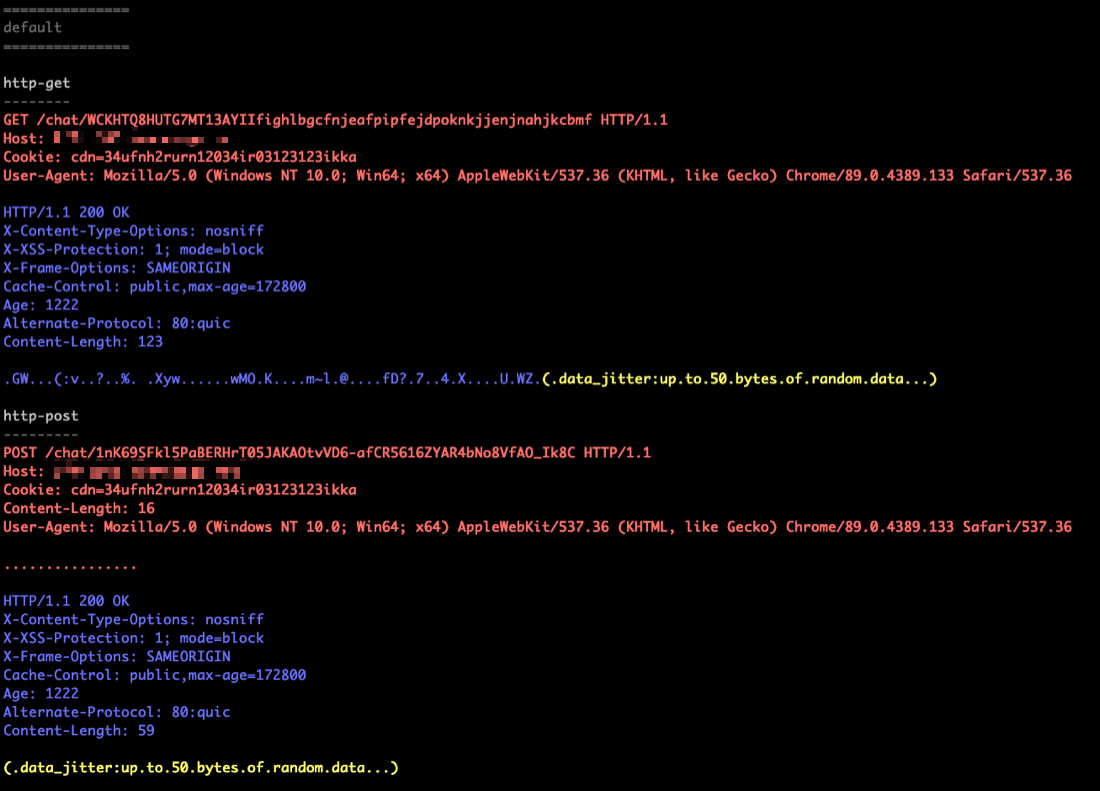
SourcePoint, Cobalt Strike C2 के लिए एक पॉलीमॉर्फिक C2 प्रोफ़ाइल जनरेटर है, जो Go में लिखा गया है। SourcePoint उड़ान भरते समय अद्वितीय C2 प्रोफ़ाइल उत्पन्न करने की अनुमति देता है जो हमारे Indicators of Compromise ("IoCs") को कम करने में मदद करता है और ऑपरेटर को न्यूनतम प्रयास के साथ जटिल प्रोफ़ाइल बनाने की अनुमति देता है। यह Articles के साथ-साथ Patch Notes की व्यापक समीक्षा करके प्रमुख कार्यों और संशोधन योग्य विशेषताओं की पहचान करके किया गया था। SourcePoint को इस मुद्दे को संबोधित करने के इरादे से डिज़ाइन किया गया था कि हमारी C2 गतिविधि को पता लगाना कैसे कठिन बनाया जाए, जिसमें दुर्भावनापूर्ण IoCs से संदिग्ध IoCs की ओर बढ़ने पर ध्यान केंद्रित किया गया। यहाँ लक्ष्य यह है कि यदि हमारे IoCs प्रकृति में दुर्भावनापूर्ण नहीं हैं तो हमारी C2 का पता लगाना कठिन होता है और संदिग्ध प्रकृति की खोज के लिए अतिरिक्त शोध की आवश्यकता होती है। SourcePoint में आपकी प्रोफ़ाइल को संशोधित करने के लिए चुनने के लिए कई अलग-अलग कॉन्फ़िगर करने योग्य विकल्प हैं (अधिकांश मामलों में यदि खाली छोड़ दिया जाए तो SourcePoint आपके लिए उन्हें बेतरतीब ढंग से चुन लेगा)। उत्पन्न प्रोफ़ाइल आपकी C2 के सभी पहलुओं को संशोधित करती हैं। इस परियोजना का लक्ष्य न केवल पहचान-आधारित नियंत्रणों को दरकिनार करने में सहायता करना है बल्कि C2 ट्रैफ़िक और गतिविधि को पर्यावरण में मिलाने में भी मदद करना है, जिससे उक्त गतिविधि का पता लगाना कठिन हो जाता है।
go install github.com/Tylous/SourcePoint
$go get gopkg.in/yaml.v2

$go build SourcePoint.go
#./SourcePoint -h

	   _____                            ____        _       __
	  / ___/____  __  _______________  / __ \____  (_)___  / /_
	  \__ \/ __ \/ / / / ___/ ___/ _ \/ /_/ / __ \/ / __ \/ __/
	 ___/ / /_/ / /_/ / /  / /__/  __/ ____/ /_/ / / / / / /_
	/____/\____/\__,_/_/   \___/\___/_/    \____/_/_/ /_/\__/
  							(@Tyl0us)


Usage of ./SourcePoint:
  -Allocation string
        Minimum amount of memory to request for injected content (must be higher than 4096)
  -BeaconGate string
        Specify beacon gate options (All, Comms, Core, Cleanup) or specific APIs
  -CDN string
        CDN cookie name (typically used for AzureEdge profiles)
  -CDN-Value string
        CDN cookie value (typically used for AzureEdge profiles)
  -Customuri string
        The base URI for custom HTTP GET/POST profile - Cannot be used with CustomuriGET or CustomuriPOST
  -CustomuriGET string
        The base URI for custom HTTP GET profile - Must be used with CustomuriPOST
  -CustomuriPOST string
        The base URI for custom HTTP POST profile - Must be used with CustomuriGET
  -Datajitter string
        Appends a value to HTTP-Get and HTTP-Post server output (default "50")
  -Forwarder
        Enabled the X-forwarded-For header (Good for when your C2 is behind a redirector)
  -Host string
        Team server domain name
  -Httplib string
        Select the default HTTP Beacon library:
        [*] wininet
        [*] winhttp' (default "winhttp")
  -Injector string
        Select the preferred method to allocate memory in the remote process:
        [*] VirtualAllocEx (Great for cross architecture i.e x86 -> x64 and x64->x86)
        [*] NtMapViewOfSection (A more stealthly option, however fails over to VirtualAllocEx, generating more events when it does)
  -Jitter string
        Jitter percentage for beacon call home
  -Keylogger string
        Select the preferred method the beacon will use to log keystrokes:
        [*] GetAsyncKeyState (Uses GetAsyncKeyState API (Separate DLL for x86/x64 process))
        [*] SetWindowsHookEx (Uses SetWindowsHookEx API)
  -Keystore string
        SSL keystore name
  -Metadata string
        Specifies how to transform and embed metadata into the HTTP request:
        [*] base64
        [*] base64url
        [*] netbios
        [*] netbiosu (default "base64url")
  -Outfile string
        Name of output file
  -PE_Clone string
        PE file beacon will mimic (Use the number):
        [1] ActivationManager.dll
        [2] audioeng.dll
        [3] AzureSettingSyncProvider.dll
        [4] BingMaps.dll
        [5] DIAGCPL.dll
        [6] EDGEHTML.dll
        [7] FILEMGMT.dll
        [8] FIREWALLCONTROLPANEL.dll
        [9] GPSVC.dll
        [10] gpupvdev.dll
        [11] libcrypto.dll
        [12] srvcli.dll
        [13] srvsvc.dll
        [14] Windows.Storage.Search.dll
        [15] Windows.System.Diagnostics.dll
        [16] Windows.System.Launcher.dll
        [17] Windows.System.SystemManagement.dll
        [18] Windows.UI.BioFeedback.dll
        [19] Windows.UI.BlockedShutdown.dll
        [20] Windows.UI.Core.TextInput.DLL
        [21] winsqlite3.dll
        [22] WMNetMgr.DLL
        [23] wwanapi.dll
        [24] WWANSVC.DLL
        [25] wow64win.dll
        [26] wow64.dll
        [27] ctiuser.dll (Carbon Black's DLL)
        [28] InProcessClient.dll (SentinelOne's DLL)
        [29] umppc.dll (CrowdStrike's DLL)
        [30] CyMemDef64.dll (Cylance's DLL)
  -Password string
        SSL certificate password
  -PostEX_Name string
        File Post-Ex activities will spawn and inject into (Use the number):
        [1] WerFault.exe
        [2] WWAHost.exe
        [3] choice.exe
        [4] bootcfg.exe
        [5] w32tm.exe
        [6] expand.exe
        [7] fsutil.exe
        [8] gpupdate.exe
        [9] gpresult.exe
        [10] logman.exe
        [11] mcbuilder.exe
        [12] mtstocom.exe
        [13] pcaui.exe
        [14] powercfg.exe
        [15] svchost.exe
  -Profile string
        HTTP GET/POST profile (Use the number):
        [1] Windowsupdate
        [2] Slack
        [3] Gotomeeting
        [4] Outlook.Live
        [5] Safebrowsing [Cloudfront Compatible]
        [6] AzureEdge [AzureEdge Compatible]
        [7] Field-Keyword [Cloudfront Compatible]
        [8] Custom (Used with ProfilePath)
  -ProfilePath string
        Path of custom HTTP GET/POST profile...
  -Sleep string
        Initial beacon sleep time
  -Stage string
        Disable host staging (Default: False) (default "false")
  -Syscall string
        Defines the ability to use direct/indirect system calls instead of the standard Windows API functions calls:
        [*] None
        [*] Direct
        [*] Indirect (default "None")
  -TasksDnsProxyMaxSize string
        The maximum size (in bytes) of proxy data to transfer via the DNS communication channel at a check in
  -TasksMaxSize string
        The maximum size (in bytes) of task(s) and proxy data that can be transferred through a communication channel at a check in
  -TasksProxyMaxSize string
        The maximum size (in bytes) of proxy data to transfer via the communication channel at a check in
  -ThreadSpoof
        Sets post-ex DLLs to spawn threads with a spoofed start address. These are generated randomly (default true)
  -RdllUseDriploading
        Enable driploading for RDLL stage (gradually loads beacon in smaller chunks to evade memory scanners) (default true)
  -RdllDriploadDelay string
        Delay in milliseconds between loading chunks for RDLL driploading (default: random 100-200ms)
  -UseDriploading
        Enable driploading for process injection (gradually writes payload in smaller chunks to evade EDR) (default true)
  -DriploadDelay string
        Delay in milliseconds between writing chunks for process injection driploading (default: random 100-200ms)
  -CopyPEHeader
        Copy PE Header to match cloned DLL characteristics (default false)
  -EafBypass
        Enable Export Address Filtering (EAF) bypass (default false)
  -RdllLoader string
        Rdll Loader Options:
        [*] PrependLoader (default)
        [*] StompLoader (Older method)
  -RdllUseSyscalls
        Use Syscalls for Rdll operations (default false)
  -SmartInject
