
टीमों के लिए एक आधुनिक git-आधारित age-एन्क्रिप्टेड सीक्रेट्स मैनेजर।
<p align="center">
<picture>
<source media="(prefers-color-scheme: dark)" srcset="https://s13.gifyu.com/images/b7mxd.webp">
<source media="(prefers-color-scheme: light)" srcset="https://s13.gifyu.com/images/b7mxl.webp">
<img alt="The cottage logo" width="600" src="https://assets.kitploit.com/production/public/readmes/7490/2c8e4c6f8fa352cb9dcf2d8f22c3d84926c09a69fca9a6632d008c61b5417c28.webp">
</picture>
</p>
[](https://github.com/sayanarijit/cottage/actions/workflows/cottage-verify.yml)
[](https://crates.io/crates/cottage)
[](https://pypi.org/project/cottage/)
[](https://www.npmjs.com/package/@sayanarijit/cottage)
[](https://hub.docker.com/r/sayanarijit/cottage)
**cott*age*** टीमों के लिए एक GitOps टूल है जो git रिपॉज़िटरी में [age-encrypted](https://age-encryption.org/) secrets को प्रबंधित करता है।
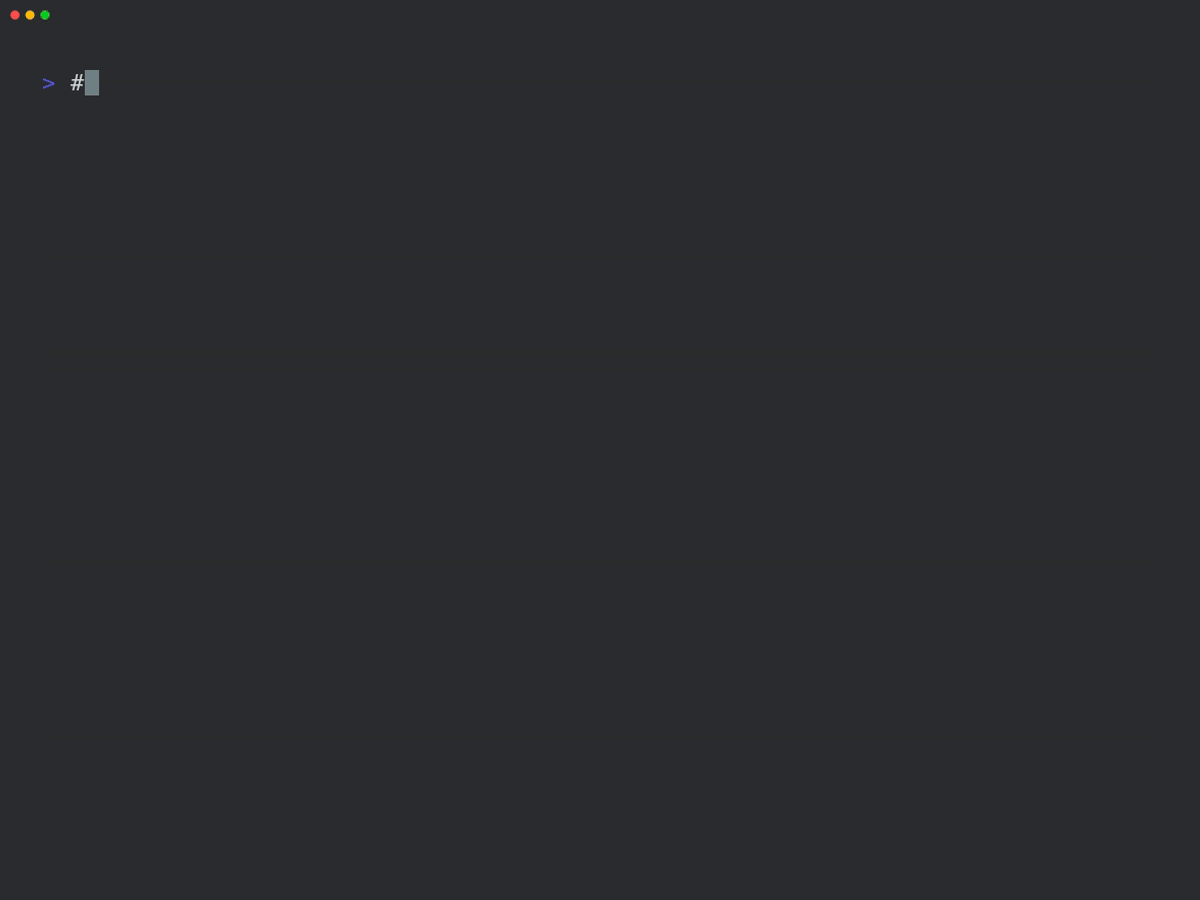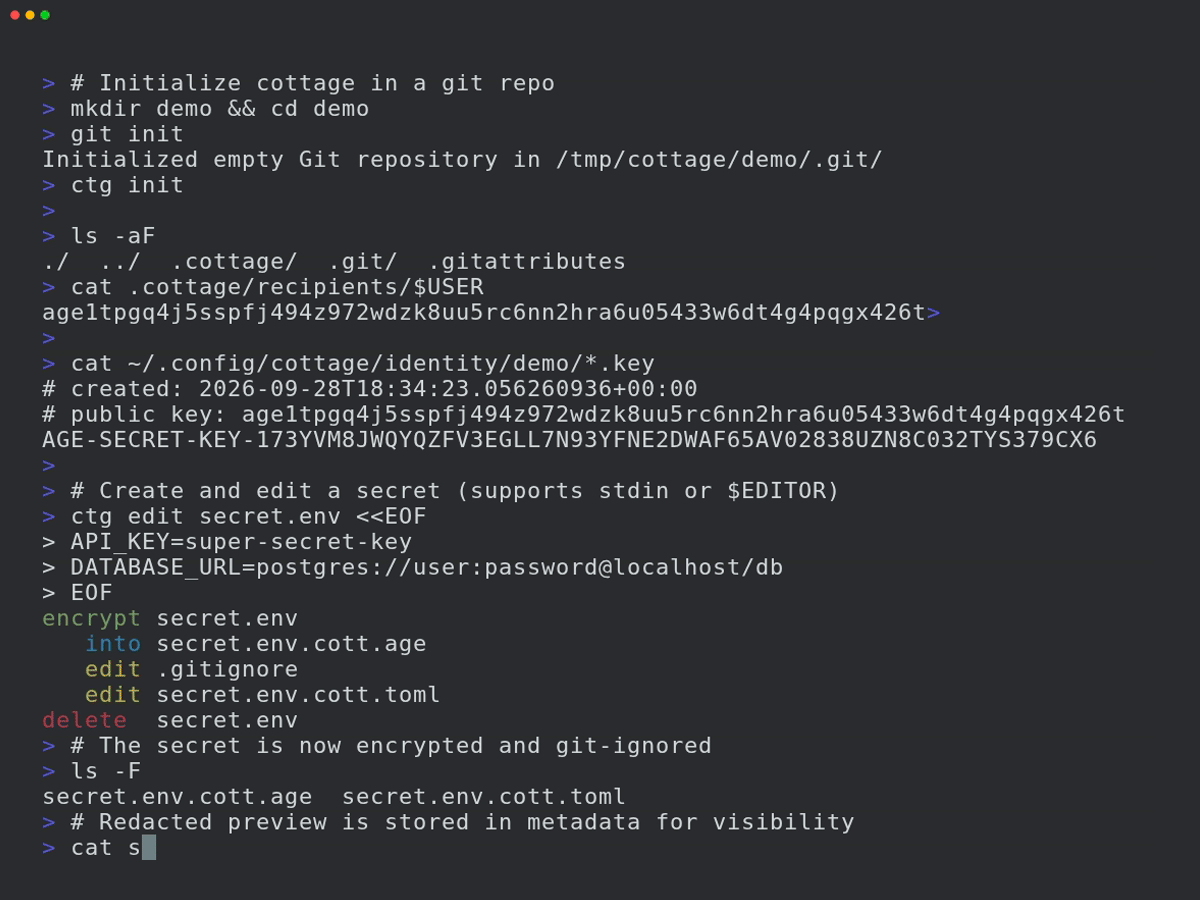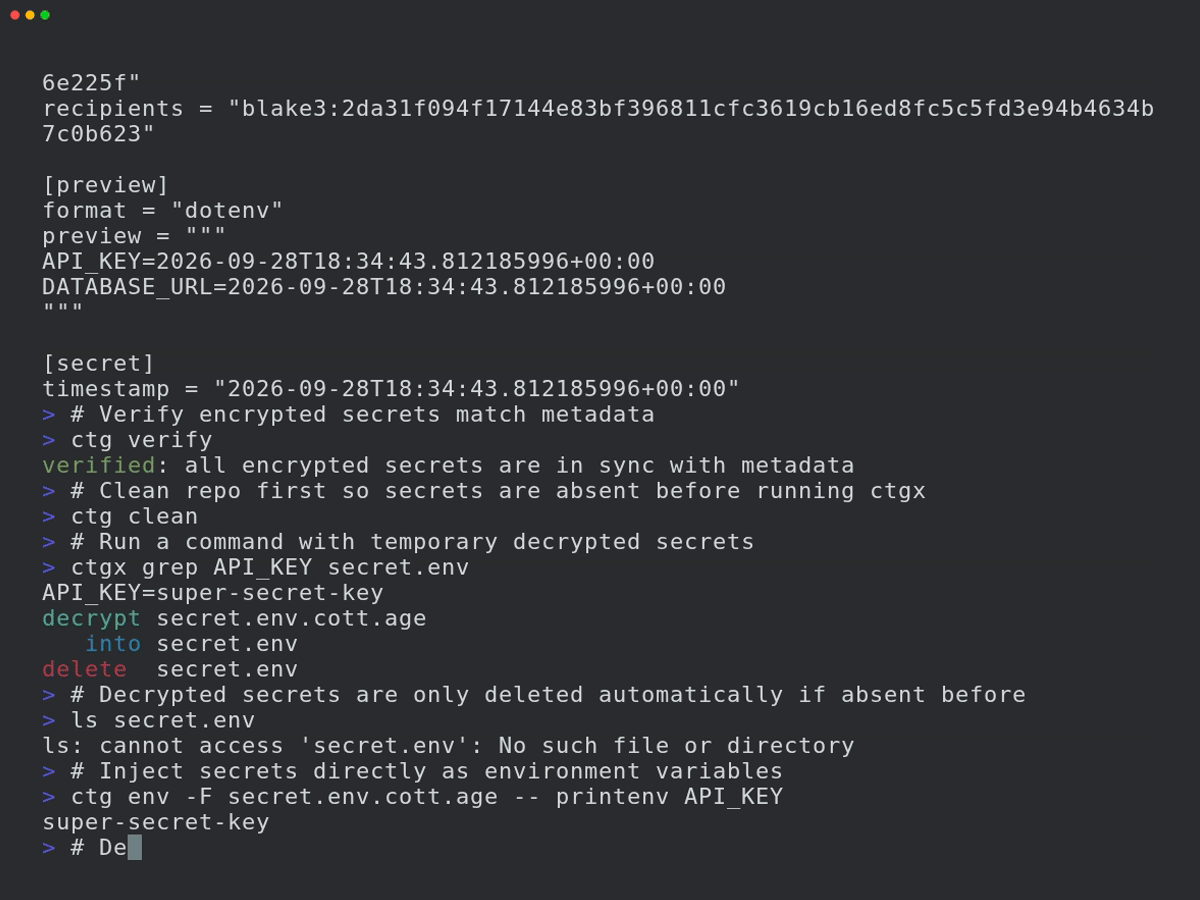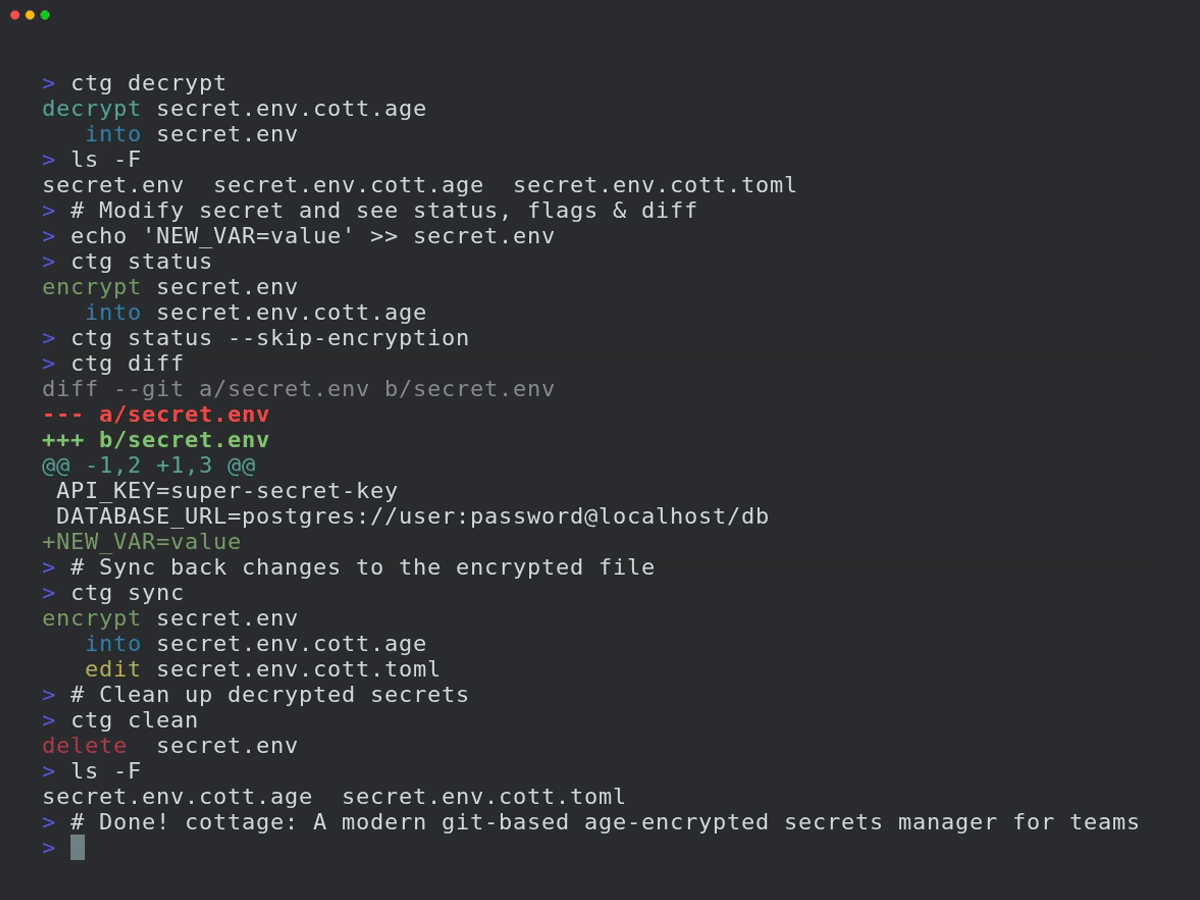
यह secrets को encrypt/decrypt करने, recipients को प्रबंधित करने, और secrets को रिपॉज़िटरी से बाहर रखने के लिए एक सरल workflow प्रदान करता है, साथ ही VCS के माध्यम से आसान शेयरिंग की सुविधा देता है। cottage बेहतर visibility के लिए encrypted secrets के redacted previews भी generate करता है और persistent तथा temporary decryption workflows दोनों का समर्थन करता है, जबकि यह सुनिश्चित करता है कि secrets कभी plaintext में commit न हों।
1. [Features](#features)
2. [Installation](#installation)
3. [Editor Integrations](#editor-integrations)
1. [VS Code Extension](#vs-code-extension)
2. [Cursor and Eclipse Extension](#cursor-and-eclipse-extension)
3. [Vim Plugin](#vim-plugin)
4. [AI Agent Integrations](#ai-agent-integrations)
1. [Claude Code Integration](#claude-code-integration)
2. [GitHub Copilot Integration](#github-copilot-integration)
3. [Codex Integration](#codex-integration)
4. [Antigravity (agy) Integration](https://github.com/sayanarijit/cottage/blob/main/%3C#antigravity-(agy)-integration>)
5. [Cursor Integration](#cursor-integration)
5. [Quick Start](#quick-start)
6. [GitOps](#gitops)
7. [Git Hooks](#git-hooks)
8. [Access Control](#access-control)
1. [Rules](#rules)
2. [Verification](#verification)
9. [Any Provider as Upstream](#any-provider-as-upstream)
1. [Example plugins](#example-plugins)
10. [Sync with any device](#sync-with-any-device)
11. [Learn More](#learn-more)
12. [Troubleshooting](#troubleshooting)
13. [Comparison](#comparison)
1. [age vs Other Encryption](#age-vs-other-encryption)
2. [cottage vs SOPS](#cottage-vs-sops)
3. [cottage vs dotenvx](#cottage-vs-dotenvx)
4. [cottage vs agebox](#cottage-vs-agebox)
## Features
- **Exposure-safe**: Rust के type system का उपयोग करता है ताकि bugs कभी गलती से secrets को expose न कर सकें।
- **Team-friendly**: रिपॉज़िटरी में public keys (recipients) साझा करें, private keys (identities) local रखें।
- **Access Control**: सरल allow/deny नियम यह नियंत्रित करने के लिए कि कौन से secrets किन recipients के लिए encrypt किए जाएँ।
- **Manages .gitignore**: unencrypted secrets को रिपॉज़िटरी से बाहर रखने के लिए `.gitignore` को स्वचालित रूप से अपडेट करता है।
- **Previews**: बेहतर visibility के लिए encrypted secrets के timestamped redacted previews generate करता है।
- **Rich diffs**: git diff को साफ़ और reviewable रखता है, जबकि `ctg diff` locally modified secrets का tracked encrypted counterparts के साथ diff दिखाता है।
- **Checksum verification**: यह सत्यापित करके tampering रोकता है कि encrypted secrets और recipient lists metadata से मेल खाते हैं।
- **Git hooks**: commit से पहले secrets को स्वचालित रूप से check/encrypt करने और checkout के बाद decrypt करने के लिए git hooks आसानी से सेट करें।
- **Persistent secrets workflow**: `ctg decrypt/sync` decrypted secrets को disk पर रखता है।
- **Smart cleanup lifecycle**: `ctg run` (shortcut `ctgx`) और `ctg edit` operation से पहले secrets decrypt करते हैं, यदि वे पहले से मौजूद थे तो उन्हें disk पर रखते हैं या यदि नहीं थे तो बाद में स्वचालित रूप से साफ़ कर देते हैं।
- **Clean on completion**: `ctg encrypt --clean`, `ctg run --clean`, और `ctg edit --clean` यह सुनिश्चित करते हैं कि decrypted files disk से साफ़ हो जाएँ, भले ही वे पहले मौजूद थीं।
- **Environment injection workflow**: `ctg env` decrypted secrets को environment variables के रूप में inject करके command चलाता है, बिना उन्हें disk पर लिखे।
- **Secure secret piping**: `ctg cat PATH` memory में decrypt करता है और stdout पर print करता है ताकि सीधे अन्य tools को stdin piping की जा सके।
- **Clean up**: `ctg clean` local repo से सभी decrypted secrets हटा देता है ताकि आप अपने AI agents को थोड़ी कम चिंता के साथ चला सकें।
- **Supports jj and non-git directories**: `ctg init` किसी भी directory को secret store में बदल देता है।
- **Sync with any provider**: आप किसी भी API वाले provider को upstream के रूप में configure कर सकते हैं, और `git pull/diff/push` की तरह `ctg pull/diff/push` का उपयोग शुरू कर सकते हैं।
- **Sync with any device**: cottage से encrypted और git repo में प्रबंधित secrets को [Cottage Sync](https://cottage-sync.github.io) के साथ devices के बीच sync किया जा सकता है।
## Installation
```bash
# rust: cargo-binstall/cargo
cargo binstall --locked cottage
cargo install --locked cottage
# python: pip/uv/uvx
pip install cottage
uv pip install cottage
uvx --from cottage ctg --version
# node: yarn/pnpm/npx
yarn global add @sayanarijit/cottage
pnpm add -g @sayanarijit/cottage
npx -p @sayanarijit/cottage ctg --version
```
Docker images के रूप में भी उपलब्ध है:
```bash
# Docker
docker run --rm -v $PWD:/app sayanarijit/cottage --version
# Podman
podman run --rm -v $PWD:/app quay.io/sayanarijit/cottage --version
```
या [GitHub](https://github.com/sayanarijit/cottage/releases) से नवीनतम release डाउनलोड करें।
## Editor Integrations
### VS Code Extension
`ctg` install करने, Copilot safety hooks जोड़ने, Explorer से files encrypt करने, और editor workflow के माध्यम से `.cott.age` files खोलने के लिए [Cottage VS Code extension](https://github.com/sayanarijit/vscode-plugin-cottage) का उपयोग करें।
[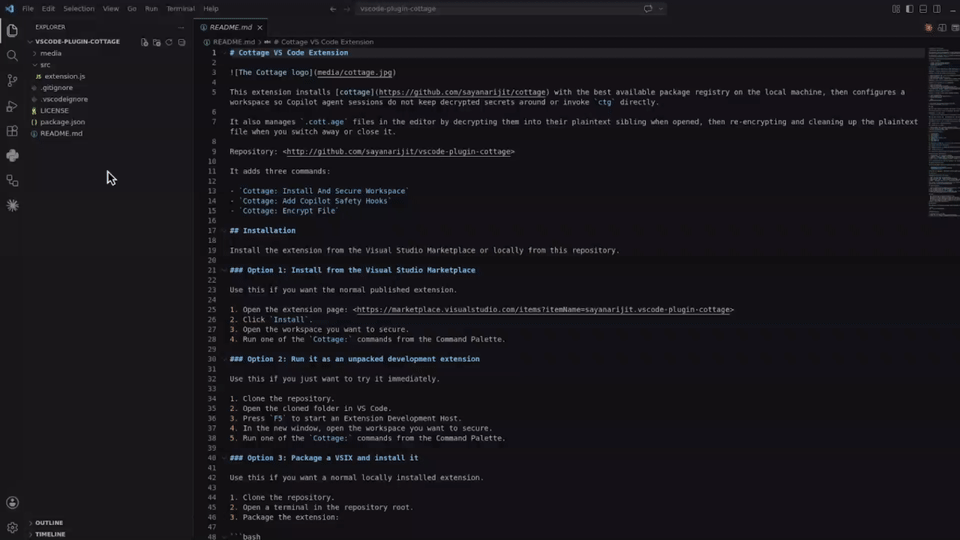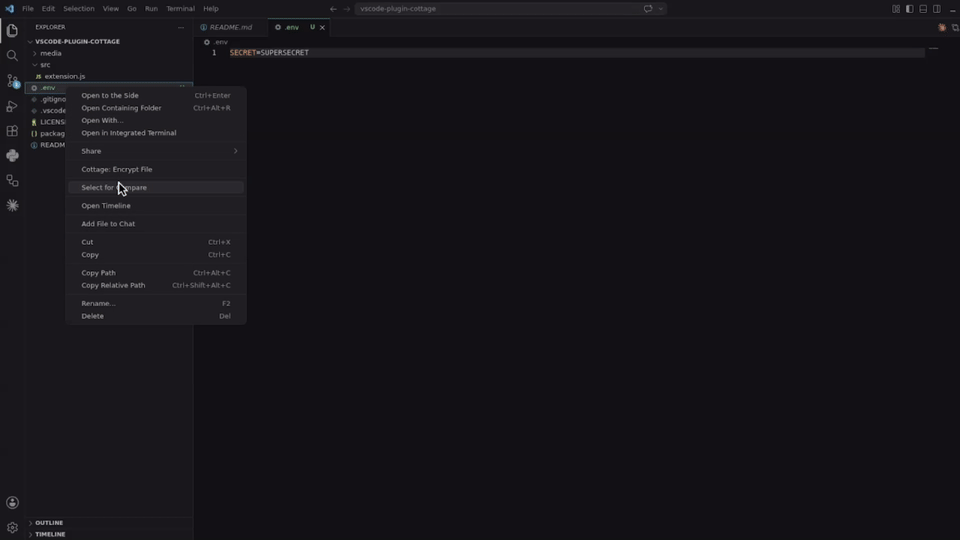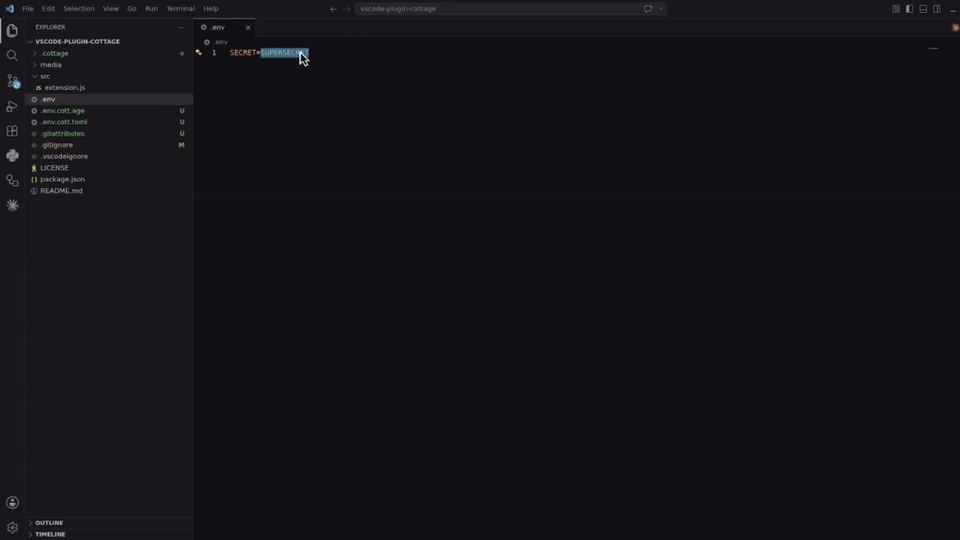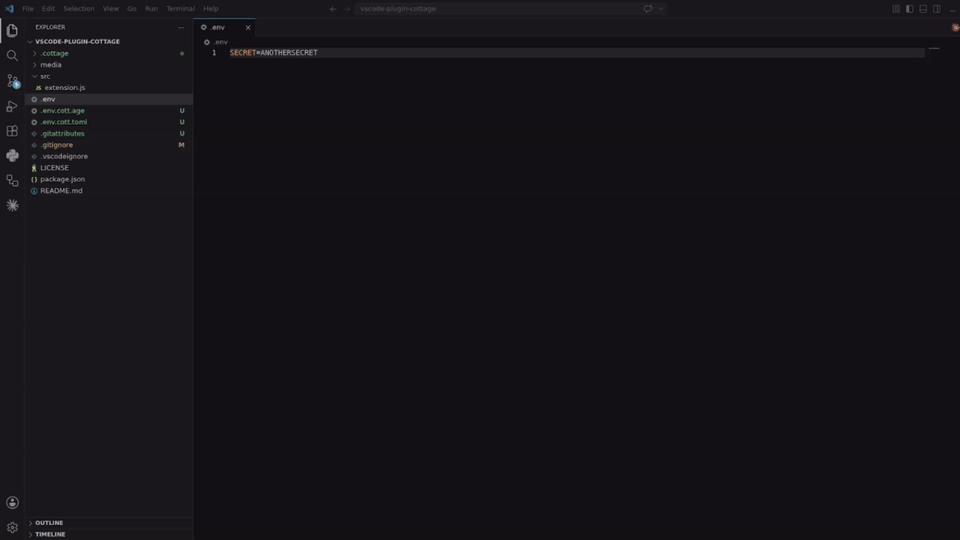](https://marketplace.visualstudio.com/items?itemName=sayanarijit.vscode-plugin-cottage)
इसे [Visual Studio Marketplace](https://marketplace.visualstudio.com/items?itemName=sayanarijit.vscode-plugin-cottage) से install करें, या [`vscode-plugin-cottage`](https://github.com/sayanarijit/vscode-plugin-cottage) से locally build और install करें।
### Cursor and Eclipse Extension
[VSX file](https://open-vsx.org/extension/sayanarijit/vscode-plugin-cottage) डाउनलोड करें और इसे अपने Cursor या Eclipse IDE में install करें। यह VS Code extension की तरह ही काम करता है।
### Vim Plugin
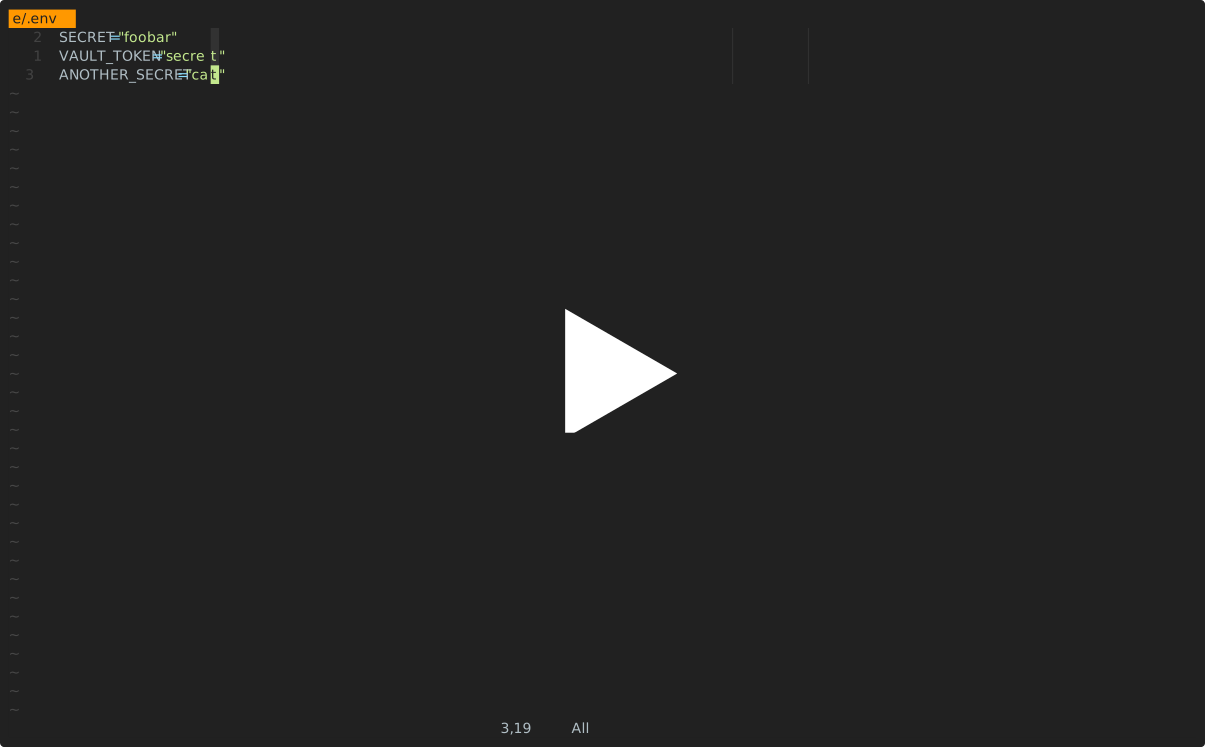
Vim या Neovim से secrets को encrypt/decrypt करने के लिए [cottage.vim](https://github.com/sayanarijit/cottage.vim) plugin का उपयोग करें।
[](https://asciinema.org/a/1264076)
## AI Agent Integrations
नीचे दिए गए सभी integrations AI agents को सीधे `ctg`/`ctgx` चलाने और secret files को देखने या edit करने से रोकते हैं: `.cottage/` के अंदर कुछ भी, कोई भी `*.cott.*` file (encrypted `*.cott.age` blobs और redacted `*.cott.toml` previews), और कोई भी decrypted file जिसका disk पर अभी भी `*.cott.age` counterpart मौजूद है।
### Claude Code Integration
यदि आप Claude Code का उपयोग कर रहे हैं, तो secrets वाले अपने repos में [`.claude/settings.json`](https://github.com/sayanarijit/cottage/blob/main/.claude/settings.json) और [`.claude/hooks/deny-secrets.py`](https://github.com/sayanarijit/cottage/blob/main/.claude/hooks/deny-secrets.py) जोड़ें ताकि Claude Code sessions secrets को सुरक्षित रूप से संभालें, या [claude-plugin-cottage](https://github.com/sayanarijit/claude-plugin-cottage) plugin install करें।
### GitHub Copilot Integration
यदि आप VS Code में GitHub Copilot का उपयोग कर रहे हैं, तो secrets वाले अपने repos में [`.github/hooks/ctg-policy.json`](https://github.com/sayanarijit/cottage/blob/main/.github/hooks/ctg-policy.json) और [`.github/hooks/scripts/deny_ctg_command.py`](https://github.com/sayanarijit/cottage/blob/main/.github/hooks/scripts/deny_ctg_command.py) जोड़ें ताकि Copilot sessions decrypted files को साफ़ करें, सीधे `ctg` shell commands को block करें, और secret files तक पहुँच को block करें, या इसे VS Code से सेट करने के लिए [vscode-plugin-cottage](https://github.com/sayanarijit/vscode-plugin-cottage) extension install करें।
VS Code [`.claude/settings.json`](https://github.com/sayanarijit/cottage/blob/main/.claude/settings.json) hook definitions को भी load करता है। यदि आप एक ही repo में Claude और Copilot दोनों hook files रखते हैं, तो सुनिश्चित करें कि आप गलती से एक ही cleanup hook दो बार न चलाएँ।
### Codex Integration
यदि आप Codex का उपयोग कर रहे हैं, तो secrets वाले अपने repos में [`.codex/hooks.json`](https://github.com/sayanarijit/cottage/blob/main/.codex/hooks.json) और [`.codex/hooks/deny-ctg.py`](https://github.com/sayanarijit/cottage/blob/main/.codex/hooks/deny-ctg.py) जोड़ें ताकि Codex sessions secrets को सुरक्षित रूप से संभालें, या [codex-plugin-cottage](https://github.com/sayanarijit/codex-plugin-cottage) plugin install करें।
Codex को चलने से पहले local hooks की समीक्षा आवश्यक है। files जोड़ने के बाद, repo में Codex शुरू करें और project hooks की समीक्षा और भरोसा करने के लिए `/hooks` का उपयोग करें।
### Antigravity (agy) Integration
यदि आप Antigravity (`agy`) का उपयोग कर रहे हैं, तो secrets वाले अपने repos में [`.agents/hooks.json`](https://github.com/sayanarijit/cottage/blob/main/.agents/hooks.json) और [`.agents/scripts/deny-ctg.py`](https://github.com/sayanarijit/cottage/blob/main/.agents/scripts/deny-ctg.py) जोड़ें ताकि Antigravity sessions secrets को सुरक्षित रूप से संभालें, या [agy-plugin-cottage](https://github.com/sayanarijit/agy-plugin-cottage) plugin install करें।
### Cursor Integration
यदि आप Cursor का उपयोग कर रहे हैं, तो secrets वाले अपने repos में [`.cursor/hooks.json`](https://github.com/sayanarijit/cottage/blob/main/.cursor/hooks.json), [`.cursor/hooks/deny-ctg.py`](https://github.com/sayanarijit/cottage/blob/main/.cursor/hooks/deny-ctg.py), [`.cursor/hooks/deny-read-secrets.py`](https://github.com/sayanarijit/cottage/blob/main/.cursor/hooks/deny-read-secrets.py), [`.cursor/rules/deny-ctg.mdc`](https://github.com/sayanarijit/cottage/blob/main/.cursor/rules/deny-ctg.mdc), और [`.cursorignore`](https://github.com/sayanarijit/cottage/blob/main/.cursorignore) जोड़ें ताकि Cursor sessions secrets को सुरक्षित रूप से संभालें।
Cursor में पहले hooks enable करना आवश्यक है। Cursor Settings > Hooks खोलें और hooks enable करें, फिर agent session को restart करें ताकि project hooks प्रभावी हों। `.cursorignore` इसके अतिरिक्त secret files को Cursor की indexing और Agent के context से बाहर रखता है।
## Quick Start
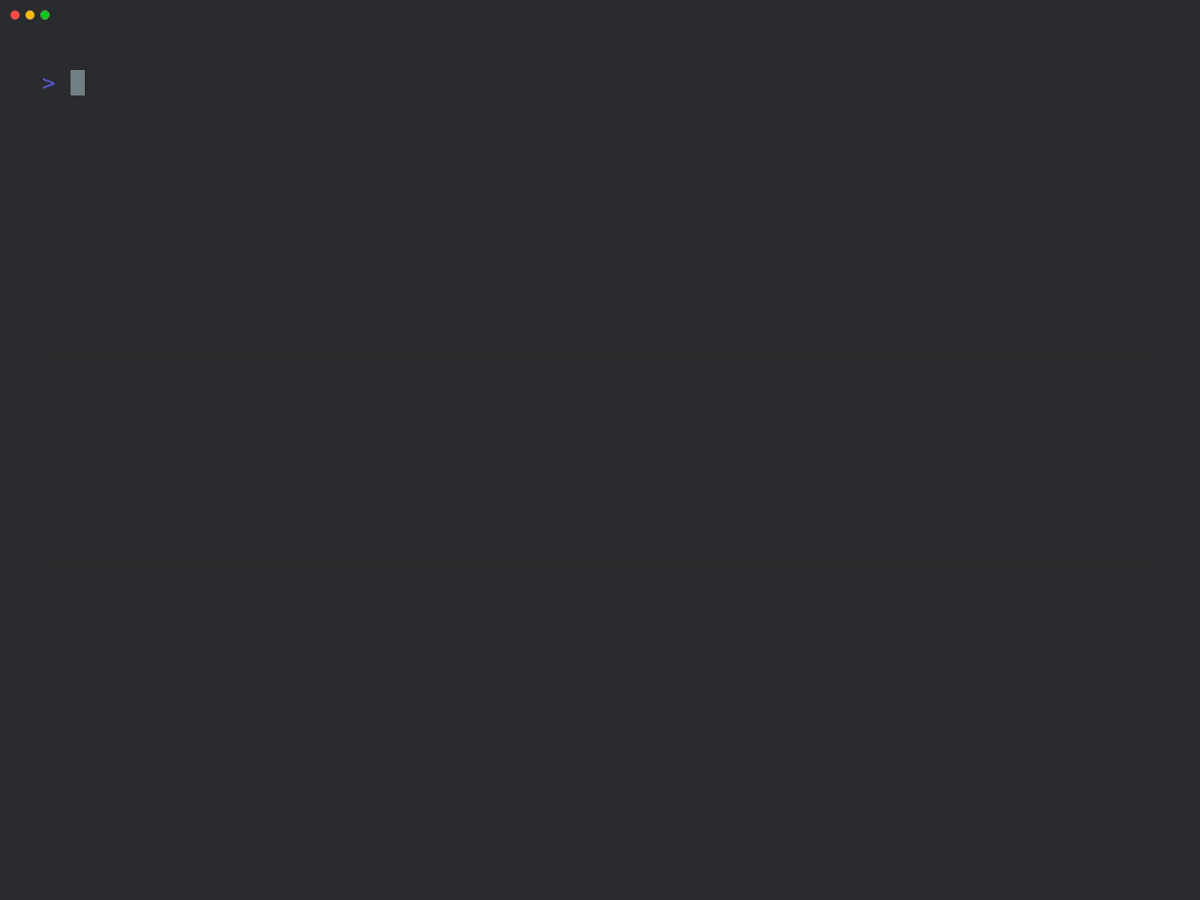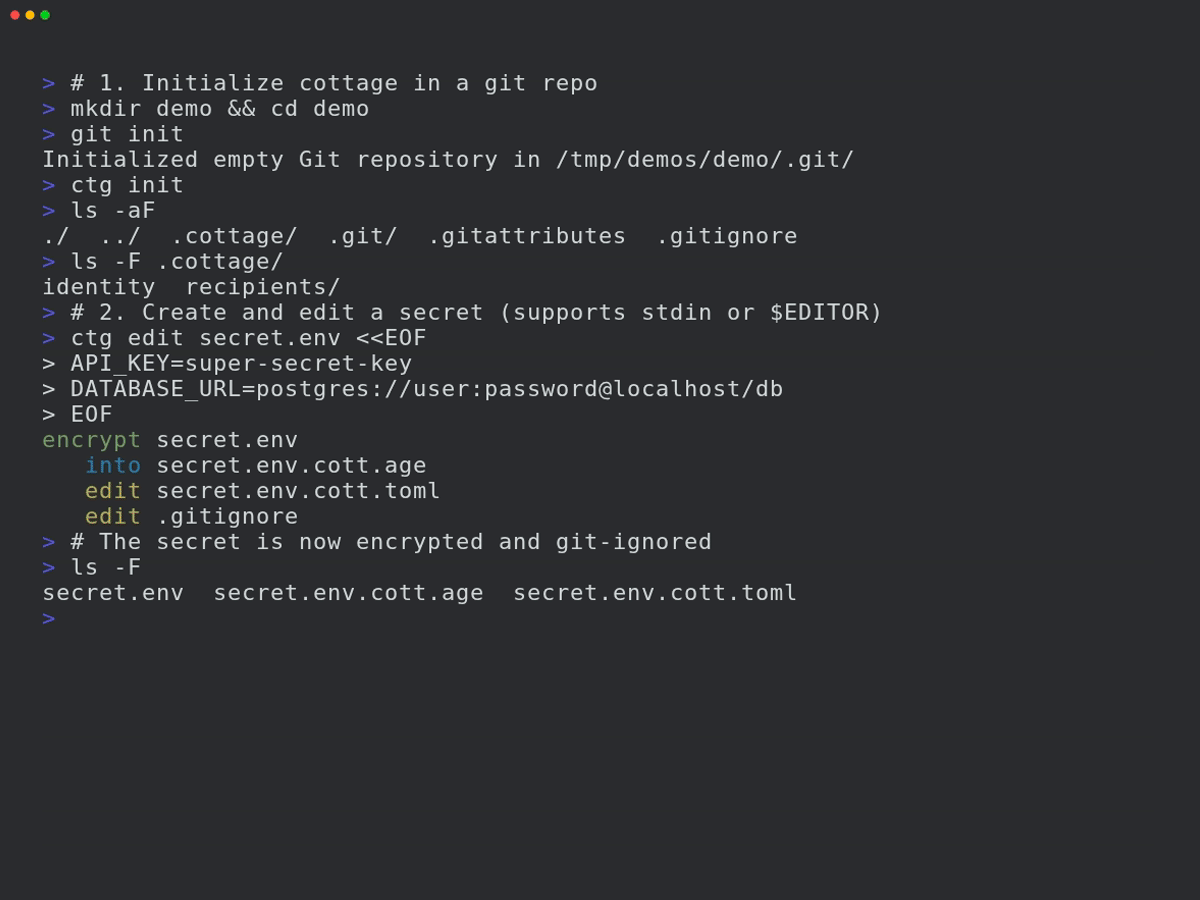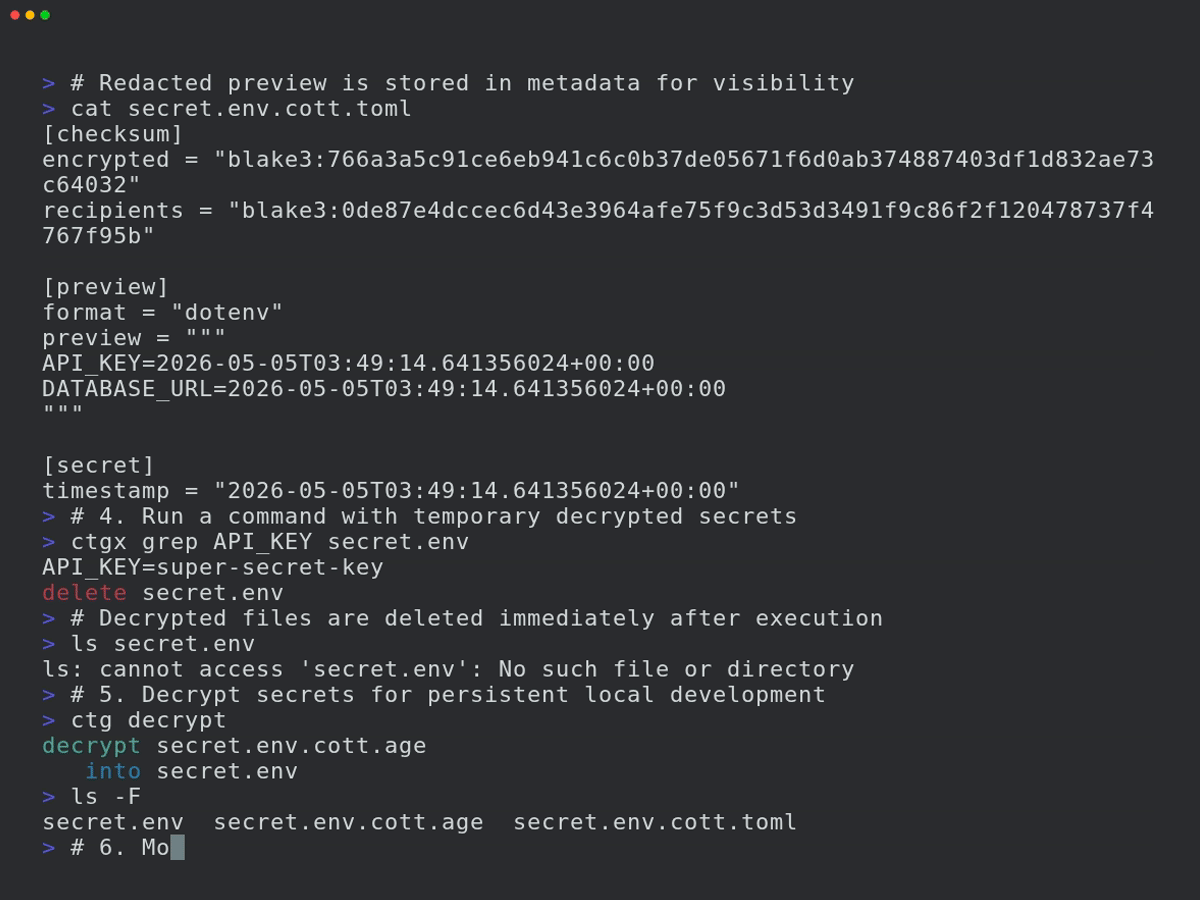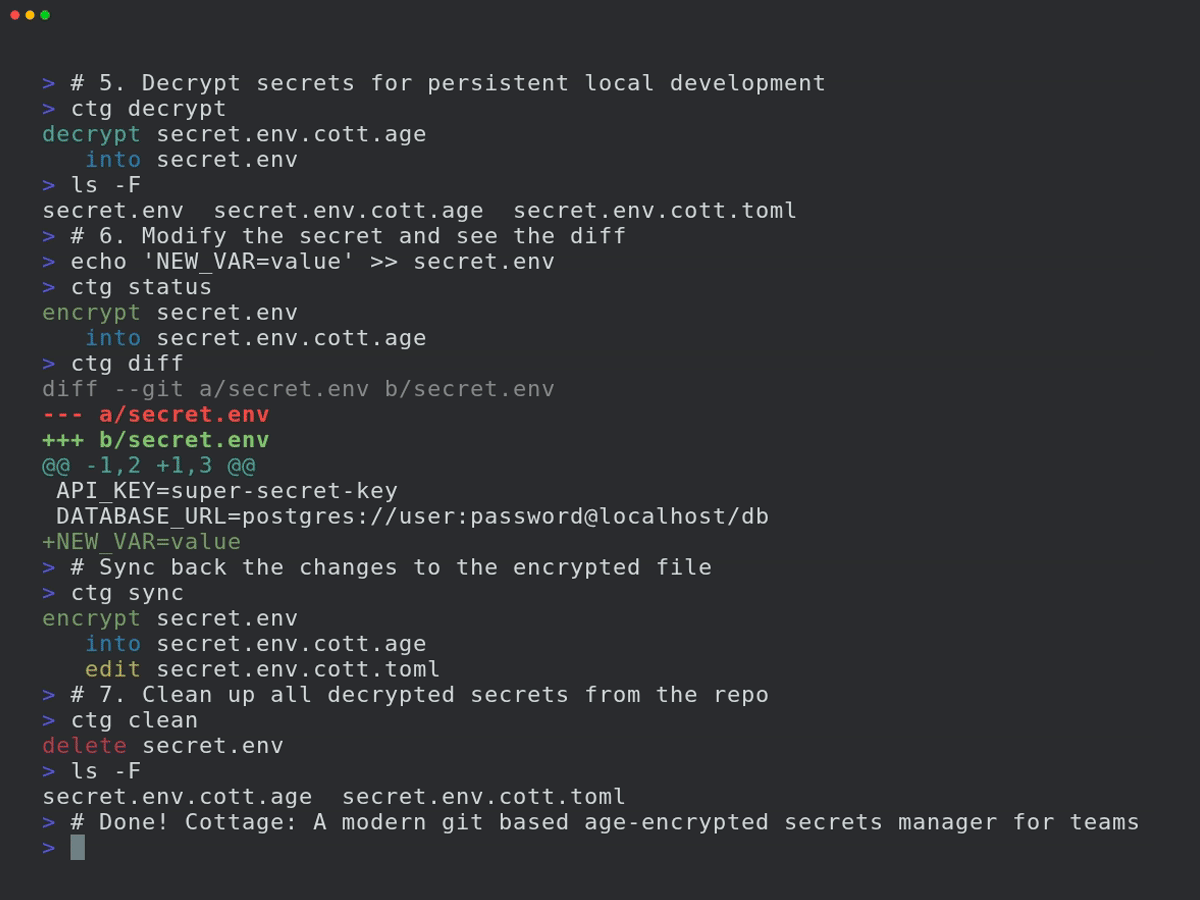
Project init करें:
```bash
mkdir project && cd project
git init # Optional, cottage works better with git but it's not required
ctg init # Sets up the .cottage directory and necessary files
tree -a
# .
# ├ .cottage/ <- Auto-generated by `ctg init`
# │ └ recipients/ <- This is where your team keeps the public keys of all the recipients.
# │ └ sayanarijit <- Your public key. Commit it. To use an existing public key, just copy that key here.
# ├ .git/...
# └ .gitattributes <- Added `*.cott.age binary linguist-generated filter=cottage-encrypted -diff` to avoid polluting git diff
# Your private key is stored safely in `~/.config/cottage/identity/<dirname>/<timestamp>.key`.
# You can run `ctg clean --all` anytime to clean up everything cottage ever did.
```
एक secret बनाएँ या edit करें:
```bash
# `ctg edit` decrypts the file before opening in $EDITOR and re-encrypts upon save.
# If the decrypted file was not present on disk before running `ctg edit`, it is cleaned up afterwards.
# If it was already present, it is kept on disk.
ctg edit secret.yml
# Use `--clean` with `ctg edit` or `ctg encrypt` to ensure decrypted files are deleted even if present before
ctg edit secret.yml --clean # Opens in $EDITOR, encrypts on save, and cleans up
ctg encrypt secret.yml --clean # Encrypts secret.yml and cleans up
# encrypt secret.yml
# into secret.yml.cott.age
# edit secret.yml.cott.toml
# edit .gitignore
# delete secret.yml
```
Decrypted secrets के साथ एक command चलाएँ:
```bash
cat secret.yml
# cat: secret.yml: No such file or directory
# `ctg run` (or shortcut `ctgx`) decrypts secrets before running the command.
# If the decrypted files were not present on disk beforehand, they are automatically cleaned up after the command finishes.
# If they were already present beforehand, they are kept on disk.
ctg run -- kubectl apply -f secret.yml # decrypts secret.yml.cott.age to secret.yml and runs the command
ctg run -- kubectl apply -f secret.yml.cott.age # also replaces the path argument with the decrypted file path
ctg run -- kubectl apply -f . # decrypts all .cott.age files in . and runs the command
ctg run -- ./deploy.sh # decrypts all .cott.age files in repo and runs the command
cat secret.yml
# cat: secret.yml: No such file or directory
# Use `--clean` to ensure decrypted files are cleaned up even if they were present before
ctg run --clean ./deploy.sh
```
या shortcut का उपयोग करें:
```bash
ctgx -- ./deploy.sh
ctgx --clean -- ./deploy.sh
```
एक decrypted secret को disk पर लिखे बिना पढ़ें और pipe करें:
```bash
ctg cat secret.yml.cott.age
ctg cat secret.yml | kubectl apply -f -
ctg cat .env.prod | docker run --rm --env-file /dev/stdin my-image:latest
```
Secrets को environment variables के रूप में inject करके एक command चलाएँ, बिना disk पर लिखे:
```bash
ctg env -- ./deploy.sh # Export secrets from .env.cott.age (default) without writing them to disk, then run deploy.sh
ctg env -F .env.prod.cott.age -- ./deploy.sh # exports from .env.prod.cott.age instead of .env.cott.age
ctg env -F secrets.json.cott.age -- printenv COTTAGE_SECRET # Also supports non-dotenv files.
```
## GitOps
अपने secrets को team members के साथ साझा करने के लिए, बस git repo में push करें।
```bash
git add .
git commit -m "Add secret.yml"
git push origin main
```
अपने साथियों से कहें कि वे अपनी public keys `.cottage/recipients` में जोड़ें और changes push करें। फिर आप pull कर सकते हैं और उनके लिए secrets को re-encrypt कर सकते हैं।
```bash
git pull origin main
ctg decrypt --skip-verify-recipients # Decrypt missing secrets for re-encryption
ctg encrypt # Re-encrypt all secrets
# encrypt secret.yml
# into secret.yml.cott.age
# edit secret.yml.cott.toml
ctg clean # optional
# delete secret.yml
# review changes, commit and push
git add .
git commit -m "Add new recipient to secrets"
git push origin main
```
अब आपके साथी नवीनतम changes pull कर सकते हैं और अपने लिए secrets decrypt कर सकते हैं।
## Git Hooks
आप commit से पहले secrets को स्वचालित रूप से check/encrypt करने और checkout के बाद decrypt करने के लिए git hooks सेट करने हेतु [prek](https://github.com/j178/prek) या [pre-commit](https://pre-commit.com/) का उपयोग कर सकते हैं।
[यहाँ example prek configuration देखें](https://github.com/sayanarijit/cottage/blob/main/examples/prek.toml)।
`prek.toml` file जोड़ने के बाद, चलाएँ:
```bash
prek install
prek install --hook-type post-checkout
prek install --hook-type post-merge
prek install --hook-type post-rewrite
```
## Access Control
### Rules
Metadata file में, आप annotate कर सकते हैं कि secret किन recipients के लिए encrypt किया जाना चाहिए।
यह आपको विभिन्न environments (जैसे staging vs production) के लिए अलग-अलग secrets रखने और उन्हें केवल relevant recipients के लिए encrypt करने की सुविधा देता है।
```toml
# secret.yml.cott.toml
[secret]
allow = ["sayanarijit"] # Only encrypt for sayanarijit
```
```toml
# secret.yml.cott.toml
[secret]
deny = ["sayanarijit"] # Encrypt for everyone except sayanarijit
```
```toml
# secret.yml.cott.toml
[secret]
allow = ["env/staging/*"] # Supports glob patterns, only encrypt for recipients in env/staging
deny = ["env/staging/badservice"] # Encrypt for everyone in env/staging except badservice
```
Deny rules allow rules पर प्राथमिकता लेते हैं।
अधिक जानकारी के लिए [metadata specification](https://github.com/sayanarijit/cottage/blob/main/SPECIFICATION.md#secretmetadata) देखें।
### Verification
Tampering रोकने के लिए, आप CI में `ctg verify` चला सकते हैं ताकि यह सत्यापित हो सके कि encrypted secrets और recipient lists metadata rules से मेल खाते हैं।
```yaml
# .github/workflows/cottage-verify.yml
name: Cottage Verify
on: [push, pull_request]
permissions:
contents: read
jobs:
verify-secrets:
runs-on: ubuntu-latest
steps:
- uses: actions/checkout@v3
- name: Verify secrets
run: docker run --rm -v "${{ github.workspace }}:/app" ghcr.io/sayanarijit/cottage verify
```
## Any Provider as Upstream
cottage के साथ, आप secrets को किसी भी API वाले provider के साथ sync कर सकते हैं, केवल git ही नहीं।
इसके लिए, project root में `cottage.toml` नाम की एक file बनाएँ और upstream settings configure करें।
[यहाँ example `cottage.toml` देखें](https://github.com/sayanarijit/cottage/blob/main/cottage.toml) और [यहाँ secret specific upstream configuration देखें](https://github.com/sayanarijit/cottage/blob/main/examples/secrets/secret.json.cott.toml)।
[यहाँ example plugin implementation देखें](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-vault-in-kubernetes.py)।
Workflow git के समान है, लेकिन `git pull` और `git push` के बजाय, आप configured upstream के साथ secrets sync करने के लिए `ctg pull` और `ctg push` चलाते हैं।
उदाहरण:
```bash
# Pull latest changes into local encrypted secrets
# Similar to `git pull origin`
ctg pull myvault
# Compare diff with local decrypted secrets
ctg diff
# Sync local decrypted secrets with local encrypted secrets
ctg sync
# Push changes from local encrypted secrets to upstream
# Similar to `git push origin main`
ctg push myvault
```
अधिक जानकारी के लिए [upstream configuration specification](https://github.com/sayanarijit/cottage/blob/main/SPECIFICATION.md#upstreamconfig) देखें।
### Example plugins
Cottage आपके secrets को sync करने के लिए विभिन्न plugin providers का समर्थन करता है। तैयार-से-उपयोग plugin scripts [examples/plugins](https://github.com/sayanarijit/cottage/blob/main/examples/plugins) directory में उपलब्ध हैं:
- [1Password](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-onepassword.py)
- [AWS Secrets Manager](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-aws-secretsmanager.py)
- [Azure Key Vault](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-azure-keyvault.py)
- [Bitwarden](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-bitwarden.py)
- [Dashlane](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-dashlane.py)
- [Doppler](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-doppler.py)
- [ejson](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-ejson.py)
- [GitHub Secrets](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-github-secrets.py)
- [Google Cloud Secret Manager](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-gcp-secretmanager.py)
- [HashiCorp Vault](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-vault.py) (also see [Vault in Kubernetes](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-vault-in-kubernetes.py))
- [Keeper Security](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-keeper.py)
- [KeePass (Passhole)](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-passhole.py)
- [LastPass](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-lastpass.py)
- [pass (password-store)](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-pass.py)
- [Proton Pass](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-protonpass.py)
- [System Keyring](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-keyring.py)
- [Zoho Vault](https://github.com/sayanarijit/cottage/blob/main/examples/plugins/cottage-plugin-zoho-vault.py)
## Sync with any device
अपने secrets को अपने devices के बीच sync करने और CLI की आवश्यकता के बिना browse करने के लिए [Cottage Sync](https://cottage-sync.github.io) का उपयोग करें।
## Learn More
अधिक उपयोग उदाहरणों के लिए [examples](https://github.com/sayanarijit/cottage/blob/main/examples) directory देखें।
## Troubleshooting
```bash
# See debug logs with -v, -vv or -vvv
ctg run -vvv -- ./deploy.sh
```
## Comparison
### age vs Other Encryption
[age](https://age-encryption.org) सुरक्षित file encryption के लिए optimized एक आधुनिक, सरल algorithm का उपयोग करता है, जिसमें usability और minimal attack surface पर ध्यान केंद्रित है। यह [SSH RSA और Ed25519 keys का भी समर्थन करता है](https://words.filippo.io/using-ed25519-keys-for-encryption/), हालाँकि अलग-अलग purposes और scopes के लिए अलग-अलग keys का उपयोग करने की सिफारिश की जाती है।
### cottage vs SOPS
हालाँकि [SOPS](https://getsops.io/) और cottage में कई overlapping features हैं, cottage के निम्नलिखित लाभ हैं:
- unencrypted secrets कभी git में commit न हों, यह सुनिश्चित करने के लिए .gitignore को auto manage करता है।
- Encrypted secrets के pure age encrypted .age files होने से tools के व्यापक ecosystem के साथ बेहतर interoperability संभव होती है।
- Cleaner diffs - SOPS के विपरीत, जो हर secret के हर value के लिए diffs generate करता है, भले ही वास्तविक change केवल एक recipient जोड़ना/हटाना हो, cottage प्रति file केवल एक diff generate करता है, जो recipients checksum में change को स्पष्ट रूप से इंगित करता है।
### cottage vs dotenvx
cottage ने `ctg env` API [dotenvx](https://dotenvx.com) से उधार ली है।
- केवल dotenv files ही नहीं, किसी भी file type का समर्थन करता है।
- एक repo में कई secrets प्रबंधित करता है।
- विशिष्ट recipients के लिए secrets encrypt करने के लिए access control rules।
- Cleaner diffs - [cottage vs SOPS](#cottage-vs-sops) देखें।
### cottage vs agebox
[agebox](https://github.com/slok/agebox) core philosophy में cottage के बहुत समान है लेकिन इसमें कई [features](#features) की कमी है।
