 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.

Block malicious packages before they install.



Developers and AI coding agents install packages every day. Each npm install or pip install executes thousands of lines of code that nobody reviews.
Recent compromises in popular ecosystems:
PMG is free, open source (Apache 2.0), and requires no account or API key. It intercepts every package install and checks it against SafeDep's free community API for known malware before code executes. For unknown malware, it uses dependency cooldown and opt-in sandbox for proactive security defense.
PMG takes a defense in depth approach. Zero config, works across Zsh, Bash, and Fish. Each intercepted install passes through the protection layers that apply to it before code runs, along with an audit trail.

npm, pip, and other package managers. Developers and AI agents use the same commands. No workflow changes.PMG is the only free, open-source, install-time package firewall that covers developers and AI agents alike and ships with sandboxing and cooldown out of the box.
| Capability | PMG | Socket | safe-chain | Snyk | Dependabot |
|---|---|---|---|---|---|
| OSS / built in public | ✓ | ✗ | ✓ | ✗ | ✗ |
| No account or API key | ✓ | ✓ | ✓ | ✗ | ✗ |
| Install-time malicious package blocking | ✓ | ✓ | ✓ | ✗ | ✗ |
| Dependency cooldown policy | ✓ | ✗ | ✓ | ✗ | ✗ |
| Runtime sandboxing | ✓ | ✗ | ✗ | ✗ | ✗ |
| Protects AI coding agents transparently | ✓ | ✗ | ✗ | ✗ | ✗ |
| Local audit logs | ✓ | ✗ | ✗ | ✗ | ✗ |
| Known-CVE remediation PRs | ✗ | ✗ | ✗ | ✓ | ✓ |
curl -fsSL https://raw.githubusercontent.com/safedep/pmg/main/install.sh | sh
See Installation for Homebrew, npm, and other install methods.
Wire PMG into your shell so it intercepts package managers.
pmg setup install
# Restart your terminal to apply changes
Tip: Re-run
pmg setup installafter upgrading PMG to pick up new configuration options.All-users / golden images:
sudo pmg setup install --systemon Linux, orpmg setup install --systemas administrator on Windows — see docs/system-install.md.
Validate your installation and verify protection is working:
pmg setup doctor
Optional: PMG inspects HTTPS traffic with an on-the-fly CA that it injects into package managers per run. To persist a single CA across runs and trust it in your OS trust store (needed for tools that ignore CA environment variables, such as Go on macOS and Windows), install it once:
pmg setup cert install          # user scope, no sudo
pmg setup cert status           # check trust state and expiry
See Certificate Authority for scopes, rotation, and removal.
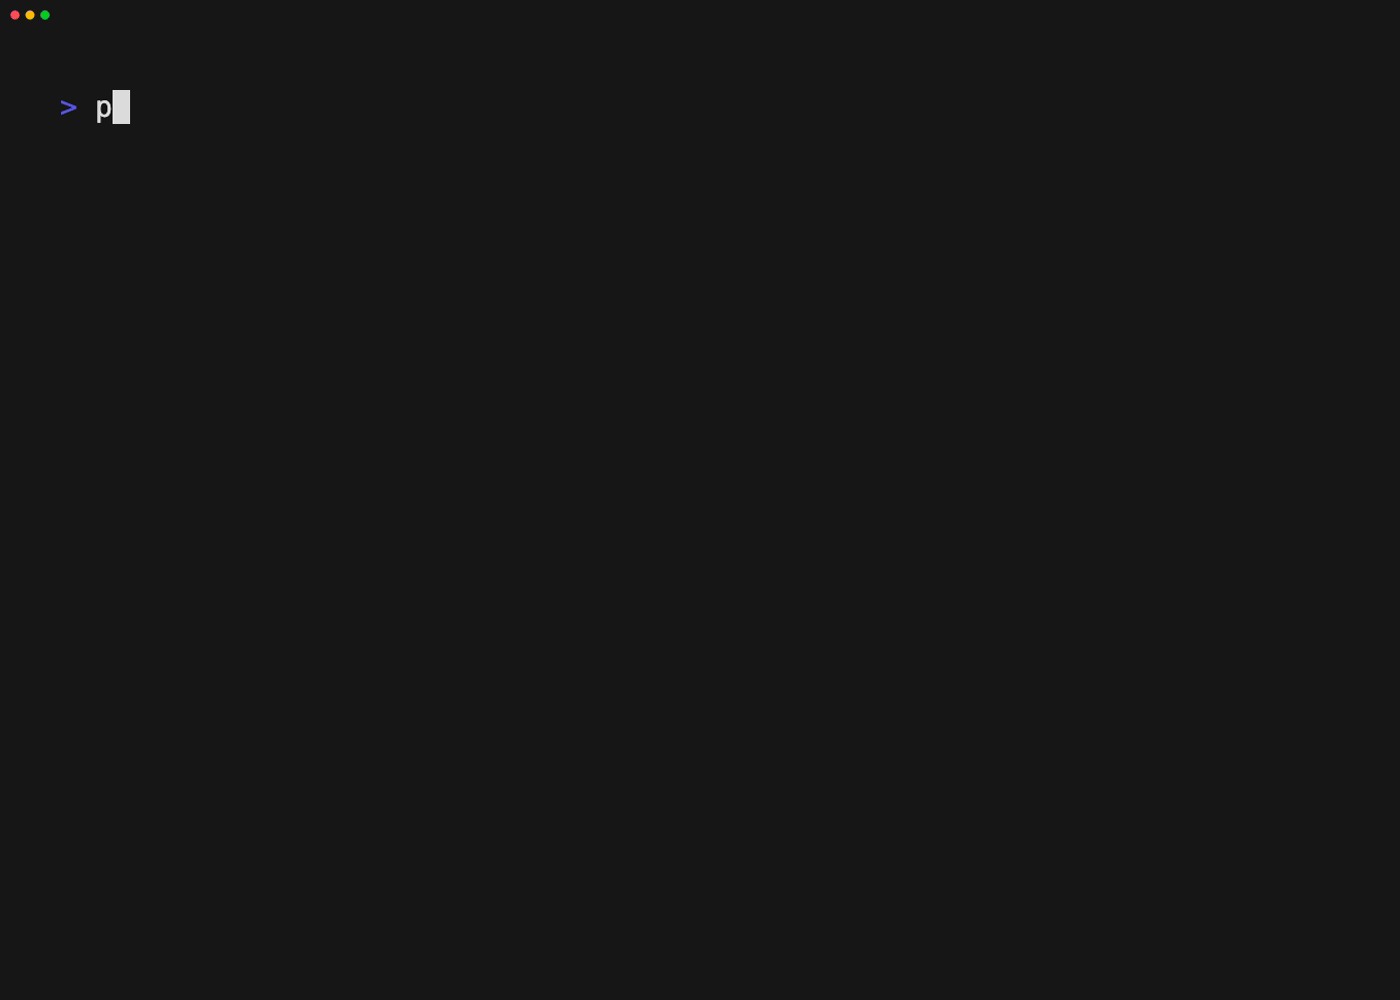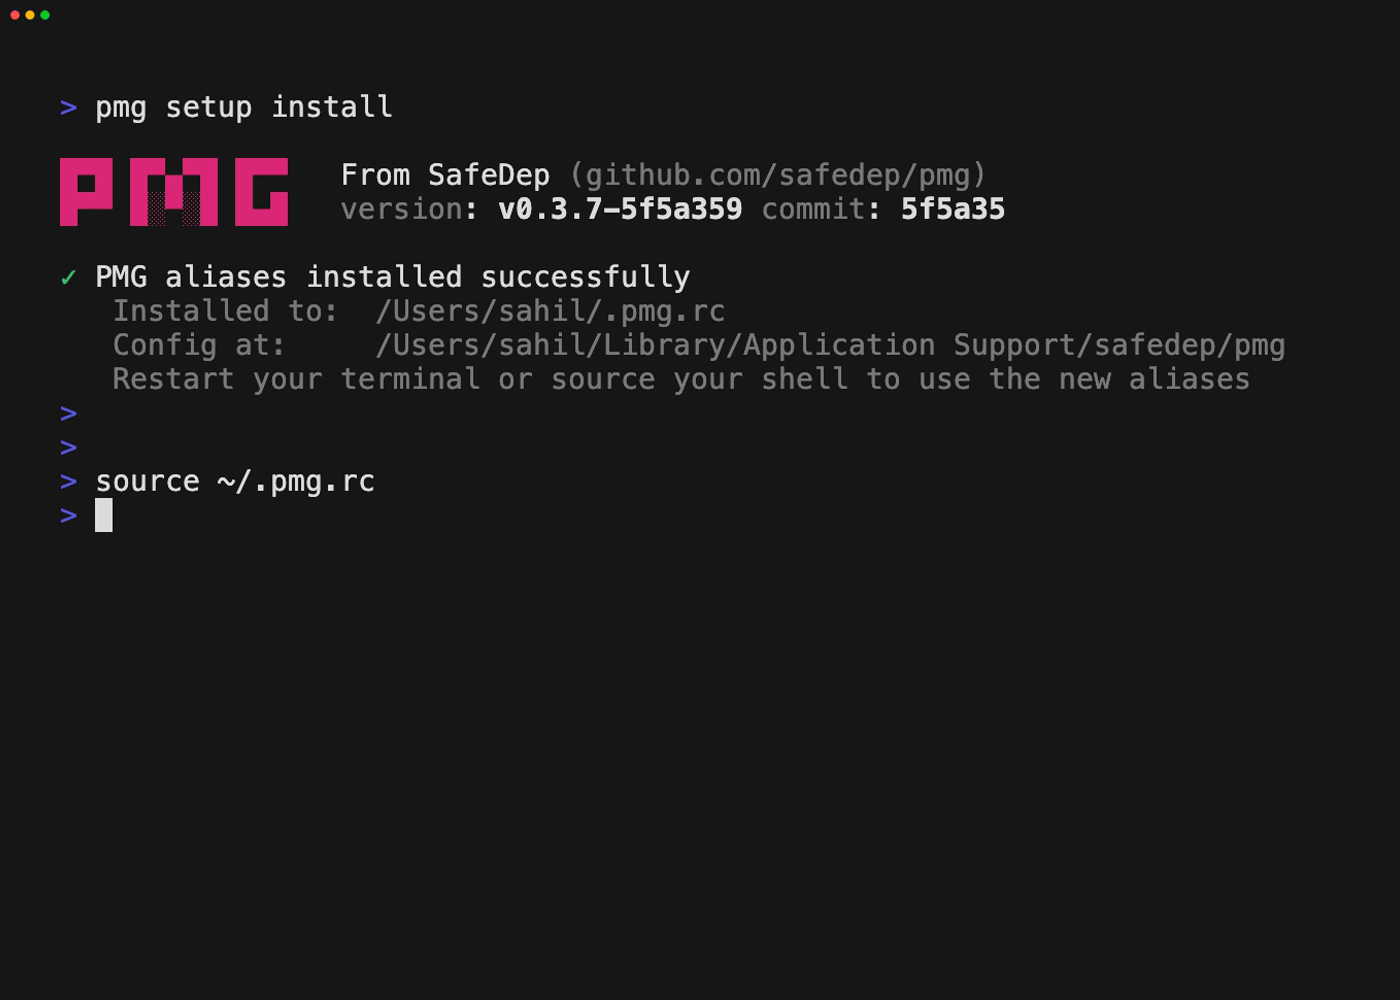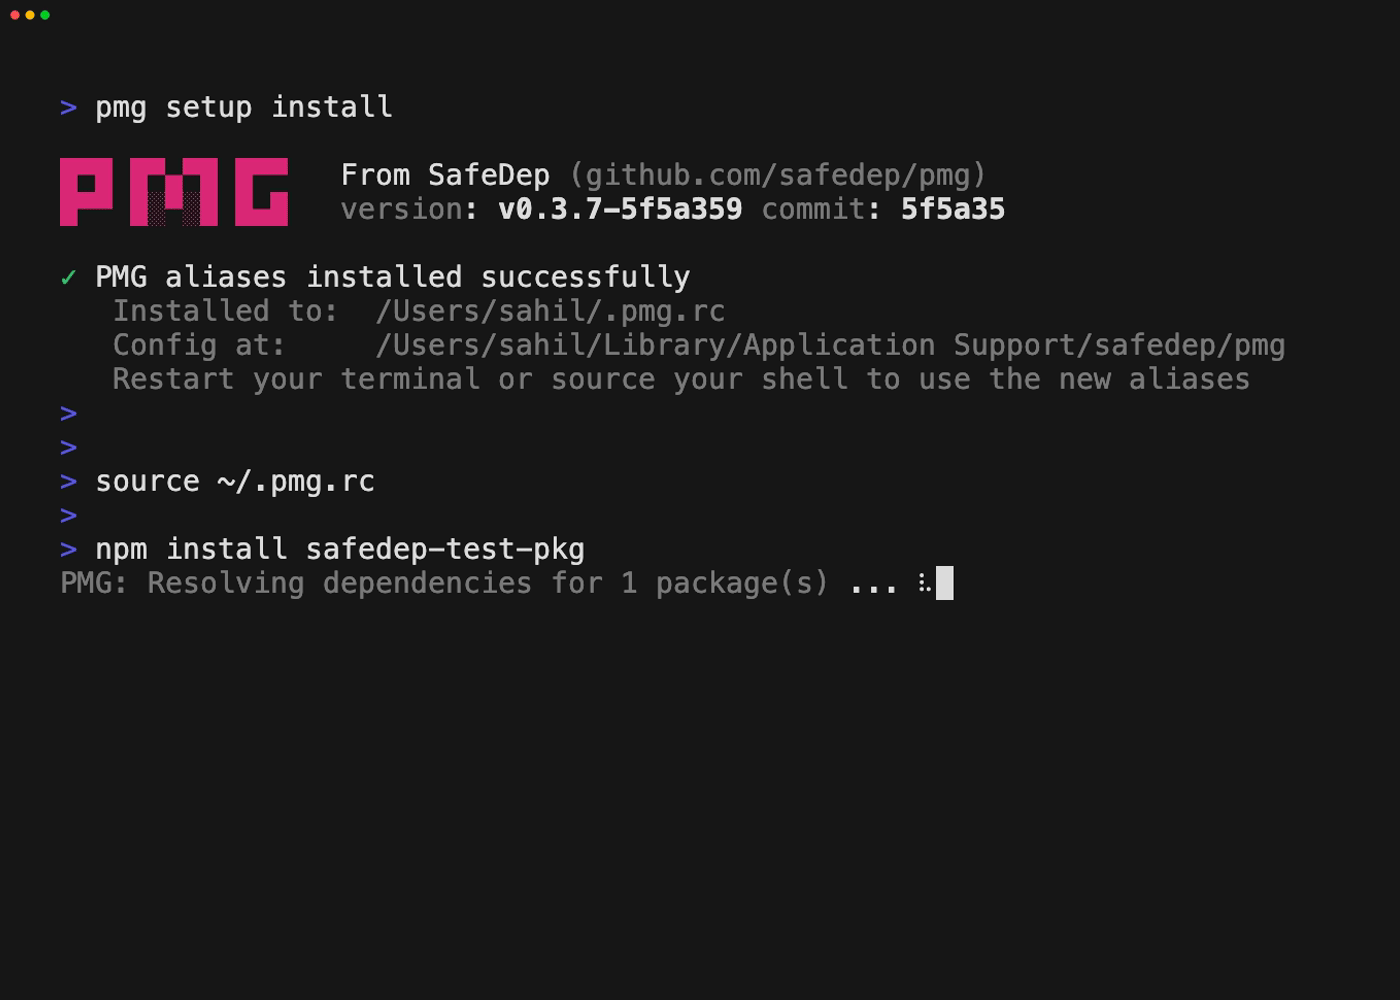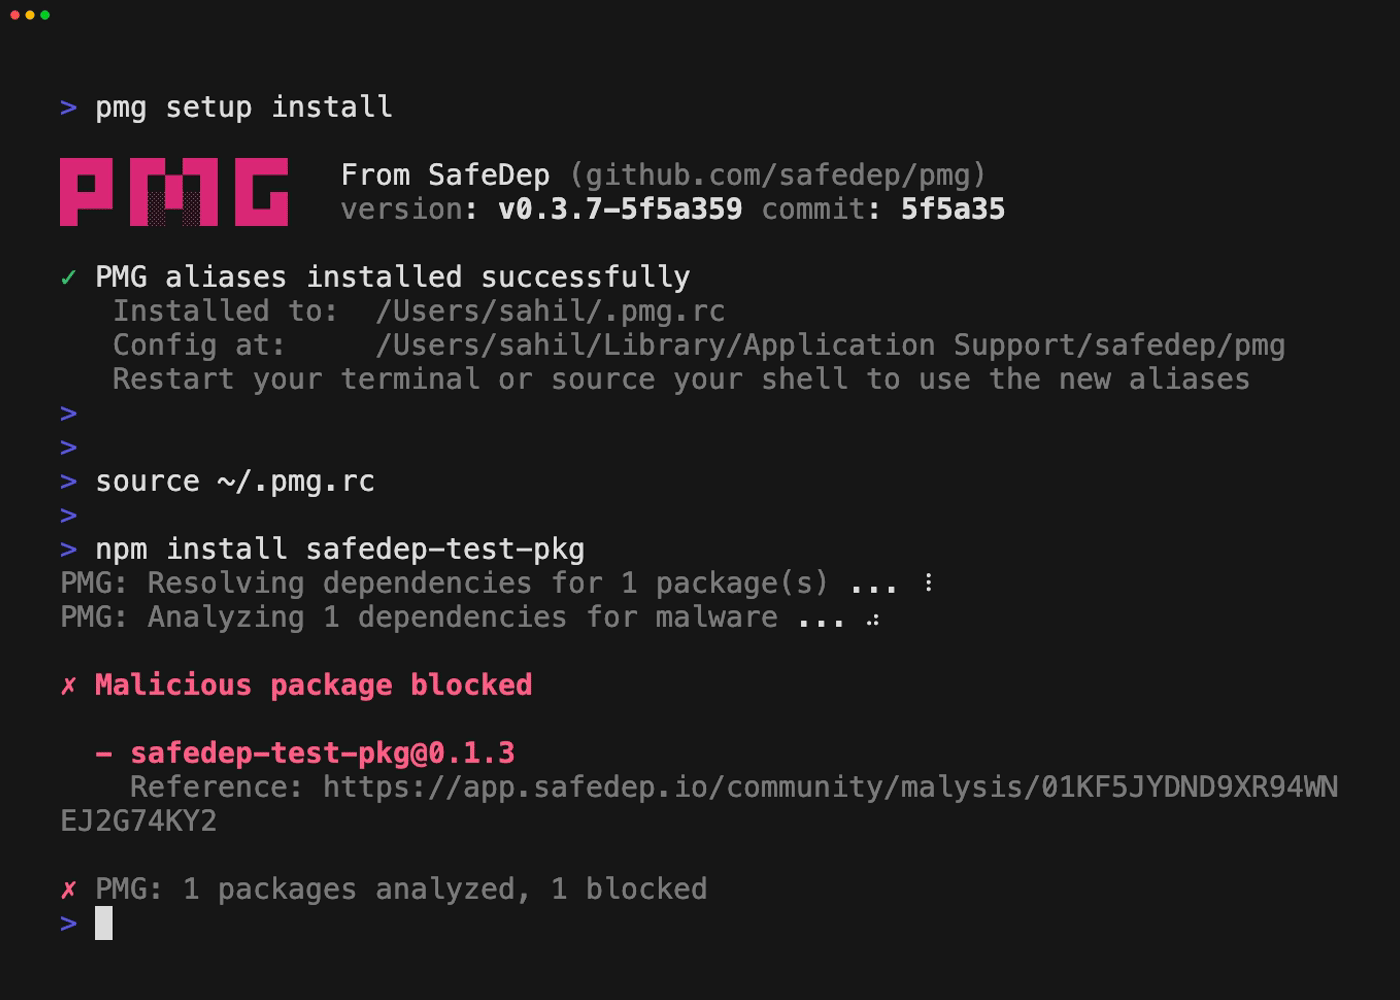
See PMG blocking threats.
npm install --no-cache --prefer-online [email protected]
Note:
safedep-test-pkgis a benign test package flagged as malicious in SafeDep's database for testing and verification purposes.
Continue using your package managers as usual, or let your AI coding agent run them. PMG sits in the path, blocking malicious packages.
npm install express
# or
pip install requests
PMG supports the tools you already use: