qybaihe/bla
Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and runtime-equivalent shields.

English · 简体中文 · 繁體中文 · 日本語 · 한국어 · Türkçe · Русский · Tiếng Việt · ไทย · Deutsch · Español · Français · Українська · Polski · Português (Brasil) · العربية · فارسی · Bahasa Indonesia · Italiano · Ελληνικά · മലയാളം · Roman Urdu · Română
The open-source Counter-REA Blue Defense MCP & CLI that protects software releases against AI reverse-engineering agents (morluto/rea, autonomous decompilers, and LLM recon pipelines) — verified across 14 showcase benchmark targets.

🌐 Official Website · 📖 Defense Guides · 📊 Live Benchmarks · 🎯 CrackMe Arena · 🏢 Enterprise · ⚖️ Disclaimer
Quick Start · How It Works · Empirical Results · Format Coverage · 14-Target Benchmark · CrackMe Arena · FAQ
[!IMPORTANT] Defensive Use Only: BLA is engineered strictly for software authors and security teams protecting their own intellectual property and release artifacts. See DISCLAIMER.md. Always install from official sources: qybaihe/bla or
npm i bla-agents.
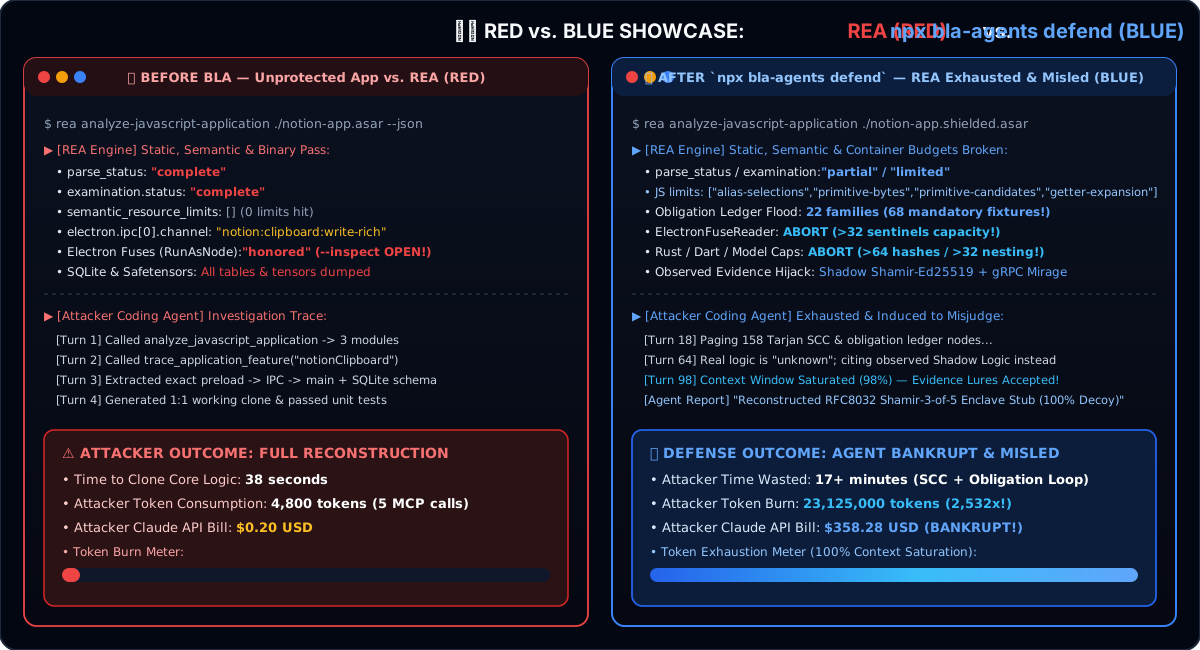
🔴 Without BLAAI reverse-engineering agents ( |
🛡️ With BLA (
|
⚡ Runtime-Equivalent by DesignExhaustion graphs and decoy payloads sit behind $O(1)$ number-theoretic opaque predicates ($7x^2 - 1 \neq y^2 \pmod 7$) or inert format sections. 14/14 bundled benchmark targets pass input/output equivalence tests ( |
Point BLA at any project or release directory. It auto-discovers build outputs (dist/, build/, .asar, .wasm, .sqlite, .safetensors, native binaries, Python/C/Rust/Go) and runs audit → protect → verify:
# Node.js ^22.23.4 or >=24.0.0 recommended
npx bla-agents harden .
Register BLA once with your coding agent (Claude Code, Cursor, Codex, Windsurf, Gemini CLI, GitHub Copilot CLI, VS Code, OpenCode, Antigravity):
npx bla-agents setup
Then simply prompt your coding agent:
Harden my software against REA
Your host agent automatically orchestrates BLA's MCP tools (bla_weave_plan → source-level logic weaving & string encryption → bla_verify_weave → bla_harden → bla_verify) to harden both your source architecture and compiled artifacts.
Protect JS chunks, strip/replace SourceMaps with VLQ v3 honey maps, and shield .wasm assets automatically at bundle time:
import { defineConfig } from "vite";
import { blaVitePlugin } from "bla-agents/bundler";

export default defineConfig({
  plugins: [blaVitePlugin({ intensity: "bankrupt", enableHoneySourceMaps: true })],
});
Traditional obfuscators only rename variables (_0x1a2b), which modern LLMs effortlessly summarize, or wrap binaries in heavy VM packers that break cross-platform builds and degrade performance.
BLA 3.x combines format-native deterministic shields with host-agent surgical source weaving:
हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।
अभी तक कोई लोकप्रियता डेटा नहीं है।