


secator - पेन्टेस्टर का स्विस चाकू
<h1 align="center">
<img src="https://assets.kitploit.com/production/public/readmes/6300/dc9ae605fb3dd81cb606836bd853e391122c4acde19b8554c2db00fcaa28a6e5.png" width="400">
</h1>
<h4 align="center">पेंटेस्टर की स्विस चाकू।</h4>
<p align="center">
<!-- <a href="https://goreportcard.com/report/github.com/freelabz/secator"><img src="https://goreportcard.com/badge/github.com/freelabz/secator"></a> -->
<img src="https://img.shields.io/badge/python-3.6-blue.svg">
<a href="https://github.com/freelabz/secator/releases"><img src="https://img.shields.io/github/release/freelabz/secator"></a>
<a href="https://github.com/freelabz/secator/blob/main/LICENSE"><img src="https://img.shields.io/badge/License-BSL%201.1-brightgreen.svg"></a>
<a href="https://pypi.org/project/secator/"><img src="https://img.shields.io/pypi/dm/secator"></a>
<a href="https://twitter.com/freelabz"><img src="https://img.shields.io/twitter/follow/freelabz.svg?logo=twitter"></a>
<a href="https://youtube.com/@FreeLabz"><img src="https://img.shields.io/youtube/channel/subscribers/UCu-F6SpU0h2NP18zBBP04cw?style=social&label=Subscribe%20@FreeLabz"></a>
<a href="https://discord.gg/nyHjC2aTrq"><img src="https://img.shields.io/discord/695645237418131507.svg?logo=discord"></a>
</p>
<p align="center">
<a href="#features">विशेषताएँ</a> •
<a href="#supported-commands">समर्थित कमांड</a> •
<a href="#install-secator">स्थापना</a> •
<a href="#usage">उपयोग</a> •
<a href="https://docs.freelabz.com">दस्तावेज़ीकरण</a> •
<a href="https://discord.gg/nyHjC2aTrq">Discord पर हमसे जुड़ें!</a>
</p>
`secator` एक कार्य और वर्कफ़्लो रनर है जो सुरक्षा मूल्यांकन के लिए उपयोग किया जाता है। यह दर्जनों प्रसिद्ध सुरक्षा उपकरणों का समर्थन करता है और इसे पेंटेस्टर्स और सुरक्षा शोधकर्ताओं की उत्पादकता बढ़ाने के लिए डिज़ाइन किया गया है।
# विशेषताएँ
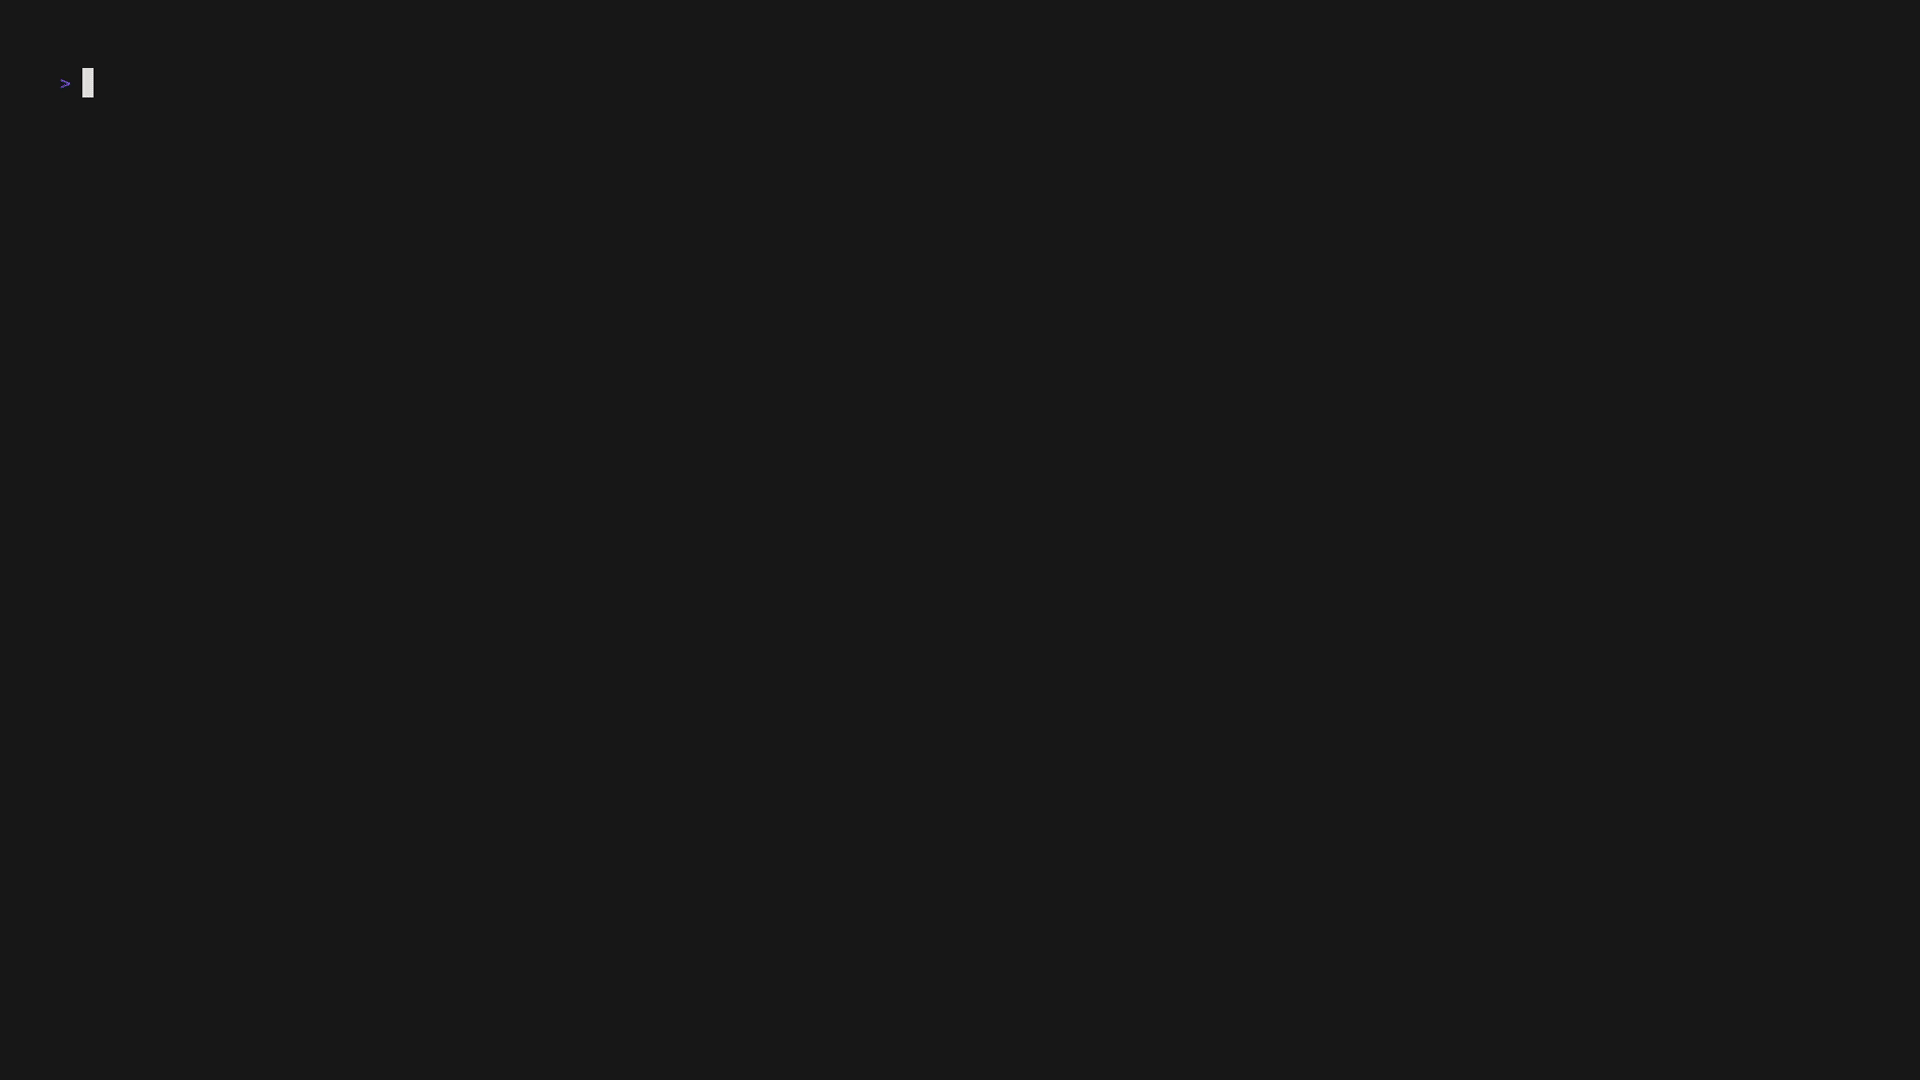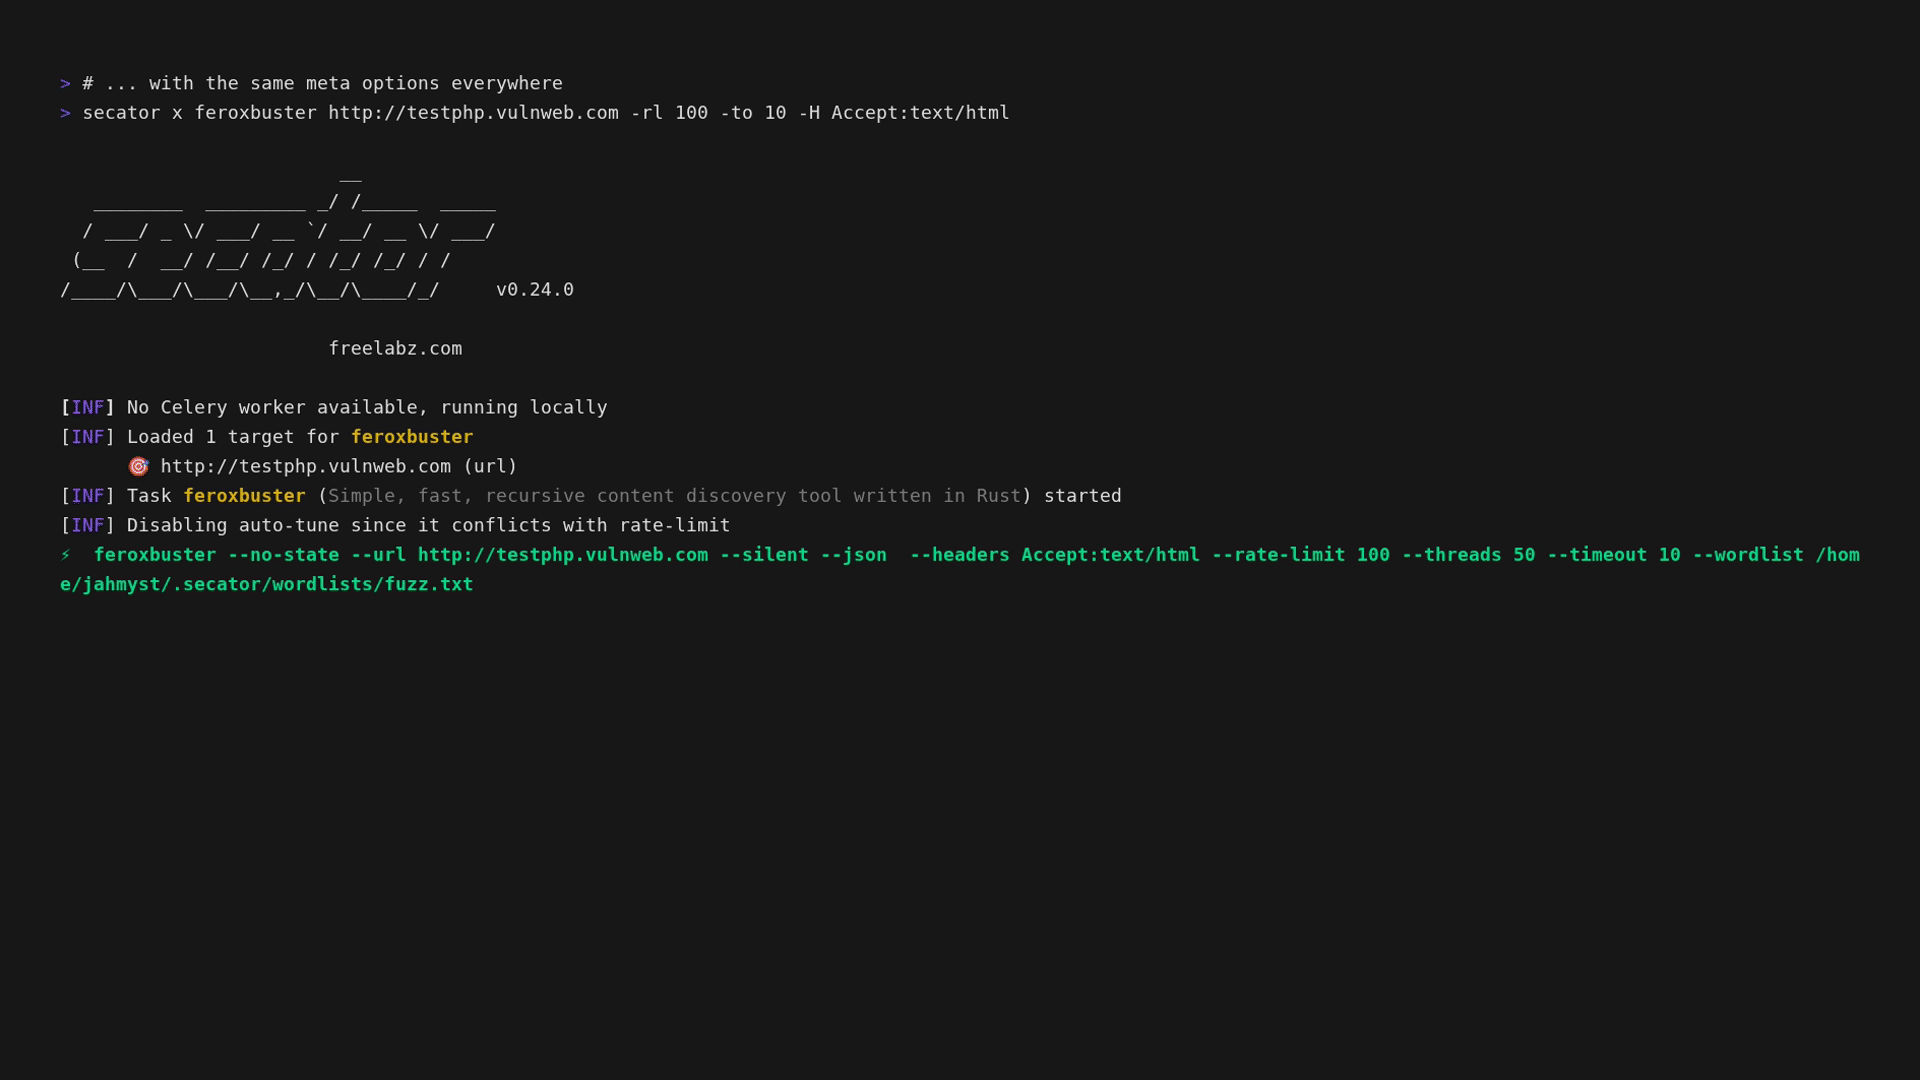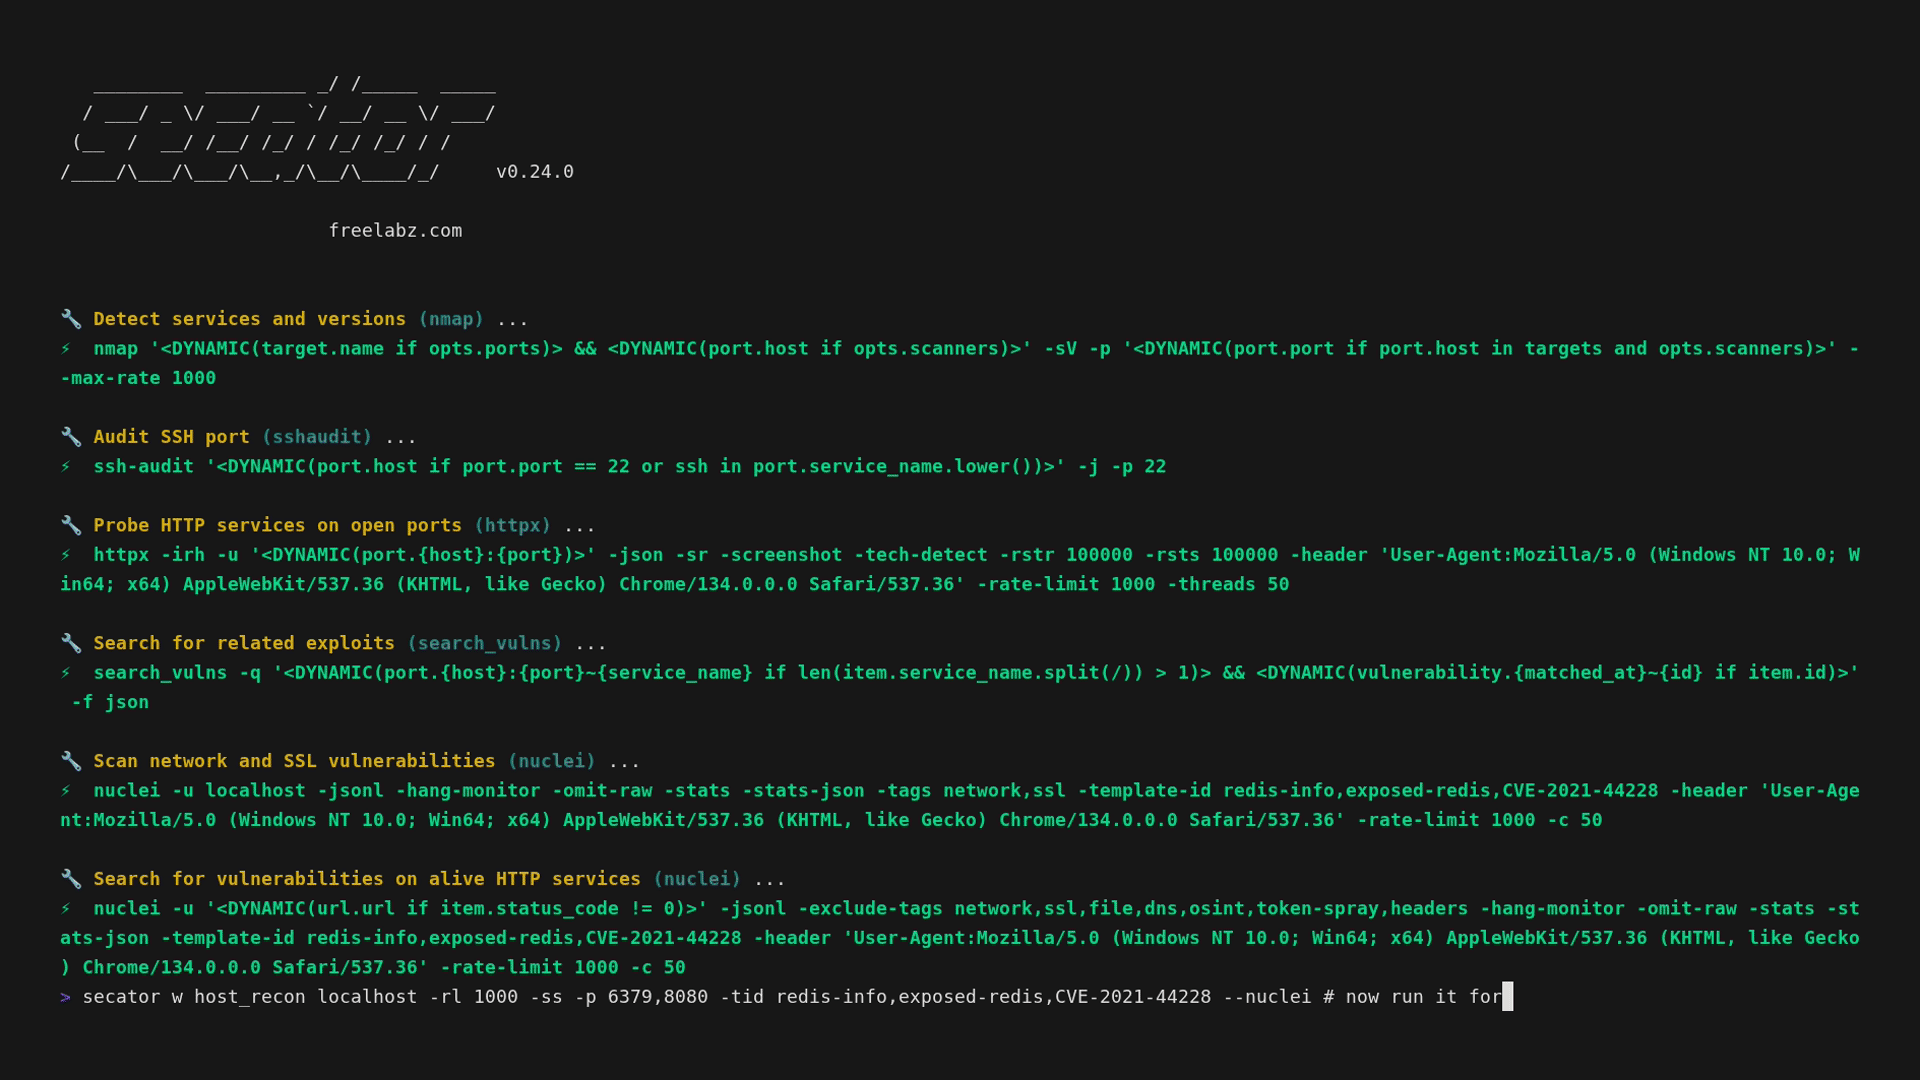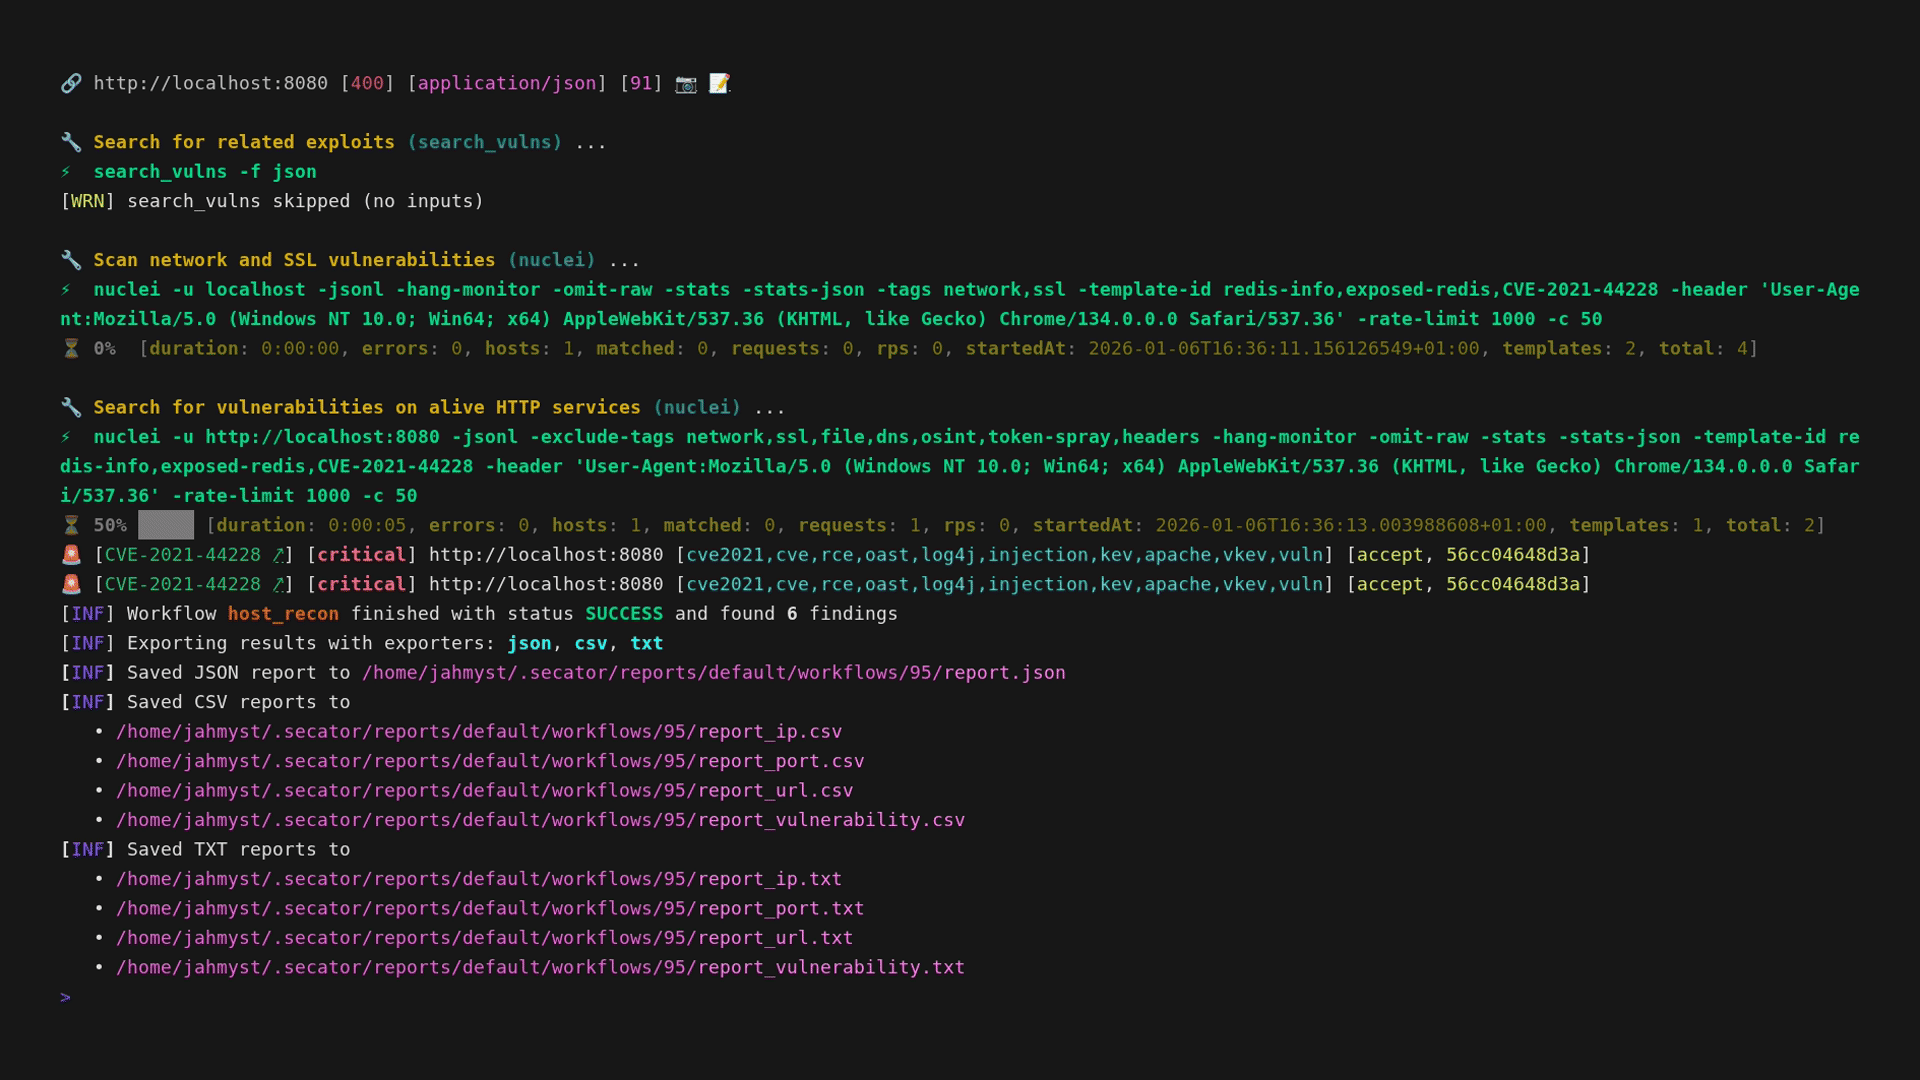
* **चुनी हुई कमांड की सूची**
* **एकीकृत इनपुट विकल्प**
* **एकीकृत आउटपुट स्कीमा**
* **CLI और लाइब्रेरी उपयोग**
* **Celery के साथ वितरित विकल्प**
* **सरल कार्यों से लेकर जटिल वर्कफ़्लो तक जटिलता**
* **अनुकूलन योग्य**
## समर्थित उपकरण
`secator` निम्नलिखित उपकरणों को एकीकृत करता है:
<!-- START_TOOLS_TABLE -->
| नाम | विवरण | श्रेणी |
|-----------------------------------------------------------------|----------------------------------------------------------------------------------|-------------------|
| [arjun](https://github.com/s0md3v/Arjun) | HTTP पैरामीटर डिस्कवरी सूट। | `url/fuzz/params` |
| arp | सिस्टम ARP कैश प्रदर्शित करें। | `ip/recon` |
| [arpscan](https://github.com/royhills/arp-scan) | ARP का उपयोग करके जीवित होस्ट के लिए CIDR रेंज स्कैन करें। | `ip/recon` |
| [bbot](https://github.com/blacklanternsecurity/bbot) | बहुउद्देशीय स्कैनर। | `vuln/scan` |
| [bup](https://github.com/laluka/bypass-url-parser) | 40X बाइपासर। | `url/bypass` |
| [cariddi](https://github.com/edoardottt/cariddi) | एंडपॉइंट, सीक्रेट, API कुंजी, एक्सटेंशन, टोकन क्रॉल करें... | `url/crawl` |
| [dalfox](https://github.com/hahwul/dalfox) | शक्तिशाली ओपन सोर्स XSS स्कैनिंग टूल। | `url/fuzz` |
| [dirsearch](https://github.com/maurosoria/dirsearch) | उन्नत वेब पथ ब्रूट-फोर्सर। | `url/fuzz` |
| [dnsx](https://github.com/projectdiscovery/dnsx) | dnsx एक तेज़ और बहुउद्देशीय DNS टूलकिट है जिसे विभिन्न retryabledns लाइब्रेरी चलाने के लिए डिज़ाइन किया गया है। | `dns/fuzz` |
| [feroxbuster](https://github.com/epi052/feroxbuster) | Rust में लिखा गया सरल, तेज़, पुनरावर्ती सामग्री डिस्कवरी टूल | `url/fuzz` |
| [ffuf](https://github.com/ffuf/ffuf) | Go में लिखा गया तेज़ वेब फ़ज़र। | `url/fuzz` |
| [fping](https://github.com/schweikert/fping) | नेटवर्क होस्ट को ICMP इको प्रोब भेजें, ping के समान, लेकिन बहुत बेहतर। | `ip/recon` |
| [gau](https://github.com/lc/gau) | AlienVault's Open Threat Exchange, Wayback Machine, Common Crawl, और URLScan से ज्ञात URL प्राप्त करें। | `pattern/scan` |
| [getasn](https://github.com/Vulnpire/getasn) | IP पते से ASN जानकारी प्राप्त करें। | `ip/probe` |
| [gf](https://github.com/tomnomnom/gf) | grep के चारों ओर रैपर, चीज़ों को grep करने में मदद करने के लिए। | `pattern/scan` |
| [gitleaks](https://github.com/gitleaks/gitleaks) | git रिपॉजिटरी, फ़ाइलों और stdin में पासवर्ड, API कुंजी और टोकन जैसे रहस्यों का पता लगाने का उपकरण। | `secret/scan` |
| [gospider](https://github.com/jaeles-project/gospider) | Go में लिखा गया तेज़ वेब स्पाइडर। | `url/crawl` |
| [grype](https://github.com/anchore/grype) | कंटेनर छवियों और फ़ाइल सिस्टम के लिए भेद्यता स्कैनर। | `vuln/scan` |
| [h8mail](https://github.com/khast3x/h8mail) | ईमेल जानकारी और पासवर्ड लुकअप टूल। | `user/recon/email` |
| [httpx](https://github.com/projectdiscovery/httpx) | तेज़ और बहुउद्देशीय HTTP टूलकिट। | `url/probe` |
| [jswhois](https://github.com/jschauma/jswhois) | JSON प्रारूप में WHOIS | `domain/info` |
| [katana](https://github.com/projectdiscovery/katana) | अगली पीढ़ी का क्रॉलिंग और स्पाइडरिंग फ्रेमवर्क। | `url/crawl` |
| [maigret](https://github.com/soxoj/maigret) | उपयोगकर्ता नाम से किसी व्यक्ति पर डोजियर एकत्र करें। | `user/recon/username` |
| [mapcidr](https://github.com/projectdiscovery/mapcidr) | दिए गए सबनेट/CIDR रेंज के लिए कई ऑपरेशन करने की उपयोगिता प्रोग्राम। | `ip/recon` |
| [msfconsole](https://docs.rapid7.com/metasploit/msf-overview/) | Metasploit Framework तक पहुँचने और उसके साथ काम करने के लिए CLI। | `exploit/attack` |
| [naabu](https://github.com/projectdiscovery/naabu) | Go में लिखा गया पोर्ट स्कैनिंग टूल। | `port/scan` |
| [nmap](https://github.com/nmap/nmap) | Network Mapper एक मुफ़्त और ओपन सोर्स उपयोगिता है नेटवर्क डिस्कवरी और सुरक्षा ऑडिटिंग के लिए। | `port/scan` |
| [nuclei](https://github.com/projectdiscovery/nuclei) | सरल YAML आधारित DSL पर आधारित तेज़ और अनुकूलन योग्य भेद्यता स्कैनर। | `vuln/scan` |
| [search_vulns](https://github.com/ra1nb0rn/search_vulns) | उत्पाद नाम या CPE द्वारा सॉफ़्टवेयर में ज्ञात भेद्यताओं की खोज करें। | `vuln/recon` |
| [searchsploit](https://gitlab.com/exploit-database/exploitdb) | ExploitDB पर आधारित एक्सप्लॉइट खोजक। | `exploit/recon` |
| [sshaudit](https://github.com/jtesta/ssh-audit) | SSH सर्वर और क्लाइंट सुरक्षा ऑडिटिंग (बैनर, की एक्सचेंज, एन्क्रिप्शन, मैक, कम्प्रेशन, आदि)। | `ssh/audit/security` |
| [subfinder](https://github.com/projectdiscovery/subfinder) | तेज़ निष्क्रिय उपडोमेन गणना उपकरण। | `dns/recon` |
| [testssl](https://github.com/testssl/testssl.sh) | SSL/TLS सुरक्षा स्कैनर, सिफर, प्रोटोकॉल और क्रिप्टोग्राफ़िक दोषों सहित। | `dns/recon/tls` |
| [trivy](https://github.com/aquasecurity/trivy) | व्यापक और बहुमुखी सुरक्षा स्कैनर। | `vuln/scan` |
| [trufflehog](https://github.com/trufflesecurity/trufflehog) | TruffleHog का उपयोग करके git रिपॉजिटरी और फ़ाइल सिस्टम में रहस्य खोजने का उपकरण। | `secret/scan` |
| [urlfinder](https://github.com/projectdiscovery/urlfinder) | पाठ में URL खोजें। | `pattern/scan` |
| [wafw00f](https://github.com/EnableSecurity/wafw00f) | वेब एप्लिकेशन फ़ायरवॉल फ़िंगरप्रिंटिंग टूल। | `waf/scan` |
| [whois](https://github.com/mboot-github/WhoisDomain) | whois उपकरण डोमेन नाम और IP पतों के बारे में पंजीकरण जानकारी प्राप्त करता है। | |
| [wpprobe](https://github.com/Chocapikk/wpprobe) | तेज़ वर्डप्रेस प्लगइन गणना उपकरण। | `vuln/scan/wordpress` |
| [wpscan](https://github.com/wpscanteam/wpscan) | वर्डप्रेस सुरक्षा स्कैनर। | `vuln/scan/wordpress` |
| [x8](https://github.com/Sh1Yo/x8) | Rust में लिखा गया हिडन पैरामीटर डिस्कवरी सूट। | `url/fuzz/params` |
| [xurlfind3r](https://github.com/hueristiq/xurlfind3r) | किसी दिए गए डोमेन के लिए URL को सरल, निष्क्रिय और कुशल तरीके से खोजें | `url/recon` |
<!-- END_TOOLS_TABLE -->
बेझिझक एक इश्यू खोलकर नए टूल जोड़ने का अनुरोध करें, लेकिन कृपया ऐसा करने से पहले जाँच लें कि टूल हमारे चयन मानदंडों का पालन करता है। यदि ऐसा नहीं होता है लेकिन फिर भी आप इसे `secator` में एकीकृत करना चाहते हैं, तो आप इसे प्लग इन कर सकते हैं (देखें [डेव गाइड](https://docs.freelabz.com/for-developers/writing-custom-tasks))।
## secator स्थापित करना
<details>
<summary>Bash</summary>
```sh
bash -c "$(curl -fsSL https://raw.githubusercontent.com/freelabz/secator/main/scripts/install_universal.sh)"
```
***नोट:** वैकल्पिक फ़्लैग `--version`, `--templates`, `--addons`, और `--tools` का समर्थन करता है — विवरण के लिए स्क्रिप्ट को `--help` के साथ चलाएँ।*
</details>
<details>
<summary>Pipx</summary>
```sh
pipx install secator
```
***नोट:** सुनिश्चित करें कि [pipx](https://pipx.pypa.io/stable/installation/) स्थापित है।*
</details>
<details>
<summary>Pip</summary>
```sh
pip install secator
```
</details>
<details>
<summary>Docker</summary>
```sh
docker run -it --rm --net=host -v ~/.secator:/root/.secator freelabz/secator --help
```
वॉल्यूम माउंट -v आपकी होस्ट मशीन पर सभी secator रिपोर्ट सहेजने के लिए आवश्यक है, और--net=host होस्ट नेटवर्क तक पूर्ण पहुंच देने के लिए अनुशंसित है।
आप इस कमांड को आसानी से चलाने के लिए alias बना सकते हैं:
```sh
alias secator="docker run -it --rm --net=host -v ~/.secator:/root/.secator freelabz/secator"
```
अब आप secator को ऐसे चला सकते हैं जैसे कि यह baremetal पर स्थापित हो:
```
secator --help
```
</details>
<details>
<summary>Docker Compose</summary>
```sh
git clone https://github.com/freelabz/secator
cd secator
docker-compose up -d
docker-compose exec secator-client secator --help
```
</details>
***नोट:*** यदि आपने Docker या Docker Compose स्थापना विधियाँ चुनी हैं, तो आप अगले अनुभाग छोड़ सकते हैं और सीधे [Usage](#usage) पर जा सकते हैं।
## उपयोग
```sh
secator --help
```
### उपयोग उदाहरण
`secator` के साथ आप क्या कर सकते हैं इसकी पूरी चीटशीट प्राप्त करने के लिए, कृपया इसका आउटपुट पढ़ें:
```sh
secator cheatsheet
```
फ़ज़िंग कार्य चलाएँ (`ffuf`):
```sh
secator x ffuf http://testphp.vulnweb.com/FUZZ
```
URL क्रॉल वर्कफ़्लो चलाएँ:
```sh
secator w url_crawl http://testphp.vulnweb.com
```
होस्ट स्कैन चलाएँ:
```sh
secator s host mydomain.com
```
आपके द्वारा उपयोग किए जा सकने वाले सभी कार्य / वर्कफ़्लो / स्कैन सूचीबद्ध करने के लिए:
```sh
secator x --help
secator w --help
secator s --help
```
यह पता लगाने के लिए कि आपके सिस्टम पर कौन सी भाषाएँ या उपकरण स्थापित हैं (उनके संस्करण के साथ):
```sh
secator health
```
### क्वेरीज़
`secator` आपको `secator query` (या `secator q`) कमांड के साथ सभी पिछली रिपोर्टों को क्वेरी करने और क्वेरीज़ का पुन: उपयोग करने देता है।
`secator q <arg>` अपने तर्क को तीन चरणों में हल करता है:
1. **सहेजी गई क्वेरी नाम** — यदि `<arg>` किसी सहेजी गई क्वेरी से मेल खाता है, तो उसकी अभिव्यक्ति का उपयोग किया जाता है।
2. **फ़िल्टर अभिव्यक्ति** — यदि `<arg>` फ़िल्टर जैसा दिखता है (इसमें `==`, `<`, `~=`, `&&`, … शामिल हैं), तो इसे सीधे पारित किया जाता है।
3. **प्राकृतिक भाषा** — अन्यथा इसे AI चैट पर भेजा जाता है (`secator x ai --mode chat`)।
```sh
# Run raw expressions directly
secator q "vulnerability.tags ~= 'kev' && vulnerability.confidence == 'high'" # vulns KEV (Known-Exploited Vulnerabilities) + high confidence
secator q "vulnerability.severity == 'critical' && vulnerability.tags ~= 'exploitable' && vulnerability.confidence == 'high'" # vulns critical + exploitable + high confidence
secator q "vulnerability.severity_nb < 2 && vulnerability.confidence == 'high'" # vulns severity > high + high confidence
secator q "exploit.cves ~= 'CVE-2021-44521'" # exploits found for vuln CVE-2021-44521
secator q "port" -f "{host} {port} {service_name}" | cut -d " " -f2 | sort | uniq -c | sort -nr | head -n 15 # top 15 ports
secator q "port" -f "{host} {port} {service_name}" | cut -d " " -f3,4,5,6 | awk 'NF > 0' | sort | uniq -c | sort -nr | head -n 15 # top 15 services
secator q "technology" -f "{product}/{version}" | sort | uniq -c | sort -nr | head -n 15 # top 15 technologies
secator q "port.state == 'open'" -rf scans/23,tasks/10 # only results from scan 23 and task 10
# Save a query and run it
secator c set queries.critical_vulns "vulnerability.severity_nb < 2" # save a query
secator c get queries # list saved queries
secator q critical_vulns -f "{vulnerability.matched_at}" -ws secator.cloud # run a saved query on workspace + extract targets
# Ask a natural-language question (runs the AI chat task)
secator q "Analyze my workspace data"
```
`secator q` वही विकल्प स्वीकार करता है जो `secator r show` (`-o/--output`,
`-d/--time-delta`, `-f/--format`, `-w/-ws/--workspace`, `--driver`, `--dedupe`),
साथ ही `-rf/--report-filter` क्वेरी को विशिष्ट रनर पथों तक सीमित करने के लिए (जो
`r show` के `REPORT_QUERY` तर्क के बराबर है)। AI-चैट पथ पर केवल कार्यक्षेत्र और संकेत का उपयोग किया जाता है।
### शेल पूर्णता
`secator` bash, zsh, और fish के लिए शेल पूर्णता का समर्थन करता है। यह निम्न के लिए ऑटो-पूर्णता प्रदान करता है:
- कार्य नाम (जैसे, `nmap`, `httpx`, `nuclei`)
- वर्कफ़्लो नाम (जैसे, `url_crawl`, `subdomain_recon`)
- स्कैन नाम (जैसे, `host`, `domain`, `network`)
- CLI विकल्प जैसे `--profiles`, `--workspace`, `--driver`, `--output`
शेल पूर्णता स्थापित करने के लिए:
**Bash:**
```sh
secator util completion --shell bash --install
source ~/.bashrc
```
**Zsh:**
```sh
secator util completion --shell zsh --install
source ~/.zshrc
```
**Fish:**
```sh
secator util completion --shell fish --install
```
स्थापना के बाद, आप टैब पूर्णता का उपयोग कर सकते हैं:
```sh
secator x n<TAB> # completes to nmap, naabu, nuclei, etc.
secator w url_<TAB> # completes to url_crawl, url_fuzz, url_dirsearch, etc.
secator x nmap --profiles ag<TAB> # completes to aggressive
```
## उपकरण स्थापित करना
`secator` जब आप पहली बार उपकरणों का उपयोग करते हैं तो वे स्वचालित रूप से स्थापित हो जाते हैं।
आप `secator config set security.autoinstall_commands false` या `SECATOR_SECURITY_AUTOINSTALL_COMMANDS=0` का उपयोग करके `security.autoinstall_commands` को `false` सेट करके इस व्यवहार को रोक सकते हैं।
सभी उपकरणों को स्थापित करने के लिए, आप अभी भी चला सकते हैं:
```sh
secator install tools
```
## ऐडऑन स्थापित करना
`secator` के लिए ऐडऑन उपलब्ध हैं, कृपया विवरण के लिए [हमारे दस्तावेज़](https://docs.freelabz.com/getting-started/installation#installing-addons-optional) देखें।
उदाहरण के लिए, `mongodb` ऐडऑन का उपयोग करके आप रनर परिणाम MongoDB को भेज सकते हैं।
## और जानें
`secator` के साथ गहराई में जाने के लिए, देखें:
* हमारा संपूर्ण [दस्तावेज़ीकरण](https://docs.freelabz.com)
* हमारा आरंभिक [ट्यूटोरियल वीडियो](https://youtu.be/-JmUTNWQDTQ?si=qpAClDWMXo2zwUK7)
* हमारा [Medium पोस्ट](https://medium.com/p/09333f3d3682)
* सोशल मीडिया पर हमें फॉलो करें: Twitter पर [@freelabz](https://twitter.com/freelabz) और YouTube पर [@FreeLabz](https://youtube.com/@FreeLabz)
## आंकड़े
<a href="https://star-history.com/#freelabz/secator&Date">
<picture>
<source media="(prefers-color-scheme: dark)" srcset="https://api.star-history.com/svg?repos=freelabz/secator&type=Date&theme=dark" />
<source media="(prefers-color-scheme: light)" srcset="https://api.star-history.com/svg?repos=freelabz/secator&type=Date" />
<img alt="Star History Chart" src="https://api.star-history.com/svg?repos=freelabz/secator&type=Date" />
</picture>
</a>