 fr0gger/iatelligence
IATelligence एक Python स्क्रिप्ट है जो PE फ़ाइल का IAT निकालेगी और API तथा संबंधित ATT&CK मैट्रिक्स के बारे में अधिक जानकारी प्राप्त करने के लिए GPT से अनुरोध करेगी।

IATelligence एक Python स्क्रिप्ट है जो PE फ़ाइल से Import Address Table (IAT) निकालती है और फ़ाइल द्वारा आयात किए गए प्रत्येक Windows API के बारे में विवरण प्रदान करने के लिए OpenAI के GPT-3 मॉडल का उपयोग करती है। यह स्क्रिप्ट संबंधित MITRE ATT&CK तकनीकों की भी खोज करती है और बताती है कि API का उपयोग हमलावरों द्वारा संभावित रूप से कैसे किया जा सकता है।
यह फ़ाइल के हैश भी प्रदर्शित करती है और GPT-3 अनुरोधों की लागत का अनुमान लगाती है। IATelligence, मैलवेयर विश्लेषण के लिए GPT-3 का उपयोग करने और उसके IAT के आधार पर मैलवेयर के व्यवहार का त्वरित आकलन करने के लिए एक proof of concept है।
नीचे आपको मिलने वाले परिणाम का एक त्वरित उदाहरण है। ध्यान दें कि IAT के आकार के आधार पर अनुरोध में अधिक समय लग सकता है।
इस टूल को चलाने के लिए आपको OpenAi API तक पहुँच की आवश्यकता होगी, फिर आपको अपनी स्वयं की API जोड़ने के लिए स्क्रिप्ट को संशोधित करना होगा।
# Authenticate with the OpenAI API
openai.api_key = ""
आपको requirements भी इंस्टॉल करनी होंगी।
pip install -r requirements.txt
टूल को चलाने के लिए बस स्क्रिप्ट के तर्क के रूप में एक PE फ़ाइल निर्दिष्ट करें।
python iatelligence.py sample.exe
स्क्रिप्ट हैश के साथ-साथ अनुरोध की अनुमानित लागत की भी गणना करेगी।
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
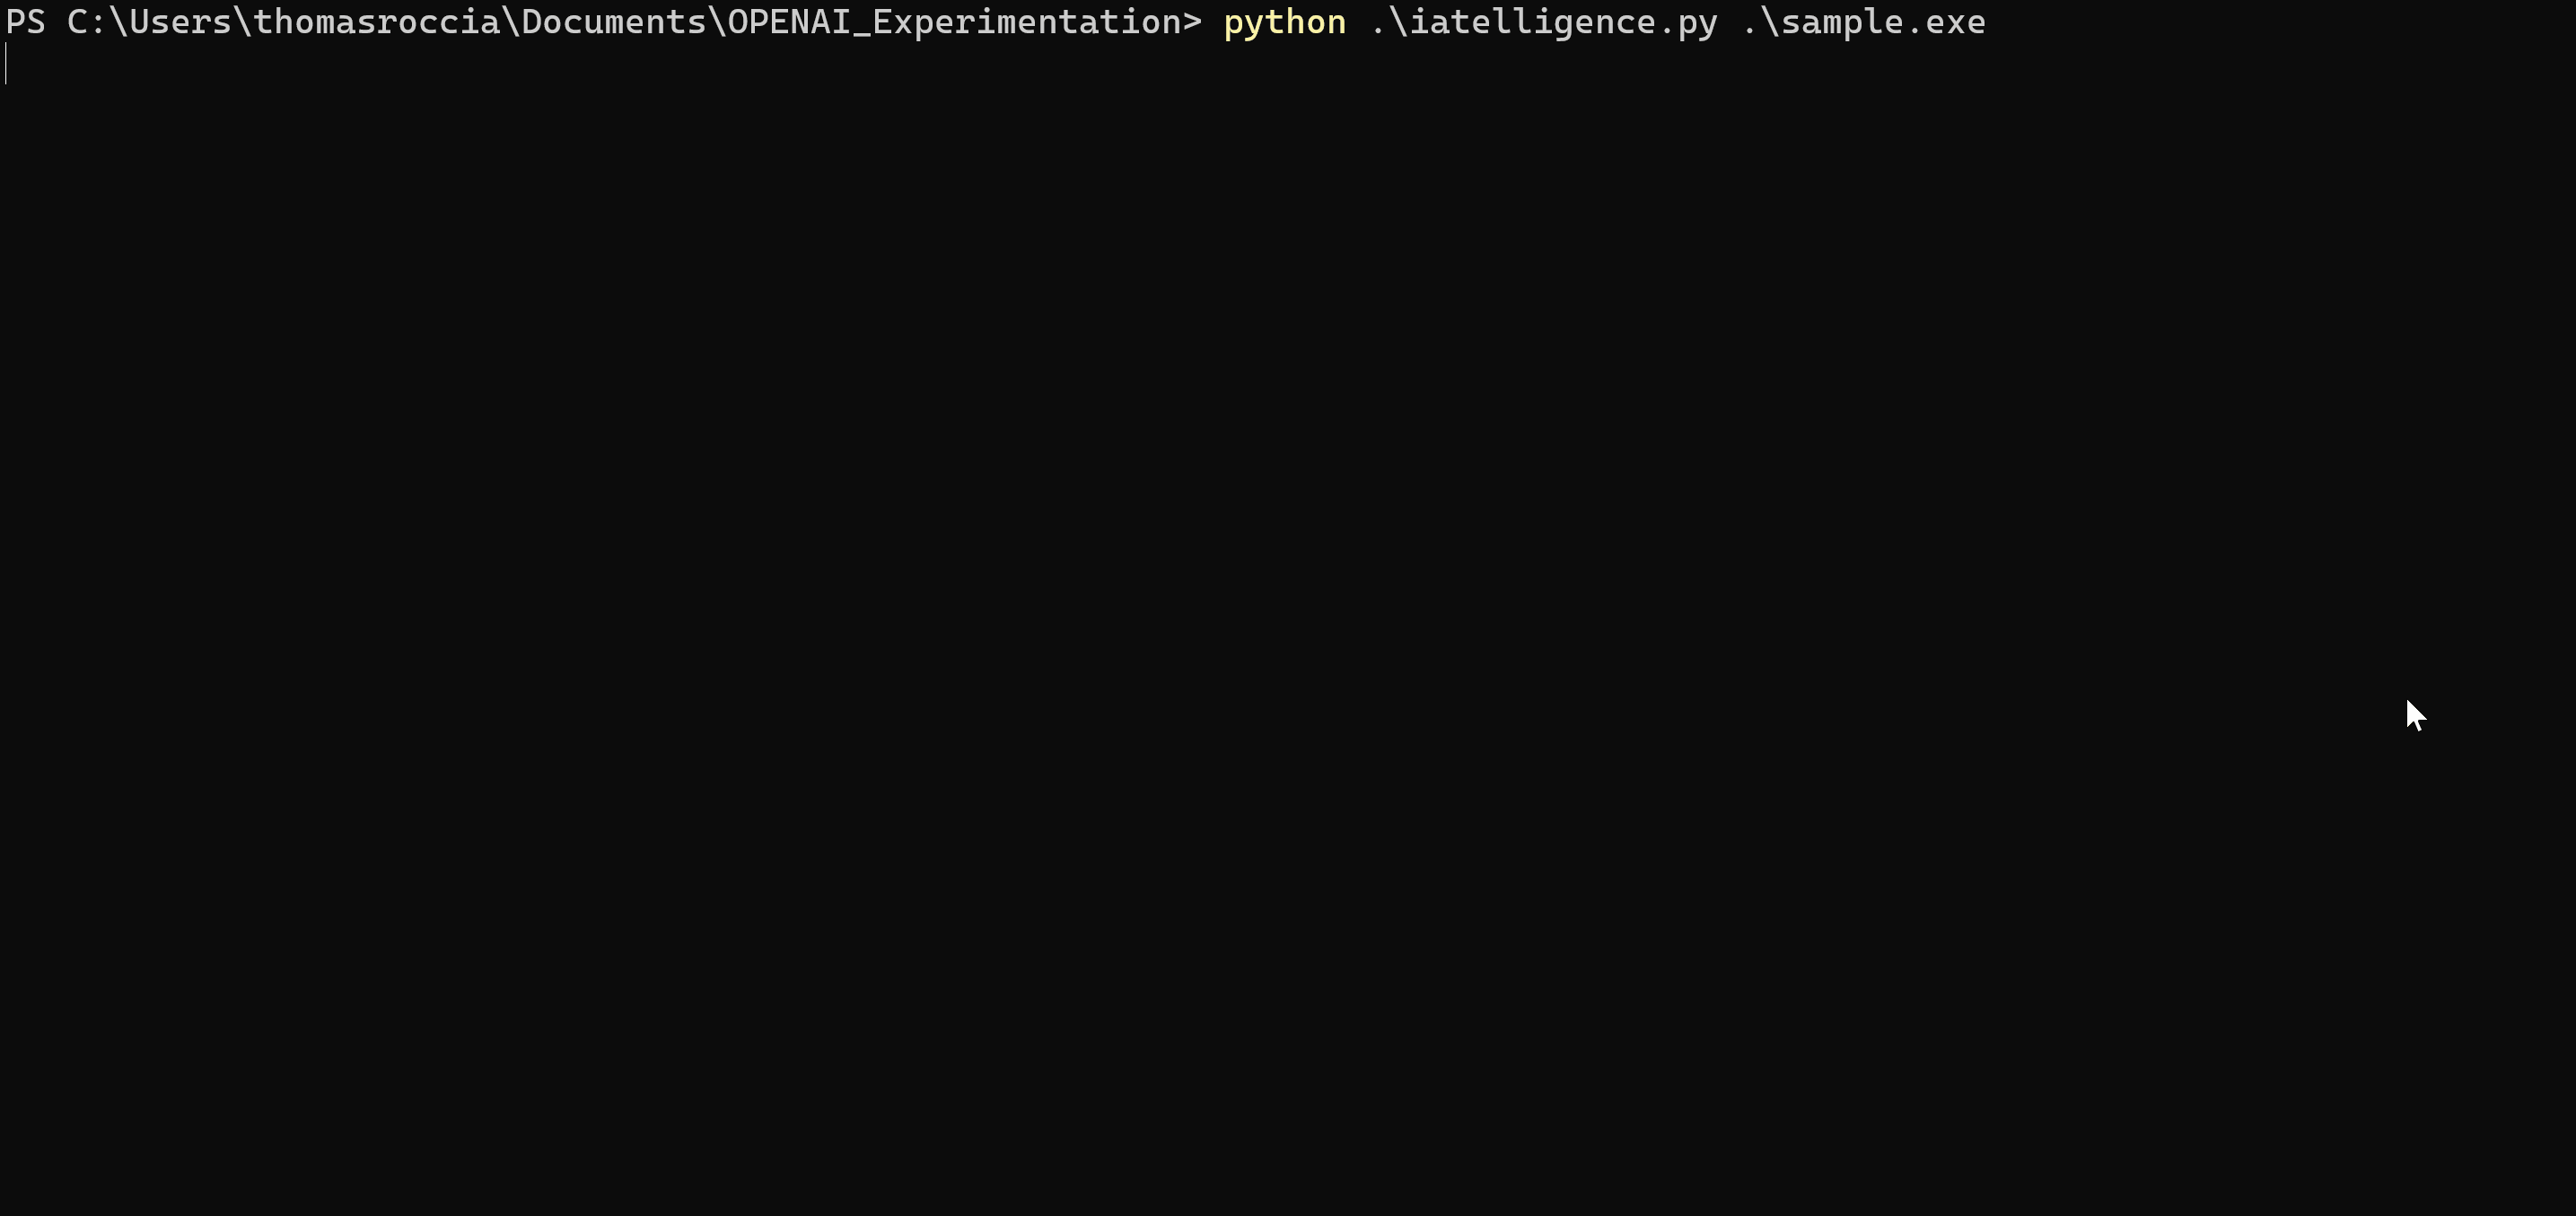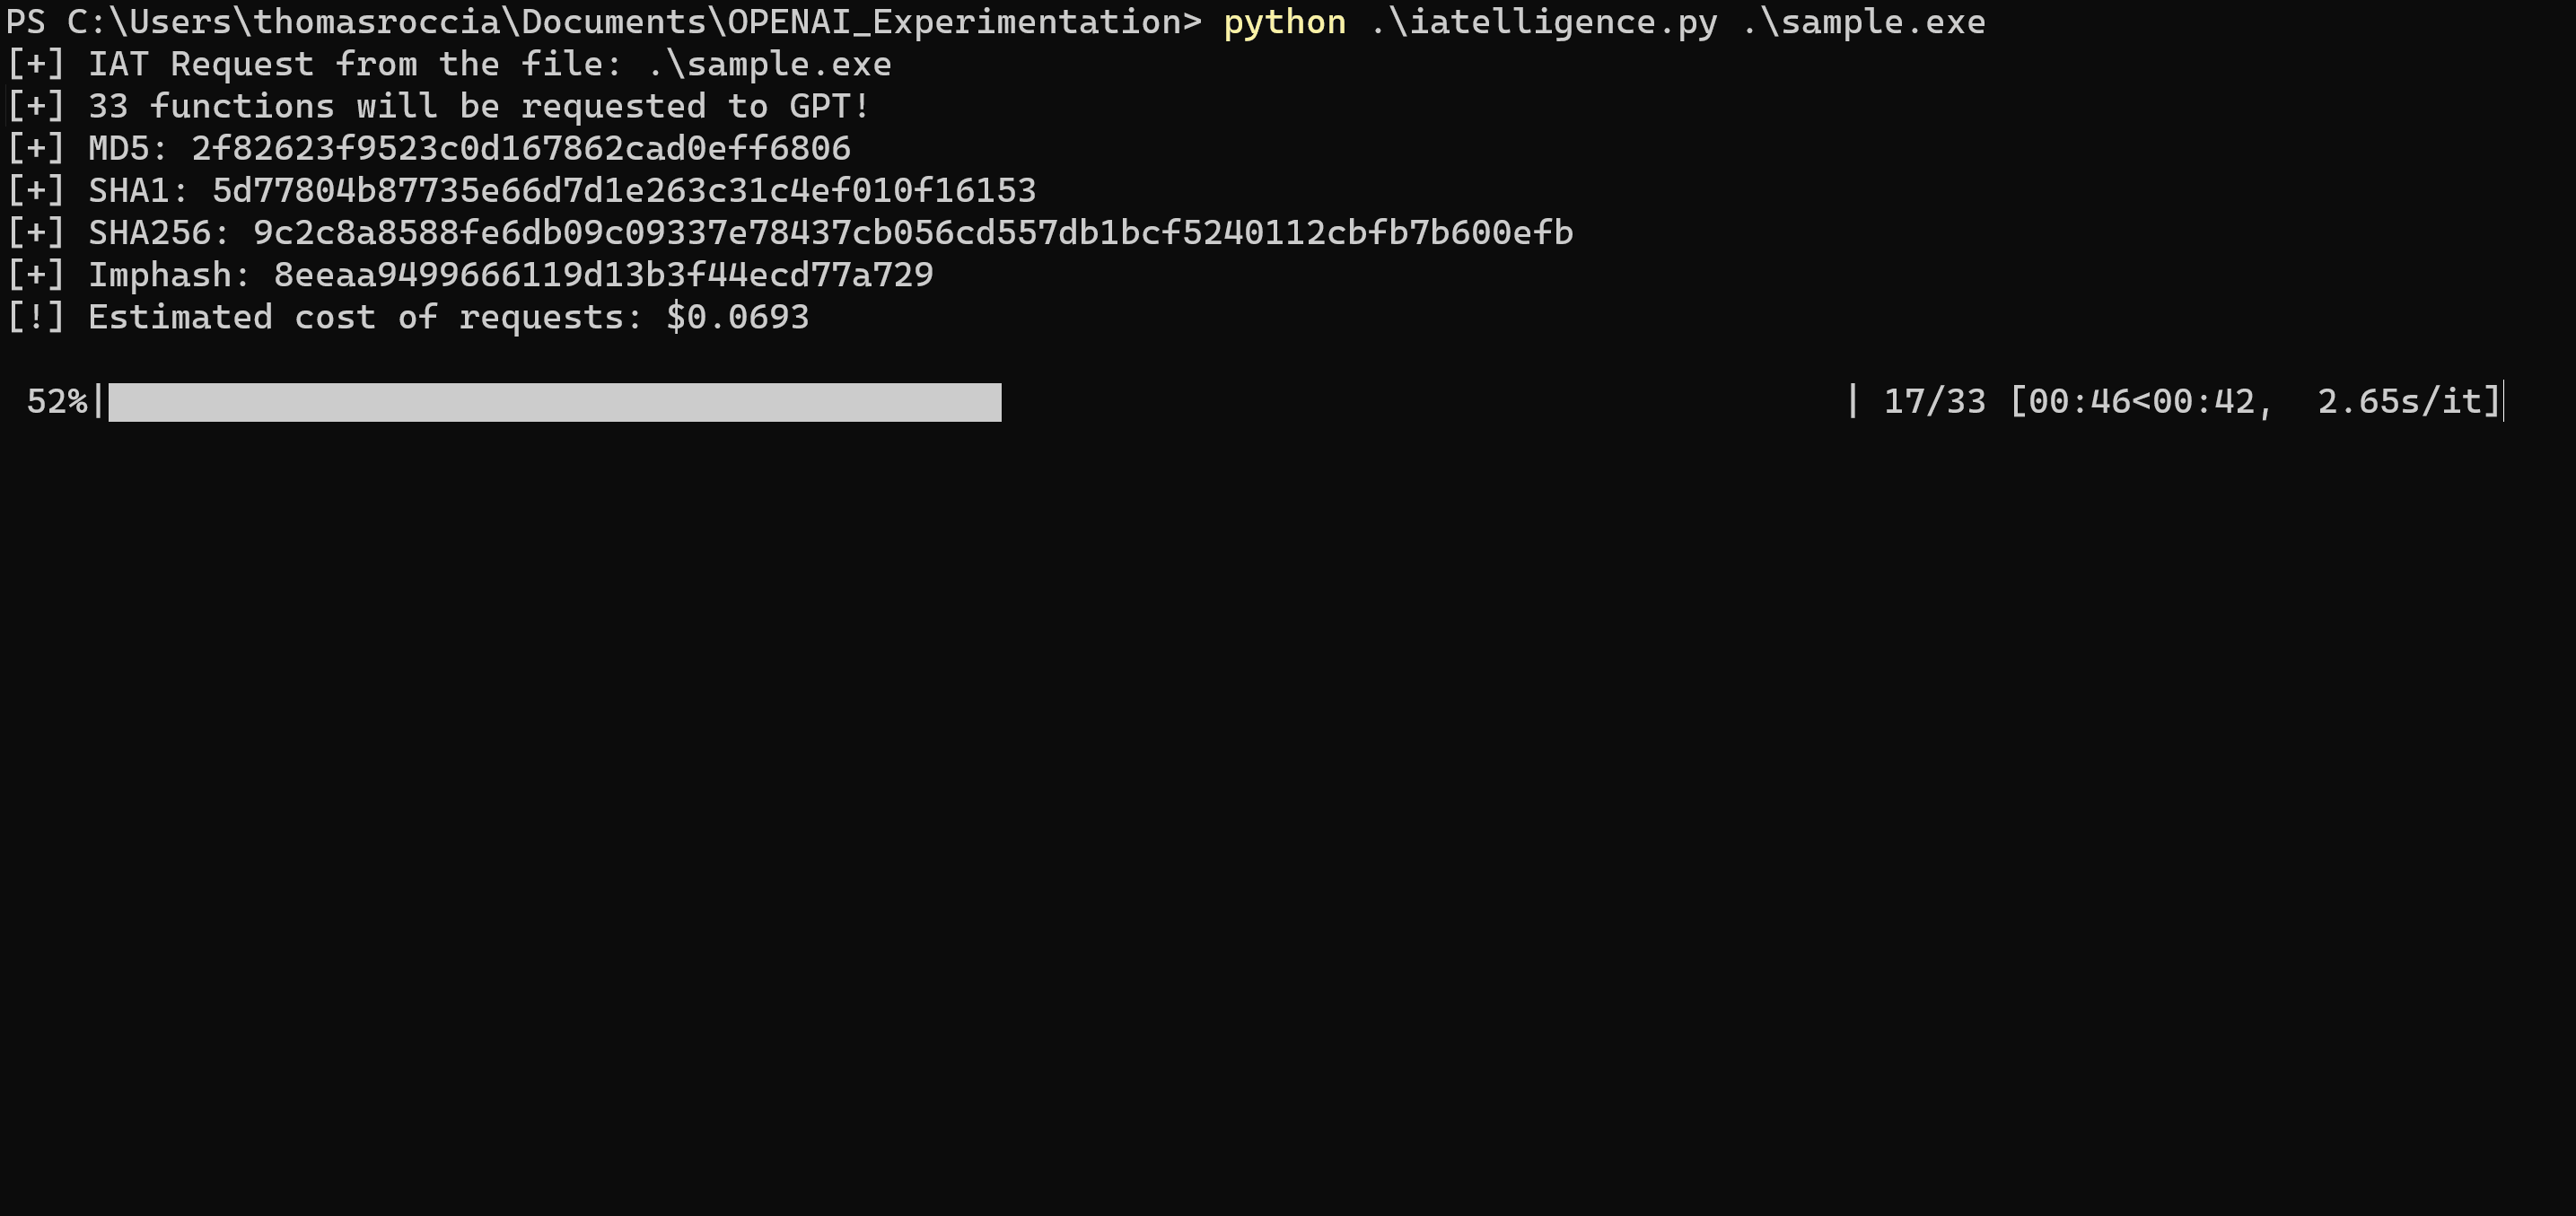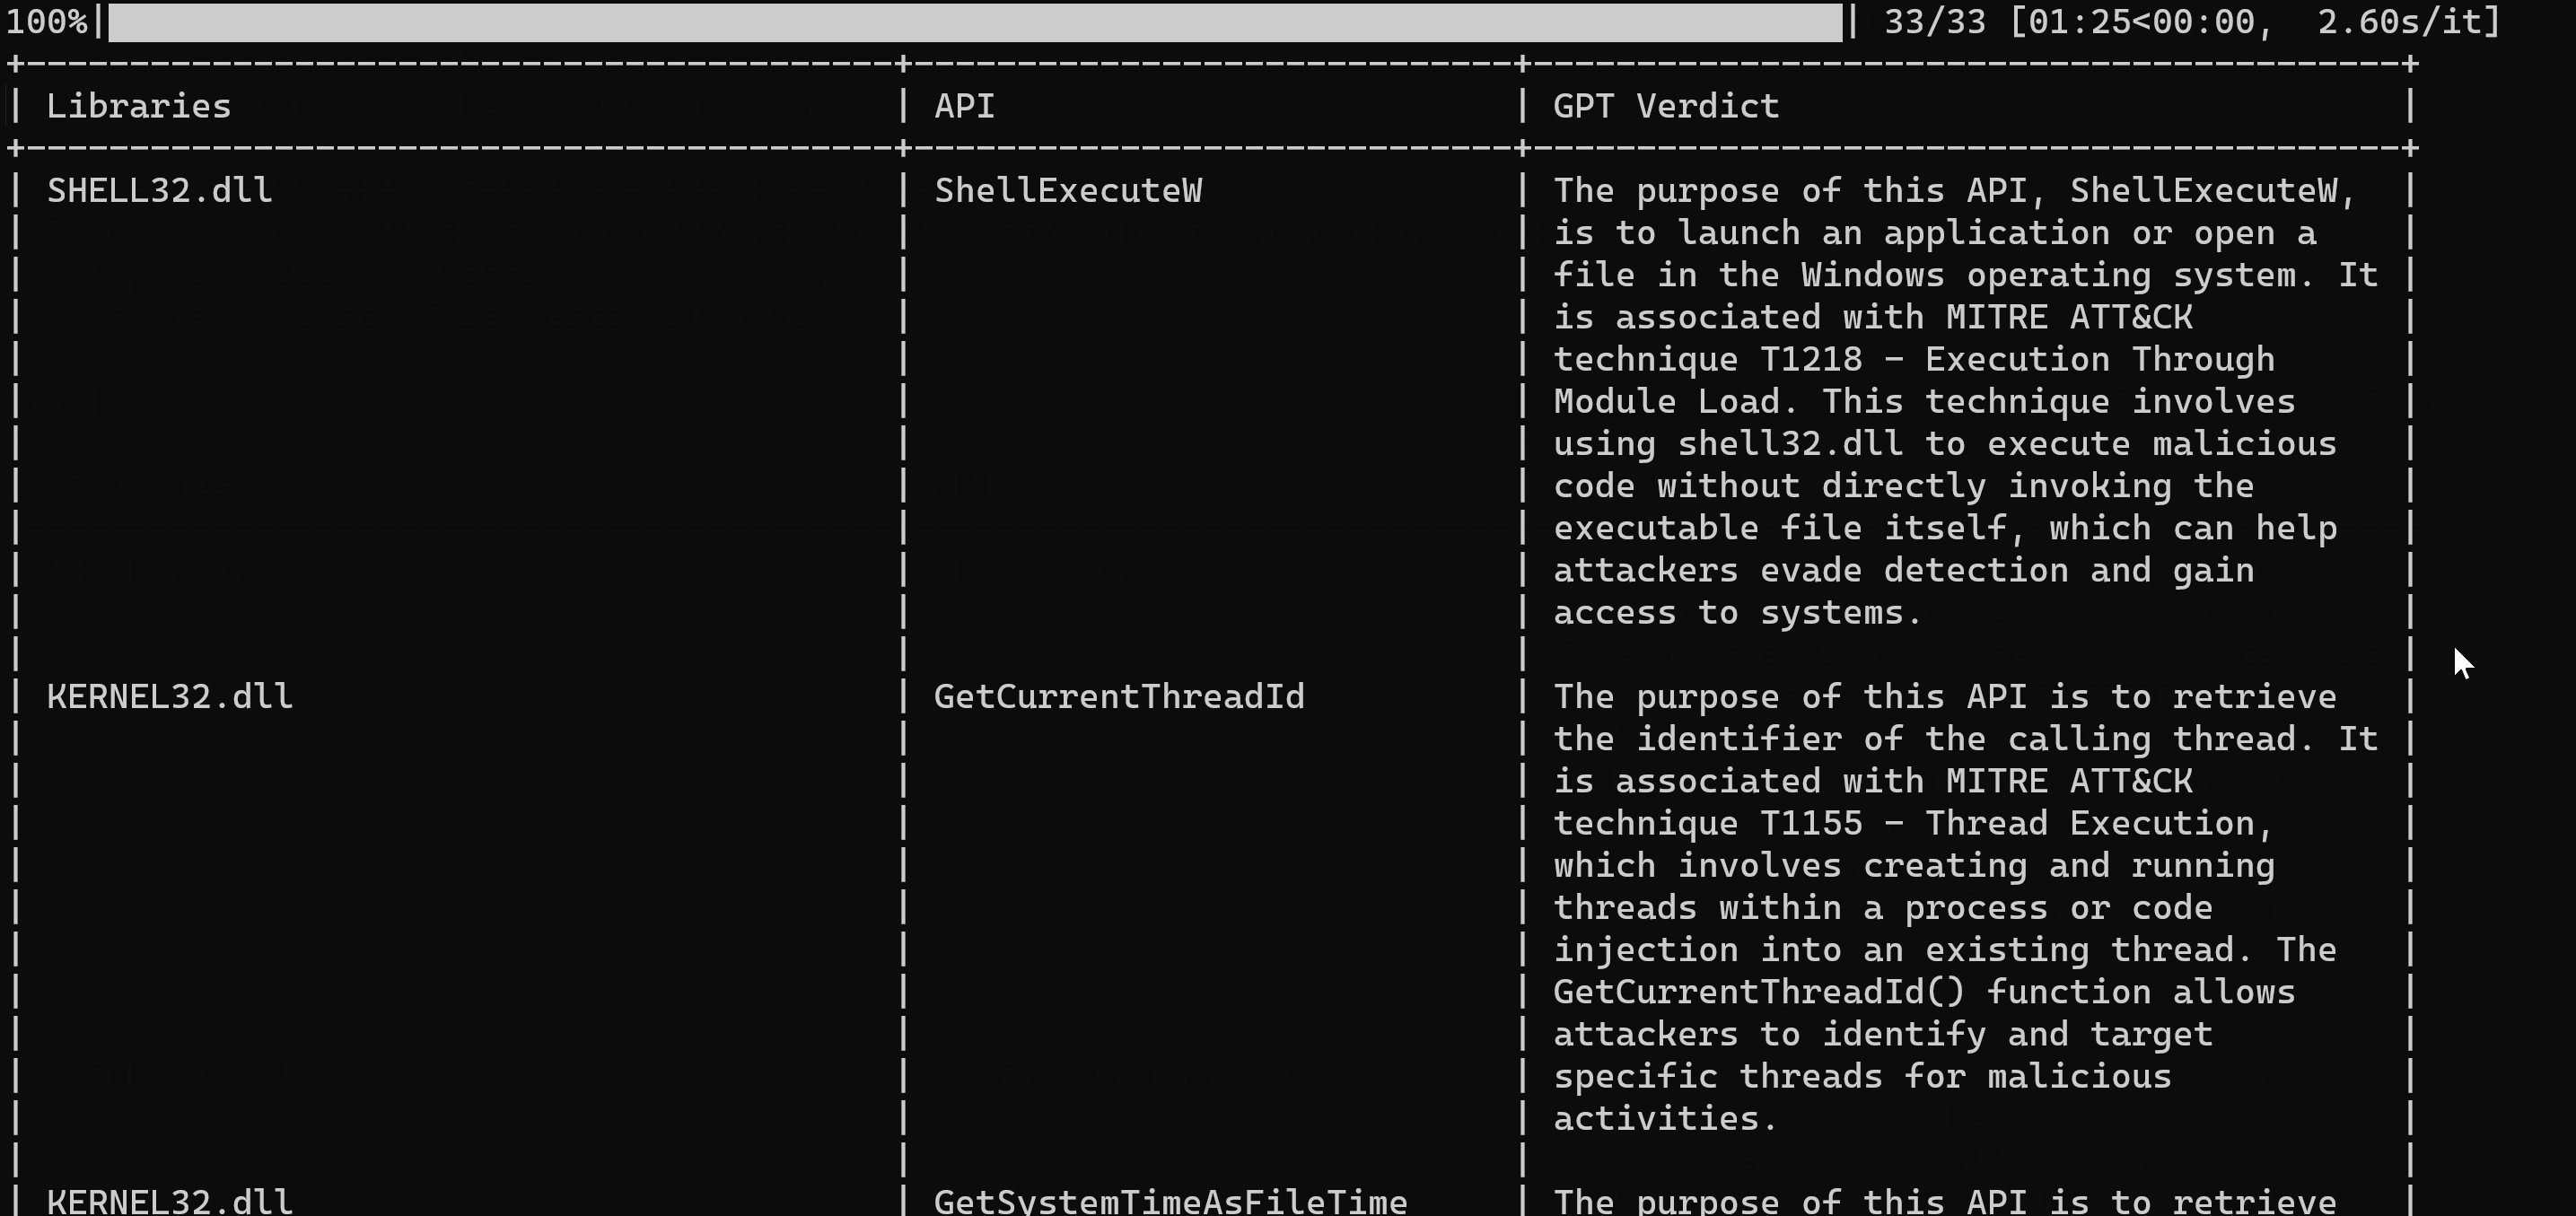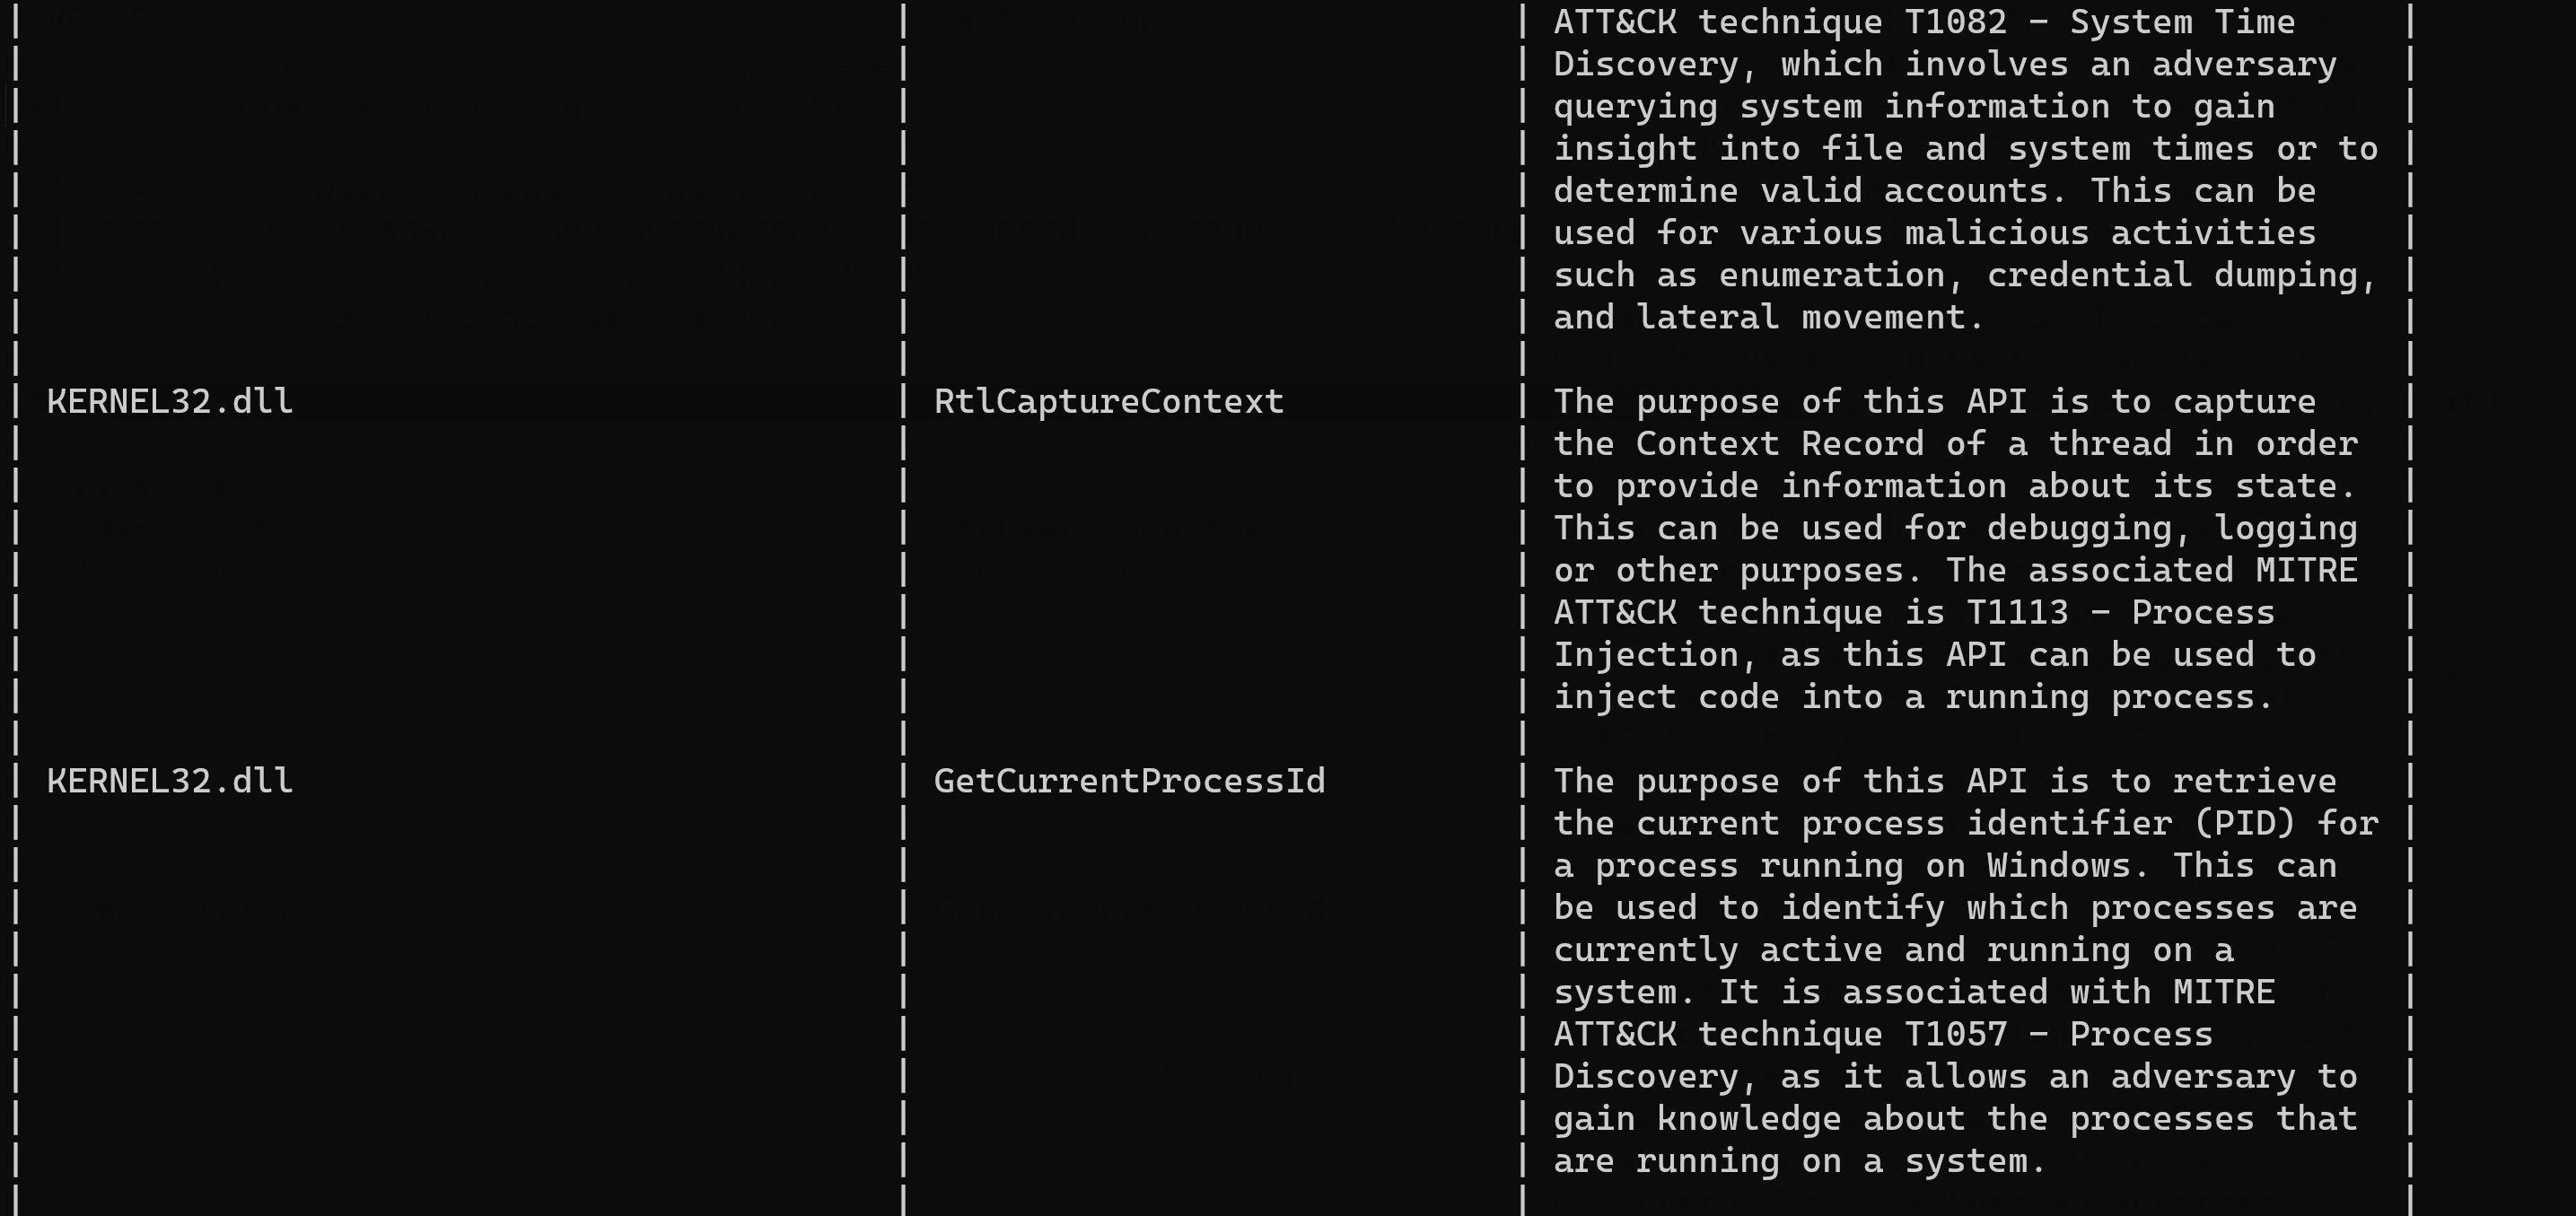
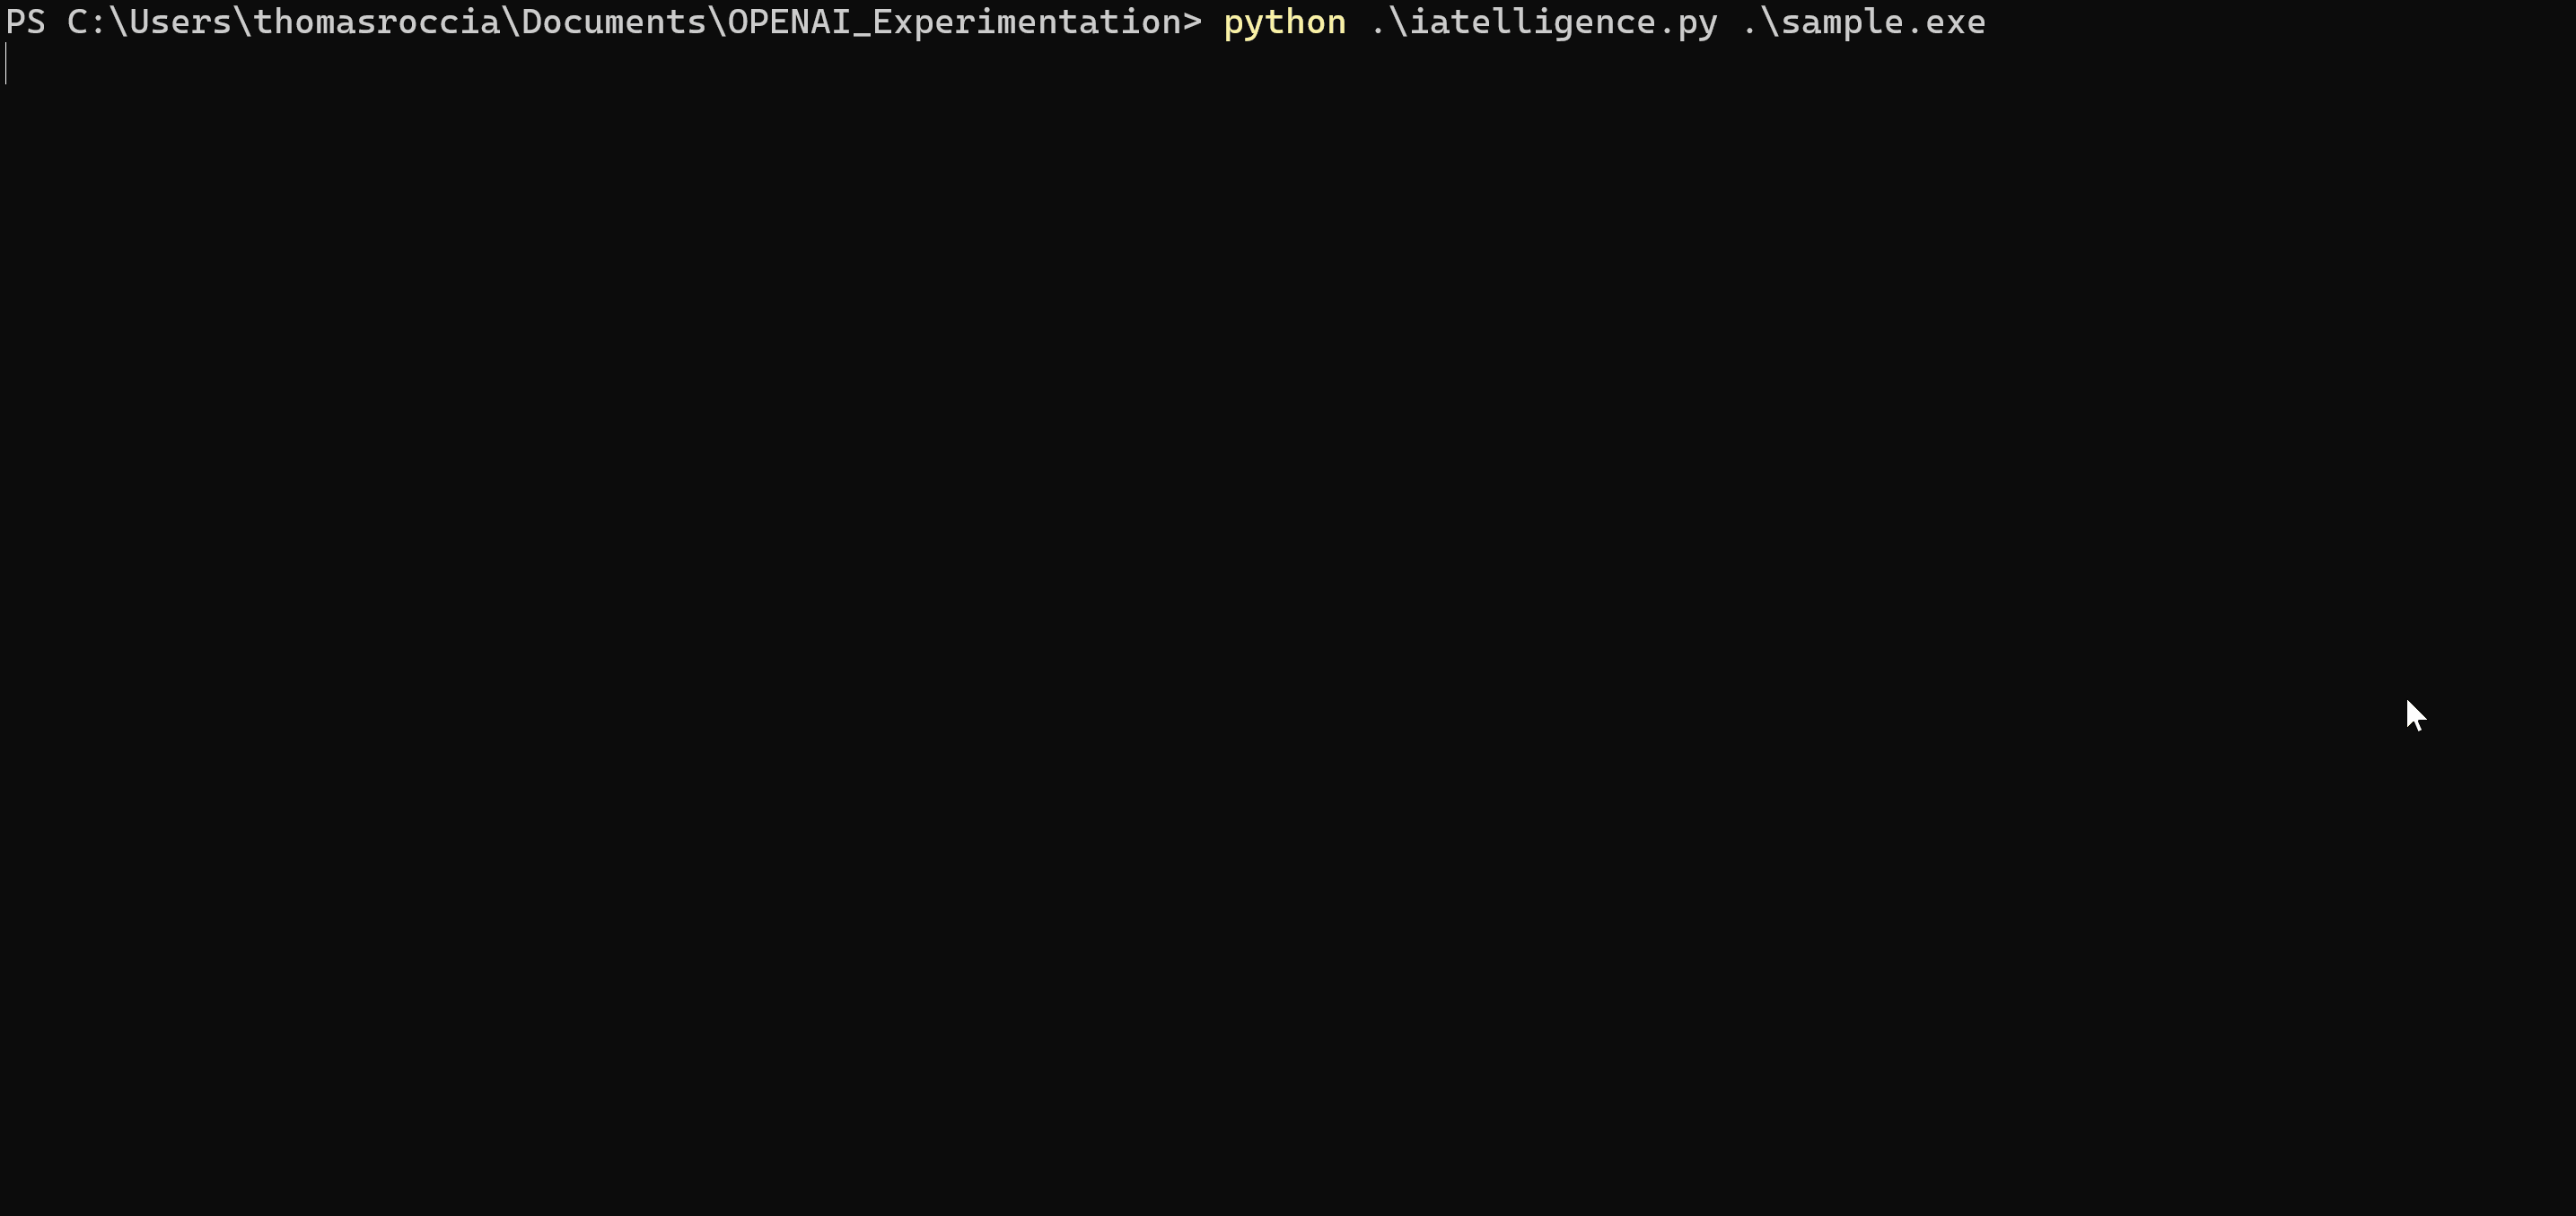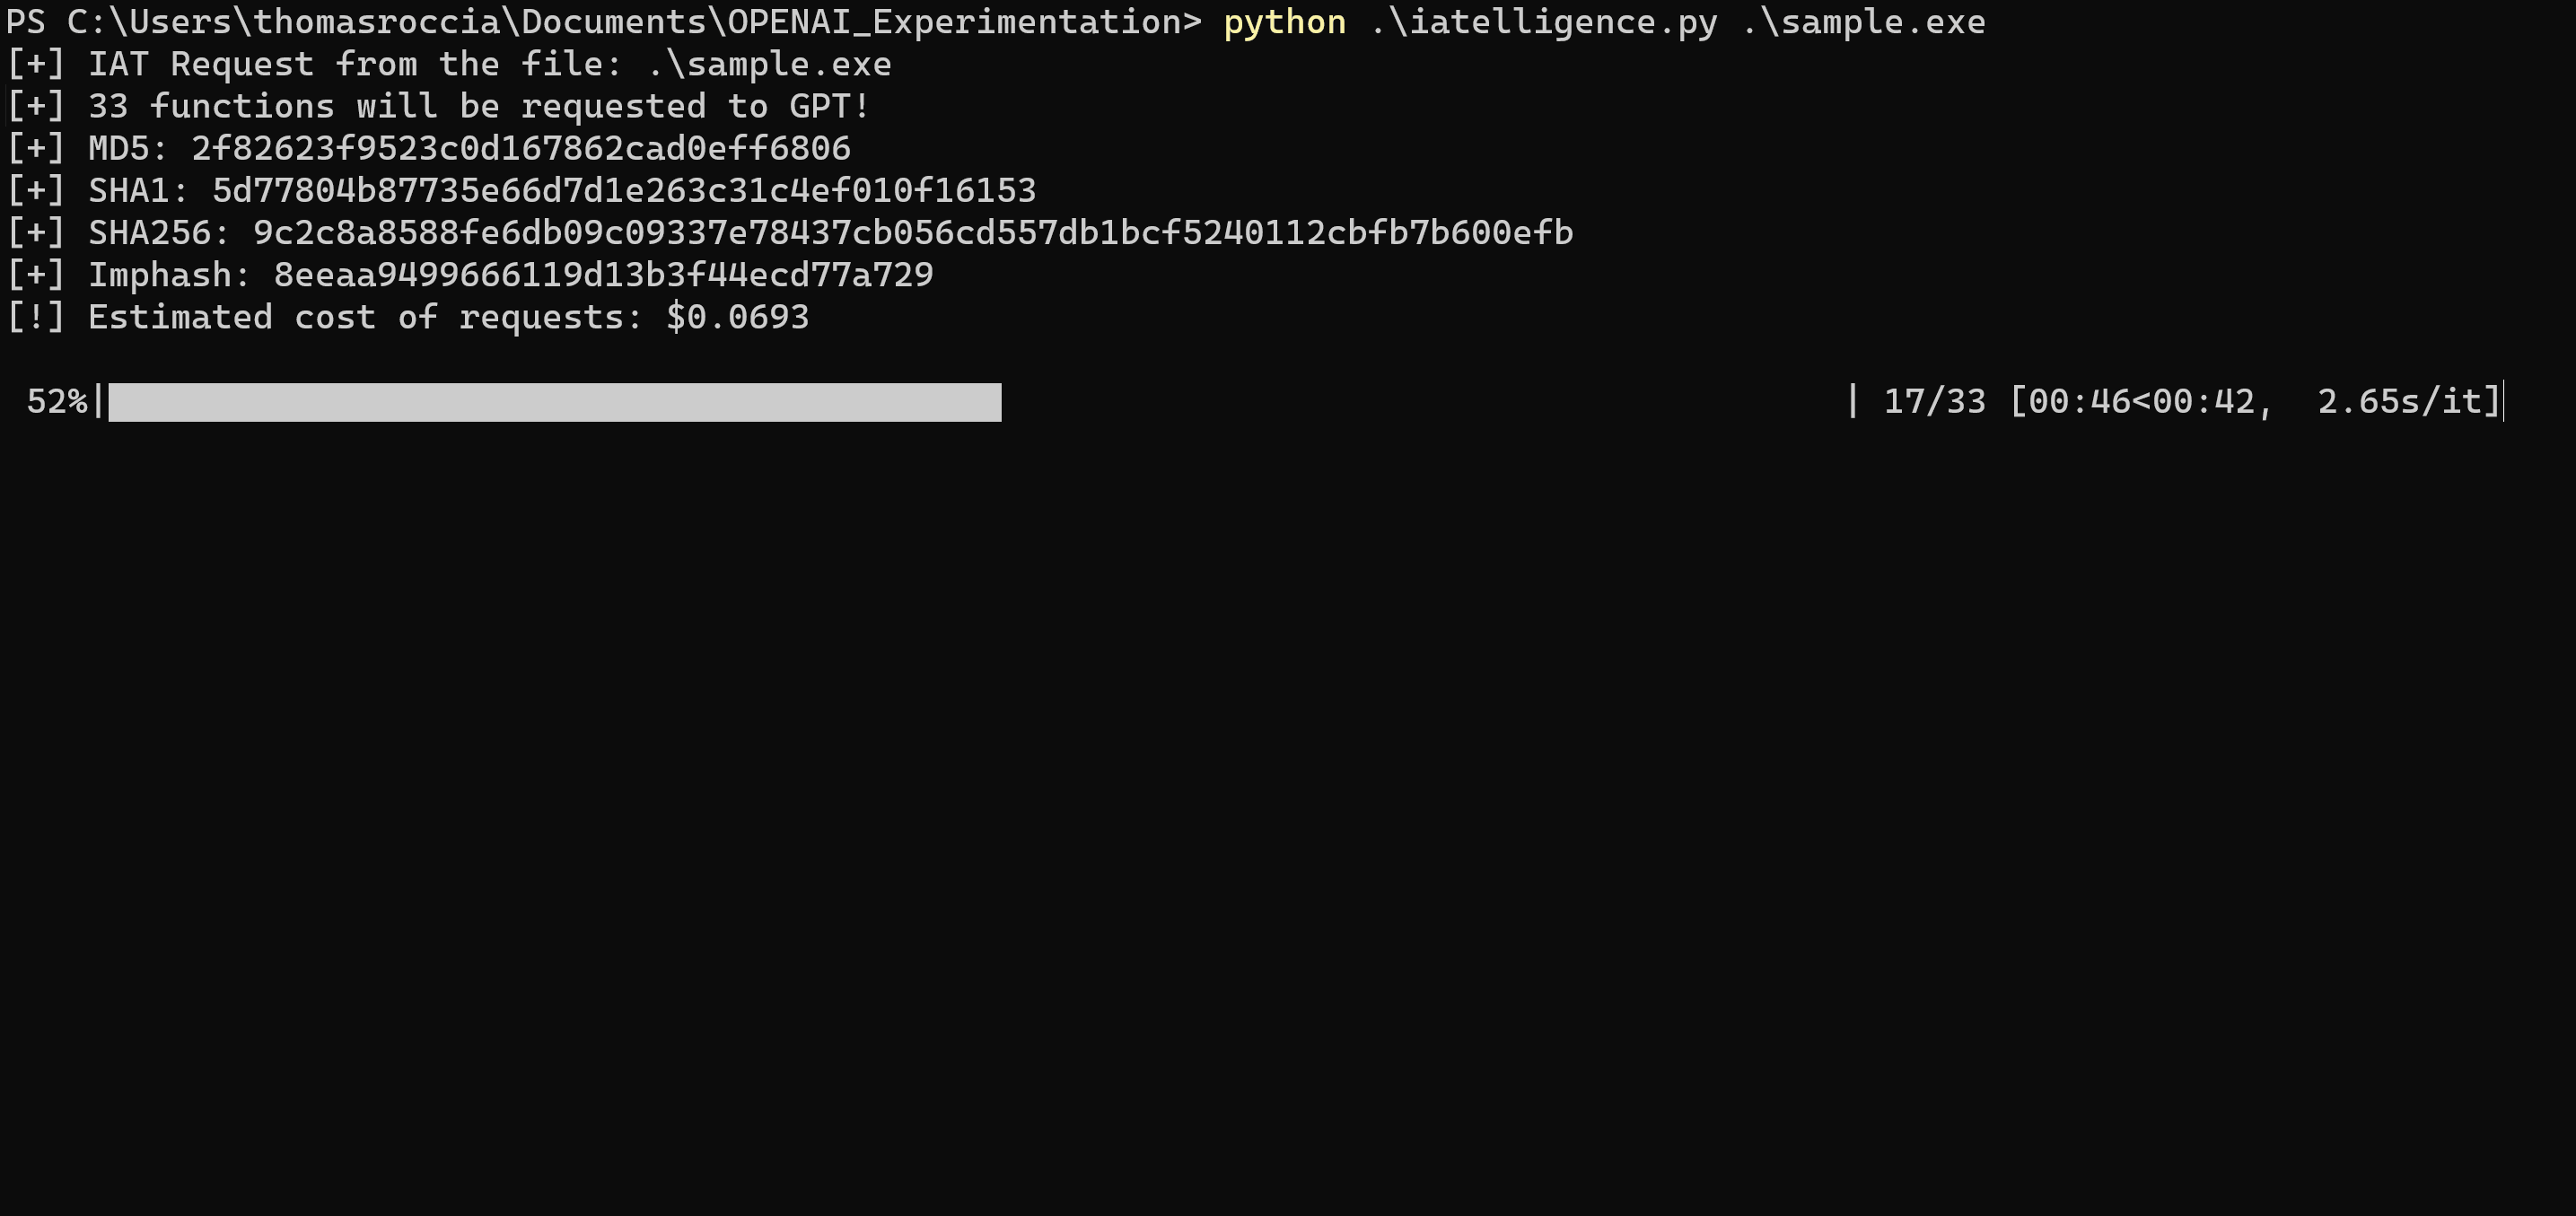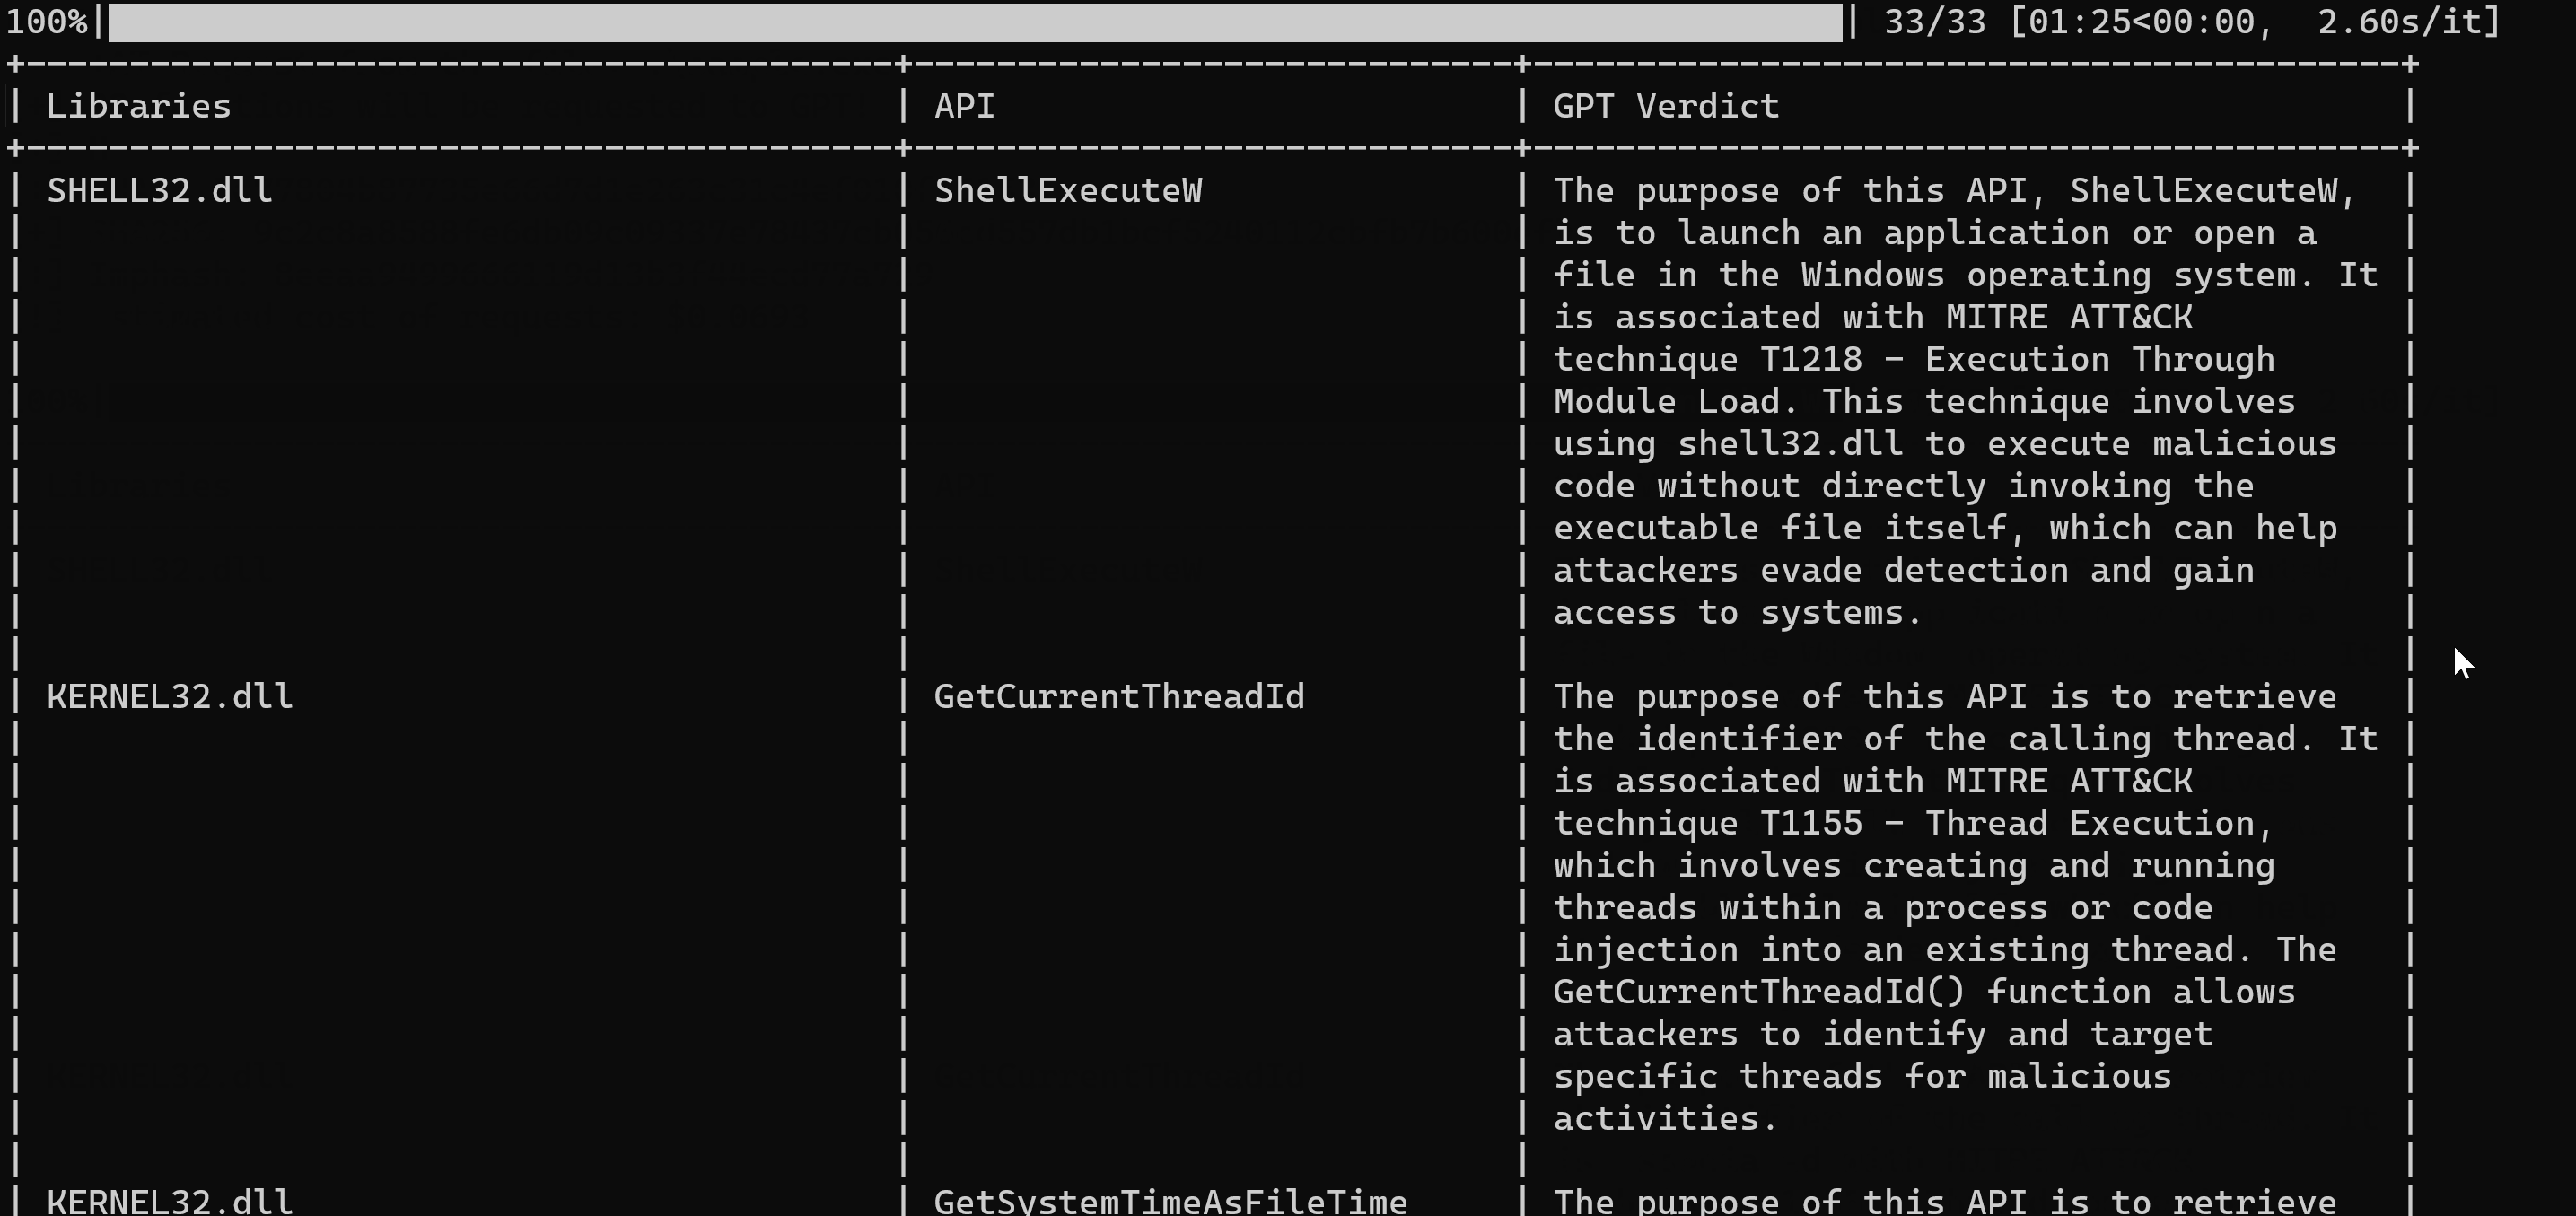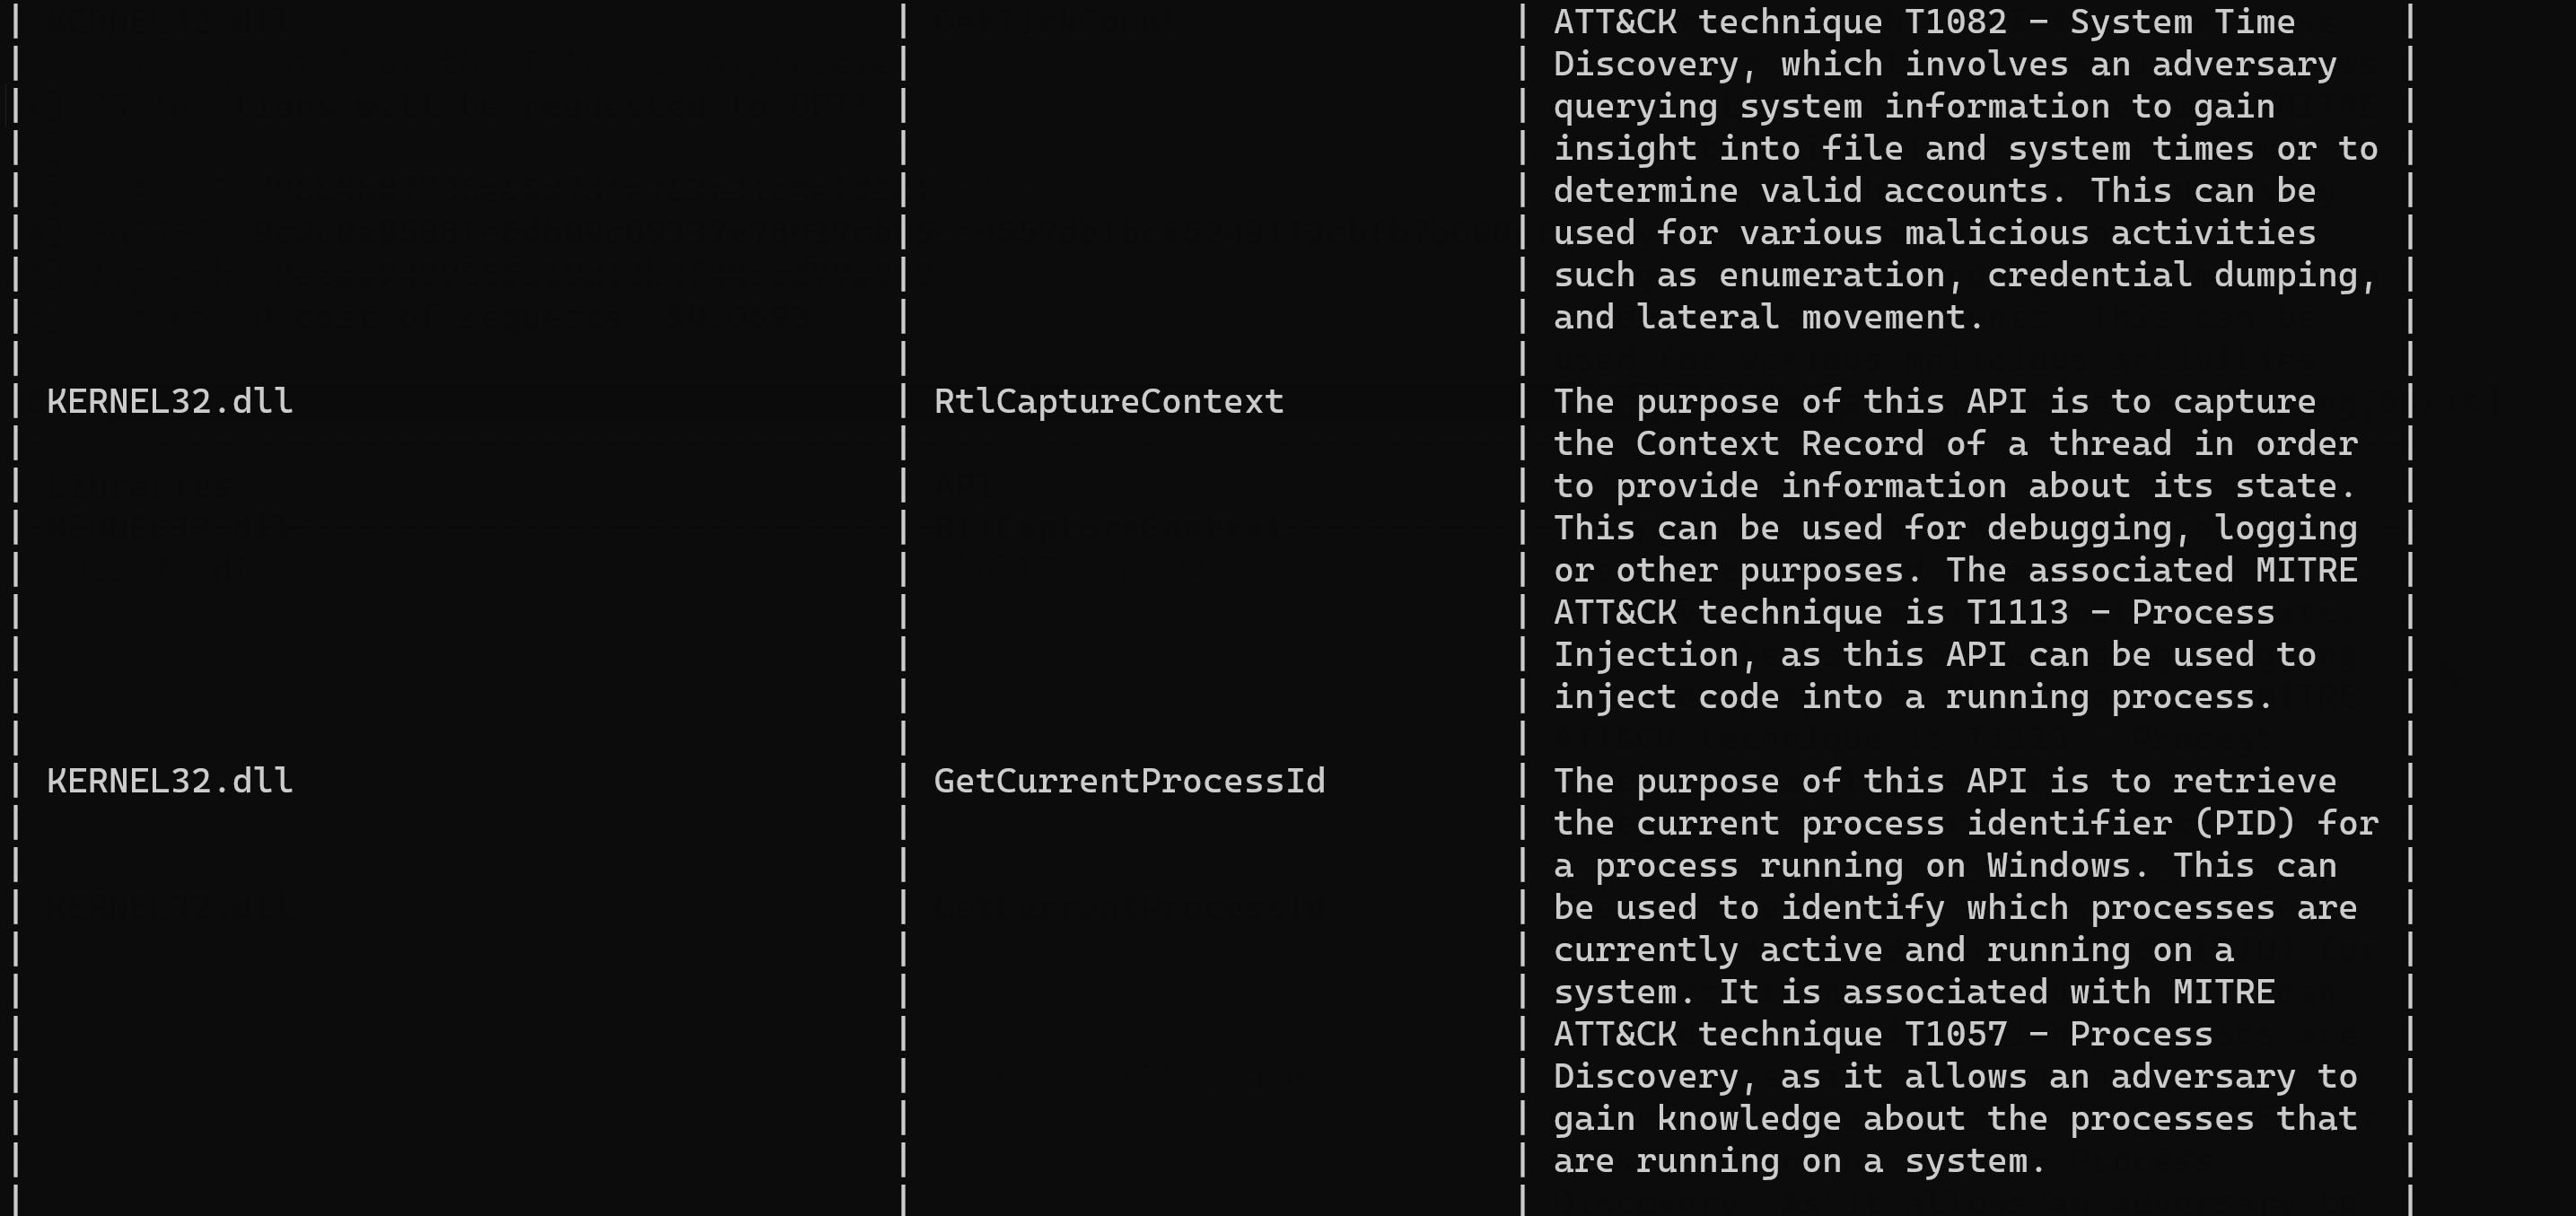
परिणाम को एक तालिका में देखा जा सकता है। नीचे एक छोटा सा अंश दिया गया है।
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
|                                          |                             | the Context Record of a thread in order  |
