 defectdojo/django-defectdojo
Open-Source Unified Vulnerability Management, DevSecOps & ASPM

Open-source vulnerability management, DevSecOps and ASPM
Pro demo · Community demo · Docs · Slack · Community · Website


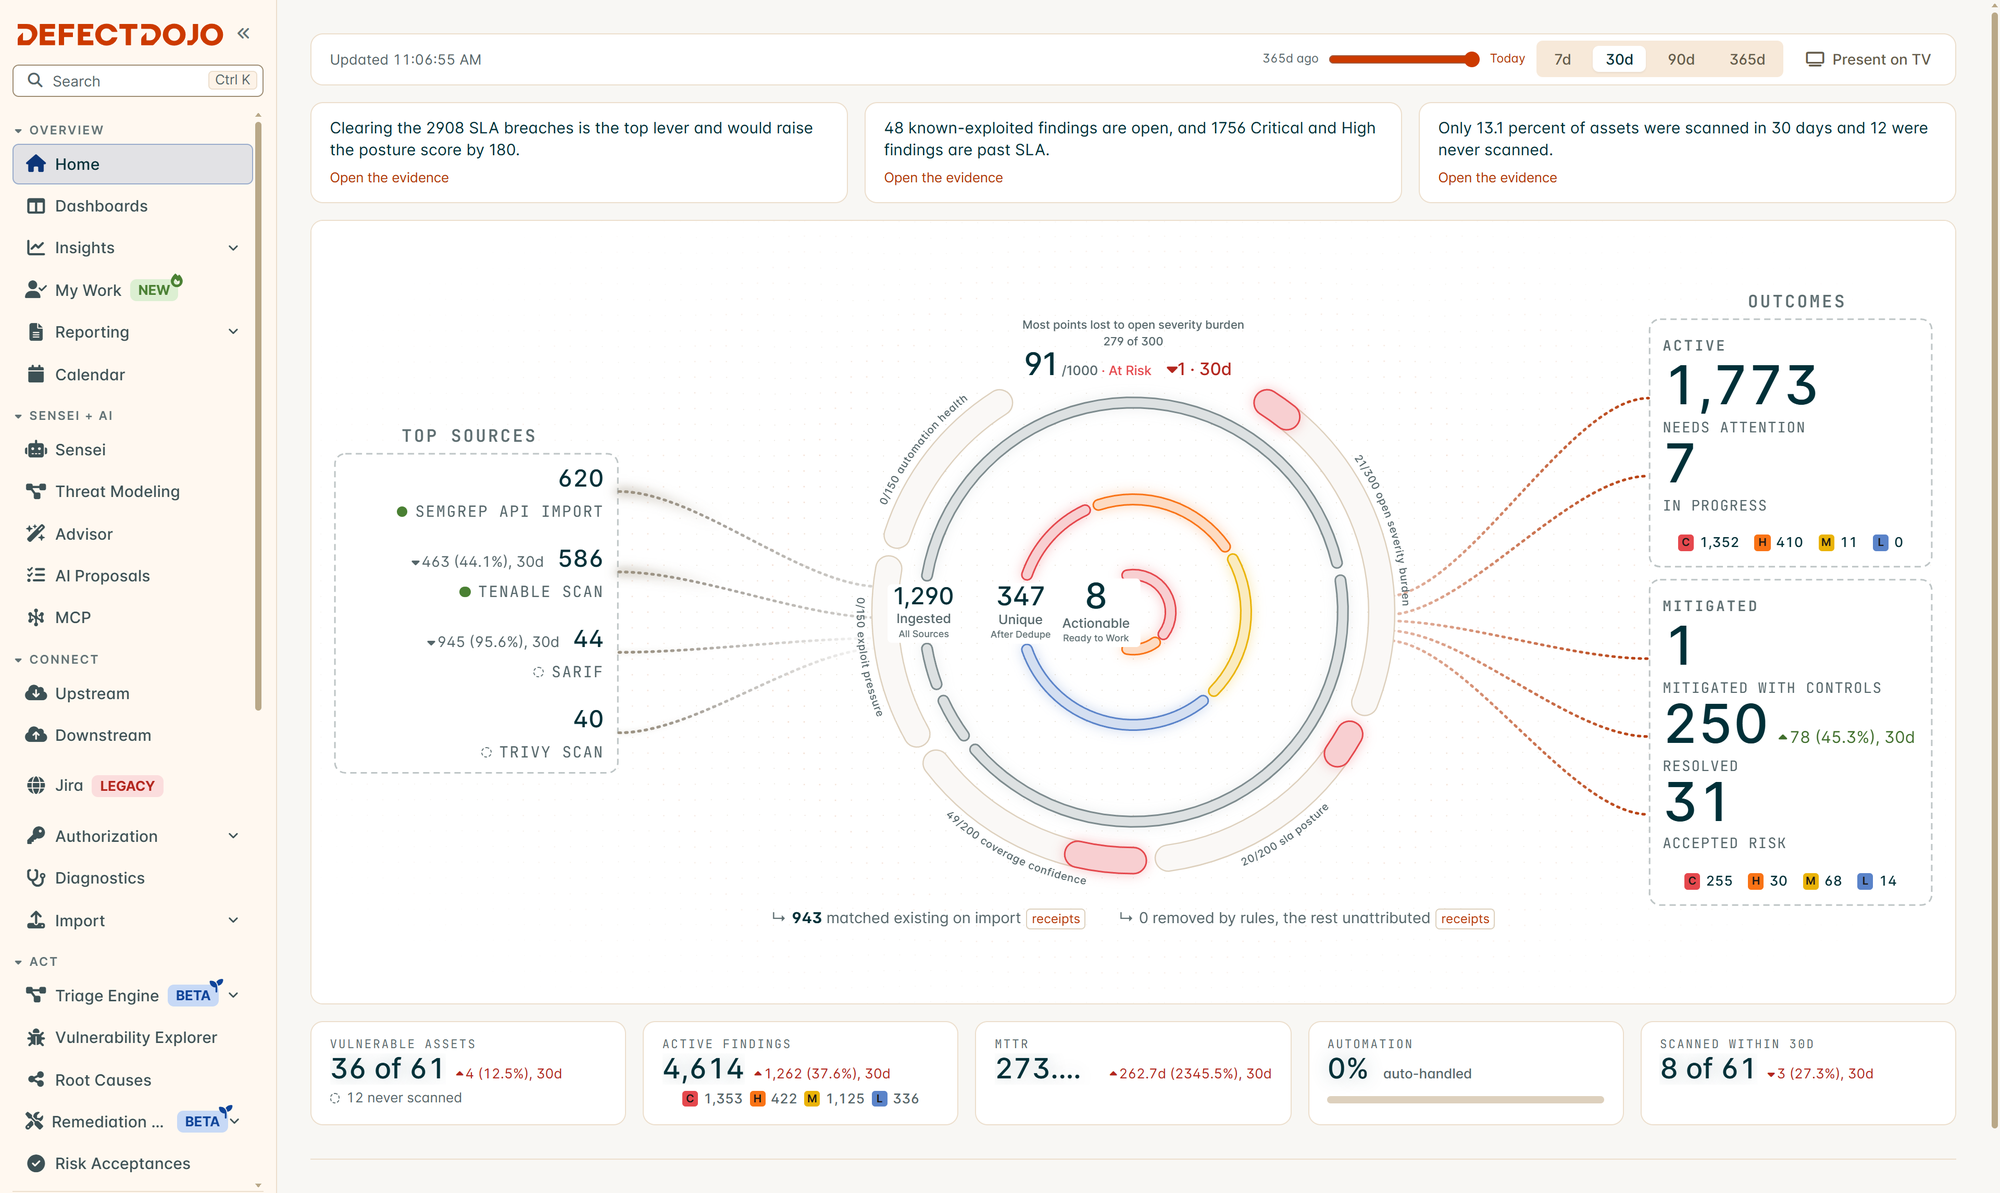
DefectDojo Pro home page. Try it on the live Pro demo.
The Community Edition demo is at demo.defectdojo.org.
Sign-in details for both are under Demo.
DefectDojo is a DevSecOps, ASPM (application security posture management), and vulnerability management tool. DefectDojo orchestrates end-to-end security testing, vulnerability tracking, deduplication, remediation, and reporting.
Pro Edition: pro.demo.defectdojo.com
OWASP Community Edition: demo.defectdojo.org
Either demo environment can be logged into with username admin and password 1Defectdojo@demo#appsec. Please note that the demos are publicly accessible
and reset every day. Do not put sensitive data in the demo. An easy way to test DefectDojo is to upload some sample scan reports.
git clone https://github.com/DefectDojo/django-DefectDojo && cd django-DefectDojo && docker compose up
This quick start guide will do the following
if running DefectDojo in detached mode via docker compose up -d, obtain admin credentials from the initializer logs with the command below. Please note, the initializer can take up to 3 minutes to run.
docker compose logs initializer | grep "Admin password:"

Checkout our new Community Portal and join the DefectDojo community on Slack!
Follow DefectDojo on LinkedIn, YouTube, and X for platform updates!
Please see our contributing guidelines for details and standards on contributing before considering or submitting a pull request.
Everyone taking part in the project follows the Code of Conduct.
