
 #1
भेद्यता परीक्षण विकसित करने, निष्पादित करने और प्रबंधित करने के लिए एकीकृत प्लेटफ़ॉर्म।
Kitploit अनुशंसित

 purpleailab/decepticon
Red Team के लिए स्वायत्त हैकिंग एजेंट
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 pennyw0rth/netexec
विंडोज/एडी वातावरण में स्वचालित नेटवर्क प्रमाणीकरण परीक्षण, क्रेडेंशियल हार्वेस्टिंग, और पार्श्व आंदोलन के लिए मॉड्यूलर प्रोटोकॉल समर्थन वाला…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 fortra/impacket
निम्न-स्तरीय नेटवर्क प्रोटोकॉल हेरफेर के लिए Python लाइब्रेरी, जिसमें SMB, MSRPC, Kerberos, और WMI कार्यान्वयन शामिल हैं, प्रमाणीकरण हमलों,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 reconmap/reconmap
Reconmap is a collaboration-first security operations platform for infosec teams and MSSPs, enabling end‑to‑end engagement management, from…
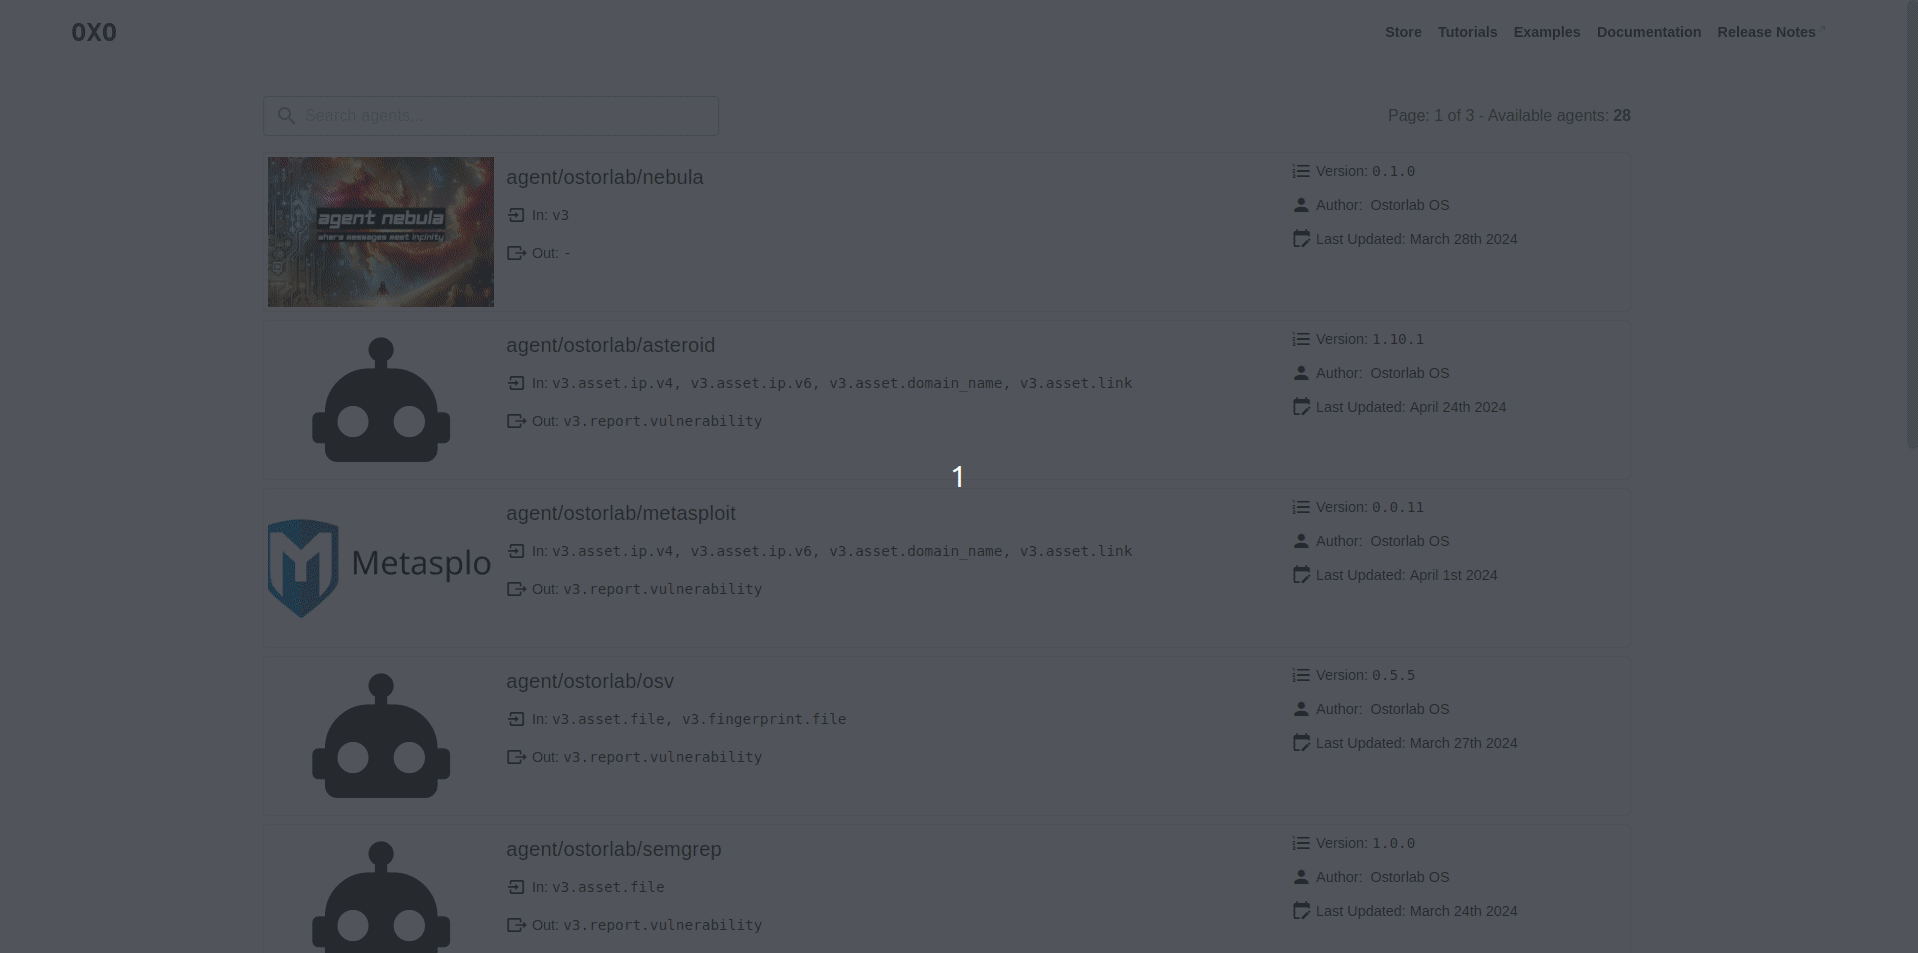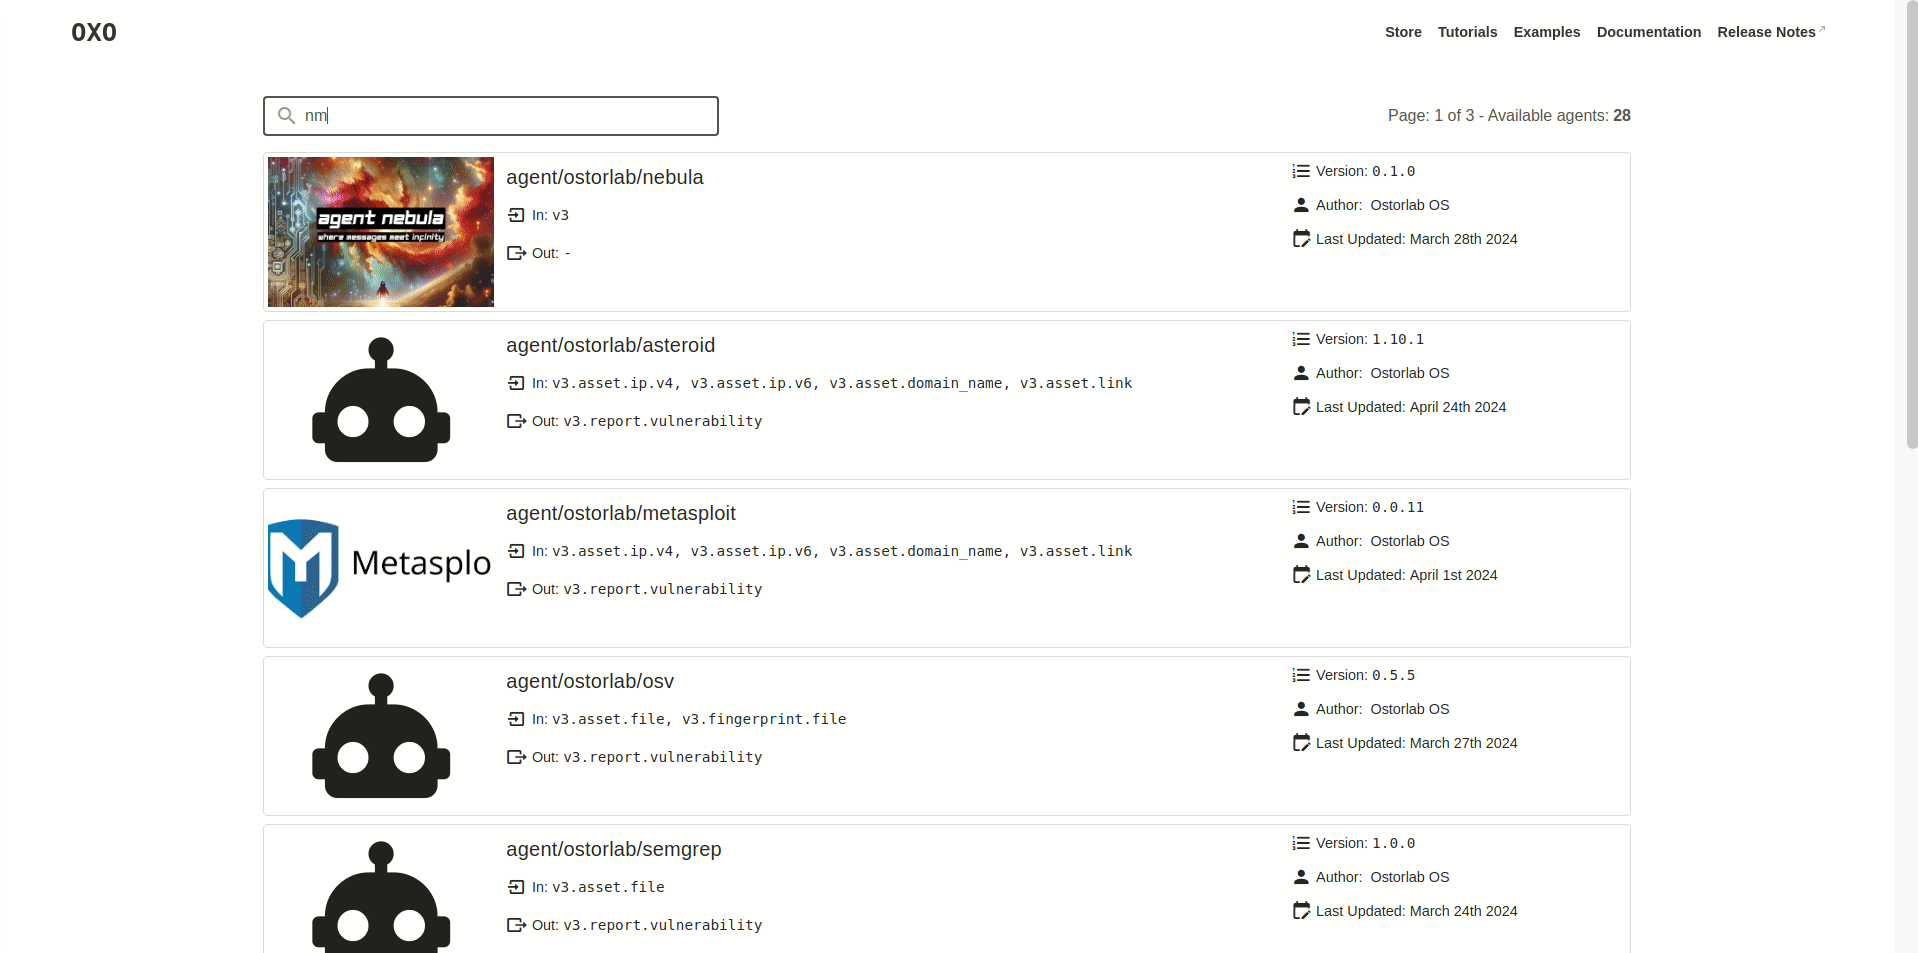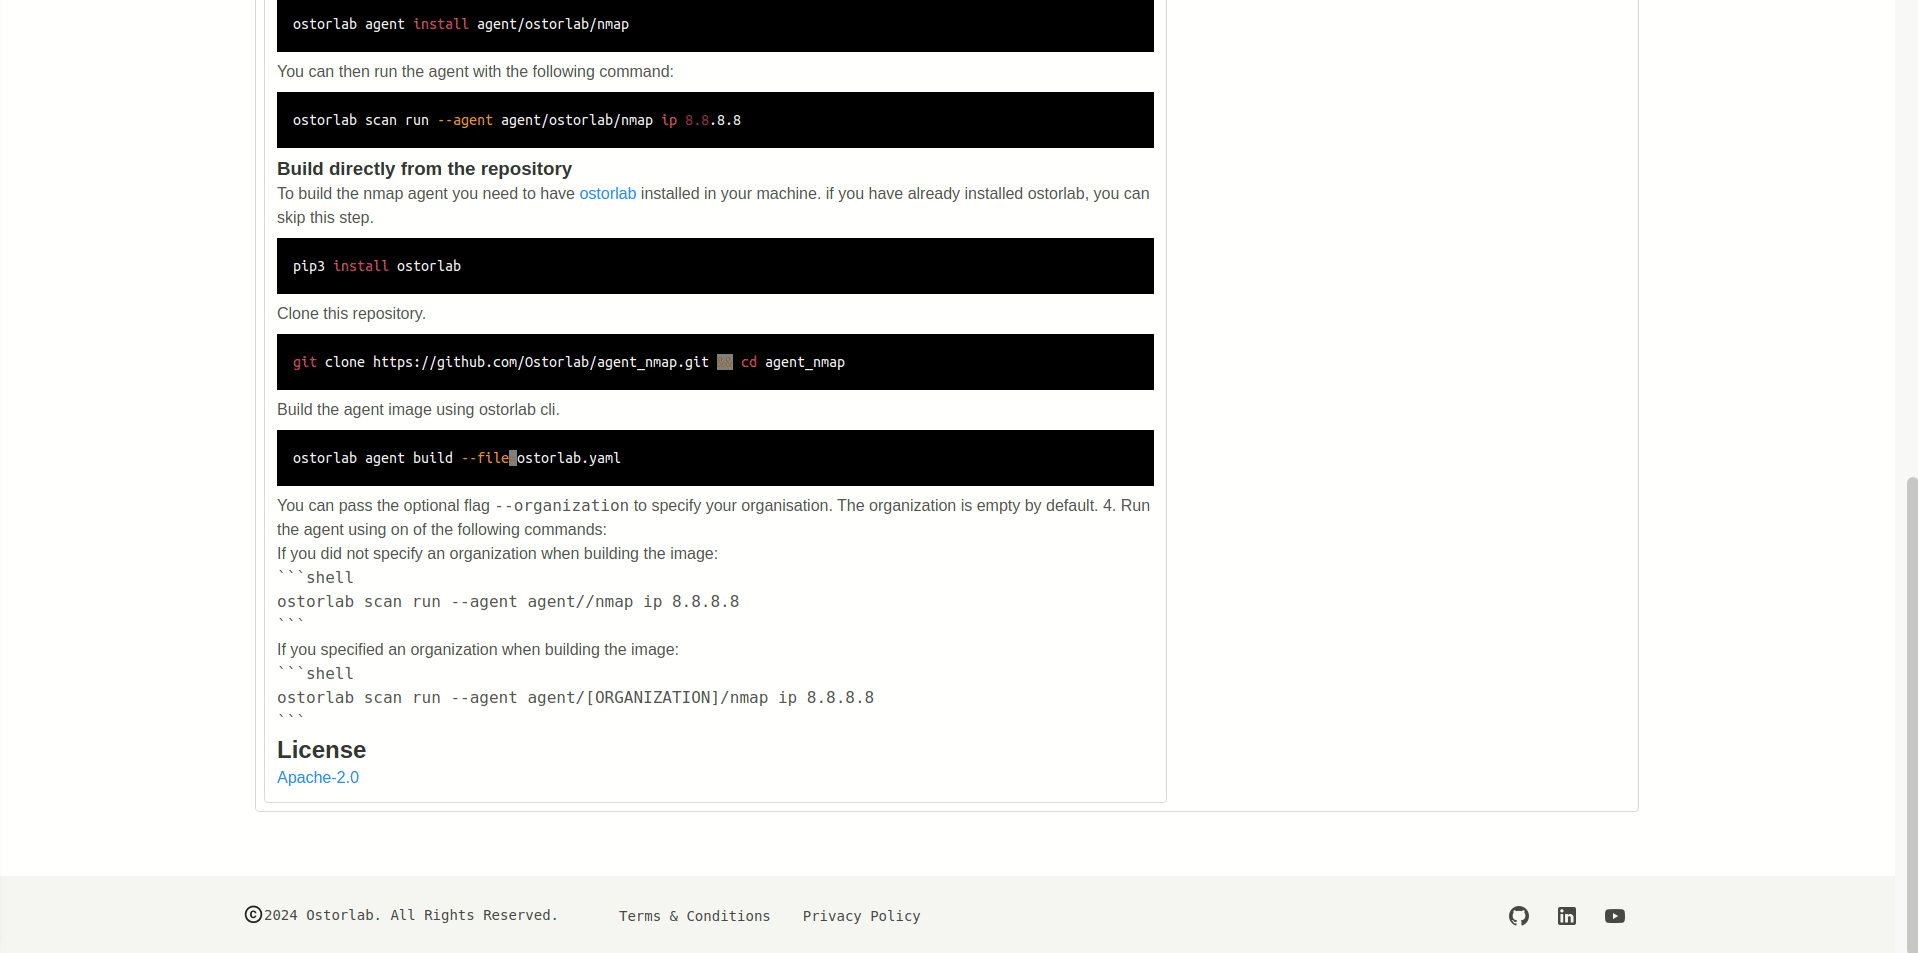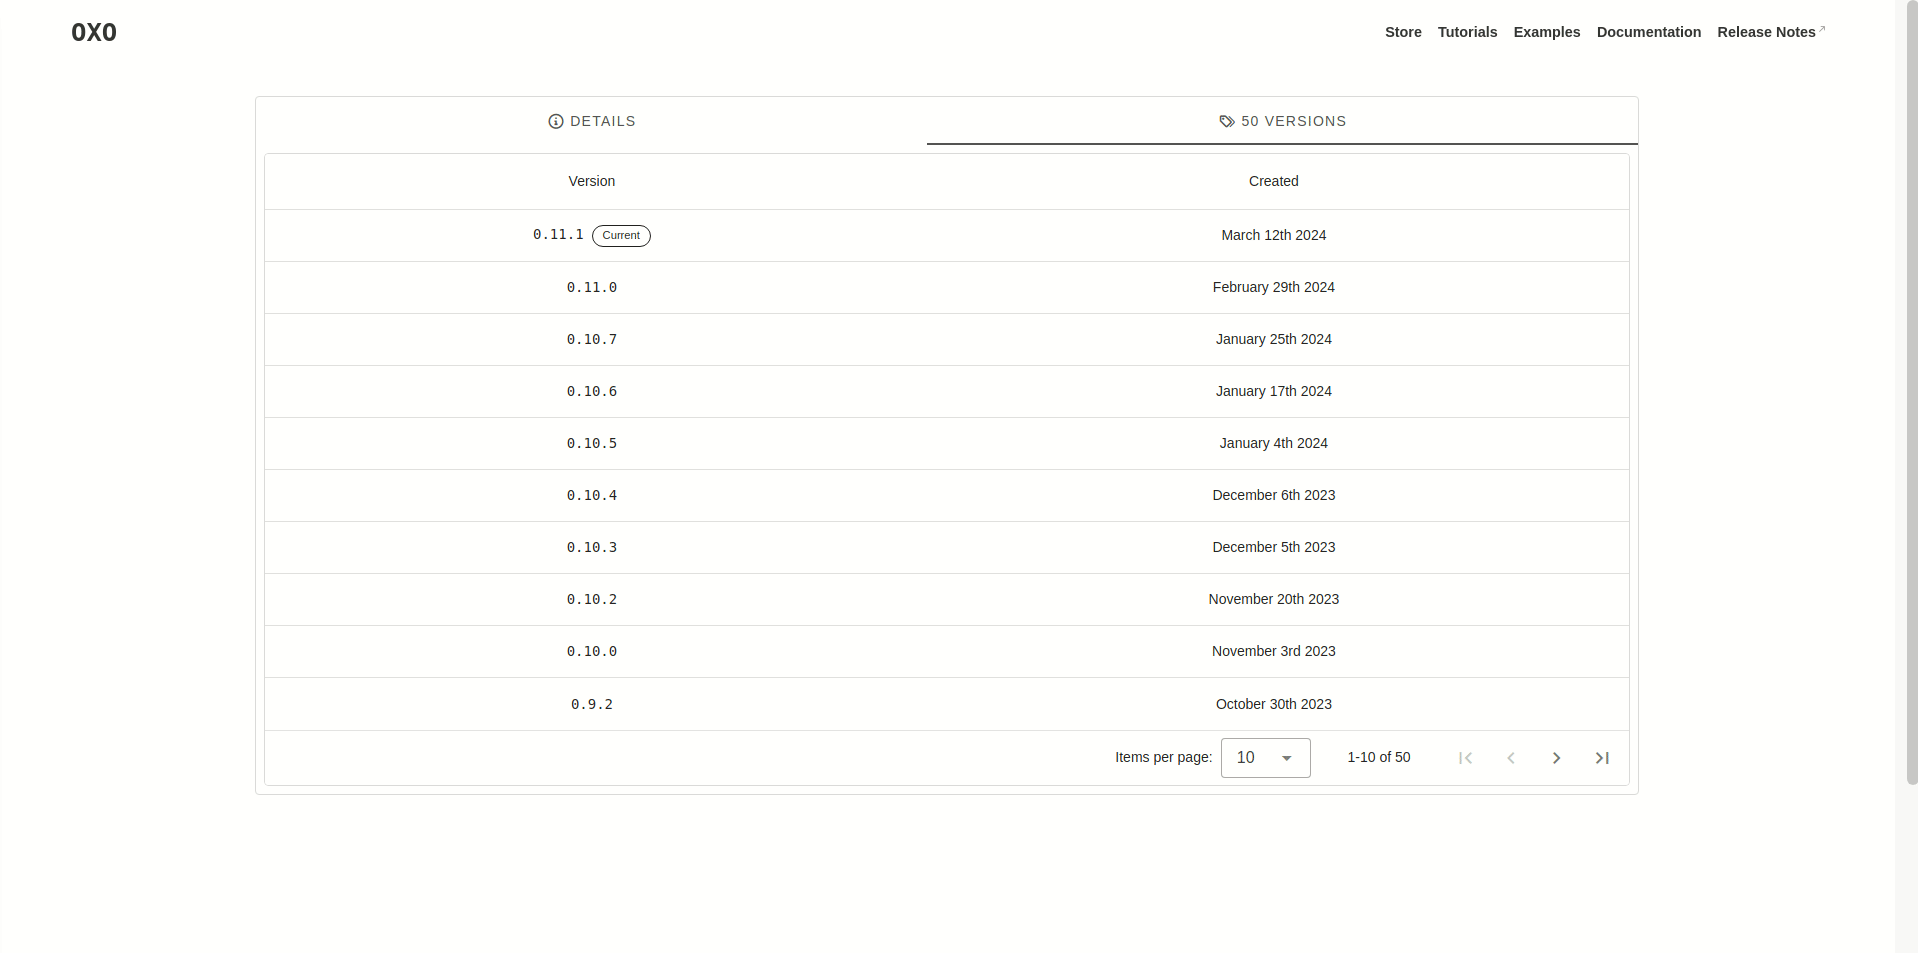 ostorlab/oxo
मॉड्यूलर सुरक्षा स्कैनिंग ऑर्केस्ट्रेटर जो नेटवर्क, वेब ऐप्स, मोबाइल ऐप्स और API में कमजोरी का पता लगाने, टोह लेने और फिंगरप्रिंटिंग के लिए विशेष…
 sia-iotechnology/kittysploit-framework
पायथन एक्सप्लॉइटेशन फ्रेमवर्क, V8 इंजन डीबगर, प्रॉक्सी इंटरसेप्टर, मार्केटप्लेस, पोस्ट-एक्सप्लॉइटेशन, बैकडोर जनरेटर,....
 zerbea/hcxtools
कैप्चर फ़ाइलों से पैकेट्स को हैश फ़ाइलों में परिवर्तित करने के लिए उपकरणों का एक छोटा सेट, जो Hashcat या John the Ripper के साथ उपयोग के लिए है।
rapid7/metasploit-frameworkखुला-स्रोत शोषण ढांचा जिसमें पेनिट्रेशन टेस्टिंग, कमजोरियों की पुष्टि और नेटवर्क व अनुप्रयोगों में सुरक्षा अनुसंधान के लिए मॉड्यूलर पेलोड, एनकोडर और…
 vulncheck-oss/go-exploit
Go-आधारित शोषण विकास ढांचा जिसमें लक्ष्य सत्यापन, संस्करण स्कैनिंग, शोषण और C2 के लिए निर्मित चरण हैं। कई पेलोड, प्रोटोकॉल सहायकों और Metasploit जैसे…
 mrwadams/stride-gpt
एक AI-संचालित खतरा मॉडलिंग उपकरण जो STRIDE पद्धति पर आधारित किसी दिए गए एप्लिकेशन के लिए खतरा मॉडल उत्पन्न करने के लिए OpenAI के GPT मॉडल का उपयोग…
 ascit31/dark-moon
स्वायत्त AI पेंटेस्टिंग इंजन — वेब, क्लाउड, AD और Kubernetes में निरंतर आक्रामक सुरक्षा। एजेंटिक तर्क और वास्तविक एक्सप्लॉइट निष्पादन प्रमाण-आधारित…
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
 beefproject/beef
ब्राउज़र शोषण फ्रेमवर्क परियोजना
 gentilkiwi/mimikatz
विंडोज सुरक्षा के साथ खेलने के लिए एक छोटा सा उपकरण
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…







