


Skip to content
KitploitKITPLOIT
उपकरणएक्सप्लॉइटब्लॉग
Log in
जमा करें
उपकरणएक्सप्लॉइटब्लॉग
जमा करें

हैकिंग, पेनटेस्ट और साइबर सुरक्षा उपकरण आपके सुरक्षा शस्त्रागार के लिए!

Kitploit हैकिंग, साइबर सुरक्षा और पेंटेस्टिंग टूल्स की एक निर्देशिका है। कमजोरियों को खोजने, सिस्टम का विश्लेषण करने, परीक्षण को स्वचालित करने और अपनी सुरक्षा को मजबूत करने के लिए नवीनतम प्रोजेक्ट अपडेट खोजें।

फ़ीडसंपर्कगोपनीयता© 2026 Kitploit

टूल निर्देशिका

श्रेणियाँ

सभी श्रेणियाँ देखें
Loading categories
OSINT (खुला स्रोत खुफिया) — पृष्ठ 68 | Kitploit
श्रेणियाँ

OSINT (खुला स्रोत खुफिया)

ऑनलाइन स्रोतों से सार्वजनिक रूप से उपलब्ध जानकारी इकट्ठा करने और उसका विश्लेषण करने के उपकरण।

Kitploit अनुशंसित

शीर्ष उपकरण

10 चयनित
sherlock preview#1

sherlock

GitHubsherlock-project/sherlock
89.1k18 दिन पहले
maigret preview#2

maigret

GitHubsoxoj/maigret
36.5k9घं 1मि पहले
social-analyzer preview#3

social-analyzer

GitHubqeeqbox/social-analyzer
23.7k11 दिन पहले
spiderfoot preview#4

spiderfoot

GitHubsmicallef/spiderfoot
20.1k3 साल पहले
GHunt preview#5

GHunt

GitHubmxrch/ghunt
19.3k7 महीने पहले
phoneinfoga preview#6

phoneinfoga

GitHubsundowndev/phoneinfoga
17.4k2 महीने पहले
theHarvester preview#7

theHarvester

GitHublaramies/theharvester
17.0k6 दिन पहले
Osintgram preview#8

Osintgram

GitHubdatalux/osintgram
13.9k24 दिन पहले
holehe preview#9

holehe

GitHubmegadose/holehe
12.0k2 साल पहले
blackbird preview#10

blackbird

GitHubp1ngul1n0/blackbird
7.5k15 दिन पहले
नवीनतमप्रासंगिकतासबसे लोकप्रियहाल ही में अपडेट किया गया
1325 परिणाम
CVE-2019-0708 preview

CVE-2019-0708

GitHubttsite/cve-2019-0708

धोखाधड़ी की रिपोर्ट करें

osintreconnaissanceinformation-gathering+2
17 साल पहले
saas_enum preview

saas_enum

GitLabhackinglz/saas_enum

DNS एन्यूमरेशन के माध्यम से किसी कंपनी द्वारा उपयोग किए जाने वाले SaaS प्लेटफ़ॉर्म की खोज के लिए कमांड-लाइन टूल


osintreconnaissancedns-subdomain-enumeration+1
1 साल पहले
getrails preview

getrails

GitHubjul10l1r4/getrails

Get trails lib: लक्ष्य के सभी अनुक्रमित URLs प्राप्त करें
osintdns-subdomain-enumerationinformation-gathering+1
4 साल पहले
logineo-scraper preview

logineo-scraper

GitHubgmh5225/logineo-scraper

Logineo इंस्टेंस से व्यक्तिगत जानकारी स्क्रैप करने के लिए त्वरित स्क्रिप्ट

osintscripting-automationdata-exfiltration+4
3 साल पहले
SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400- preview

SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400-

GitHubcyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-

चरण-दर-चरण SOC विश्लेषक का मार्गदर्शन CVE-2024-3400 (PAN-OS command injection) की जांच और उपचार के लिए। इसमें detection, log analysis, threat…

ioc-managementosintvulnerability-analysis+6
1 साल पहले
go-sherlock preview

go-sherlock

GitLabdrskelebones/go-sherlock

गो में लिखा गया उच्च-प्रदर्शन उपयोगकर्ता नाम खोज इंजन। किसी दिए गए उपयोगकर्ता नाम से जुड़े खातों को खोजने के लिए सैकड़ों सोशल नेटवर्क और वेबसाइटों को…

osintreconnaissanceinformation-gathering+2
4 साल पहले
ti-a-ti-cveexploitchecker preview

ti-a-ti-cveexploitchecker

GitHubshadowguardai/ti-a-ti-cveexploitchecker

निर्धारित करता है कि किसी दिए गए CVE के लिए सार्वजनिक एक्सप्लॉइट उपलब्ध हैं या नहीं। पहचान करने के लिए exploit-db या NVD जैसे API का उपयोग करता है

ioc-managementosintvulnerability-scanners+5
1 साल पहले
disclosure-check preview

disclosure-check

GitHubgmh5225/disclosure-check

किसी पैकेज/प्रोजेक्ट के लिए सुरक्षा भेद्यता को निजी तौर पर प्रकट करने के लिए सर्वोत्तम तंत्रों की पहचान करने का उपकरण।
defensive-toolsosintreconnaissance+4
3 साल पहले
ThreatIntelligence preview

ThreatIntelligence

GitHubsh1katagana1/threatintelligence

साइबर खतरा खुफिया से संबंधित सभी चीज़ों के लिए एक रिपॉजिटरी

osintreconnaissancevulnerability-analysis+2
8 महीने पहले
CVE-2024-31320- preview

CVE-2024-31320-

GitHubspiralbl0ck/cve-2024-31320-

CVE-2024-31320 और bluetooth का उपयोग करके शोषित उपकरण का भू-स्थान प्राप्त करें

osintreconnaissancebluetooth-security+3
1 साल पहले
shellshock_crawler preview

shellshock_crawler

GitHub352926/shellshock_crawler

गूगल का उपयोग करके "ShellShock" (CVE-2014-6271) के लिए साइटों को स्कैन करना
osintreconnaissancevulnerability-scanners+3
12 साल पहले
elastic-search-email-extractor preview

elastic-search-email-extractor

GitHubrandomrobbiebf/elastic-search-email-extractor

ईमेल पतों के लिए Elasticsearch डेटाबेस खोजता है
osintinformation-gatheringemail-harvesting
3 साल पहले
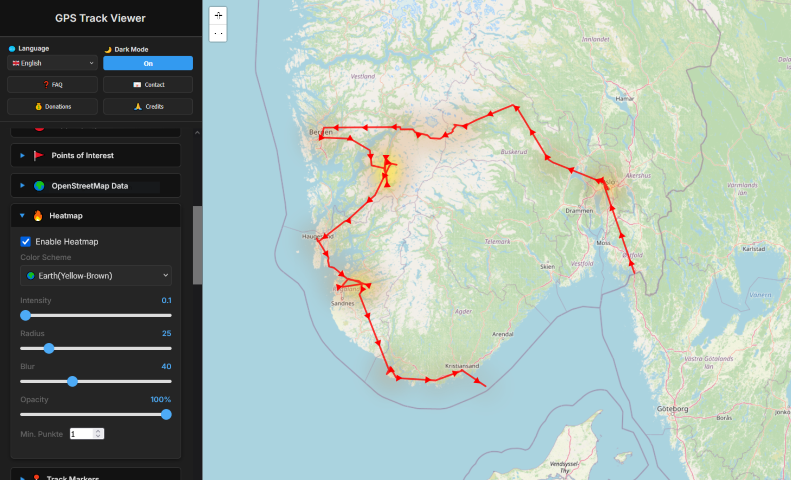
LocalExifGeoMap preview

LocalExifGeoMap

GitHublukawe/localexifgeomap

आपकी तस्वीरों से GPS डेटा को विज़ुअलाइज़ और विश्लेषण करने के लिए एक शक्तिशाली, गोपनीयता-केंद्रित, ब्राउज़र-आधारित टूल। इंटरैक्टिव मानचित्र, हीटमैप,…
general-purpose-utilitiesosintforensics+3
19 महीने पहले
exploit_CVE-2022-26134 preview

exploit_CVE-2022-26134

GitHubsunny-kathuria/exploit_cve-2022-26134

CVE-2022-26134, एक OGNL इंजेक्शन भेद्यता मौजूद है जो एक अप्रमाणित हमलावर को Confluence Server या Data Center इंस्टेंस पर मनमाना कोड निष्पादित करने की…

osintreconnaissancevulnerability-analysis+2
4 साल पहले
cve-2021-41773 preview

cve-2021-41773

GitHubmohwahyudi/cve-2021-41773

Python स्क्रिप्ट जो CVE-2021-41773 पाथ ट्रैवर्सल और फ़ाइल प्रकटीकरण के लिए कमजोर Apache HTTP सर्वर 2.4.49 इंस्टेंस खोजने के लिए Shodan का उपयोग करती…

osintreconnaissancevulnerability-analysis+3
5 साल पहले
Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413 preview

Project-NTLM-Hash-Capture-and-Phishing-Email-Exploitation-for-CVE-2024-21413

GitHubartemcyberlab/project-ntlm-hash-capture-and-phishing-email-exploitation-for-cve-2024-21413

Responder के माध्यम से NTLM हैश कैप्चर करने और CVE-2024-21413 का शोषण करने वाले फ़िशिंग ईमेल निष्पादित करके सिस्टम से समझौता करने का प्रदर्शन।
osintpassword-crackingreconnaissance+5
1 साल पहले
nuclei-CiscoRV320Dump-CVE-2019-1653 preview

nuclei-CiscoRV320Dump-CVE-2019-1653

GitHubelzerjp/nuclei-ciscorv320dump-cve-2019-1653

स्वचालित Nuclei टेम्पलेट और Shodan वर्कफ़्लो Cisco राउटर कॉन्फ़िगरेशन एक्सपोज़र (CVE-2019-1653) का पता लगाने और शोषण करने के लिए सुरक्षा ऑडिटिंग हेतु।
osintreconnaissancevulnerability-scanners+3
2 साल पहले
CVE-2017-5487 preview

CVE-2017-5487

GitHubdream434/cve-2017-5487

CVE-2017-5487 के लिए एक्सप्लॉइट जो REST API के माध्यम से WordPress उपयोगकर्ता खातों की गणना करता है, और कमजोर 4.7 इंस्टॉलेशन से संवेदनशील जानकारी…


osintreconnaissancevulnerability-analysis+2
1 साल पहले
पिछला1…676869…74अगला


