
 zerodayevil/cve-2026-20805-poc
Proof-of-concept exploit code for CVE-2026-20805, demonstrating the vulnerability for security research and validation.

🛡️ AI Security Tool Module
CVE-2026-20805: Desktop Window Manager (dwm.exe) Memory Disclosure
Official Security Audit Module for AI Security Tool Ecosystem





🌐 Web Demo • 📚 Project Website • 💬 Community Chat
Website Navigation: Home • Updates • Downloads • Modules
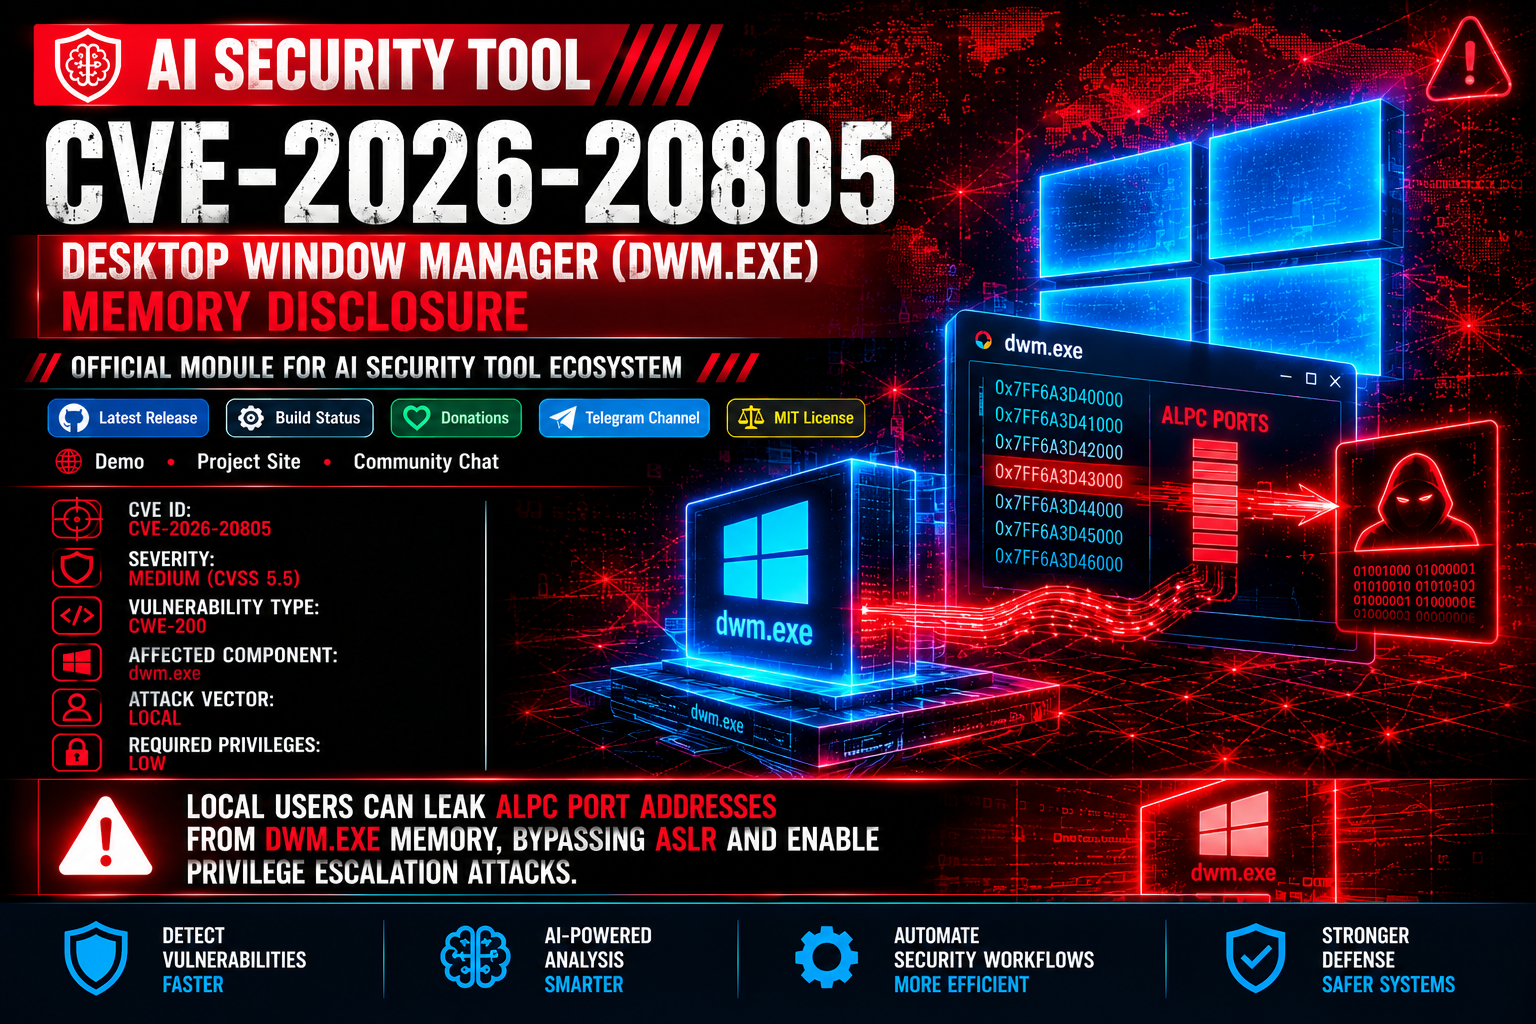
This module provides diagnostic tools for evaluating CVE-2026-20805, an information disclosure vulnerability in the Desktop Window Manager (dwm.exe) component of Microsoft Windows (classified as CWE-200).
An authenticated local attacker with low privileges can exploit this flaw to reveal remote ALPC (Asynchronous Local Procedure Call) port section addresses from DWM process memory. The leaked user-mode memory addresses allow attackers to bypass modern exploit mitigations (such as ASLR) and chain this vulnerability into a broader privilege escalation attack vector.
"Information disclosure is the primary key to bypassing modern OS mitigations."
While a memory leak in DWM does not directly yield arbitrary code execution on its own, it drastically reduces system resilience by giving attackers precise memory targets for kernel or service exploitation.
| Specification | Assigned Value | Notes |
|---|---|---|
| CVE Identifier | CVE-2026-20805 |
Information Disclosure Vulnerability |
| Severity Rating | Medium (CVSS v3.1: 5.5) | CVSS:3.1/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N |
| Vulnerability Type | CWE-200 |
Exposure of Sensitive Information to an Unauthorized Actor |
| Affected Component | Desktop Window Manager (dwm.exe) |
Windows Compositing & Graphics Subsystem |
| Attack Vector | Local | Requires execution from an authenticated user account |
| Privileges Required | Low Privileges | Standard unprivileged user access |
graph TD
    A[Authenticated Low-Priv User] -->|Initiate ALPC Calls| B[Desktop Window Manager dwm.exe]
    B -->|Trigger Unchecked Memory Read| C[Extract Remote ALPC Section Addresses]
    C -->|User-Mode Memory Leak| D[Bypass ASLR / Defense Mechanisms]
    D -->|Chain with Local Privilege Escalation| E[System Privilege Compromise]
CVE-2026-20805-POC/
├── poc/
│   └── dumper.py            # Diagnostic script to capture & analyze memory leaks
├── docs/
│   └── technical_analysis.md # Technical breakdown and internal details
├── scripts/
│   └── setup_env.ps1        # Environment configuration script
├── .gitignore
└── README.md⚠️ IMPORTANT: This module is built specifically for safe execution and diagnostics within the AI Security Tool ecosystem. Always use verified modules sourced from official repositories.
To execute the monitoring and diagnostic scripts, ensure the AI Security Tool core engine is installed:
