
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
nuclei-wordfence-cve — 80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒 | Kitploit
Outils/GitHubGitHub/topscoder/nuclei-wordfence-cve
Vulnerability ScannersVulnerability AnalysisExploitationInformation GatheringWeb SecurityCrawler
GitHubtopscoder/nuclei-wordfence-cve

nuclei-wordfence-cve

80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒

Voir le dépôt
1.3k15451il y a 20h 11mVérifié par Kitploit
Partager
Contenu non disponible dans la langue demandée. Affichage de la version anglaise.

Nuclei + Wordfence = ♥

90,951 Nuclei Templates for WordPress Security Scanning 🥳

GitHub Workflow Status pre-commit Templates added
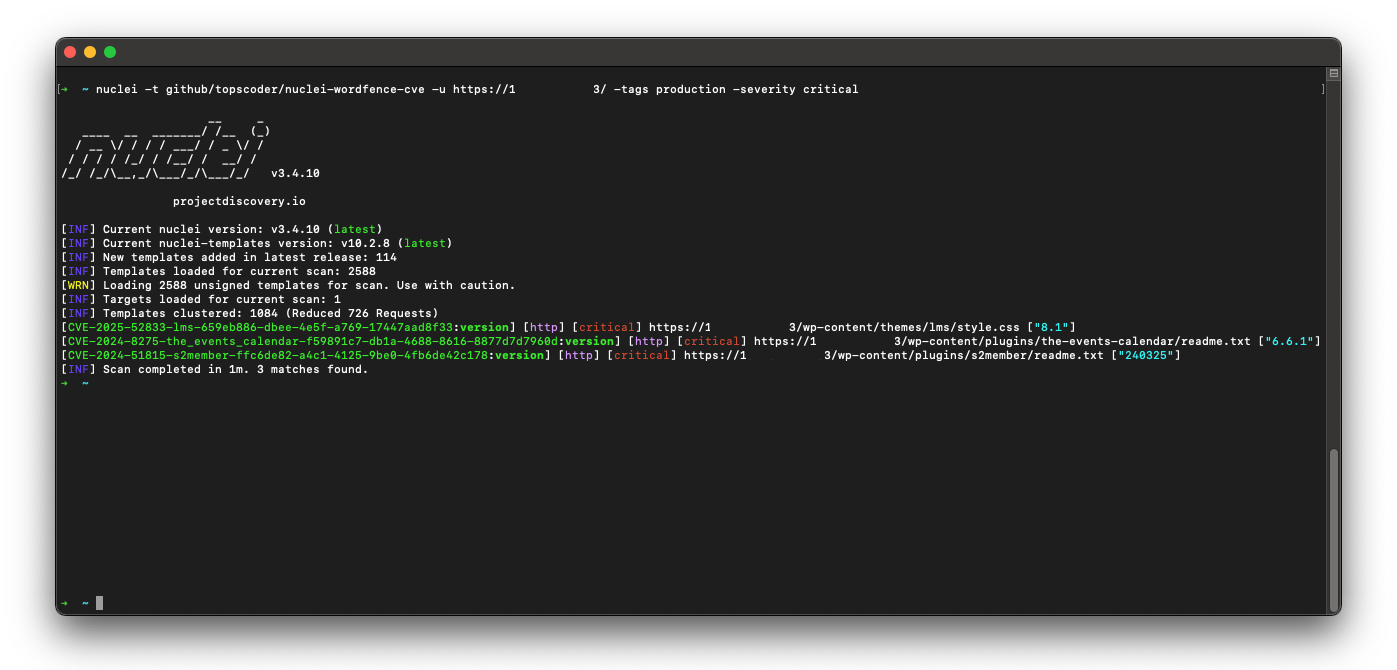
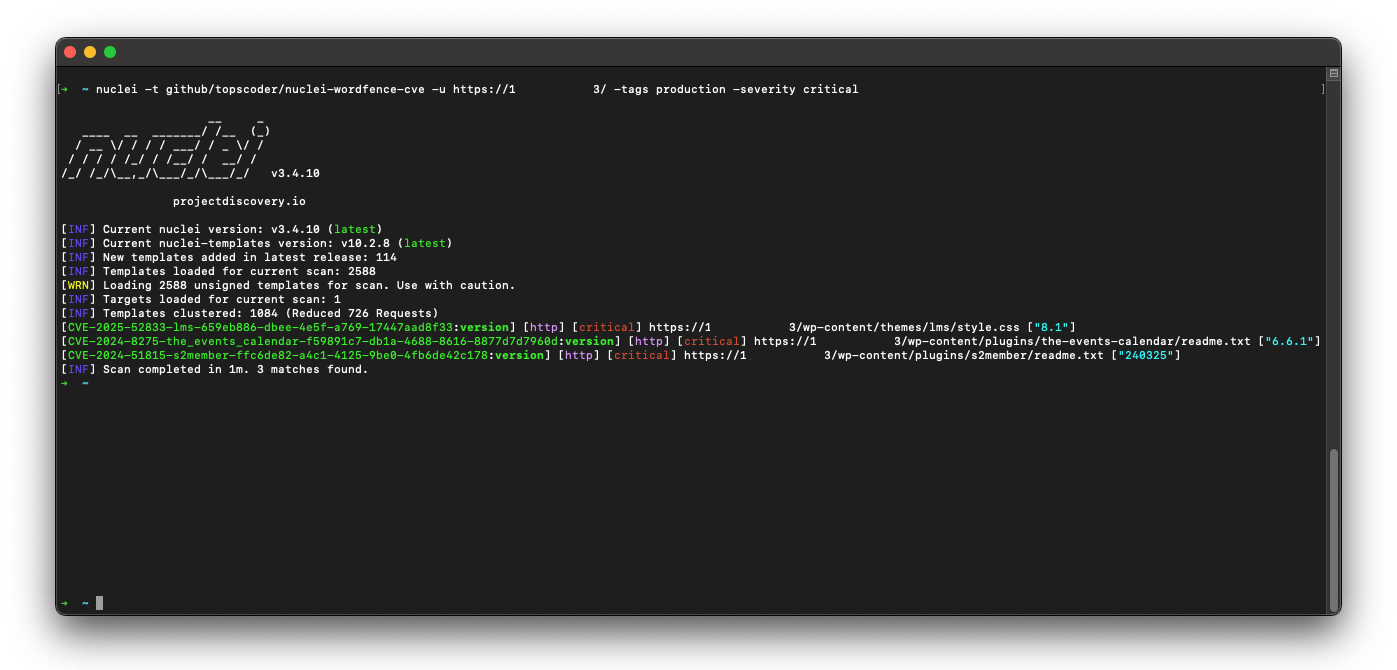
Project Demo

Level up your WordPress security game! This project's got a treasure trove of fresh Nuclei templates for WordPress. Scan for weaknesses in Core, plugins, and themes – all based on the latest intel from Wordfence.com.

Here's why this is your new best friend:

  • Massive collection: No more hunting for individual templates, you've got a whole arsenal at your fingertips.
  • Always on point: These templates stay updated with the freshest threats, so you're never behind the curve.
  • Open source magic: Need to tweak a template for a specific situation? No problem, you've got full control.

If you're guarding a WordPress site, this project is your secret weapon to identify vulnerabilities before the bad guys do. Stop wasting time and secure your sites like a pro!


[!TIP] If you found this project helpful, please consider buying me a coffee.

Buy Me A Coffee

✨ What's in it?!

categorytotal
wp-plugins83,883
wp-themes6,286
wp-core788
other0
severitytotal
critical8,859
high16,247
medium23,786
low42,059
info0

🚀 Quick Start

To install this nuclei-wordfence-cve repository for use with Nuclei, you can use the following commands:

export GITHUB_TEMPLATE_REPO=topscoder/nuclei-wordfence-cve
nuclei -update-templates

Once you have installed this template repo using the commands above, you can run the following command to scan for vulnerabilities using Nuclei:

nuclei -t github/topscoder/nuclei-wordfence-cve -u https://target.com

Wordfence provides two separate feeds for vulnerabilities. The first feed includes only production vulnerabilities, each with an assigned CVE. The second feed contains candidate vulnerabilities, which do not yet have a CVE assigned and may or may not be promoted to the production feed. To differentiate templates generated from these feeds, a tag is assigned to each template—either production or candidate—allowing you to target them using a tag filter.

Include only production templates:

nuclei -t github/topscoder/nuclei-wordfence-cve -tags production -u https://target.com

Include only candidate templates:

nuclei -t github/topscoder/nuclei-wordfence-cve -tags candidate -u https://target.com

💻 Examples

Here are some examples how to use the templates:

  • To scan for all known vulnerabilities in WordPress, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -u https://target.com
  • To scan for a CVE specific vulnerability, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -template-id cve-2023-32961 -u https://target.com
  • To scan only for critical vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -severity critical -u https://target.com
  • To scan only for WordPress core vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-core -u https://target.com
  • To scan only for WordPress plugin vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-plugin -u https://target.com
  • To scan only for WordPress theme vulnerabilities, you can run the following command:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-theme -u https://target.com
  • To go wild, you can combine and combine and combine:
nuclei -t github/topscoder/nuclei-wordfence-cve -tags wp-plugin,wp-theme -severity critical,high
  • To go even wilder, you can use the template condition flag (-tc) that allows complex expressions like the following ones:
nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'cross-site scripting') || contains(to_upper(name),'XSS')" -u https://target.com

nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'sql injection') || contains(to_lower(description),'sql injection')" -u https://target.com

nuclei -t github/topscoder/nuclei-wordfence-cve -template-condition "contains(to_lower(name),'file inclusion') || contains(to_lower(description),'file inclusion')" -u https://target.com

Télécharger l’outil

Populaires

Voir tout →

Découvrez les outils les plus utilisés par notre communauté.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 La boîte à outils OSINT ultime : graphe d'enquête, notation de confiance, familles d'alias, carte, chronologie et rapports. 49 modules, plus de 400 sites, aucune clé API requise.

    576
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Application d'exécution en un clic GhostLock (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    Plateforme autonome de tests d'intrusion multi-agents basée sur des LLM, avec agents planificateur/ouvrier, graphes d'actifs et d'exploration, enregistrement du trafic MITM et retest des vulnérabilités.

    388
  • 4

    redforge

    cybersecurity91/redforge

    Boîte à outils red team côté navigateur avec 102 outils hors ligne pour la reconnaissance, la génération de payloads, les attaques par identifiants, la cryptographie, l'encodage et le reporting d'engagement.

    330
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    Le système d'action pour la cybersécurité native IA—où l'intention devient une exécution gouvernée, les preuves deviennent une mémoire opérationnelle, et chaque opération améliore la suivante.

    255
  • 6

    antifox

    antifox-ai/antifox

    Plateforme de test d'intrusion autonome multi-agents par IA qui exécute la reconnaissance, la découverte de la surface d'attaque, la validation de l'exploitation et la livraison de rapports étayés par des preuves.

    247

Explorer tous les outils

Parcourez notre collection d'outils

Voir tous les outils →