Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Mécanismes de Persistance — Page 24 | Kitploit
Catégories

Mécanismes de Persistance

Outils pour maintenir un accès à long terme aux systèmes compromis, même après les redémarrages.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
Empire preview#1

Empire

GitHubbc-security/empire
5.2kil y a 1 mois
sliver preview#2

sliver

GitHubbishopfox/sliver
11.7kil y a 11h 15m
Mythic preview#3

Mythic

GitHubits-a-feature/mythic
4.7kil y a 10 jours
Seatbelt preview#7

Seatbelt

GitHubghostpack/seatbelt
4.7kil y a 1 an
SharpDPAPI preview#8

SharpDPAPI

GitHubghostpack/sharpdpapi
1.4kil y a 2 ans
NetExec preview#9

NetExec

GitHubpennyw0rth/netexec
5.8kil y a 19h 6m
impacket preview#10

impacket

GitHubfortra/impacket
16.0kil y a 20h 49m
mimikatz preview#11

mimikatz

GitHubgentilkiwi/mimikatz
21.8kil y a 6 mois
emp3r0r preview#13

emp3r0r

GitHubjm33-m0/emp3r0r
1.7kil y a 6 jours
merlin preview#14

merlin

GitHubne0nd0g/merlin
5.6kil y a 7 jours
Plus récentsPertinencePlus populairesMis à jour récemment
508 résultats
Flowise-CVE-2026-58057-exploit preview

Flowise-CVE-2026-58057-exploit

GitHubcerberusmrxi/flowise-cve-2026-58057-exploit

Exploit RCE Windows pour Flowise, ciblant CVE-2026-58057. Contourne la validation des variables d'environnement grâce à une faille de sensibilité à…
persistence-mechanismsvulnerability-analysisexploitation+7
1il y a 3 mois
hp-slate7-root-kit preview

hp-slate7-root-kit

GitHubvalentineus/hp-slate7-root-kit

Kit de root pour HP Slate 7 2800 sous Android 4.1.1 utilisant CVE-2015-1805.

android-securityprivilege-escalationpersistence-mechanisms+6
1il y a 2 mois
CVE-2022-34301 preview

CVE-2022-34301

GitHubthemalwareguardian/cve-2022-34301

Démontre le contournement de Secure Boot CVE-2022-34301 via le UEFI Shell signé Eurosoft (esdiags.efi), en utilisant la commande mm pour annuler…
persistence-mechanismsvulnerability-analysisexploitation+4
1il y a 1 mois
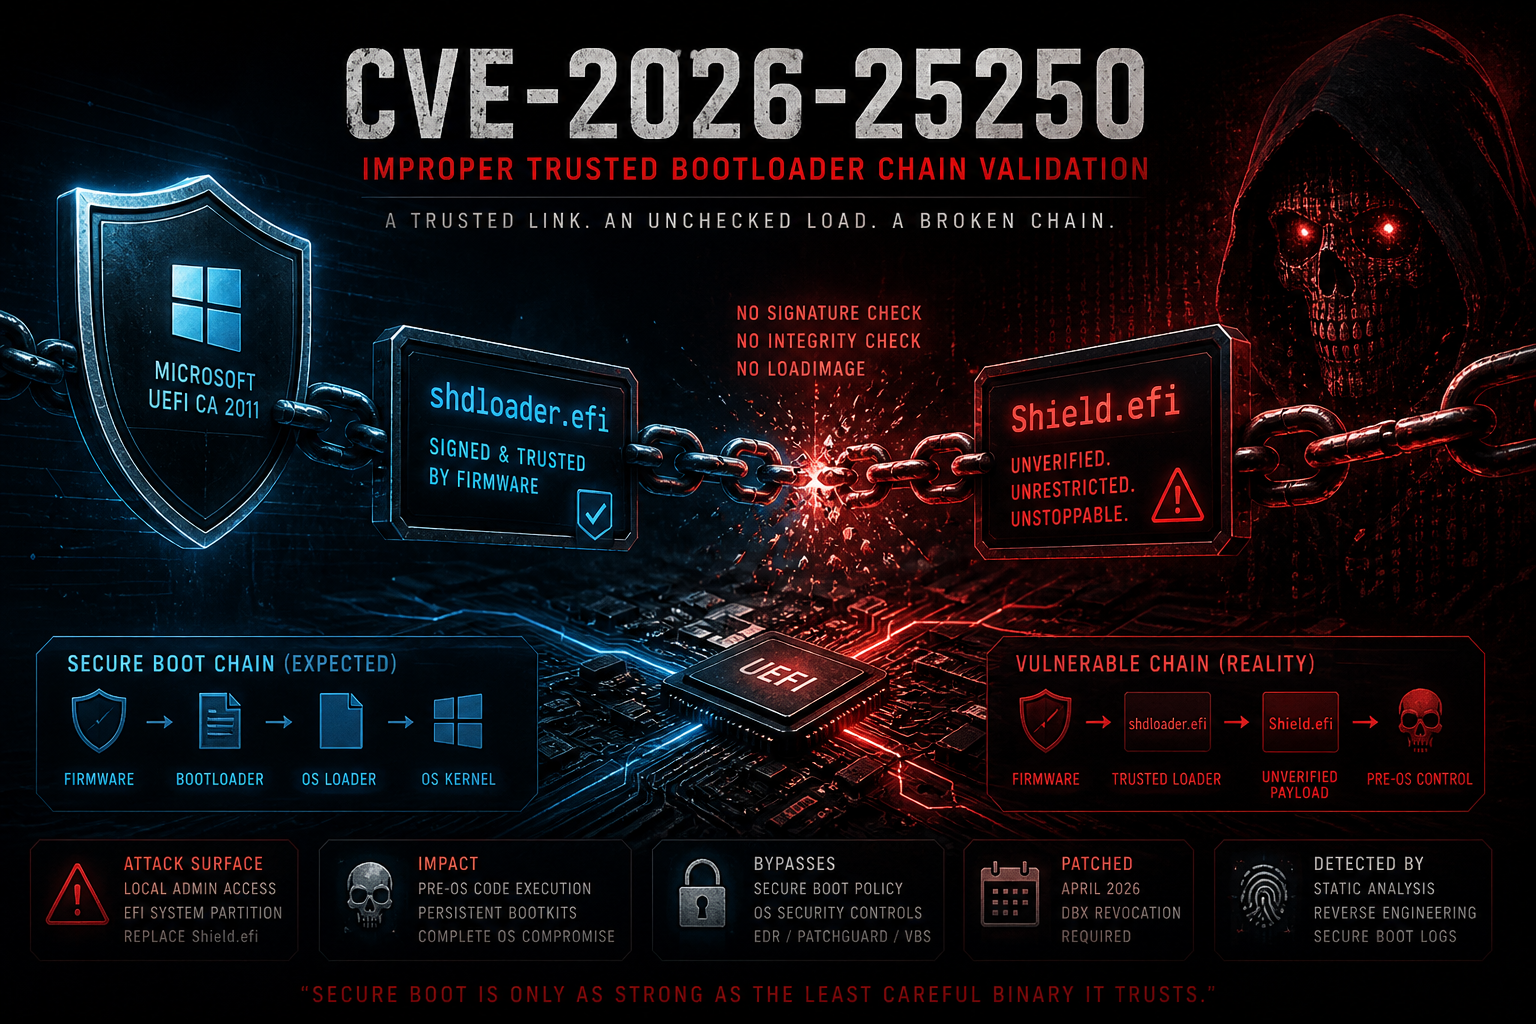
CVE-2026-25250 preview

CVE-2026-25250

GitHubthemalwareguardian/cve-2026-25250

Analyse et exploitation de la CVE-2026-25250, un contournement de Secure Boot dans Horizon DataSys Reboot Restore où shdloader.efi charge Shield.efi…
persistence-mechanismsvulnerability-analysisexploitation+3
1il y a 2 mois
Project-CVE-2026-33017 preview

Project-CVE-2026-33017

GitHube4zyy/project-cve-2026-33017

CVE-2026-33017 - Exploit RCE non authentifié de Langflow
reconnaissancepersistence-mechanismsvulnerability-analysis+6
1il y a 1 mois
WinRAR-CVE-2025-8088-Path-Traversal-PoC preview

WinRAR-CVE-2025-8088-Path-Traversal-PoC

GitHubpexlexity/winrar-cve-2025-8088-path-traversal-poc

Preuve de concept pour la vulnérabilité CVE-2025-8088 dans WinRAR (traversée de chemin via ADS)

persistence-mechanismsvulnerability-analysisexploitation+3
2il y a 1 an
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

Analyse de rétro-ingénierie de RedLine Stealer, un voleur d'informations basé sur .NET qui utilise des domaines C2 (198.46.86.63, tempuri.org), un…
memory-forensicspersistence-mechanismsreverse-engineering+4
1il y a 2 mois
ExtensionHijack preview

ExtensionHijack

GitHubal1ex/extensionhijack

ExtensionHijack

persistence-mechanismspost-exploitationred-teaming
2il y a 6 ans
Windows-Defender-Security-Auditor-CVE-2026-50656- preview

Windows-Defender-Security-Auditor-CVE-2026-50656-

GitHubeh-amish/windows-defender-security-auditor-cve-2026-50656-

Auditeur de sécurité PowerShell en lecture seule pour les postes de travail et serveurs Windows : vérifie la configuration de Defender, l'état des…
defensive-toolsioc-managementpersistence-mechanisms+8
1il y a 2 mois
CVE-2024-54085 preview

CVE-2024-54085

GitHubmr-zapi/cve-2024-54085

Juste un PoC pour CVE 2024-54085
authentication-authorizationembedded-systems-securitypersistence-mechanisms+5
2il y a 1 an
CVE-2025-8088-Winrar preview

CVE-2025-8088-Winrar

GitHubundefined-name12/cve-2025-8088-winrar

Outil avancé d'exploitation de traversée de chemin WinRAR pour CVE-2025-8088
payload-generationpersistence-mechanismsvulnerability-analysis+3
2il y a 8 mois
Exploit-CVE-2014-4210- preview

Exploit-CVE-2014-4210-

GitHubzorvithonleo/exploit-cve-2014-4210-

Exploit pour CVE-2014-4210 ciblant la désérialisation WebLogic, avec des fonctionnalités post-exploitation, y compris le déploiement de ransomware,…
privilege-escalationpersistence-mechanismsexploitation+7
2il y a 1 an
CVE-2026-5027-Langflow preview

CVE-2026-5027-Langflow

GitHublayer-6/cve-2026-5027-langflow

Outil d'exploitation multi-CVE pour l'exécution de code à distance sans authentification sur Ivanti Sentry et FortiSandbox. Dispose d'un shell…

privilege-escalationpersistence-mechanismsvulnerability-analysis+8
il y a 4 mois
honda preview

honda

GitLabnu11secur1ty/0

Exploit pour une condition de concurrence dans Windows Defender qui élève les privilèges à SYSTEM via une utilisation après libération, fait planter…
privilege-escalationpersistence-mechanismsexploitation+3
il y a 4 mois
lenovo-a1000g-mt8317-A412_01_09_130907-kernel-3.4.0-root-cve-2016-5195 preview

lenovo-a1000g-mt8317-A412_01_09_130907-kernel-3.4.0-root-cve-2016-5195

GitHubvoidgguy/lenovo-a1000g-mt8317-a412_01_09_130907-kernel-3.4.0-root-cve-2016-5195

[Assisté par IA] Méthode de root pour Lenovo IdeaTab A1000G (MT8317, kernel 3.4.0, Android 4.1) via CVE-2016-5195 (Dirty COW)
android-securityprivilege-escalationpersistence-mechanisms+4
il y a 3 mois
cve-2025-57819-exploit preview

cve-2025-57819-exploit

GitHubits1zero/cve-2025-57819-exploit

# Exploit Python pour CVE-2025-57819 ciblant FreePBX via injection SQL non authentifiée pour obtenir une exécution de code à distance avec reverse…
persistence-mechanismsvulnerability-analysisexploitation+4
il y a 3 mois
chimera preview

chimera

GitHub1neptune/chimera

Chargeur de détournement de DLL basé sur Rust pour MobaXterm (CVE-2026-6421) avec persistance
privilege-escalationpersistence-mechanismsvulnerability-analysis+4
il y a 3 mois
Powershell-C2 preview

Powershell-C2

GitHubal1ex/powershell-c2

Powershell-C2

persistence-mechanismspost-exploitationcommand-and-control+2
1il y a 6 ans
Précédent1…232425…29Suivant