
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Sniffing et Analyse de Paquets — Page 12 | Kitploit
Catégories

Sniffing et Analyse de Paquets

Outils pour la capture, l'inspection et l'analyse du trafic réseau en temps réel ou à partir de fichiers de capture.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
wireshark preview#1

wireshark

GitHubwireshark/wireshark
10.1kil y a 15h 36m
scapy preview#2

scapy

GitHubsecdev/scapy
12.5kil y a 16h 48m
zeek preview#4

zeek

GitHubzeek/zeek
7.8kil y a 14h 16m
suricata preview#5

suricata

GitHuboisf/suricata
6.5kil y a 5 jours
ntopng preview#6

ntopng

GitHubntop/ntopng
8.1kil y a 18h 17m
arkime preview#7

arkime

GitHubarkime/arkime
7.4kil y a 11h 6m
bettercap preview#8

bettercap

GitHubbettercap/bettercap
19.8kil y a 2 mois
netsniff-ng preview#9

netsniff-ng

GitHubnetsniff-ng/netsniff-ng
1.4kil y a 1 an
libpcap preview#10

libpcap

GitHubthe-tcpdump-group/libpcap
3.2kil y a 0 jours
gopacket preview#11

gopacket

GitHubgoogle/gopacket
6.8kil y a 1 an
Plus récentsPertinencePlus populairesMis à jour récemment
396 résultats
Conveigh preview

Conveigh

GitHubkevin-robertson/conveigh

Conveigh est un outil de détection de spoofing LLMNR/NBNS pour Windows PowerShell.
packet-sniffing-analysisreconnaissancenetwork-security+3
99il y a 10 ans
packETH preview

packETH

GitHubjemcek/packeth

Générateur de paquets Ethernet
packet-sniffing-analysisfuzzingnetwork-security+1
133il y a 1 an
hdmi-sniff preview

hdmi-sniff

GitHubadamlaurie/hdmi-sniff

renifler le trafic HDMI DDC (I2C)
embedded-systems-securitypacket-sniffing-analysisreverse-engineering+4
95il y a 12 ans
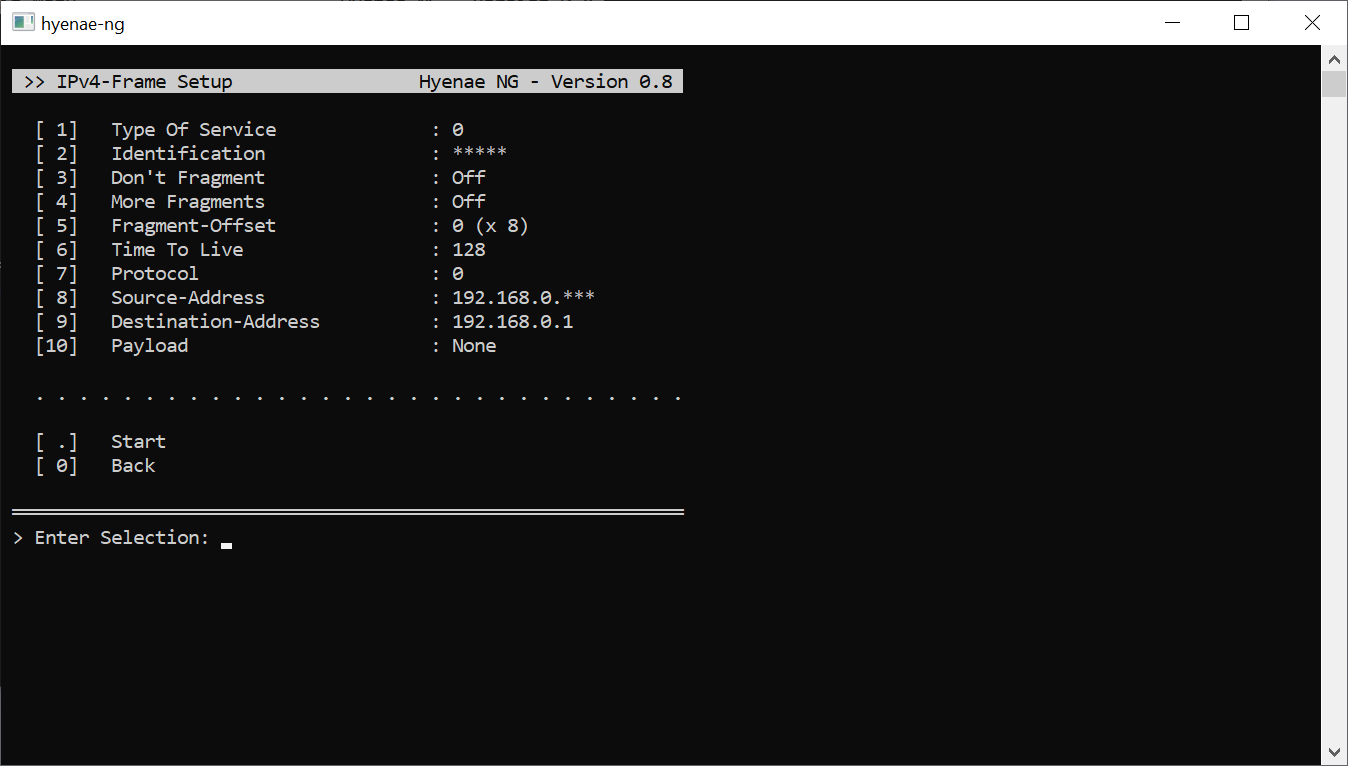
hyenae-ng preview

hyenae-ng

GitHubr-richter/hyenae-ng

Générateur de paquets réseau multiplateforme avec usurpation complète de couche, randomisation d'adresse basée sur des motifs et évasion de détection…
packet-sniffing-analysisfuzzingnetwork-security+1
133il y a 6 ans
sslnuke preview

sslnuke

GitHubjtripper/sslnuke

Proxy transparent qui déchiffre le trafic SSL et affiche les messages IRC.
packet-sniffing-analysisweb-proxies-interceptionids-ips-evasion+3
77il y a 13 ans
Preferred-Network-List-Sniffer preview

Preferred-Network-List-Sniffer

GitHubaleksamcode/preferred-network-list-sniffer

Un outil de reconnaissance pour capturer et afficher les SSIDs à partir de la liste des réseaux préférés de l'appareil.
packet-sniffing-analysisreconnaissancewi-fi-auditing+3
175il y a 9 mois
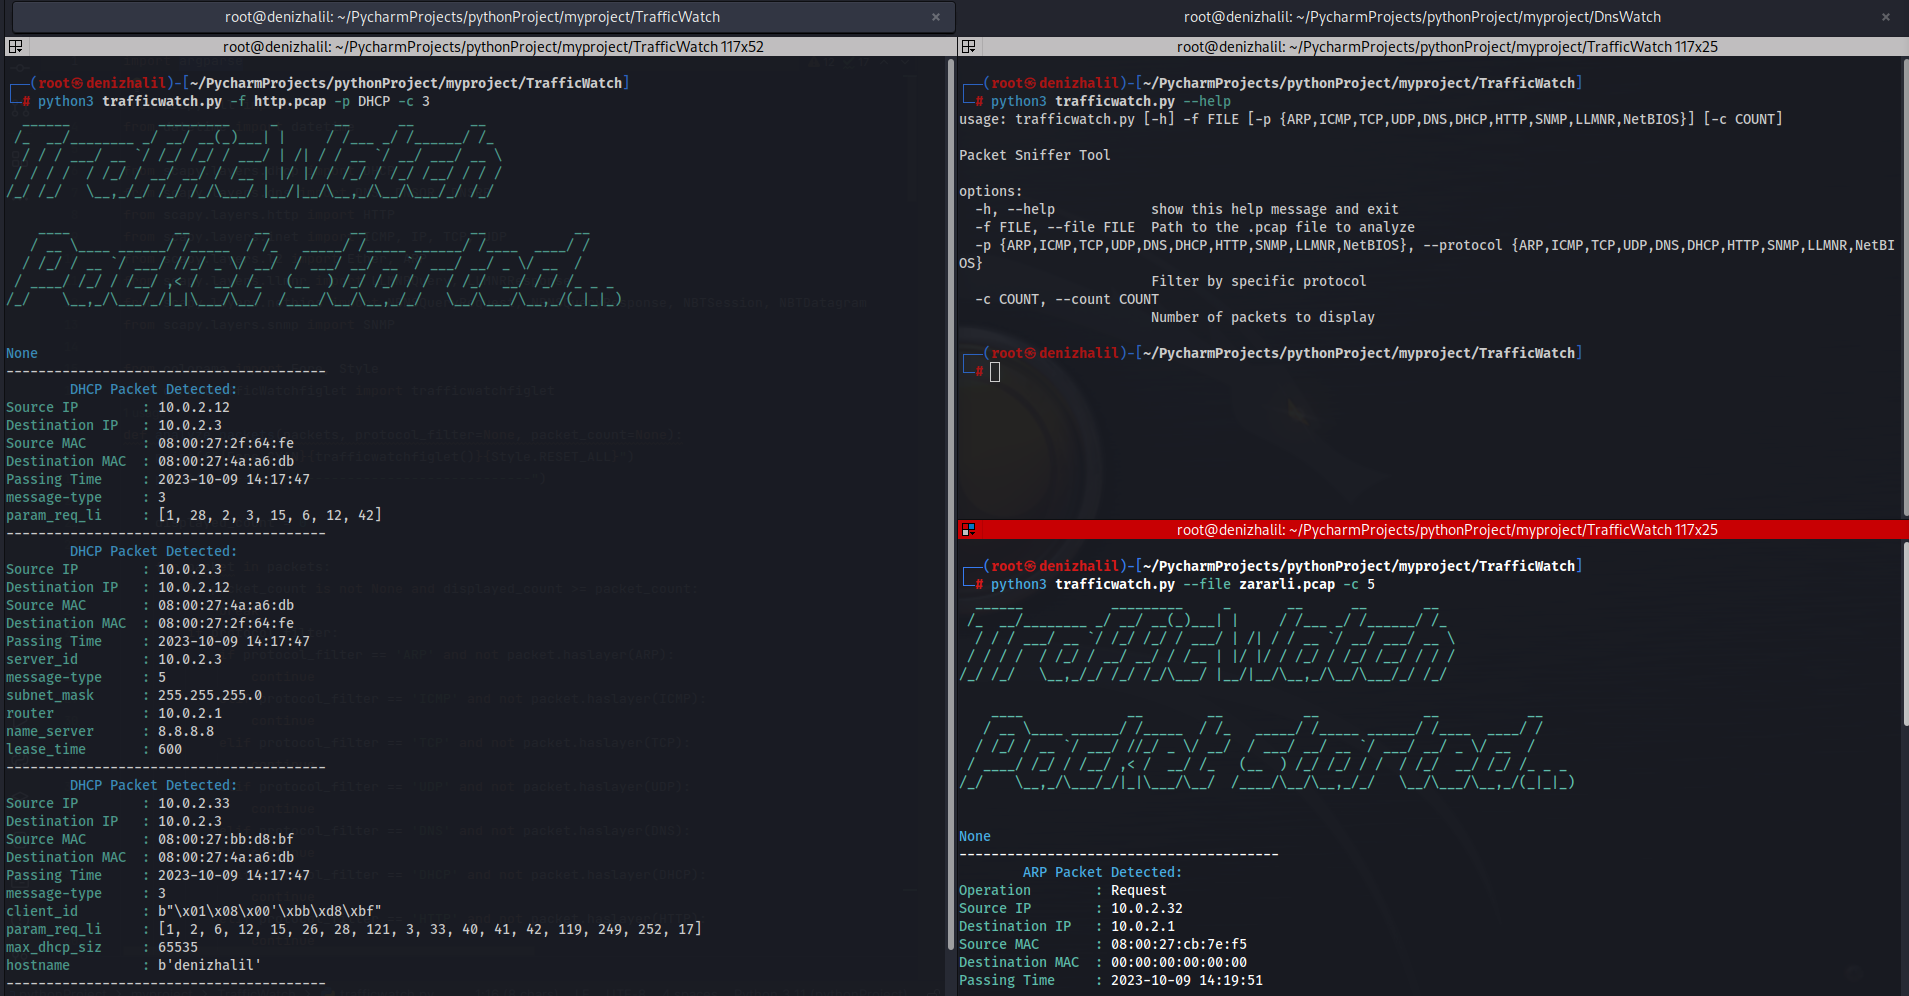
TrafficWatch preview

TrafficWatch

GitHubhalildeniz/trafficwatch

Renifleur et analyseur de paquets basé sur PCAP supportant l'inspection des protocoles ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR et NetBIOS…
packet-sniffing-analysisnetwork-mappinginformation-gathering+1
137il y a 2 ans
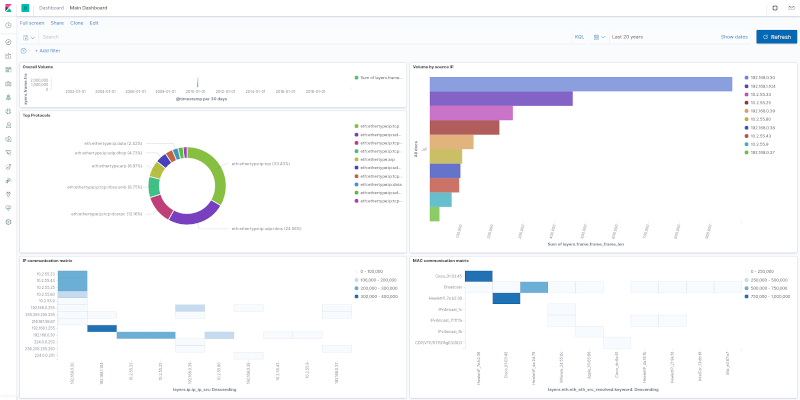
tsharkVM preview

tsharkVM

GitHubh21lab/tsharkvm

Machine virtuelle d'analyse tshark + ELK
packet-sniffing-analysisvulnerability-analysisnetwork-security+3
68il y a 7 mois
eavesarp preview

eavesarp

GitHubimpostorkeanu/eavesarp

Analyser les requêtes ARP pour identifier les hôtes communicants et les configurations d'adresses réseau obsolètes (SNACs)

packet-sniffing-analysisreconnaissanceinformation-gathering+2
68il y a 4 ans
flowinspect preview

flowinspect

GitHub7h3ram/flowinspect

Un outil d'inspection réseau
packet-sniffing-analysisvulnerability-analysisshellcode+5
82il y a 9 ans
arp-validator preview

arp-validator

GitHubrnehra01/arp-validator

Outil de sécurité pour détecter les attaques par empoisonnement ARP
defensive-toolspacket-sniffing-analysisnetwork-security+1
54il y a 8 ans
minipwner preview

minipwner

GitHubnicholasadamou/minipwner

Un script pour configurer un TP-Link MR3040 exécutant OpenWRT en une "dropbox" de test d'intrusion simple mais puissante.

packet-sniffing-analysisphishing-toolsreconnaissance+8
73il y a 1 an
phantom-grid preview

phantom-grid

GitHubhaidang-infosec/phantom-grid

Un système de défense active propulsé par eBPF qui transforme votre serveur Linux en un honeypot trompeur. Il propose une redirection transparente du…
authentication-authorizationdefensive-toolspacket-sniffing-analysis+7
77il y a 3 mois
thelightscope preview

thelightscope

GitHubthelightscope/thelightscope

TheLightScope
defensive-toolspacket-sniffing-analysisnetwork-mapping+5
69il y a 12 jours
Dosinator preview

Dosinator

GitHubhalildeniz/dosinator

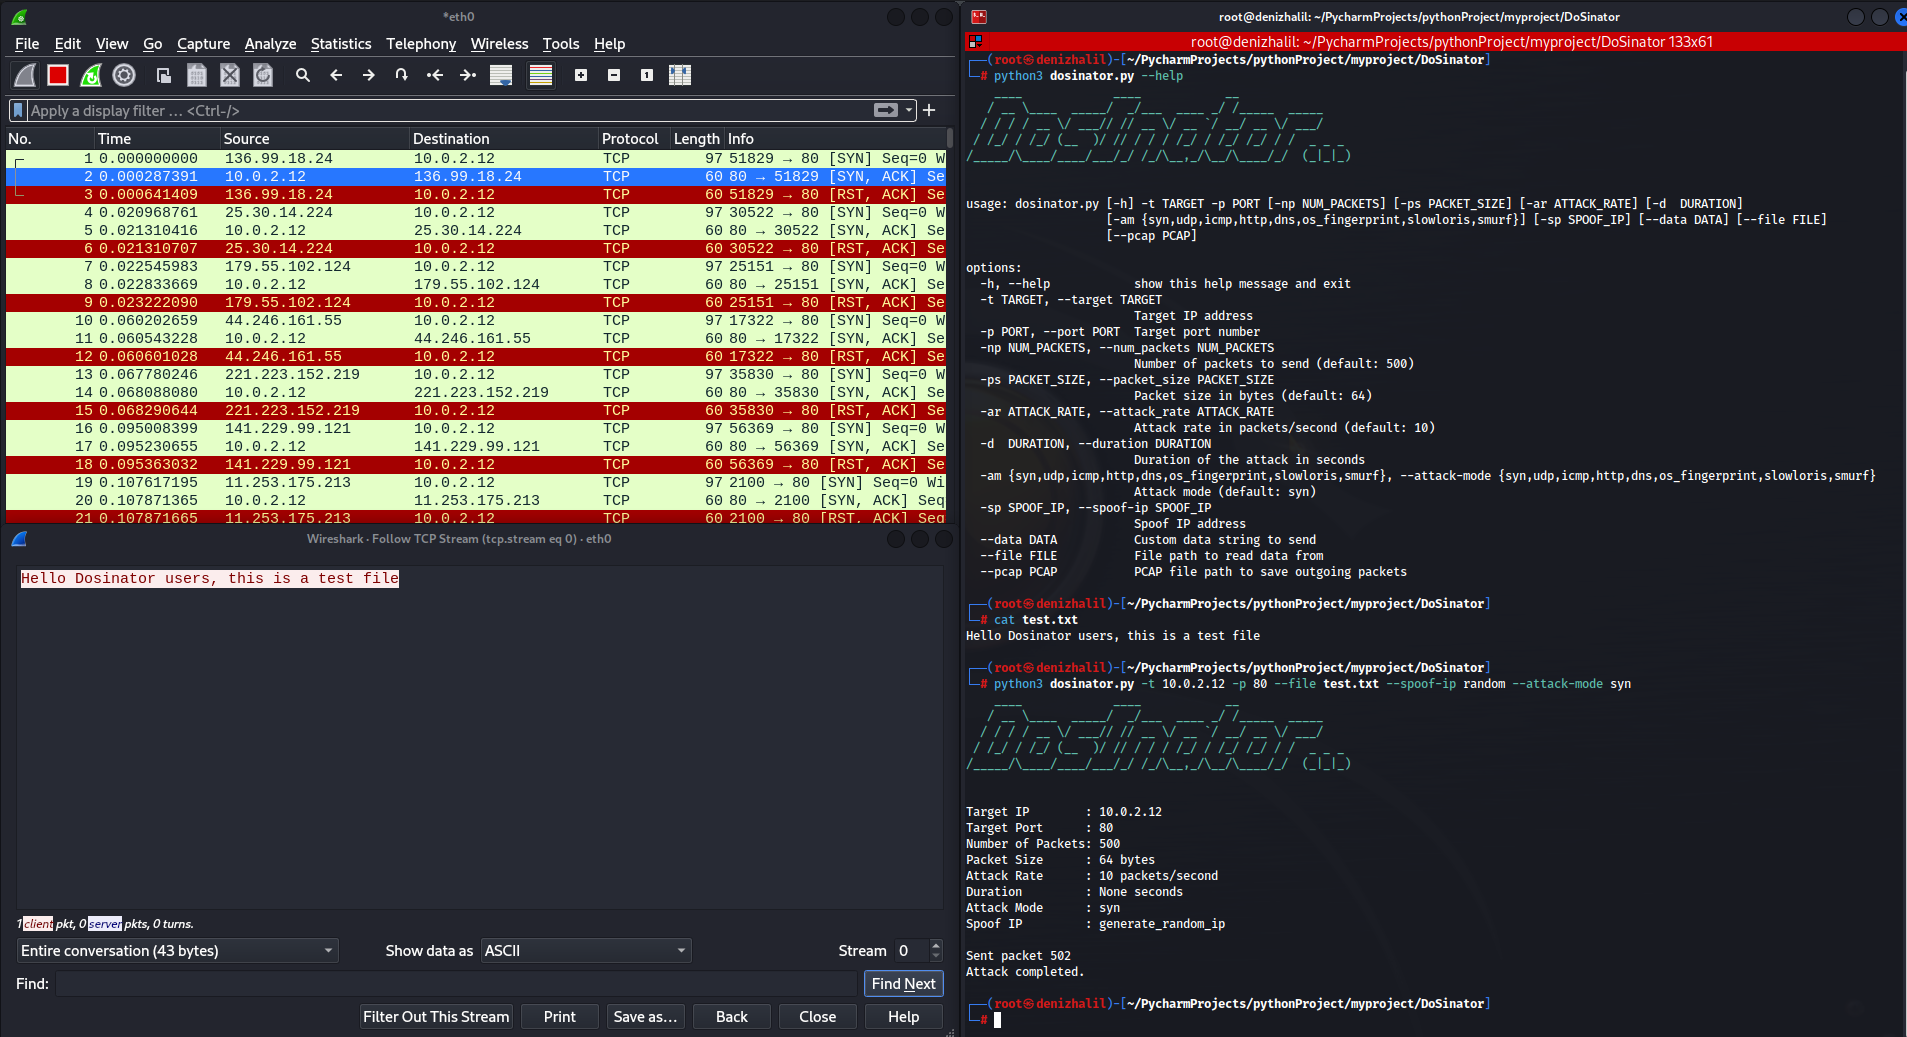
DoSinator est un puissant outil de test de déni de service (DoS) développé en Python.
packet-sniffing-analysisexploitationinformation-gathering+3
144il y a 2 ans
airpydump preview

airpydump

GitHubhash3lizer/airpydump

Analysez les paquets sans fil à la volée. Prend actuellement en charge trois Modes de fonctionnement (Reader, Live, Stealth).
packet-sniffing-analysisinformation-gatheringnetwork-security+1
53il y a 8 ans
challack preview

challack

GitHubjduck/challack

Code d'exploit de preuve de concept pour CVE-2016-5696
packet-sniffing-analysisvulnerability-analysisexploitation+3
76il y a 10 ans
usbsnoop preview

usbsnoop

GitHubyeet-src/usbsnoop

Sniffer de transferts USB en direct et à l'échelle du système en eBPF — décode le trafic USB en ligne (SETUP de contrôle, SCSI, HID) à partir de deux…


embedded-systems-securitypacket-sniffing-analysisdynamic-analysis-sandboxing+7
85il y a 2 mois
Précédent1…111213…22Suivant






