awesome-incident-response
Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
Short editorial updates from published cybersecurity tools.

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…

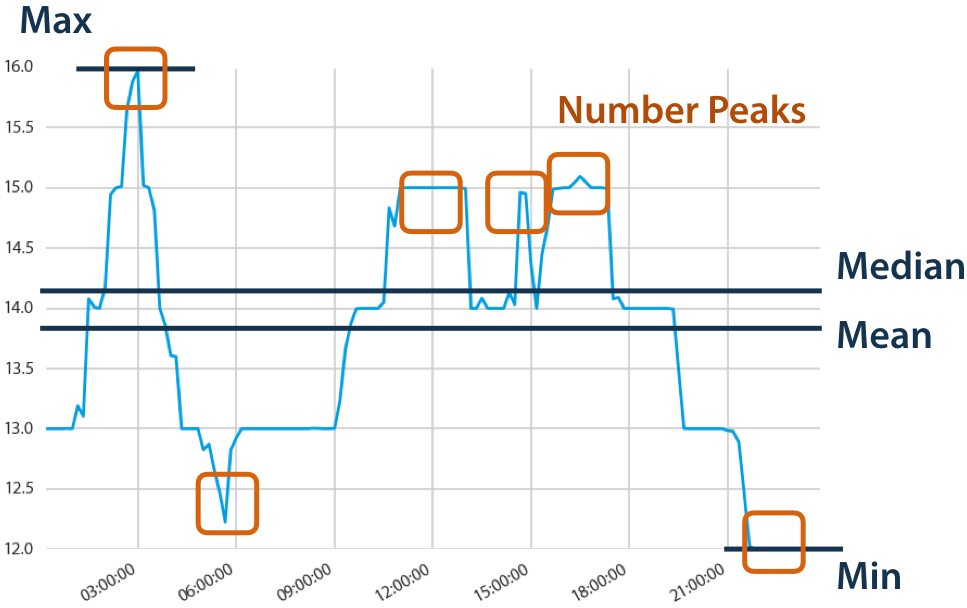
Automatic extraction of relevant features from time series:

Protocol client and CLI framework for interacting with wireless hacking devices, enabling security researchers to explore, test, and automate…

An Android NFC app for reading, writing, analyzing, etc. MIFARE Classic RFID tags.

Bluetooth Low Energy (BLE) packet sniffer and transmitter for both standard and non standard (raw bit) based on Software Defined Radio (SDR).

Angry IP Scanner - fast and friendly network scanner

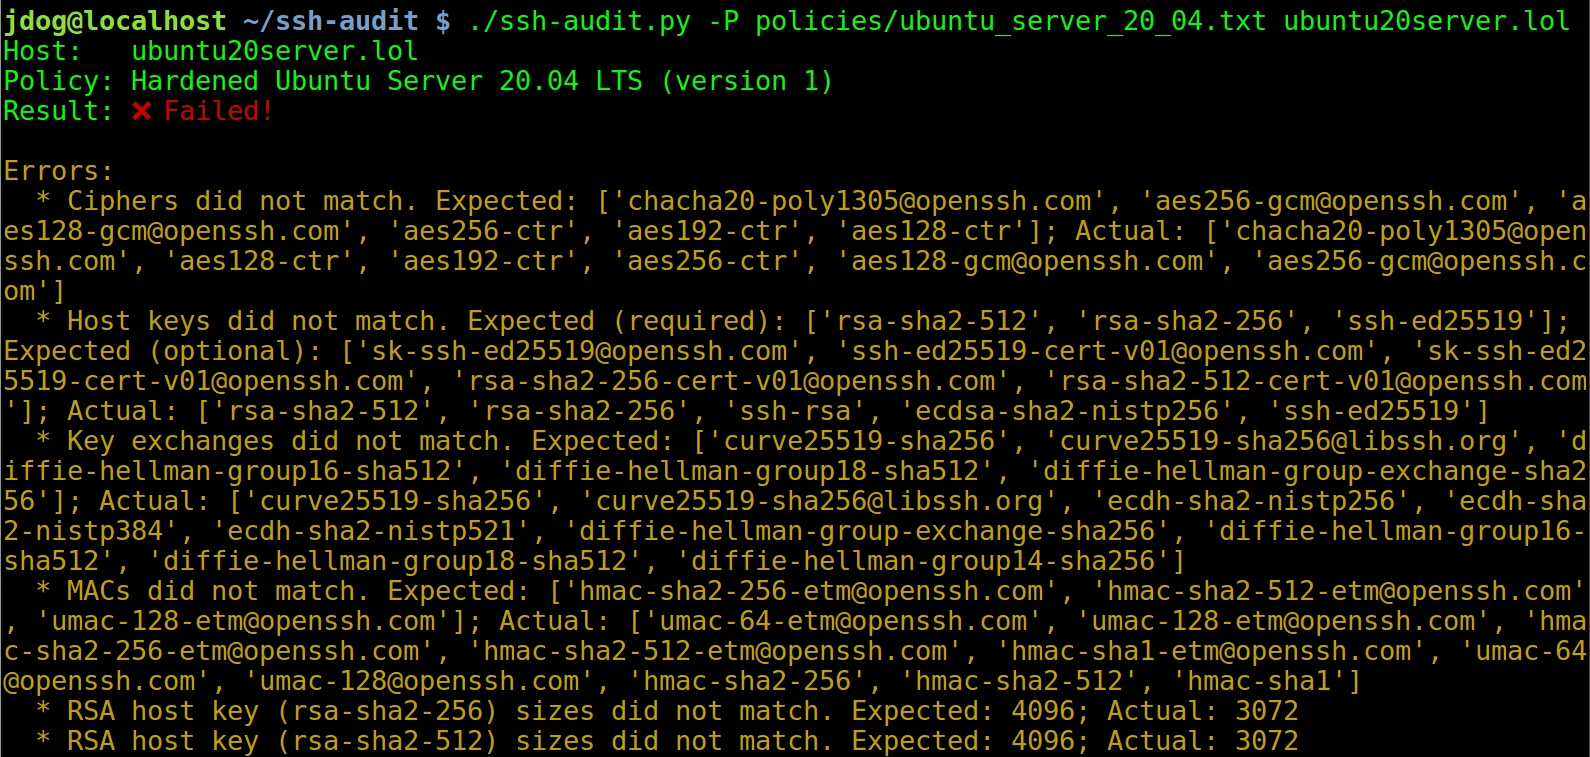
SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)

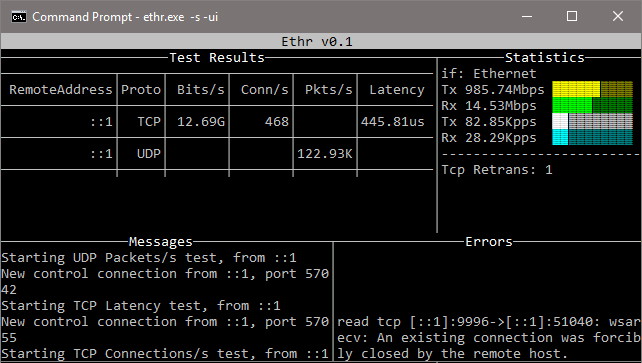
Cross-platform CLI for network performance testing over TCP, UDP, HTTP, HTTPS, and ICMP: bandwidth, connections/s, packets/s, latency, loss, jitter,…

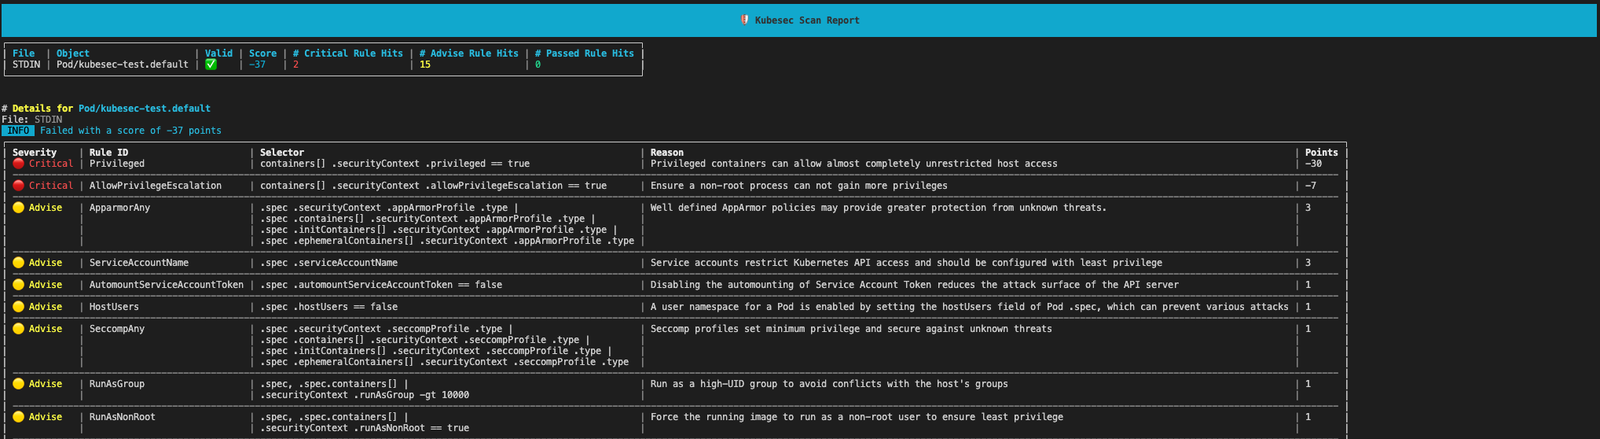
Security risk analysis for Kubernetes resources

A machine learning tool that ranks strings based on their relevance for malware analysis.

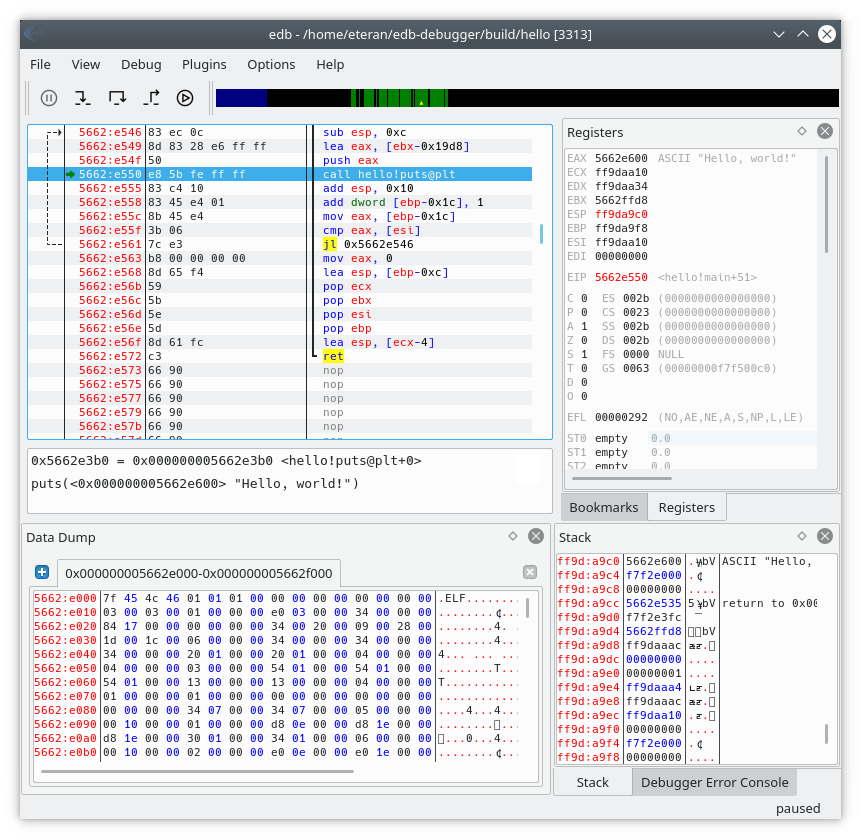
edb is a cross-platform AArch32/x86/x86-64 debugger.

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…