
New tool22 days ago
LiME
 jtsylve/lime
Kernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
Memory ForensicsForensicsMobile Forensics+2
Short editorial updates from published cybersecurity tools.
jtsylve/limeKernel module for volatile memory acquisition from Linux and Android devices, producing forensically sound captures to disk or over the network.
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 vatsal200600/stegolab
All-in-one Image Steganography Toolkit for CTFs & Forensics
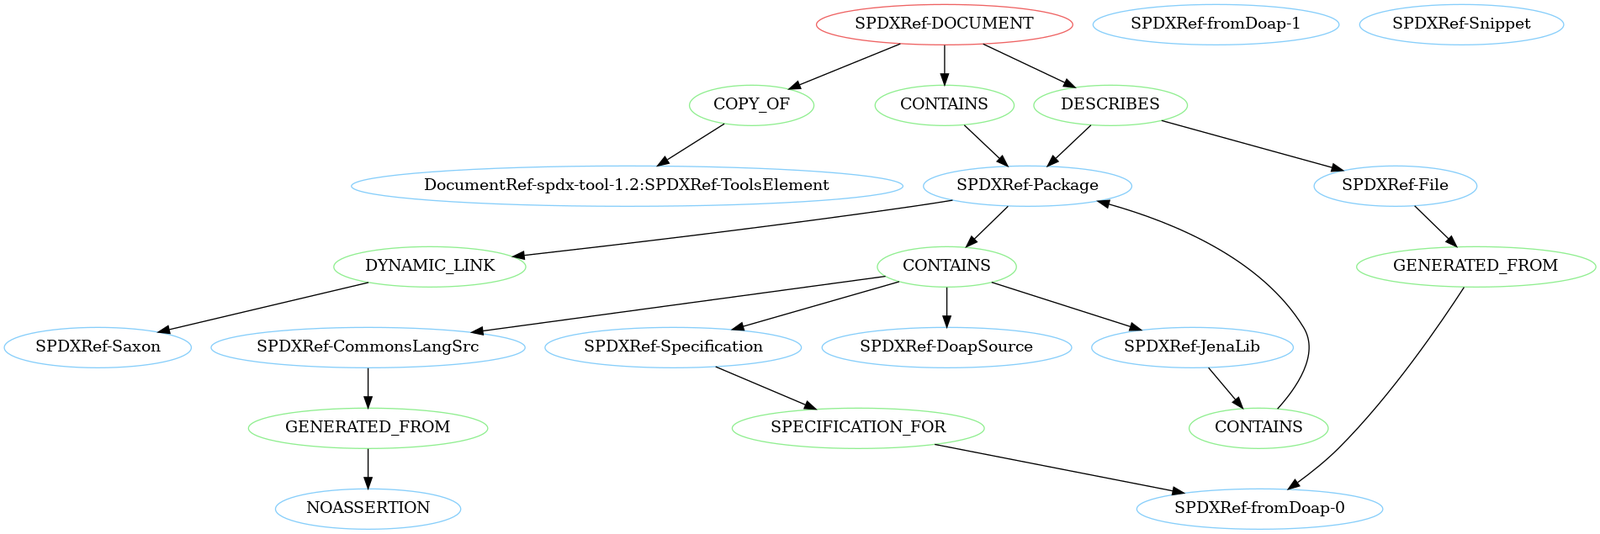 spdx/tools-python
A Python library to parse, validate and create SPDX documents.
 aydinnyunus/ai-captcha-bypass
Automates CAPTCHA solving with multimodal AI models (GPT-4o, Gemini) and Selenium, supporting text, audio, slider puzzles, and reCAPTCHA v2 via a…
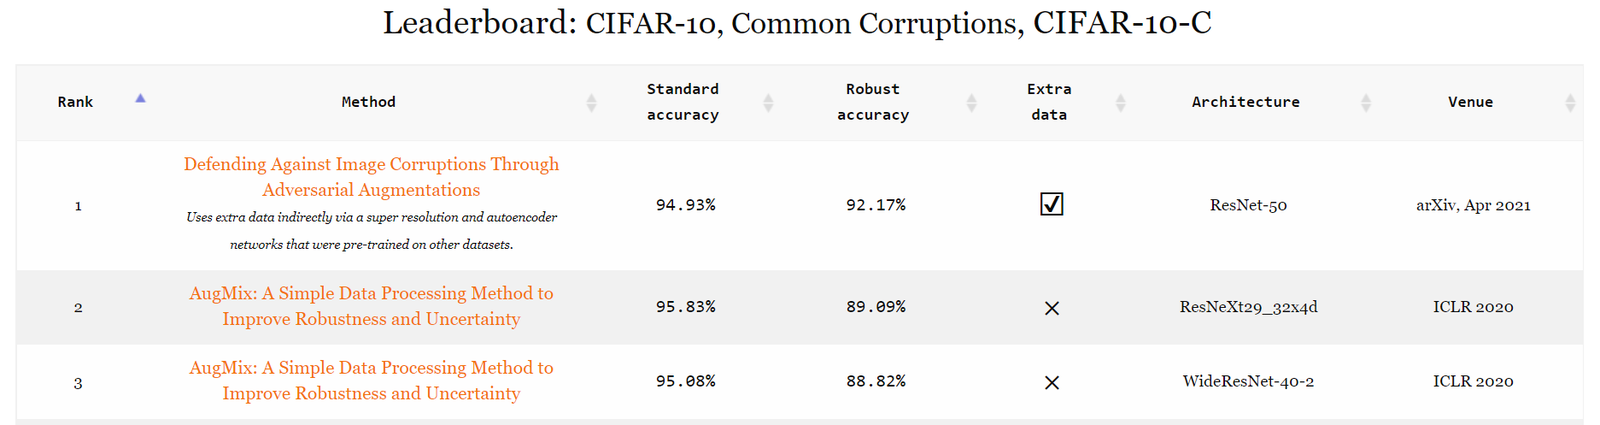 robustbench/robustbench
Standardized adversarial robustness benchmark with a public leaderboard and downloadable model zoo for evaluating ML models against Lp attacks and…
 wireguard/wireguard-tools
Cross-platform command-line tools for configuring WireGuard VPN tunnels, offering key generation, peer management, and quick interface setup via wg…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 dirkjanm/krbrelayx
Kerberos relaying and unconstrained delegation abuse toolkit
 snort3/snort3
Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…