CVE-2025-69212-for-myself
Proof-of-concept exploit for CVE-2025-69212 that authenticates to a URL with admin credentials and triggers a reverse shell to the specified attacker…
Short editorial updates from published cybersecurity tools.

Proof-of-concept exploit for CVE-2025-69212 that authenticates to a URL with admin credentials and triggers a reverse shell to the specified attacker…

Enhanced SSH client with TUI — manage connections, keys, and sessions

Deliberately insecure Ruby on Rails application designed for studying OWASP Top 10 vulnerabilities and practicing web application security testing…

Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.

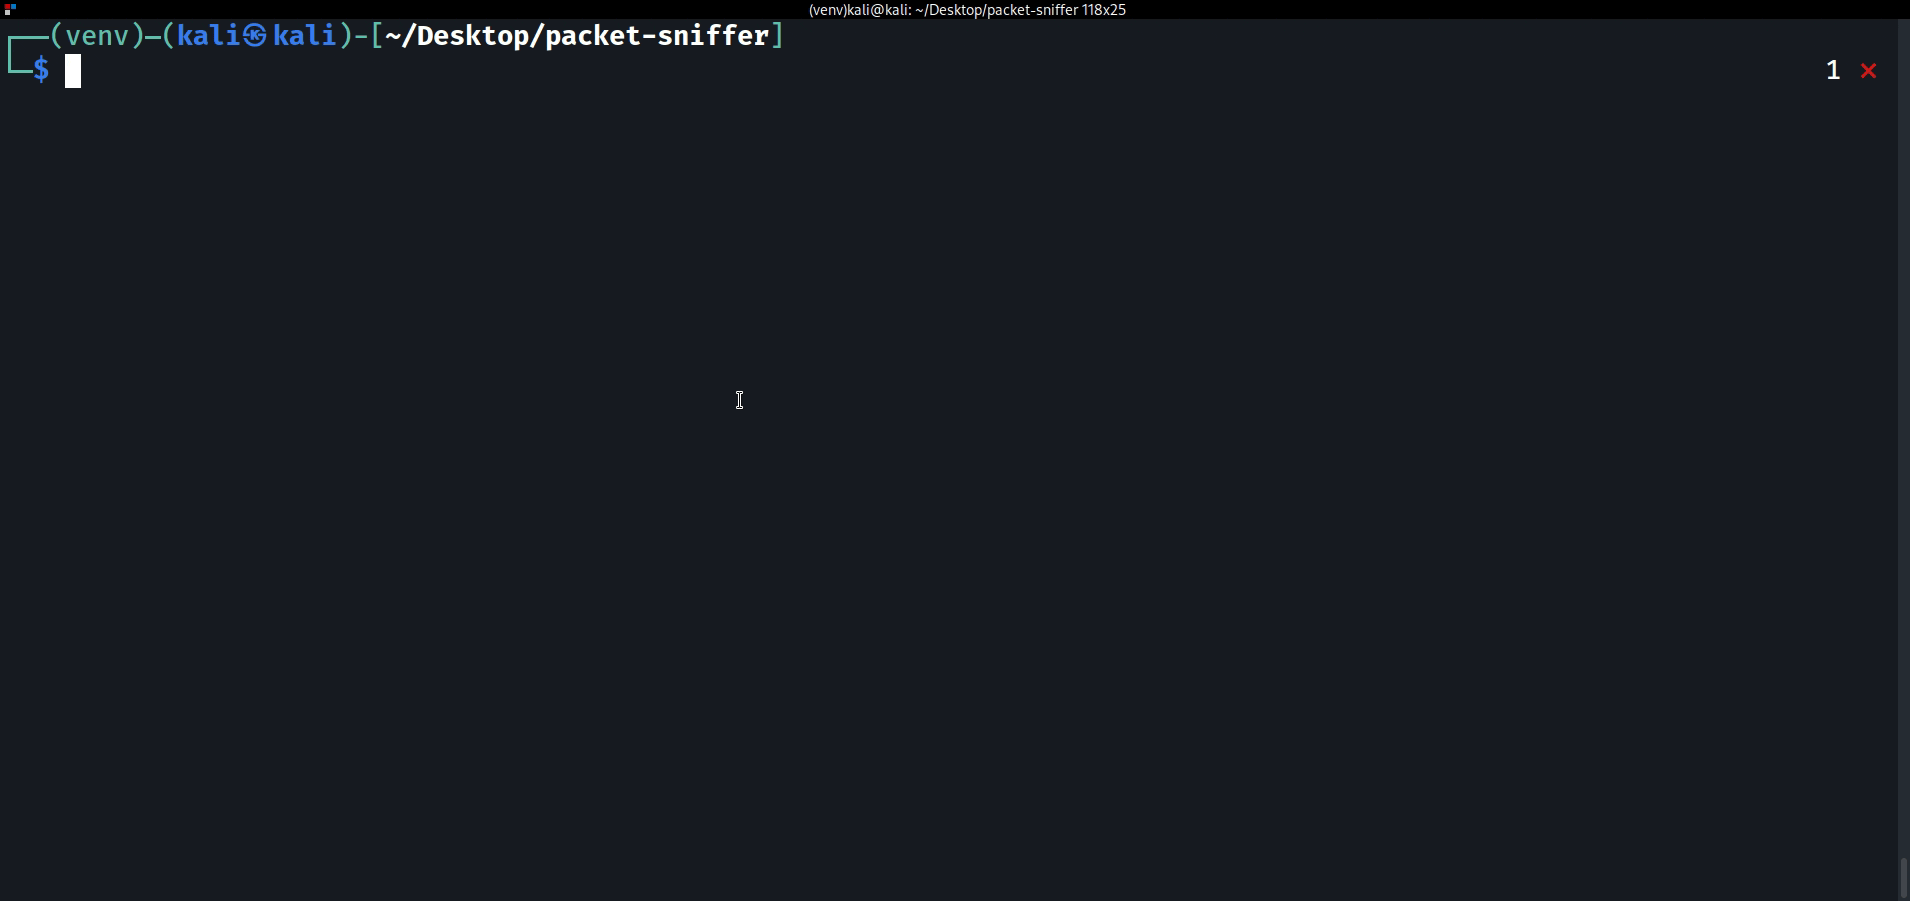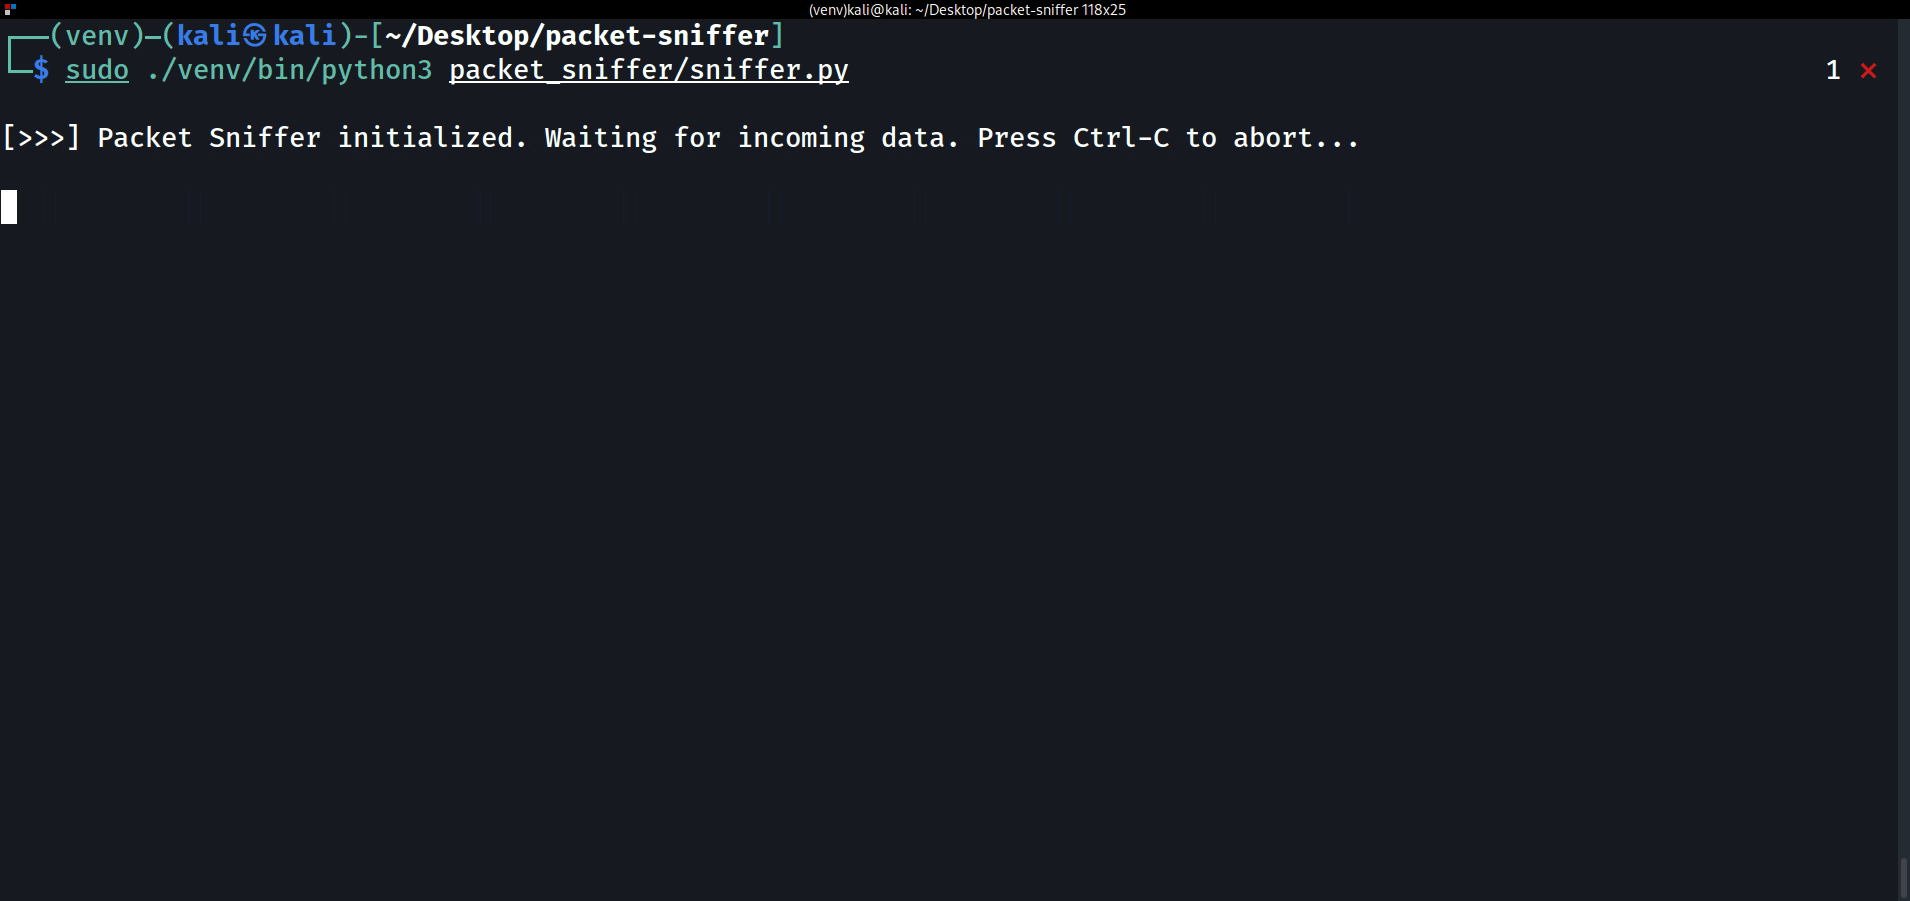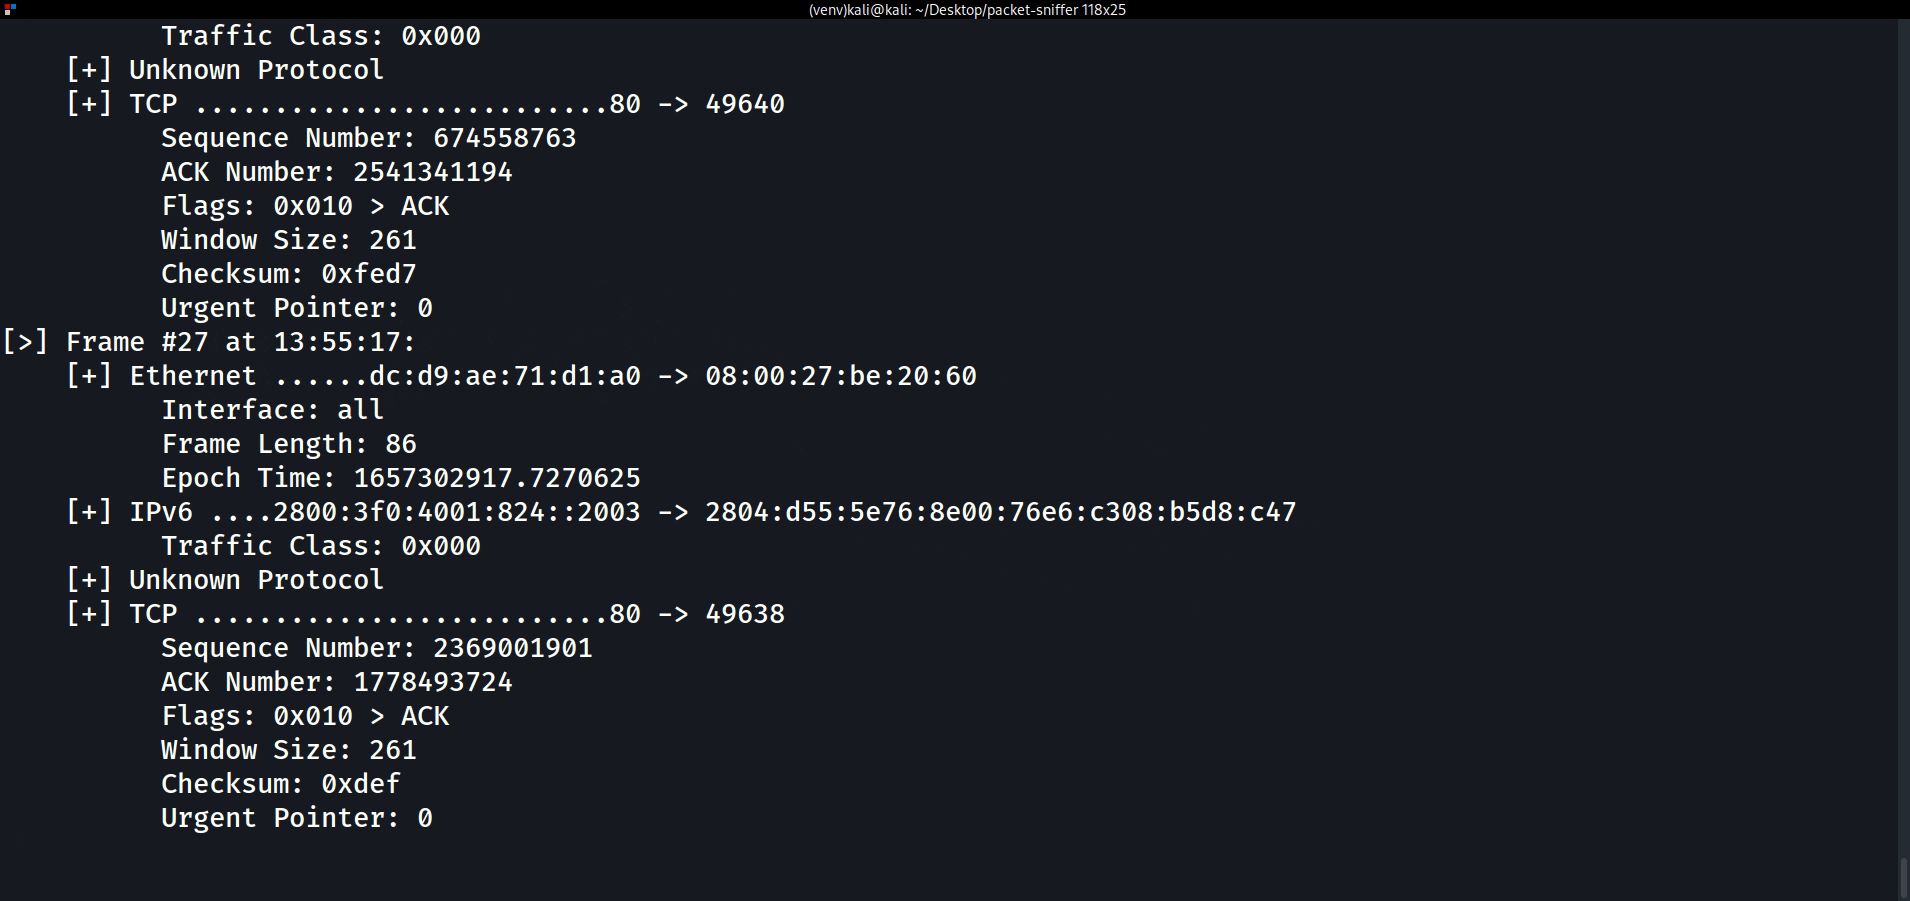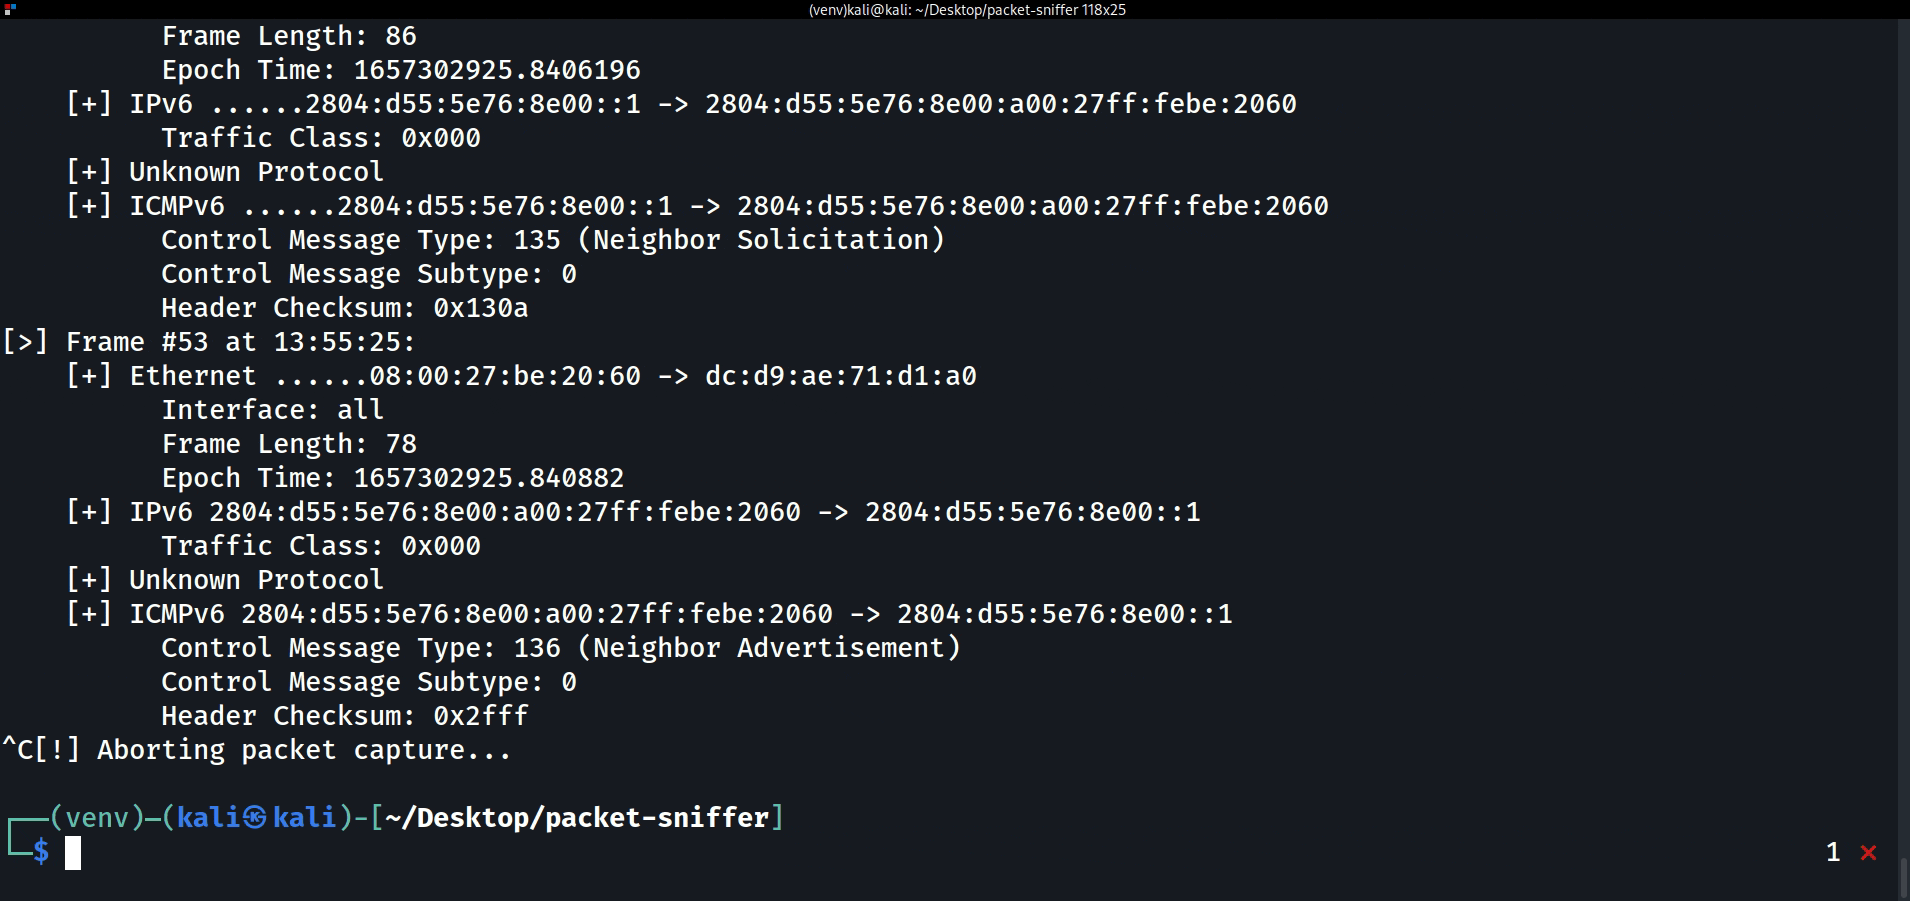
A Network Packet Sniffing tool developed in Python 3.

A tool to use AWS IAM credentials to authenticate to a Kubernetes cluster

Proof-of-concept exploit for OPNsense root remote code execution (CVE-2026-57155) targeting unauthenticated command injection in the web interface.

Exploit for CVE-2015-1328, a local privilege escalation vulnerability in the Linux kernel's overlayfs filesystem, enabling unprivileged users to gain…

Proof-of-concept exploit for CVE-2026-6279, demonstrating the vulnerability and providing a basis for security testing and patch validation.

Peirates - Kubernetes Penetration Testing tool

Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.

List of mixed boolean-arithmetic resources