
 h4k6/cve-2023-0179-poc
针对(CVE-2023-0179)漏洞利用 该漏洞被分配为CVE-2023-0179,影响了从5.5到6.2-rc3的所有Linux版本,该漏洞在6.1.6上被测试。 漏洞的细节和文章可以在os-security上找到。
 brucetg/dirtycow-exp
编译好的脏牛漏洞(CVE-2016-5195)EXP
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 ricterz/cve-2021-3560-authentication-agent
PolicyKit CVE-2021-3560 Exploit (Authentication Agent)
 graniet/inspector
The Inspector tool is a privilege escalation helper (PoC), easy to deployed on web server, this tool can list process running with root, check kernel…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 realtalk/cve-2013-2094
original cve-2013-2094 exploit and a rewritten version for educational purposes
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
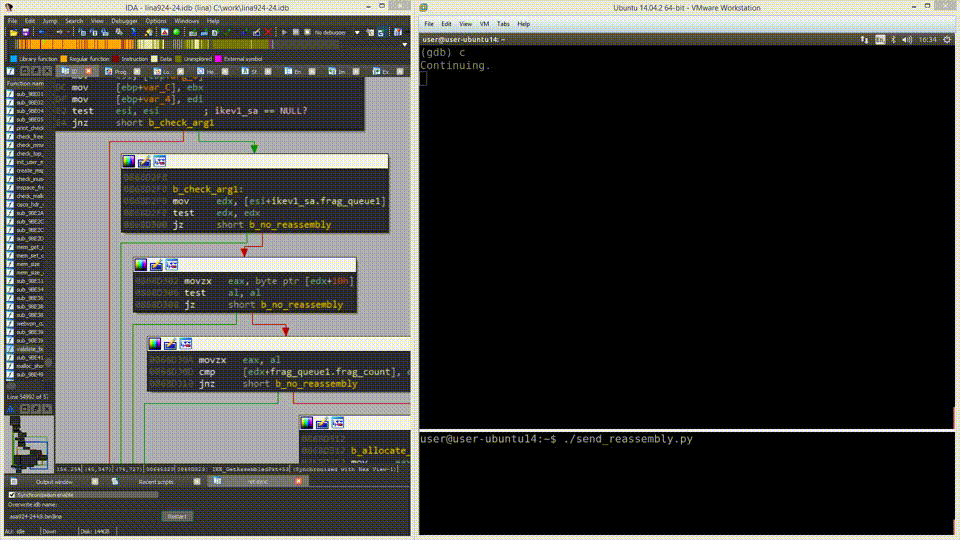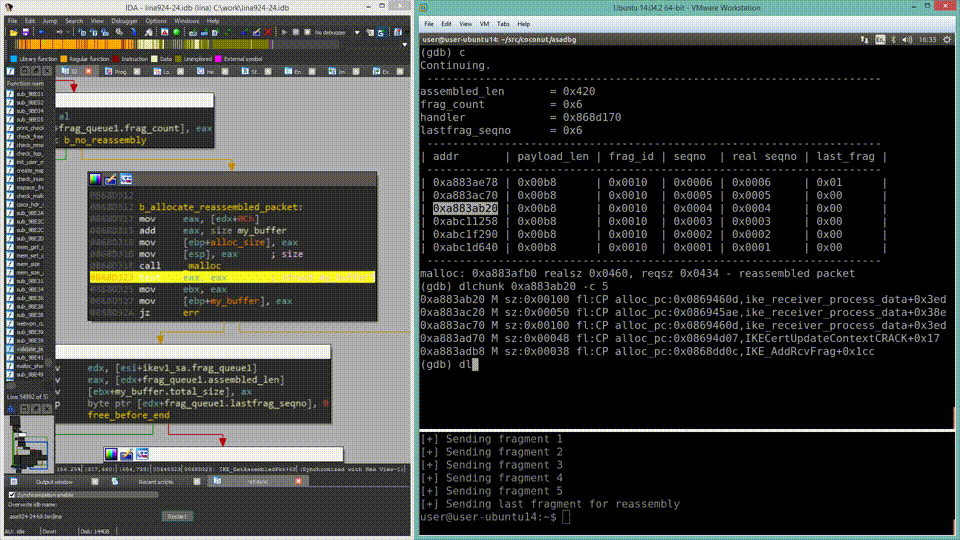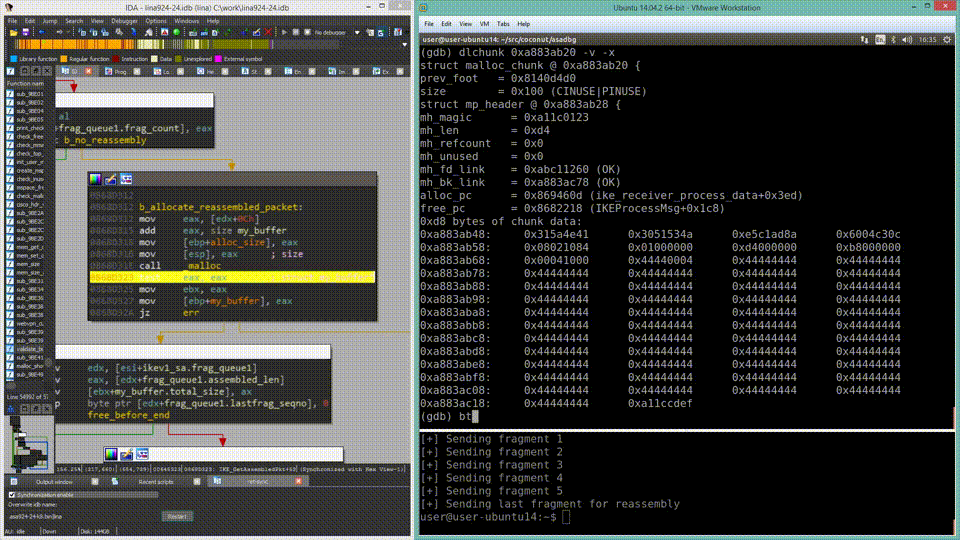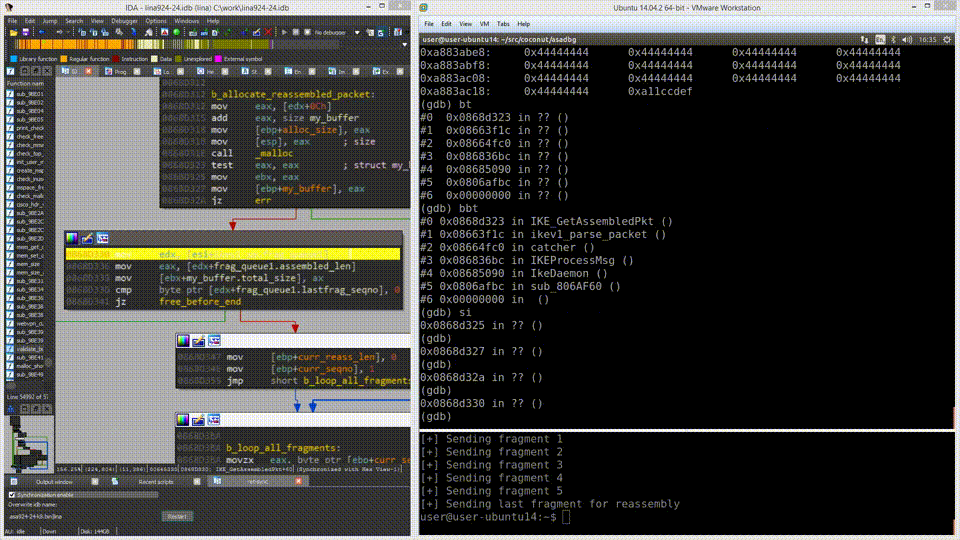 nccgroup/asadbg
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 sec-consult/msiscan
Scanning tool for identifying local privilege escalation issues in vulnerable MSI installers
 markakd/cve-2021-4154
CVE-2021-4154 exploit
 offxec/pavelow
PAVELOW Exploit Toolbox is a BASH script that corresponds with your KALI distro to better help your vulnerability hunting and exploiting proccess…
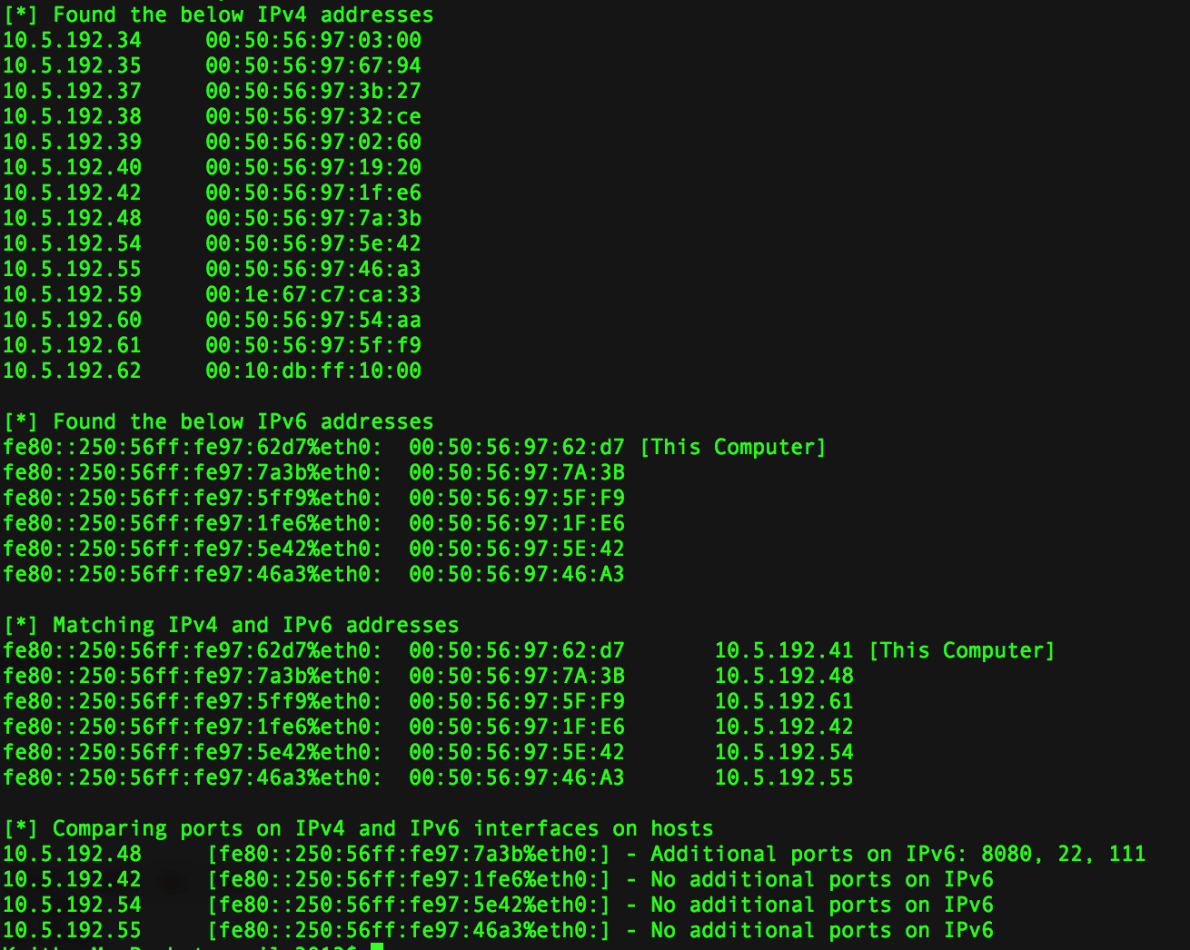 milo2012/ipv4bypass
Using IPv6 to Bypass Security
 christbowel/cve-2023-25136
OpenSSH 9.1 vulnerability mass scan and exploit
 mikispag/rosettaflash
A tool for manipulating SWF files, leveraging zlib to craft alphanumeric-only valid SWF files in order to allow CSRF with SOP bypass thanks to JSONP…