
CVE-2024-7593
 aerchy/cve-2024-7593
Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
exploitationpenetration-testingreconnaissance+2
aerchy/cve-2024-7593Exploit for CVE-2024-7593, a critical RCE in Pulse Secure VPN management interface, allowing authenticated attackers to execute arbitrary commands.…
 globaleaks/globaleaks-whistleblowing-software
GlobaLeaks is a free and open-source whistleblowing software enabling anyone to easily set up and maintain a secure reporting platform.
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
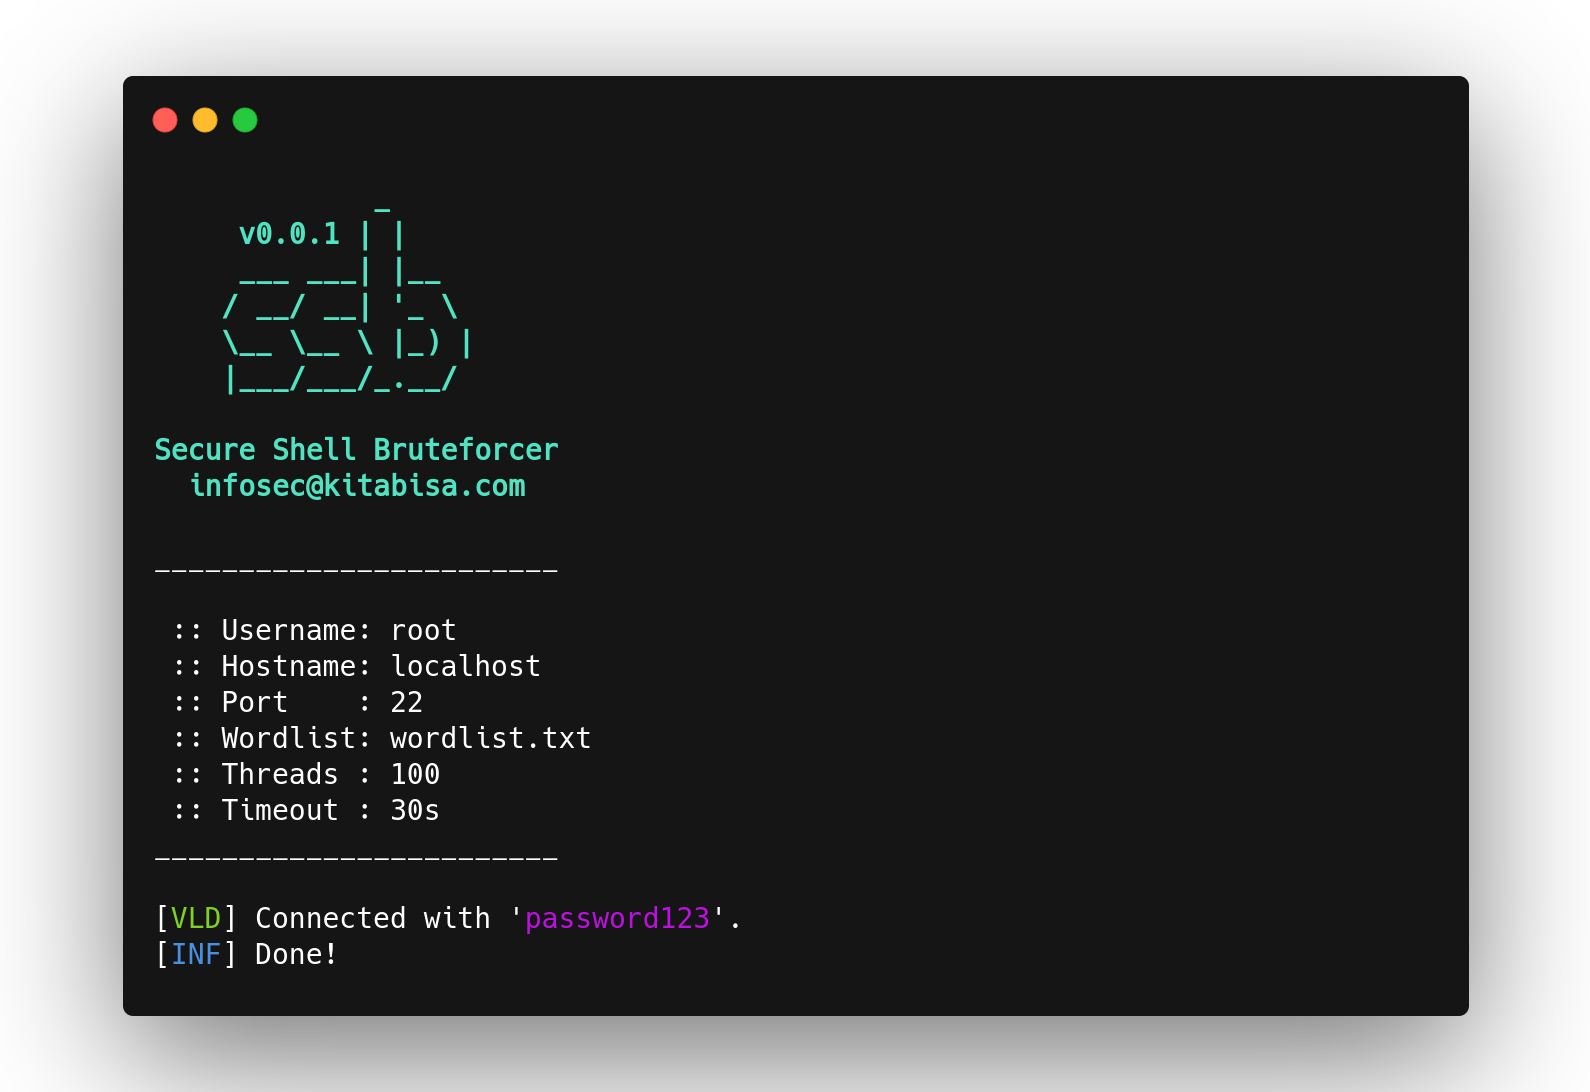 pwnesia/ssb
Secure Shell Bruteforcer — A faster & simpler way to bruteforce SSH server
 kukrimate/cve-2020-14372
Proof-of-concept exploit and write-up for CVE-2020-14372, demonstrating Secure Boot bypass via malicious ACPI SSDT to disable kernel lockdown and…
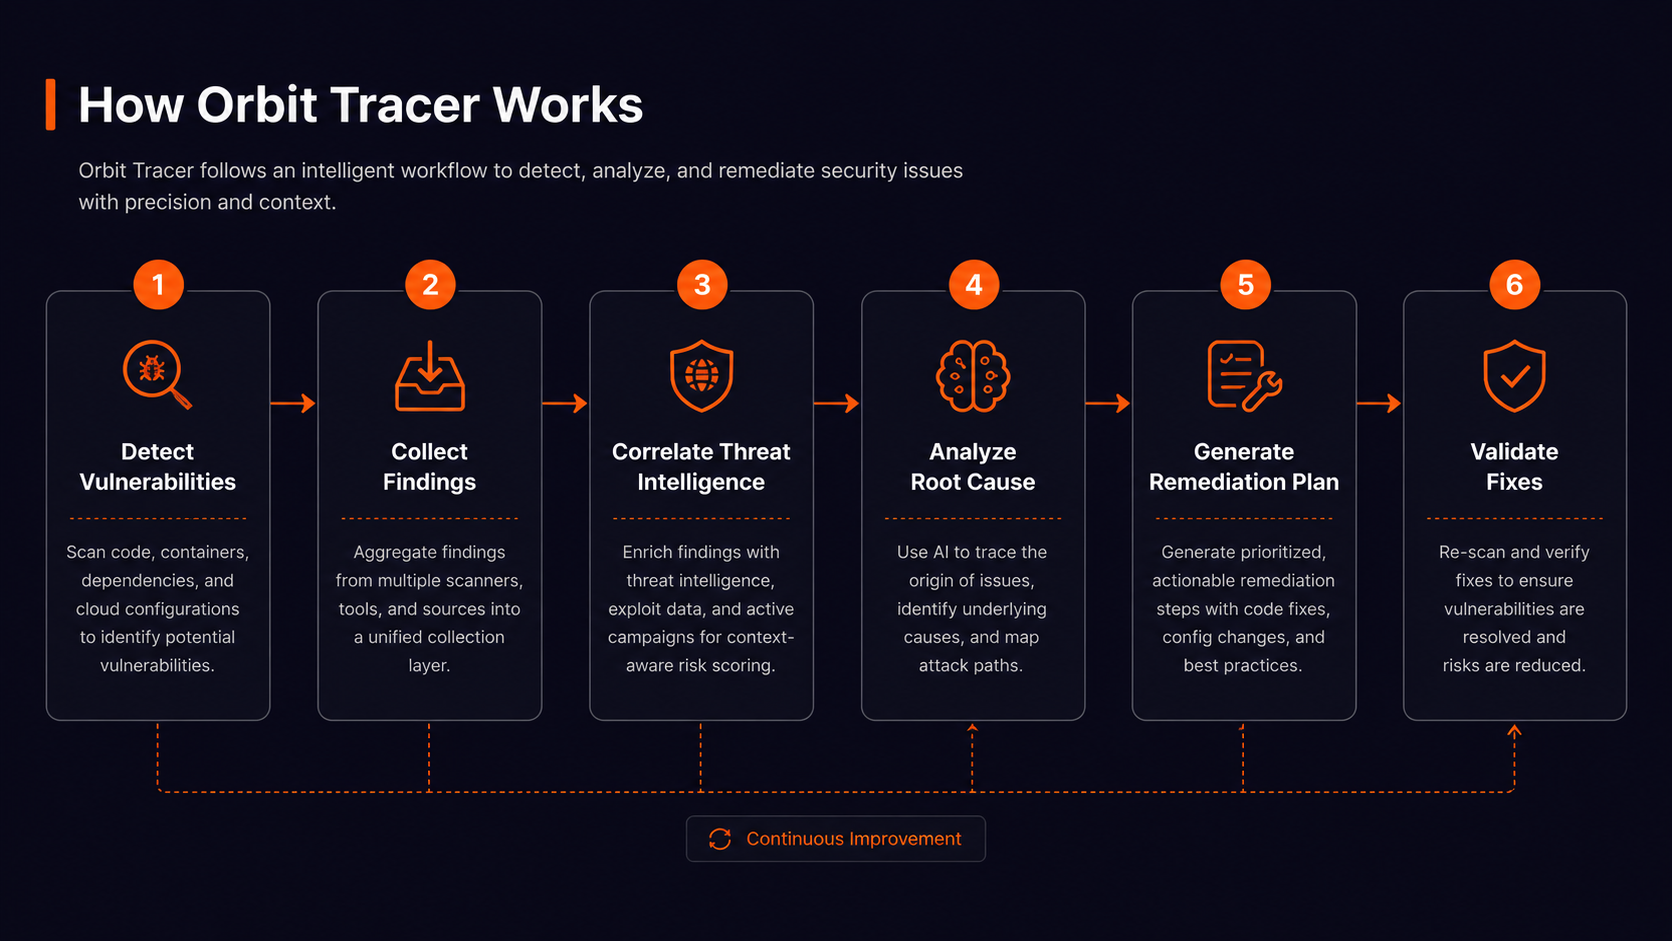
 rajus-agent/orbit-tracer
Orbit Tracer Security Agent for intelligent security remediation. Traces vulnerability blast radius using Orbit's knowledge graph, scores risk,…
 rathole-org/rathole
A lightweight and high-performance reverse proxy for NAT traversal, written in Rust. An alternative to frp and ngrok.
 rcarmo/agentbox
Docker-based sandbox for coding agents with isolated environments, preinstalled agent tooling, service control, and workspace bootstrap for secure…
 alphadelta/secure-desktop
Anti-keylogger/anti-rat application for Windows
 roxanne_ardary/safeforge
SafeForge is an open-source mobile app hub built on GitLab that enables developers to build, upload, and share applications in a secure, AI-verified…
 nozaq/terraform-aws-secure-baseline
Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…
 mingchen-script/cve-2020-1472-visualizer
PowerShell script to scan Windows Event Logs for CVE-2020-1472 indicators (events 5827-5831), export to CSV, and generate Excel pivot tables for…
 aqhmal/pulsexploit
Automated script for Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API. You must have a Shodan account to use this…
 trinadh465/platform_external_libvpx_v1.8.0_cve-2023-5217
Patched libvpx codebase addressing CVE-2023-5217 with sanitizer support and cross-platform build configurations for secure VP8/VP9 encoding.
 dshamany/privatesphare
An at-rest encrypted filesharing application with multiple clients who seek to share privately, without tracking.
 remenis/cve-2025-63666
Tenda AC15 cookie exposure
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
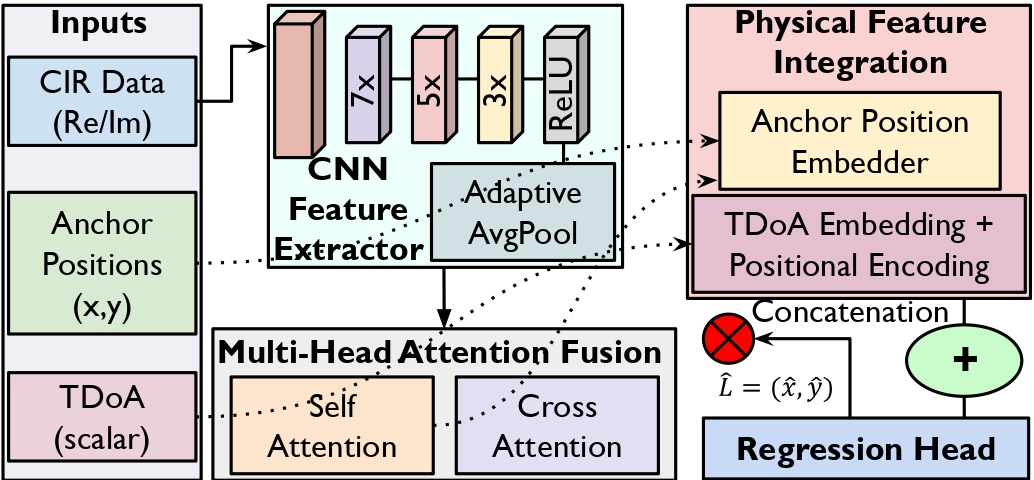 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…