CVE-2026-9998-Insecure-Deserialization-in-Blockchain-Oracle

PoC for CVE-2026-9998: RCE via insecure Python pickle deserialization in a blockchain oracle, with vulnerable node simulation and exploit script.

PoC for CVE-2026-9998: RCE via insecure Python pickle deserialization in a blockchain oracle, with vulnerable node simulation and exploit script.

Python-based exploit for CVE-2018-15473 enabling OpenSSH username enumeration via authentication response oracle, with single-user and wordlist modes.

Oracle WebLogic Server (LFI)

:poodle: Poodle (Padding Oracle On Downgraded Legacy Encryption) attack CVE-2014-3566 :poodle:

CVE-2019-2729 Exploit Script

Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…

Multi-step proof-of-concept exploit for CVE-2017-1000486 (PrimeFaces EL injection) with padding oracle secret retrieval and blacklist-bypassing…

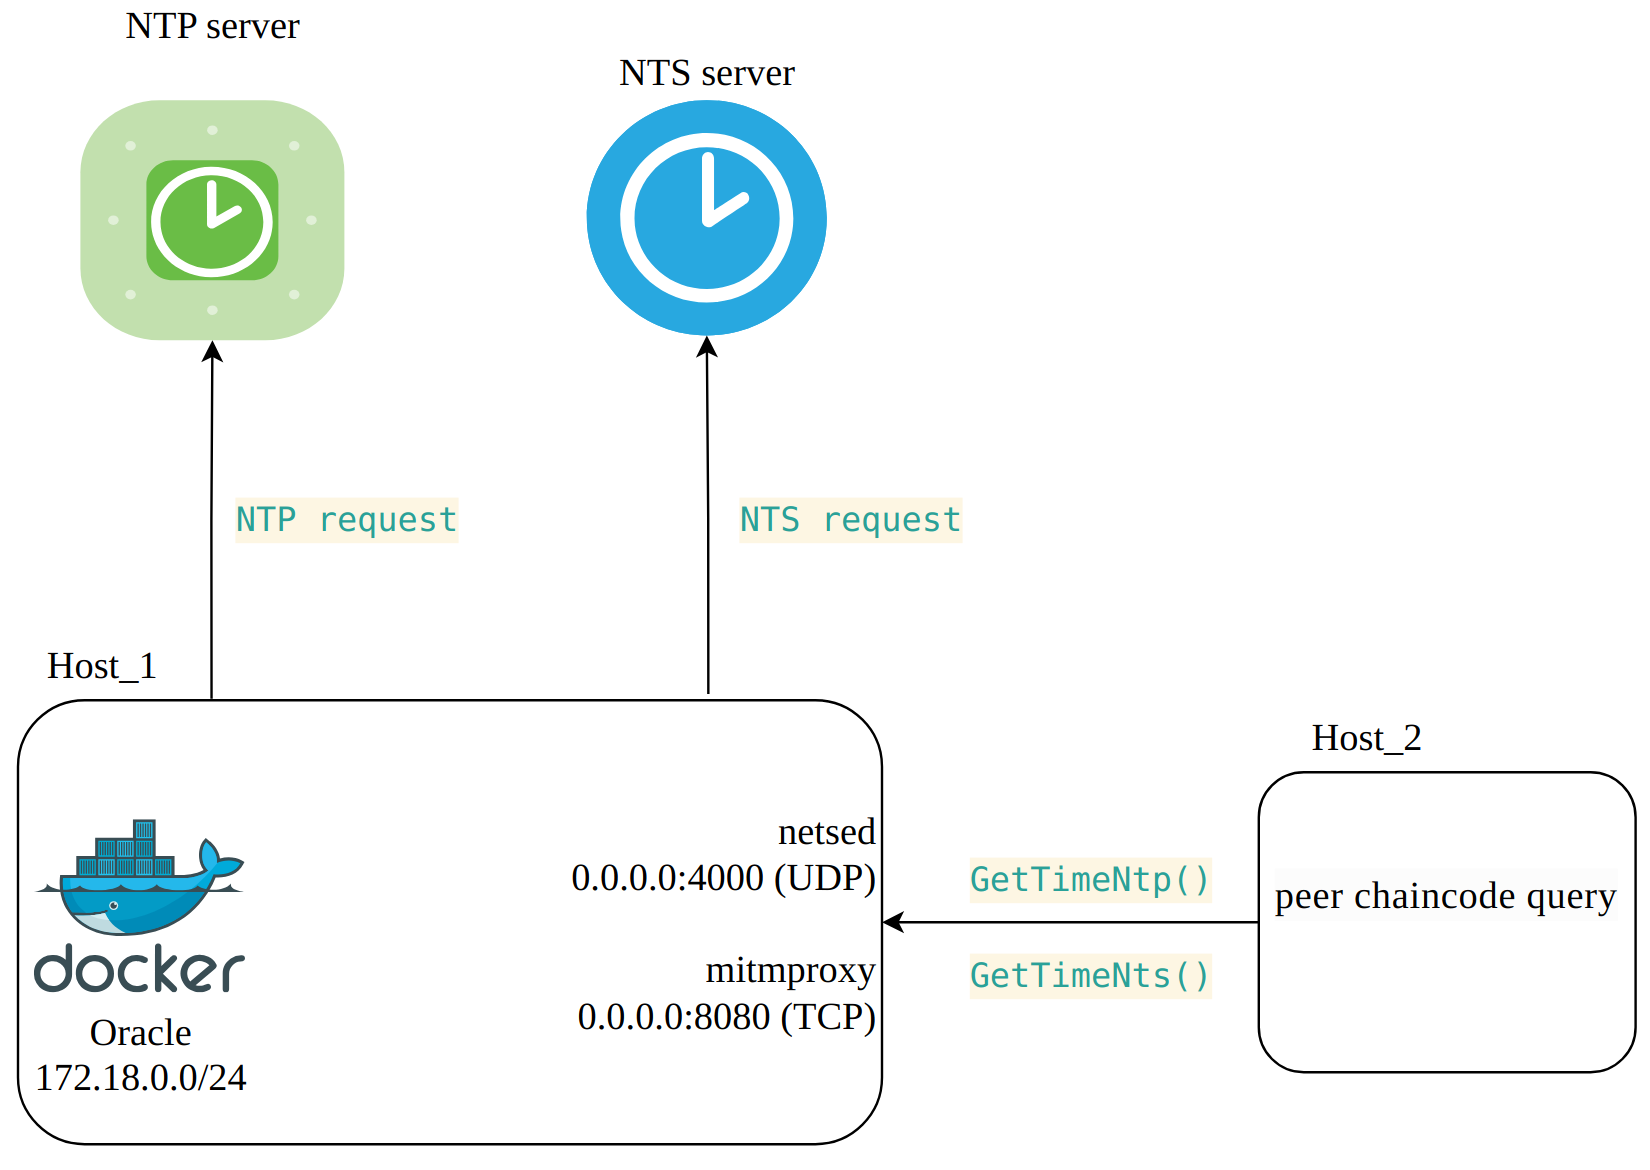
Chaincode for blockchain Hyperledger Fabric provides accurate time to other chaincodes. Thus solving the security problem associated with transaction…

Public exploit repository covering local privilege escalation, buffer overflows, and database exploits across Linux, Solaris, AIX, OpenBSD, Zyxel,…

An app with really insecure crypto. To be used to see/test/exploit weak cryptographic implementations as well as to learn a little bit more about…

Vulnerabilities which found in Oracle products

Multi-protocol honeypot simulator supporting 50+ network services with deep interaction, TCP/UDP/ICMP logging, JA3 fingerprinting, and virtual…

Free universal database tool and SQL client

Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…


Base64-based encryption oracle exploit for CVE-2017-9248 (Telerik UI for ASP.NET AJAX dialog handler)

Simple test for the May 2016 OpenSSL padding oracle (CVE-2016-2107)

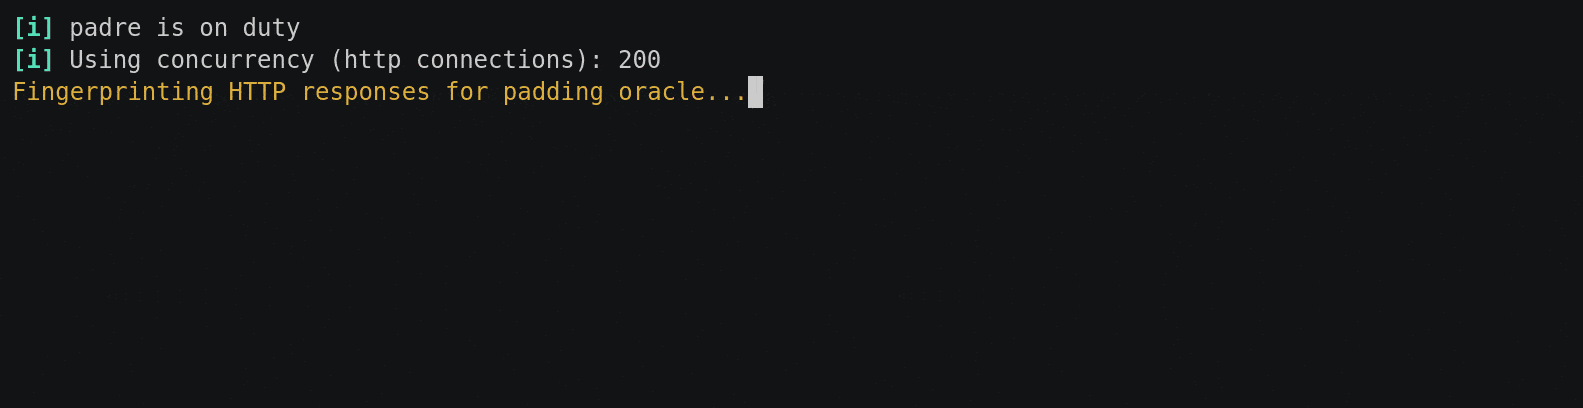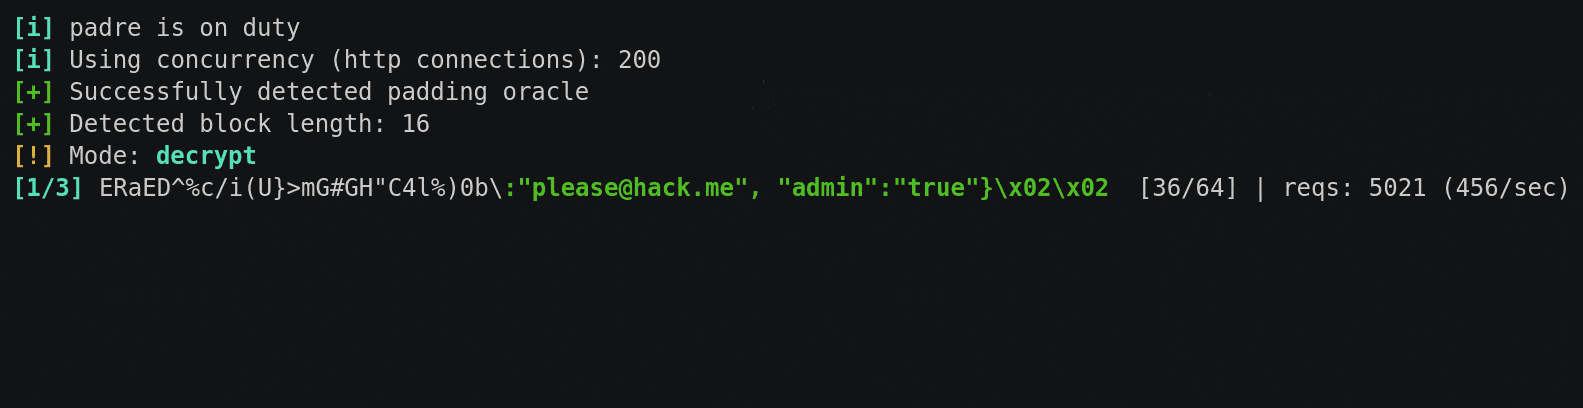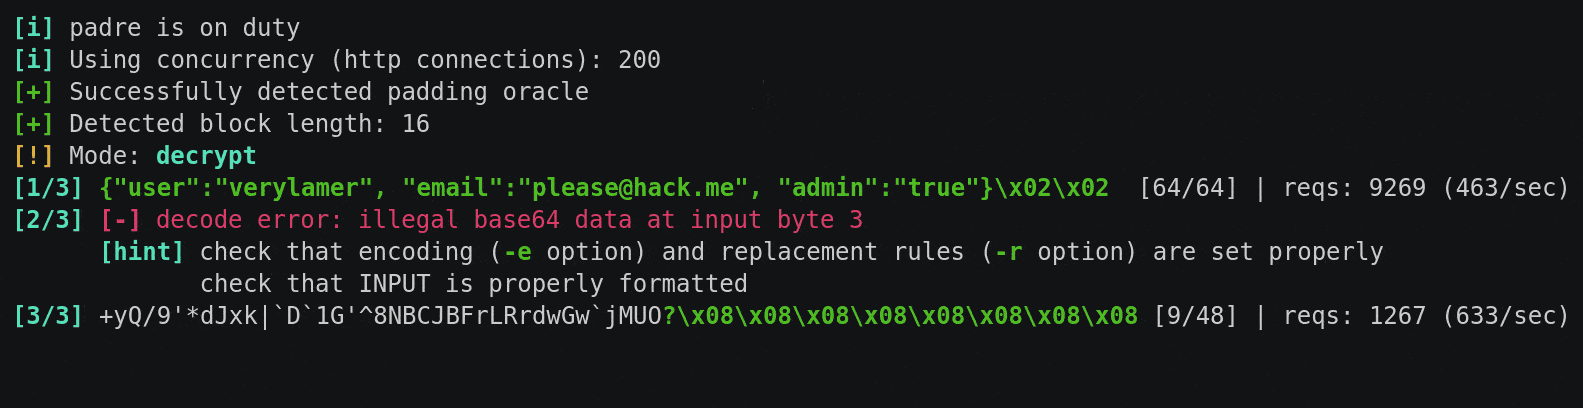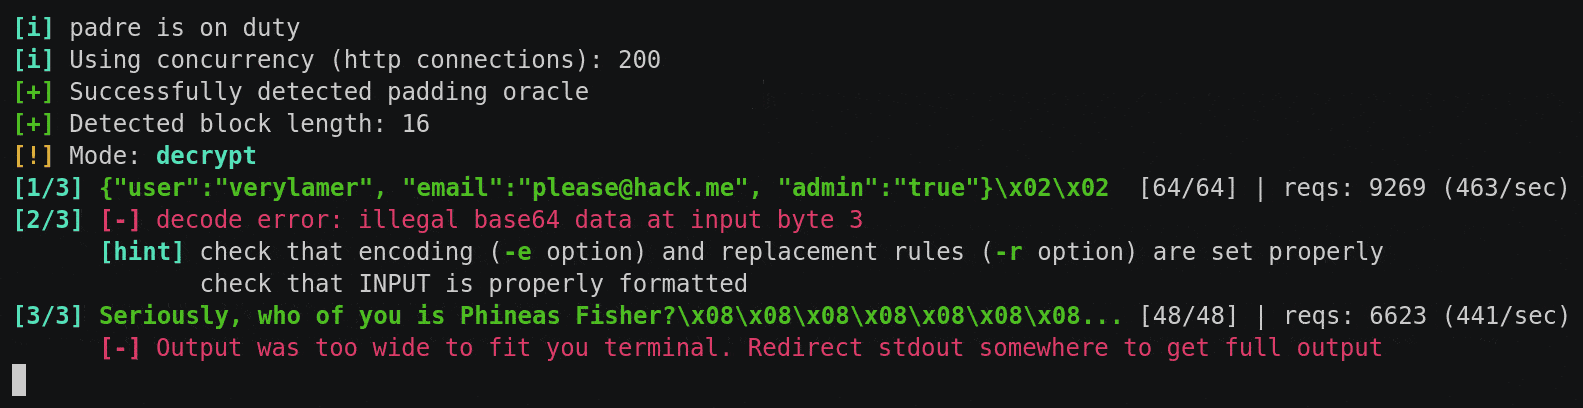
Blazing fast, advanced Padding Oracle exploit