
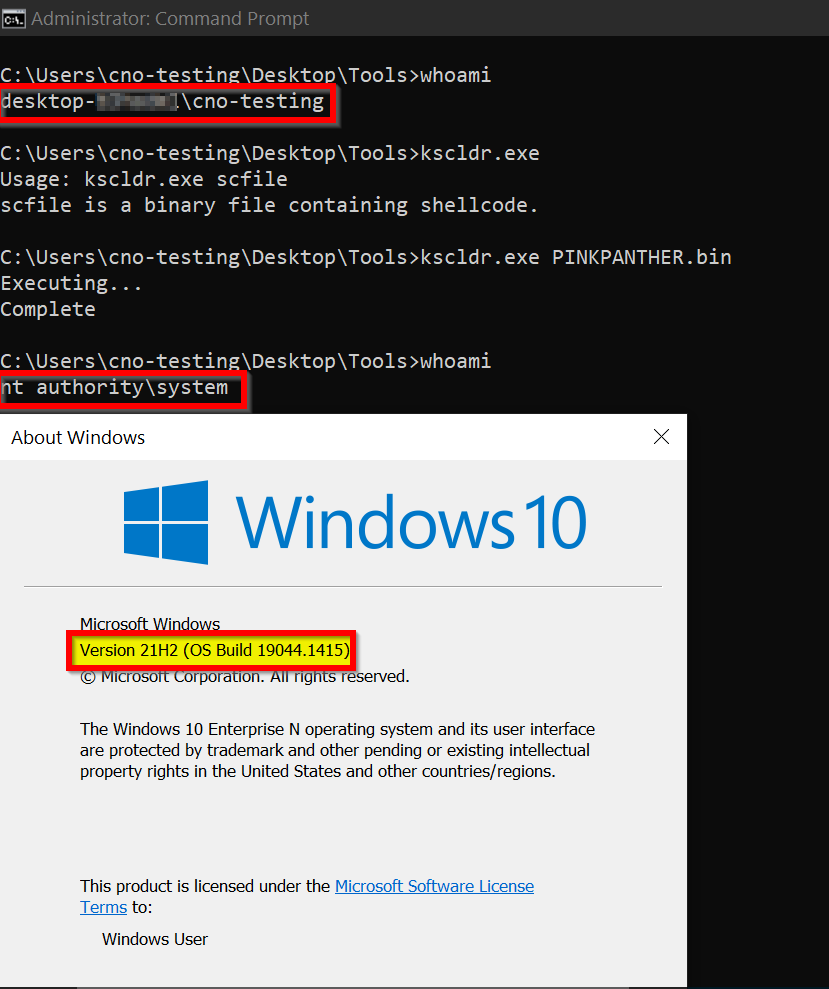
PINKPANTHER
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
519
winterknife/pinkpantherWindows x64 handcrafted token stealing kernel-mode shellcode
 trustedsec/elfloader
Loads and runs ELF objects entirely in memory across x86_64/x86 Linux systems, resolving libc symbols at runtime for stealthy post-exploitation…
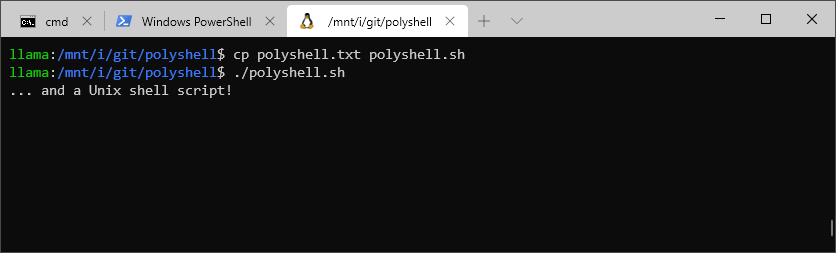 llamasoft/polyshell
A Bash/Batch/PowerShell polyglot!
 d00mfist/mystikal
macOS Initial Access Payload Generator
 nccgroup/accomplice
Tools for discovery and abuse of COM hijacks
 mythicagents/nimplant
A cross-platform implant written in Nim
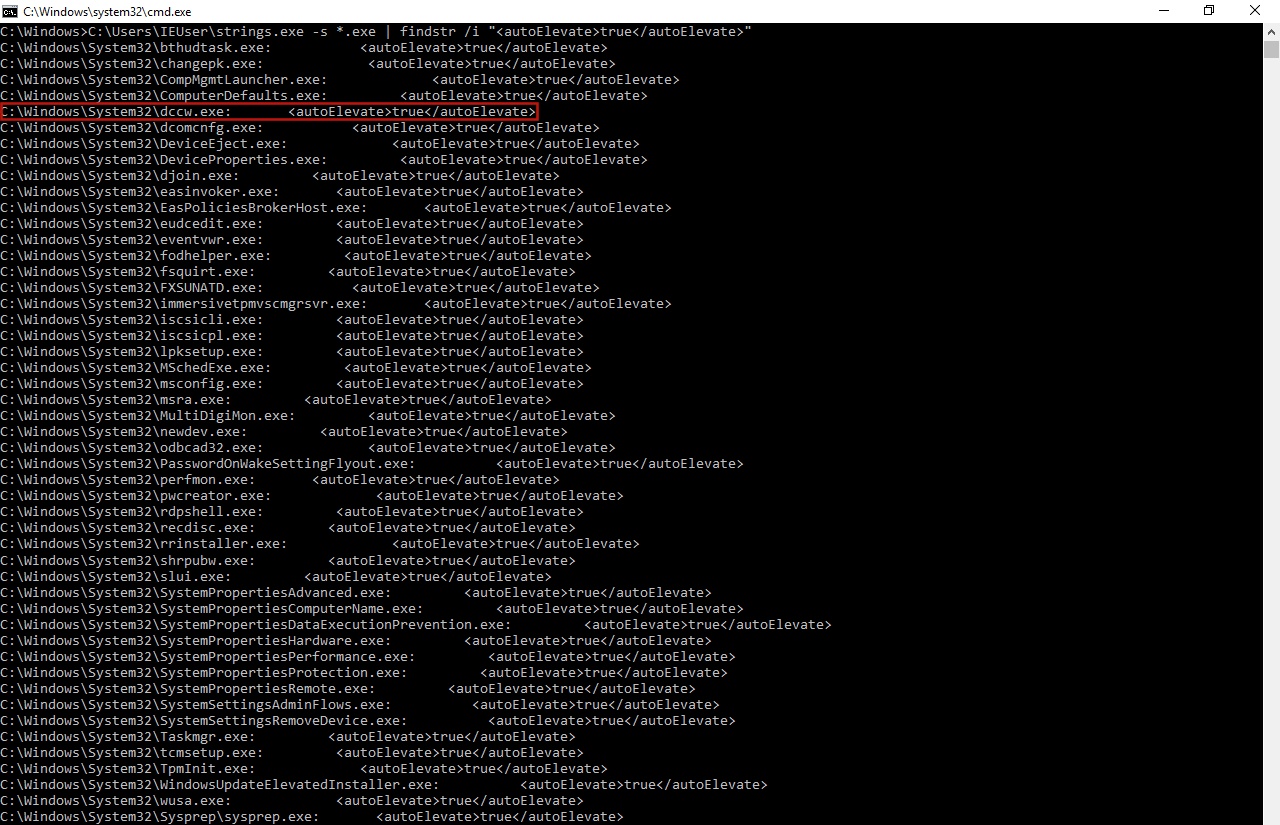 l3cr0f/dccwbypassuac
Windows 8.1 and 10 UAC bypass abusing WinSxS in "dccw.exe".

 kudaes/fiber
Rust-based PoC using Windows fibers to execute in-memory code stealthily, hiding payload stacks from EDR by switching between control and payload…
 zibility/remote
参考Gh0st源码,实现的一款PC远程协助软件,拥有远程Shell、文件管理、桌面管理、消息发送等功能。
 paranoidninja/brute-ratel-c4-community-kit
This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 h1d3r/gpu_shellcode
Hides reflective payloads in GPU memory via CUDA APIs, wiping host memory during sleep and using a VEH handler to restore executable memory, evading…
 voidsec/exploit-development
Exploit Development - Weaponized Exploit and Proof of Concepts (PoC)
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
 redcode-labs/gosh
Golang reverse/bind shell generator
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.