
CVE-2002-0748
 fauzanwijaya/cve-2002-0748
Proof of concept for LabVIEW Web Server HTTP Get Newline DoS vulnerability
exploitationpenetration-testingvulnerability-analysis+1
fauzanwijaya/cve-2002-0748Proof of concept for LabVIEW Web Server HTTP Get Newline DoS vulnerability
 kabir0104k/cve-2025-66947
Proof-of-concept for time-based blind SQL injection in a PHP admin panel. Demonstrates exploitation via unsanitized GET parameter, with mitigation…

 wavvs/nanorobeus
COFF file (BOF) for managing Kerberos tickets.

 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 duc-nt/cve-2022-44268-imagemagick-arbitrary-file-read-poc
PoC payload generator for CVE-2022-44268 ImageMagick arbitrary file read vulnerability. Demonstrates exploitation via crafted PNG files for…
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
 vpereira/cve-2009-5147
poc for CVE-2009-5147
 koozxcv/cve-2014-7911-cve-2014-4322_get_root_privilege
CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!
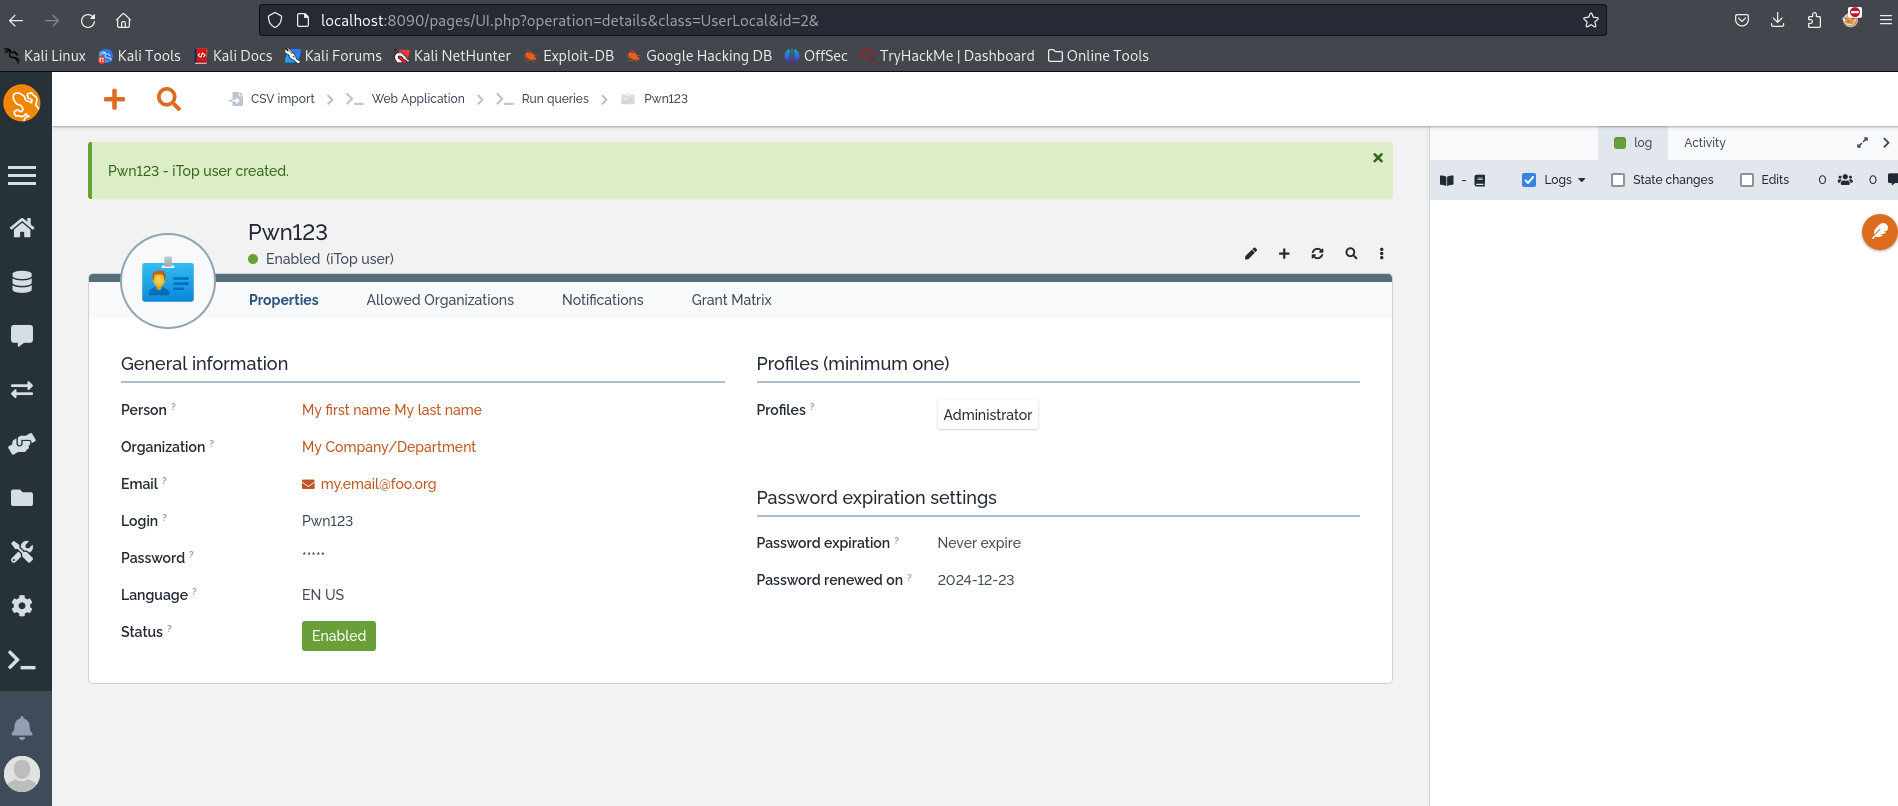 harshit-mashru/itop-cves-exploit
This repository contains exploits for iTOP CVE-2024-52002, 52000, 31998, 31448 that involve CSRF+XSS chaining to get RCE
 astrowmist/poc-cve-2016-10033
Proof Of Concept for the CVE-2016-10033 (PHPMailer)
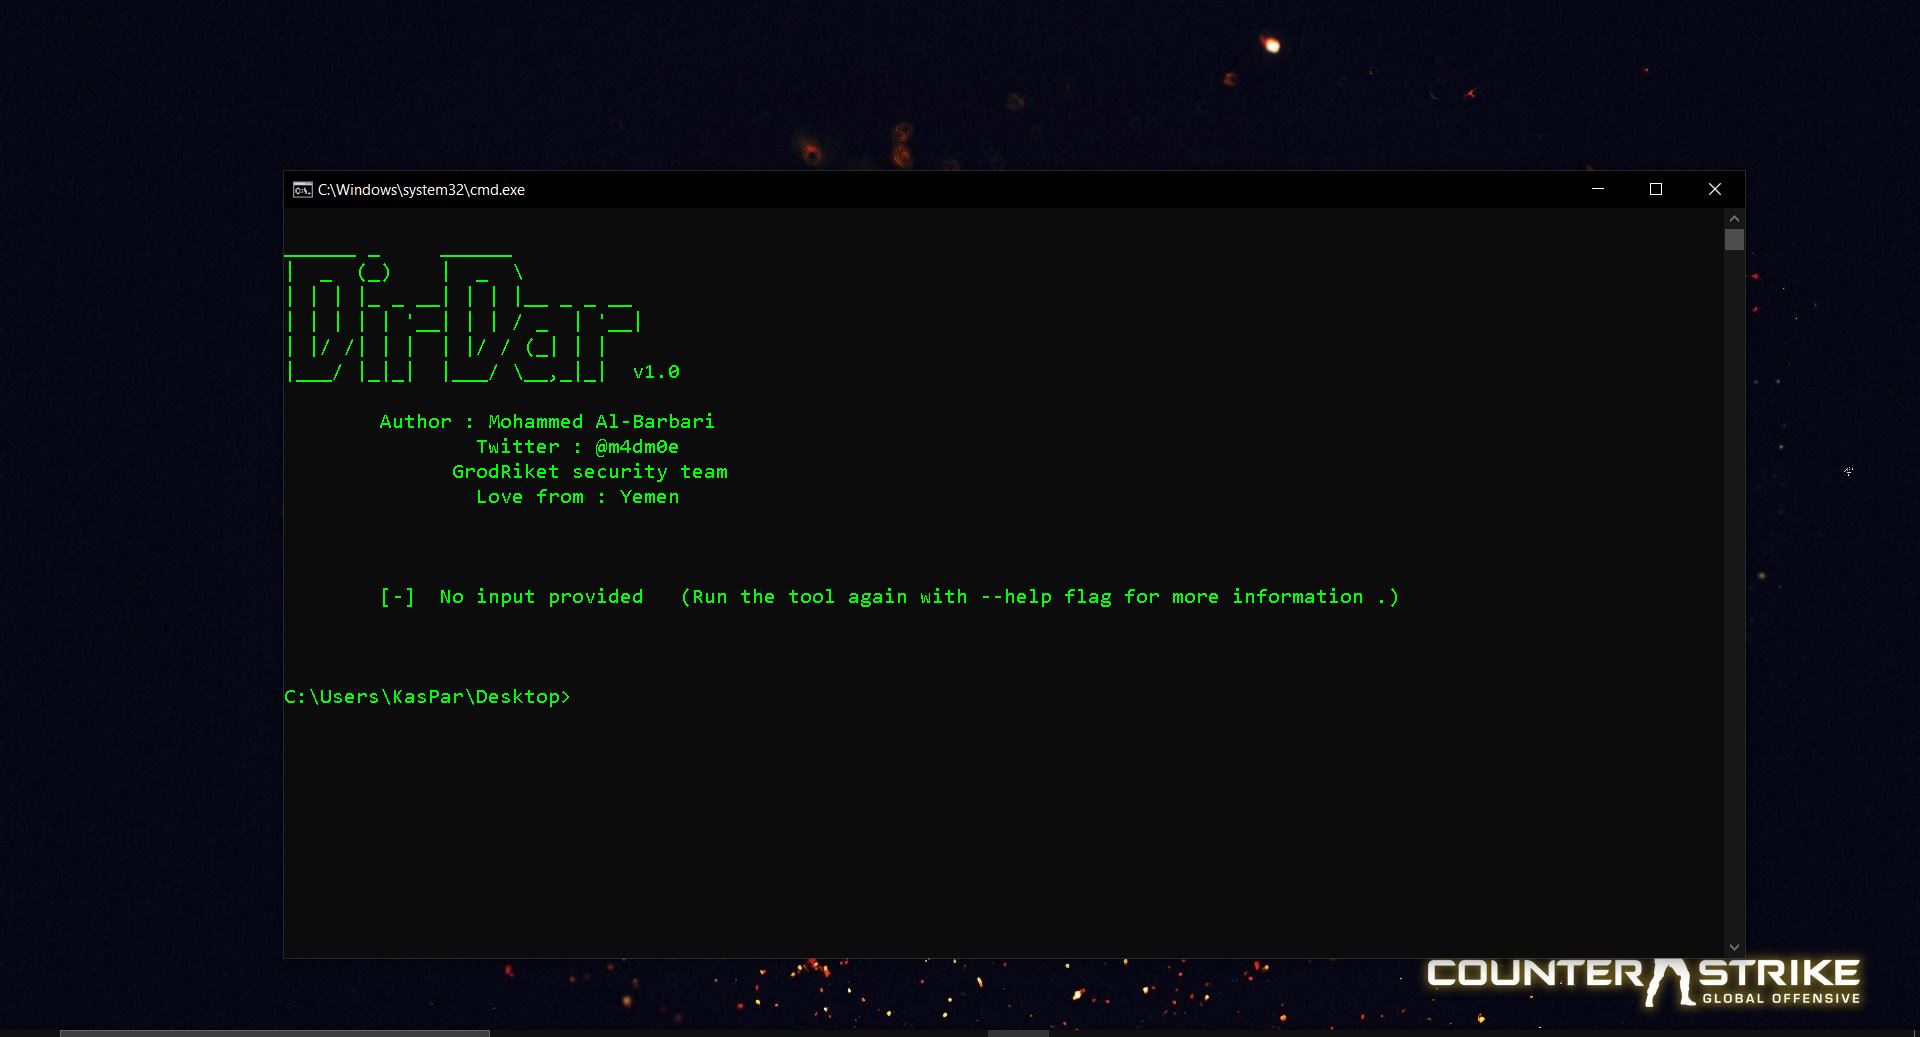 m4dm0e/dirdar
DirDar is a tool that searches for (403-Forbidden) directories to break it and get dir listing on it
 watchtowrlabs/watchtowr-vs-progress-sharefile-cve-2026-2699
Detection artifact for CVE-2026-2699 Progress ShareFile authentication bypass. Sends GET to /ConfigService/Admin.aspx to check vulnerability.
 you-ssef9/cve-2026-21440
Detection-only PoC for CVE-2026-21440 in AdonisJS BodyParser. Fingerprints AdonisJS indicators, probes upload endpoints via GET, and outputs…
 nate0634034090/nate158g-m-w-n-l-p-d-a-o-e
### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…