
freebsd-CVE-2026-7270
 babyshen/freebsd-cve-2026-7270
CVE-2026-7270 FreeBSD local privilege escalation via exec_args_adjust_args OOB memmove
binary-exploitationexploitationexploit-frameworks+4
babyshen/freebsd-cve-2026-7270CVE-2026-7270 FreeBSD local privilege escalation via exec_args_adjust_args OOB memmove
 g01d3nw01f/cve-2026-31431
Rust PoC for a Linux kernel local privilege escalation vulnerability, exploiting the Crypto API and splice to overwrite page cache and modify…
 vxqs/lenovo-cve-2025-8061
My PoC of Lenovo-CVE-2025-8061
 trex1e/copyfail-cve-2026-31431
Extended Linux Local Privilege Escalation PoC for CVE-2026-31431, with automatic kernel version detection and vulnerable range checking for…
 ready2disclose/cve-2022-31491
CVE-2022-31491
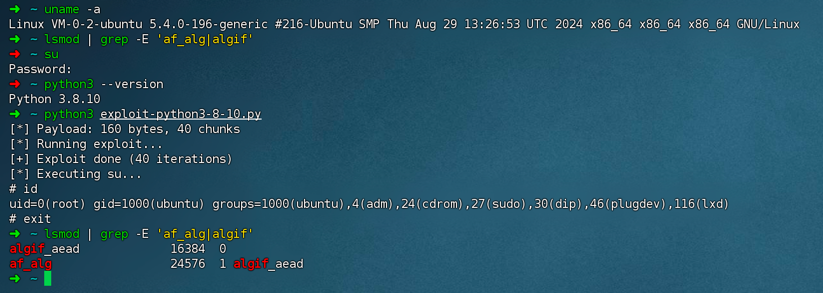 y5neko/copy-fail-cve-2026-31431-universal
Multi-language implementation and compatibility with older versions of Python.
 wostgit/cve-2025-15467-crash
Proof-of-concept for CVE-2025-15467, demonstrating a crash condition for vulnerability analysis and exploitation research.
 shazed-x/cve-2025-32463
- Vulnerable: sudo 1.9.14, 1.9.15, 1.9.16, 1.9.17 - Patched in: sudo 1.9.17p1 and later - Legacy versions older than 1.9.14 are not affected, as they…
 dengyang123x/0vercl0k
PoC for CVE-2021-28476 a guest-to-host "Hyper-V Remote Code Execution Vulnerability" in vmswitch.sys.
 fnknda/cve-2021-4034_poc
Proof Of Concept for the 2021's pkexec vulnerability CVE-2021-4034
 trone-ux/cve-2025-22457
PoC CVE-2025-22457
 nulltrace1336/samba-exploit-cve-2007-2447
Step-by-step guide to exploiting Samba 3.0.20 (CVE-2007-2447) using Metasploit, including Nmap scanning, payload setup, and reverse shell execution.
 nikosecurity/cve-2026-26179
PoC for CVE-2026-26179 / ZDI-26-276, my very own Secure Kernel bug
 cyghtinc/cve-2024-30088-binary-lpe-privielege-escalation-cyght-toctou
Compiled proof-of-concept binary for local privilege escalation exploiting CVE-2024-30088, a TOCTOU vulnerability, targeting Windows systems.
 mefulton/cve-2018-11510
Just a couple exploits for CVE-2018-11510
 ownouwa/cve-2024-23113-poc
CVE-2024-23113 是一个在 Linux Kernel 中被发现的漏洞,它属于 任意代码执行漏洞,影响了 bpf (Berkeley Packet Filter) 子系统。具体来说,这个漏洞影响了 bpf 程序的 bpf_prog 类型的对象,并且可以允许攻击者通过构造恶意的 BPF…
 7043mcgeep/cve-2017-8890-msf
For Metasploit pull request
 nanaao/dirtypipe-exploit
Dirty Pipe (CVE-2022-0847) PoC that hijacks a SUID binary to spawn. a root shell. (and attempts to restore the damaged binary as well)