

FlavorTown
 wra7h/flavortown
Various ways to execute shellcode
payload-developmentpost-exploitationred-teaming+1
wra7h/flavortownVarious ways to execute shellcode
 hagrid29/peloader
PE loader with various shellcode injection techniques
 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
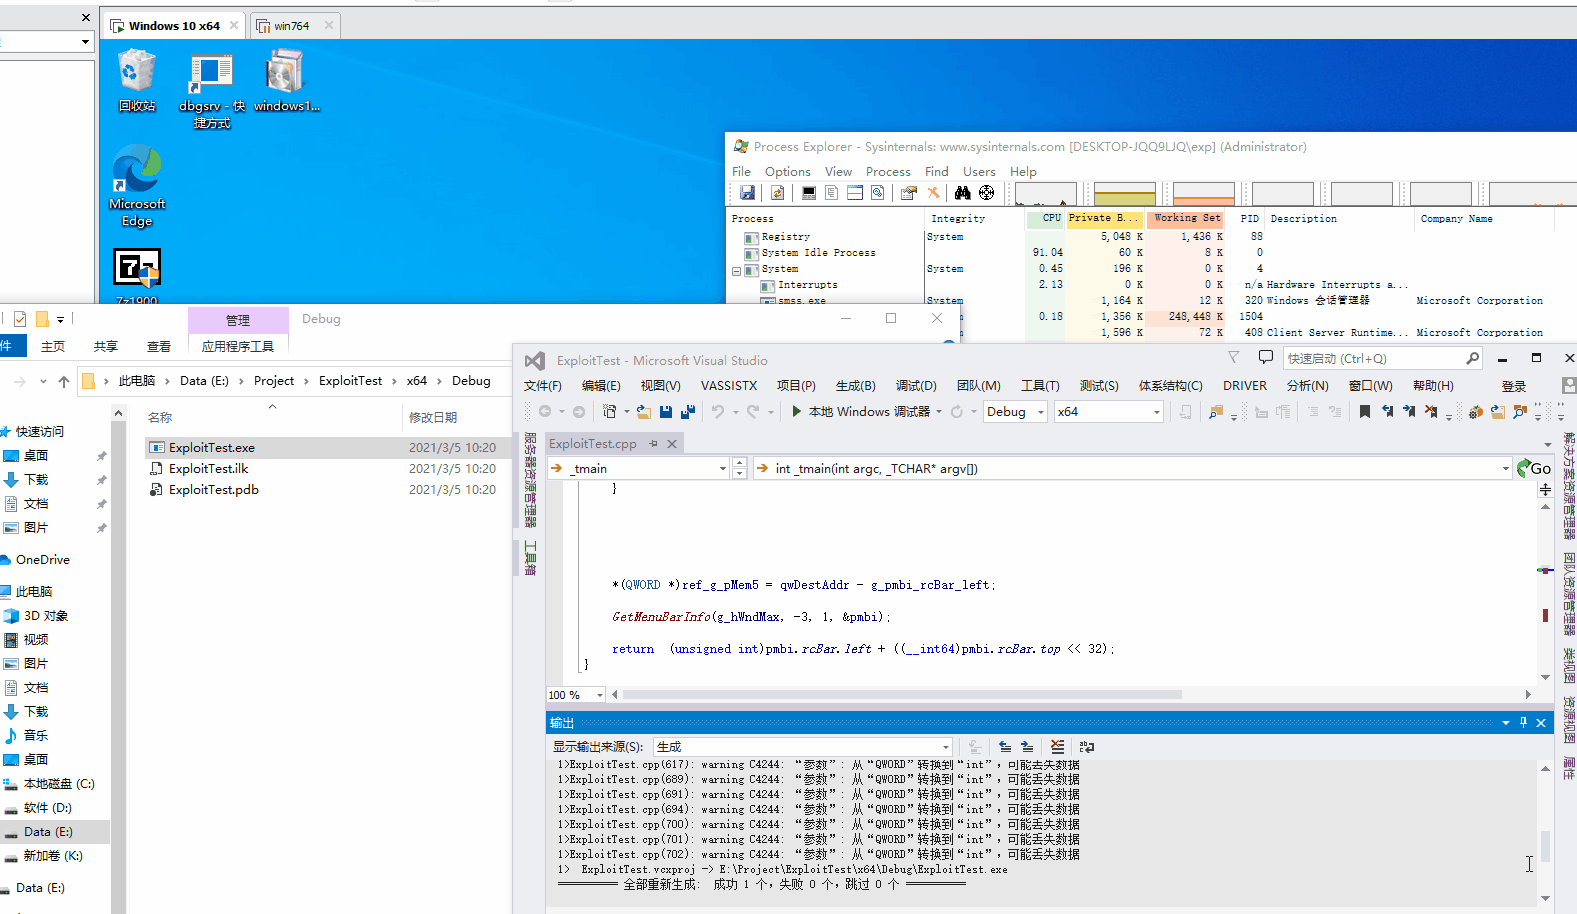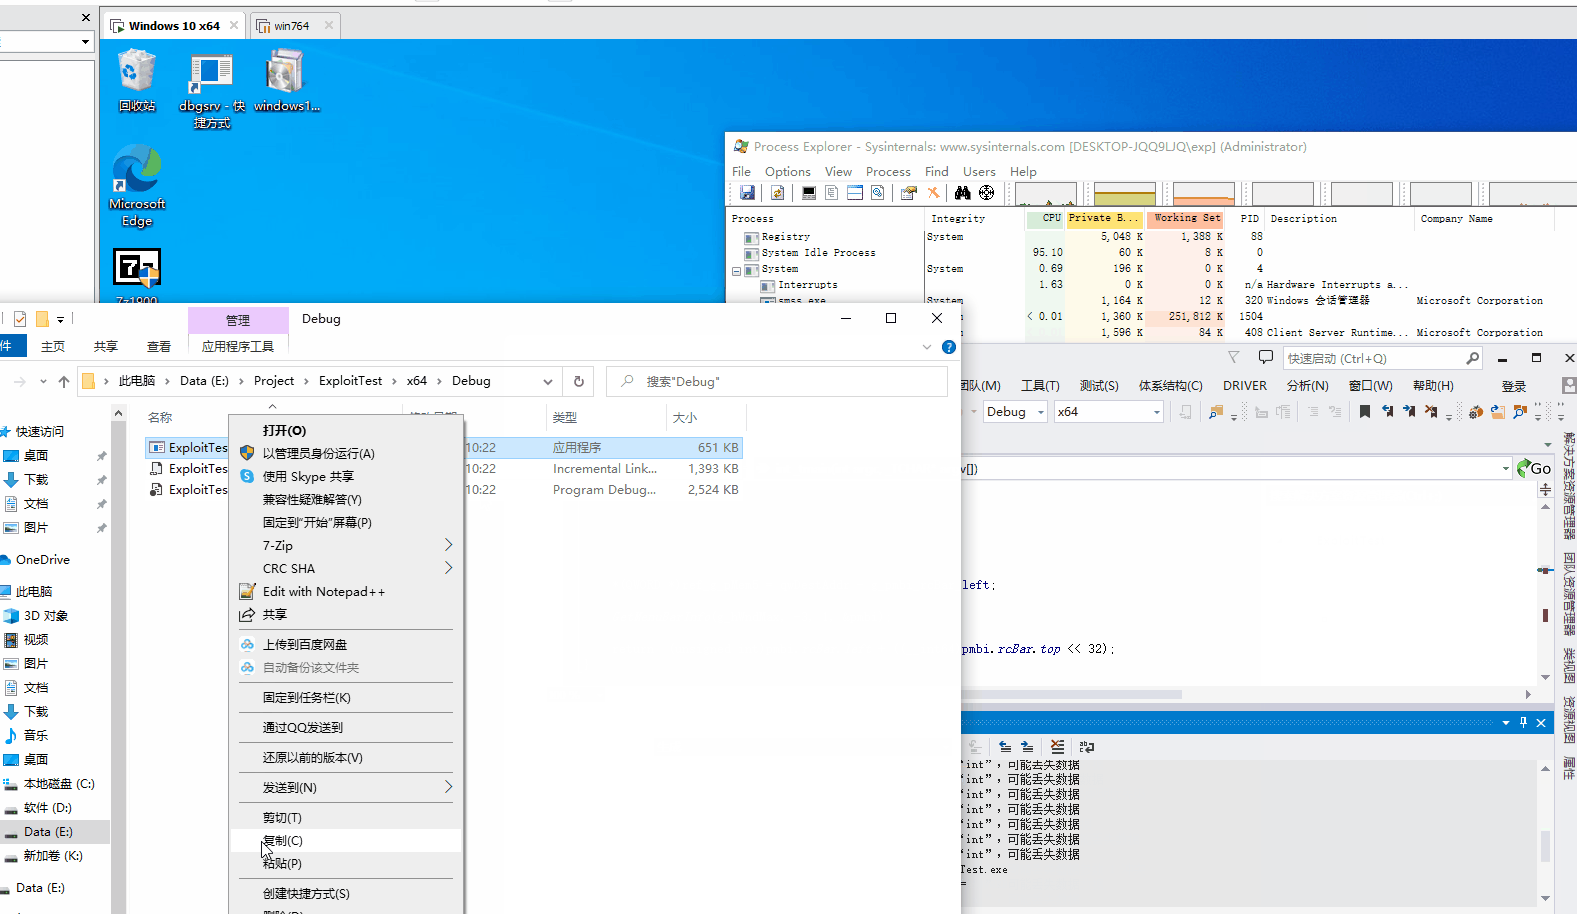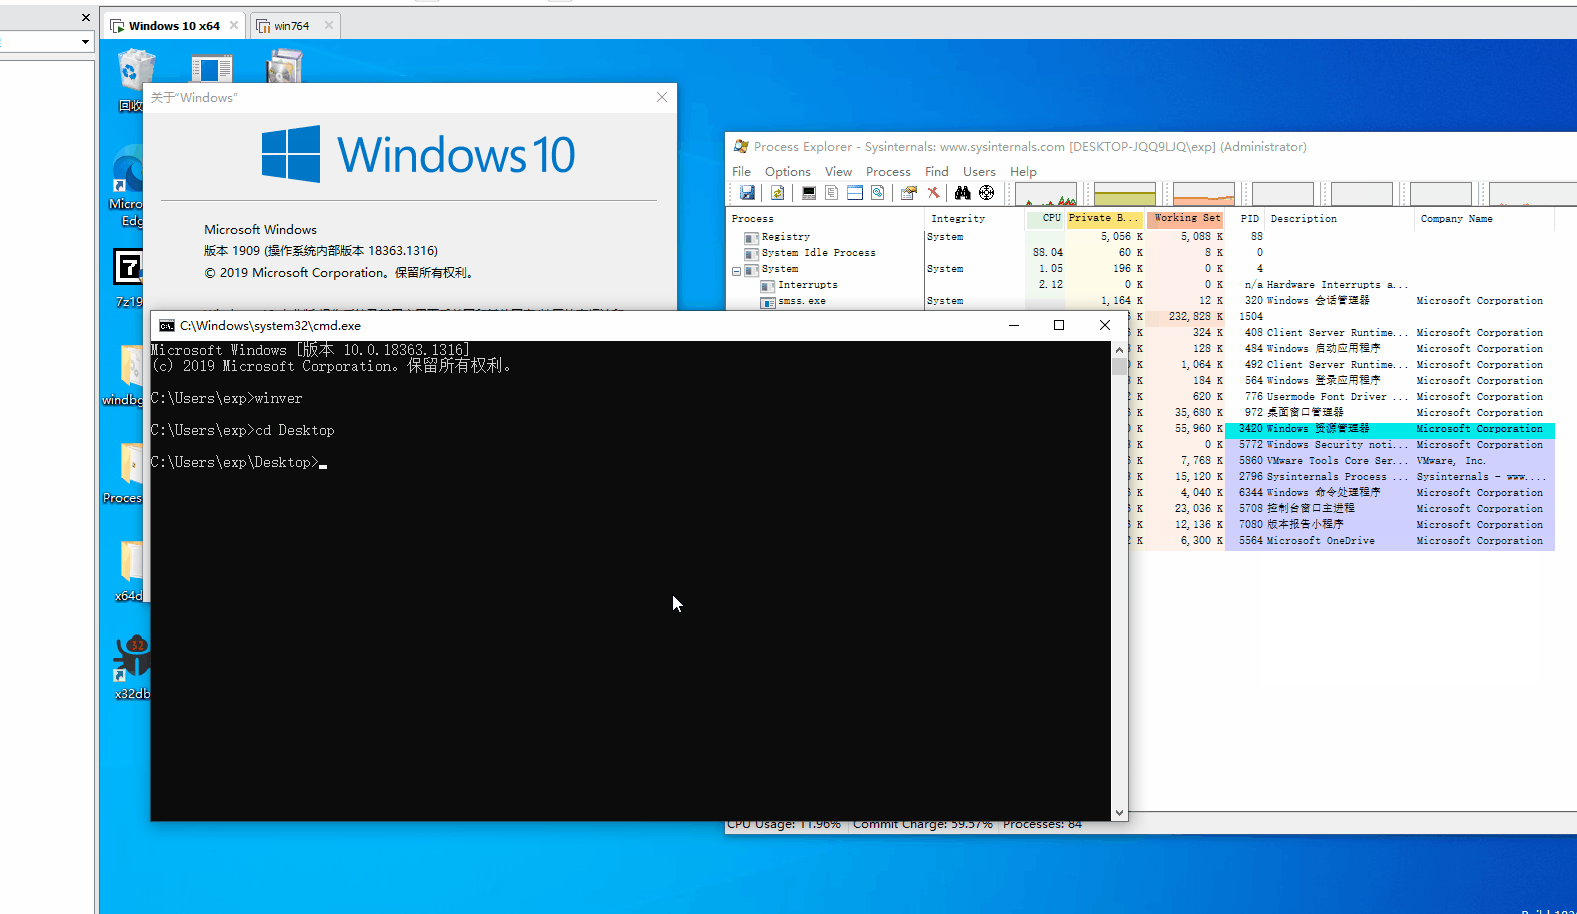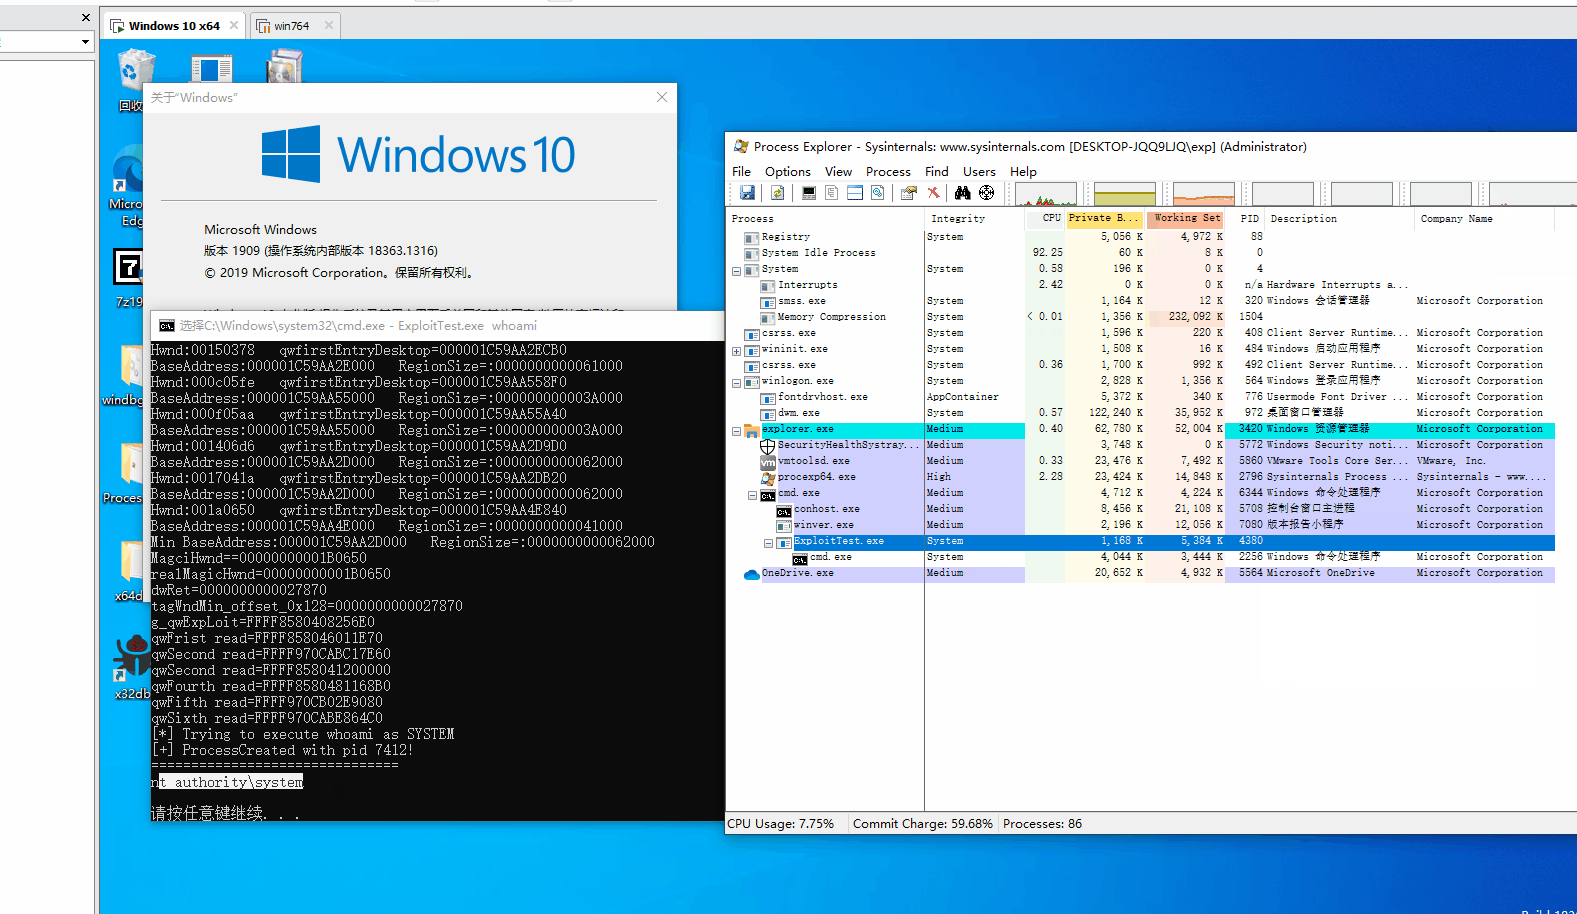 kalendsi/cve-2021-1732-exploit
CVE-2021-1732 Exploit
 pwntester/serialkillerbypassgadgetcollection
Collection of bypass gadgets to extend and wrap ysoserial payloads
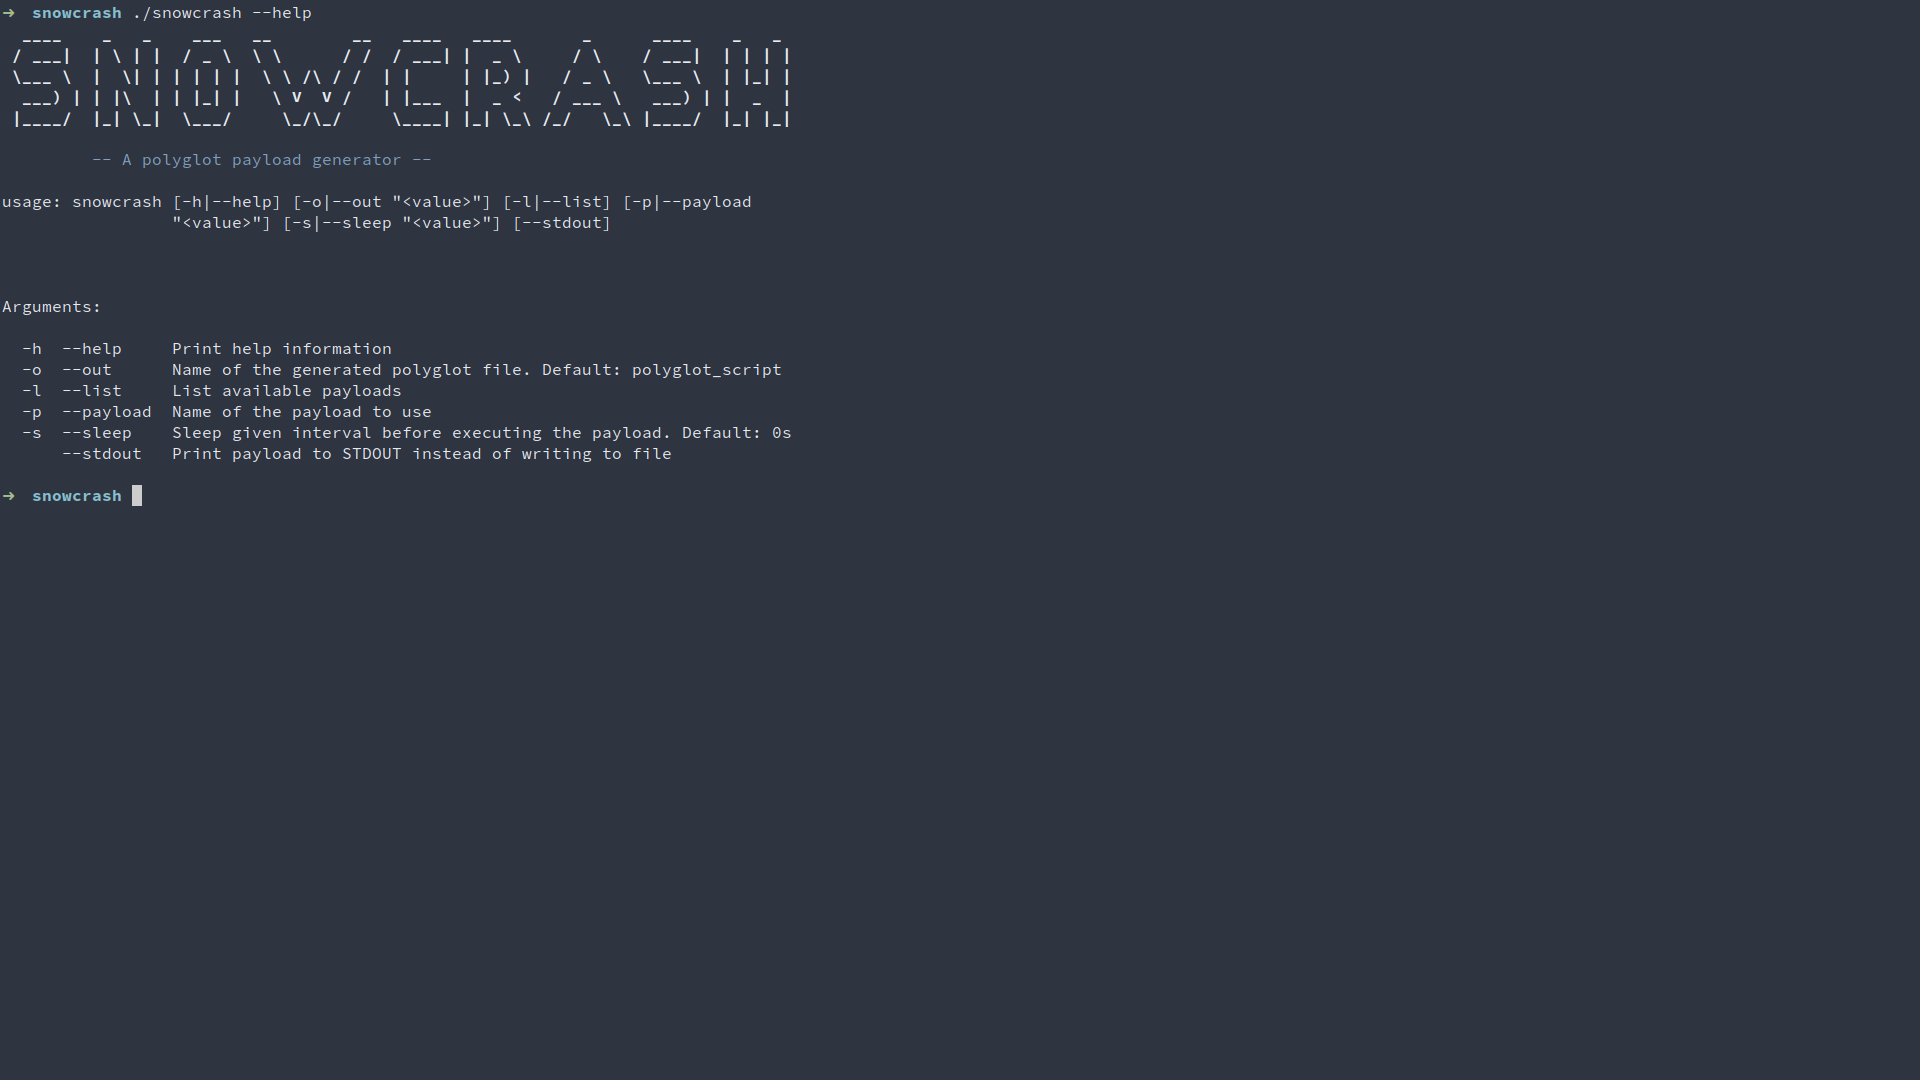 redcode-labs/snowcrash
Generates cross-platform polyglot payloads (Bash/PowerShell) for command execution, reverse shells, and binary execution, with configurable delay and…
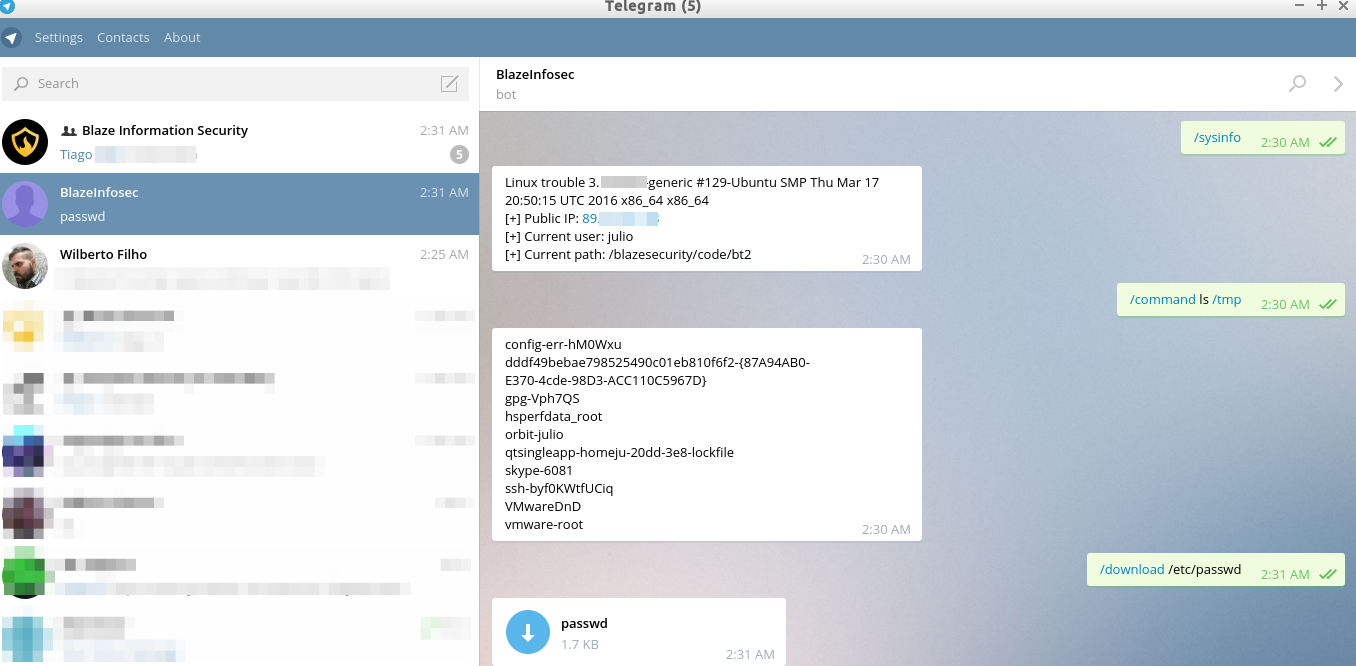 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
 lloydlabs/delete-self-poc
A way to delete a locked file, or current running executable, on disk.
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
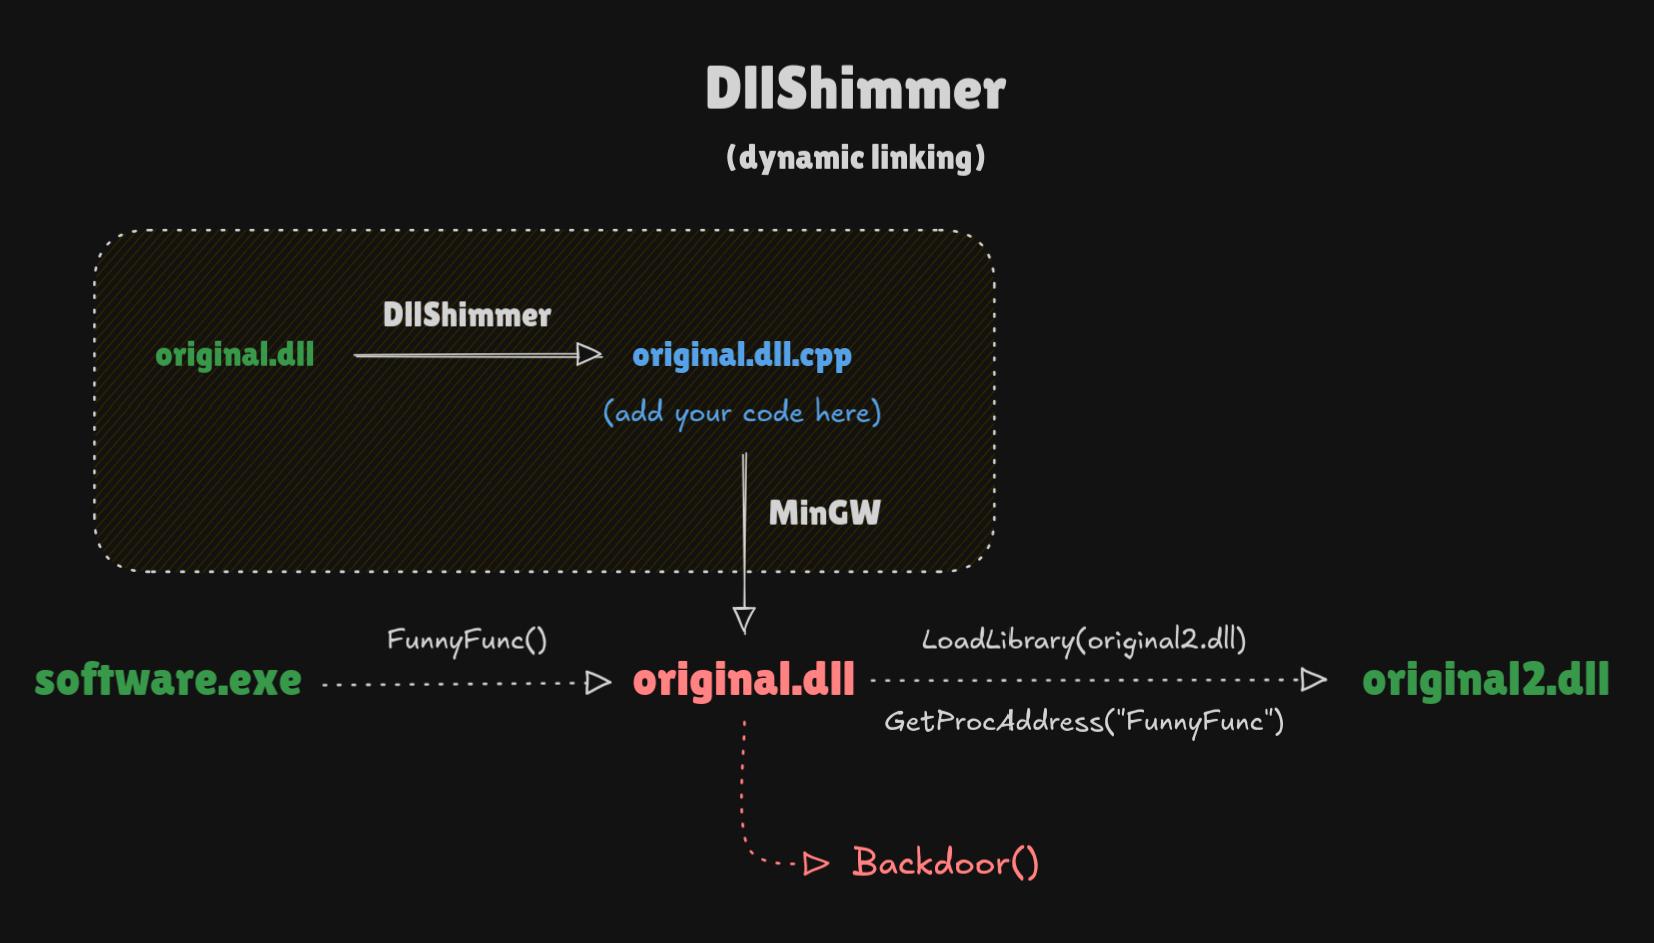 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
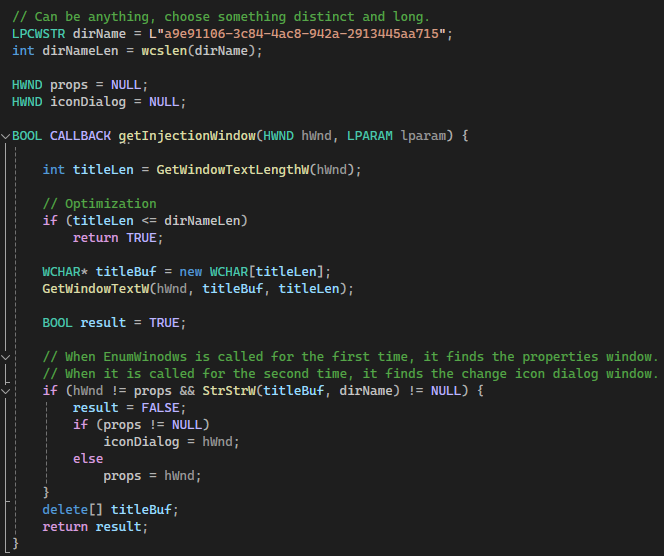 d419h/iconjector
Inject DLLs into the explorer process using icons
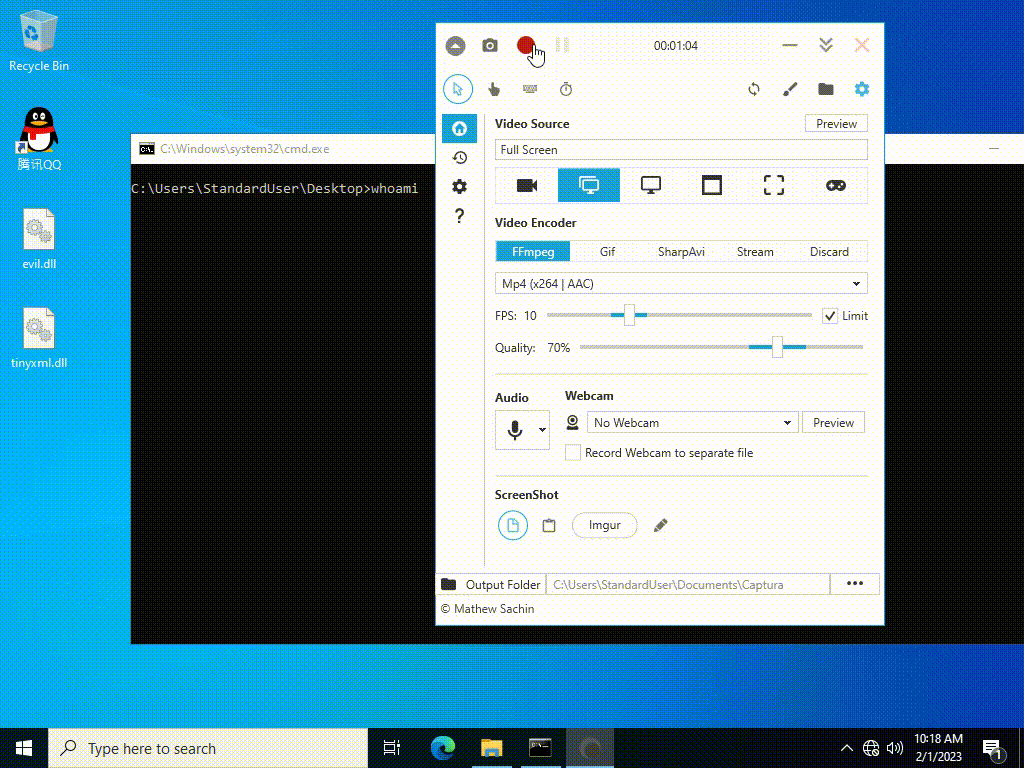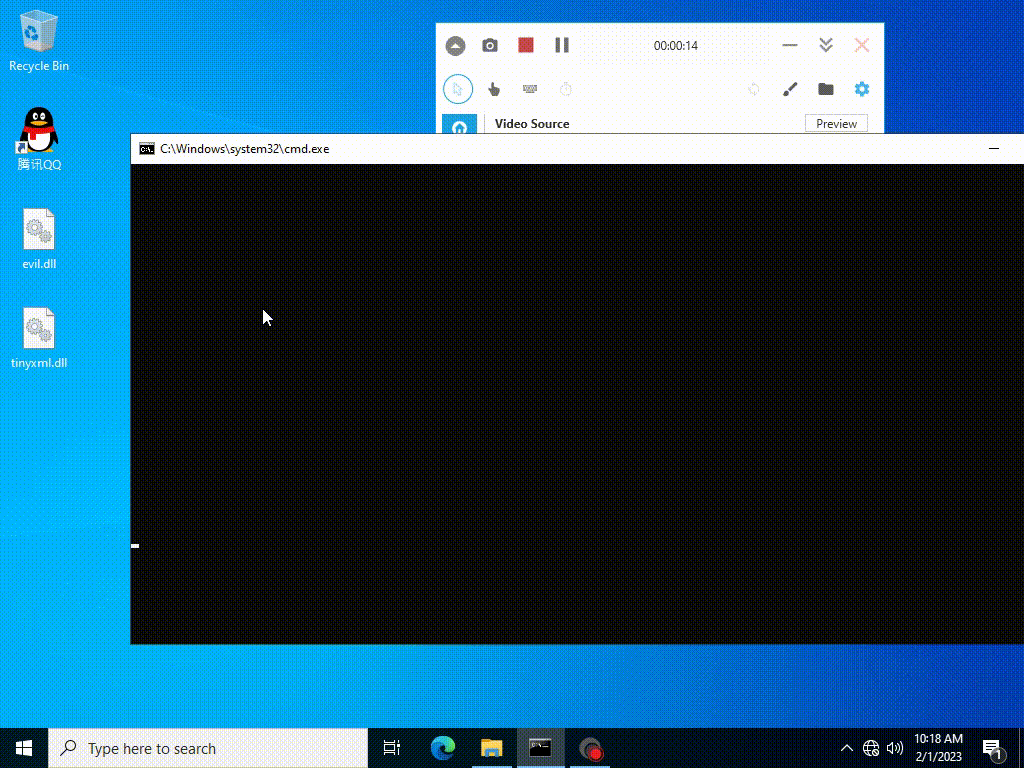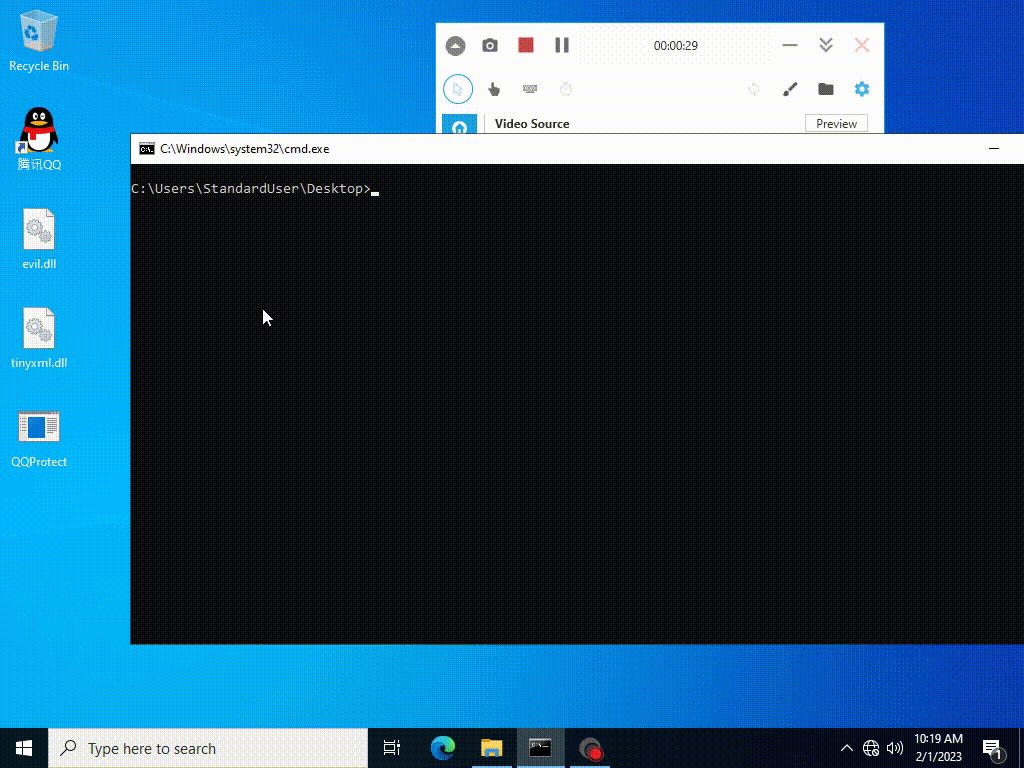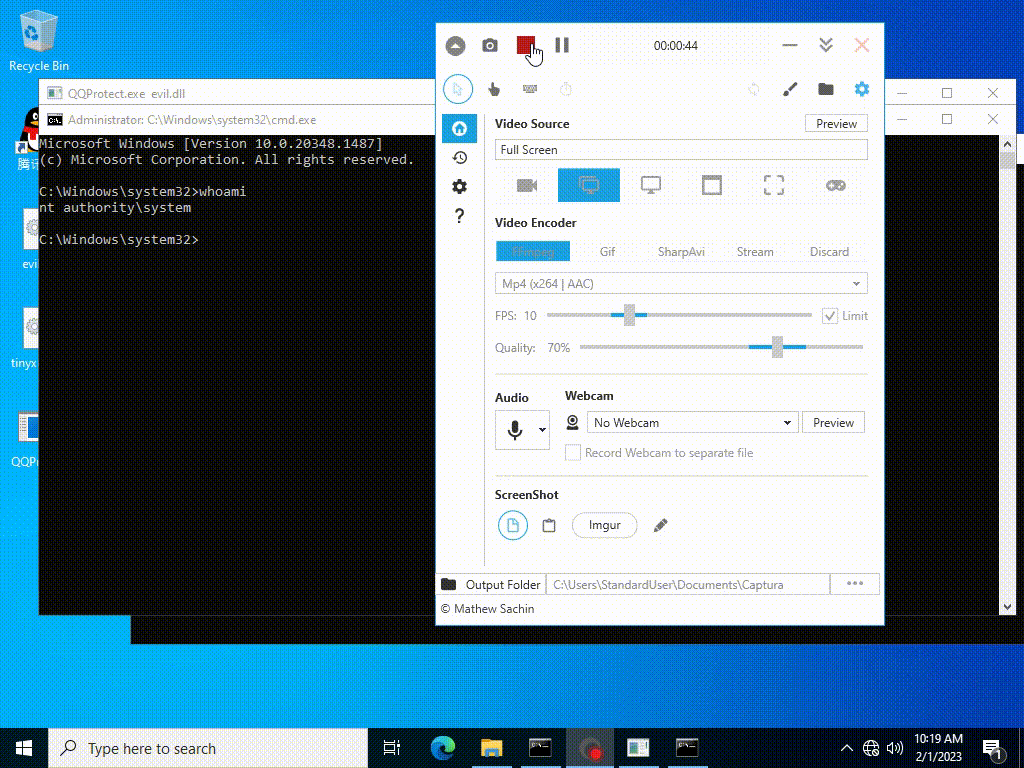 vi3t1/qq-tim-elevation
CVE-2023-34312
 ekultek/graffiti
A tool to generate obfuscated one liners to aid in penetration testing
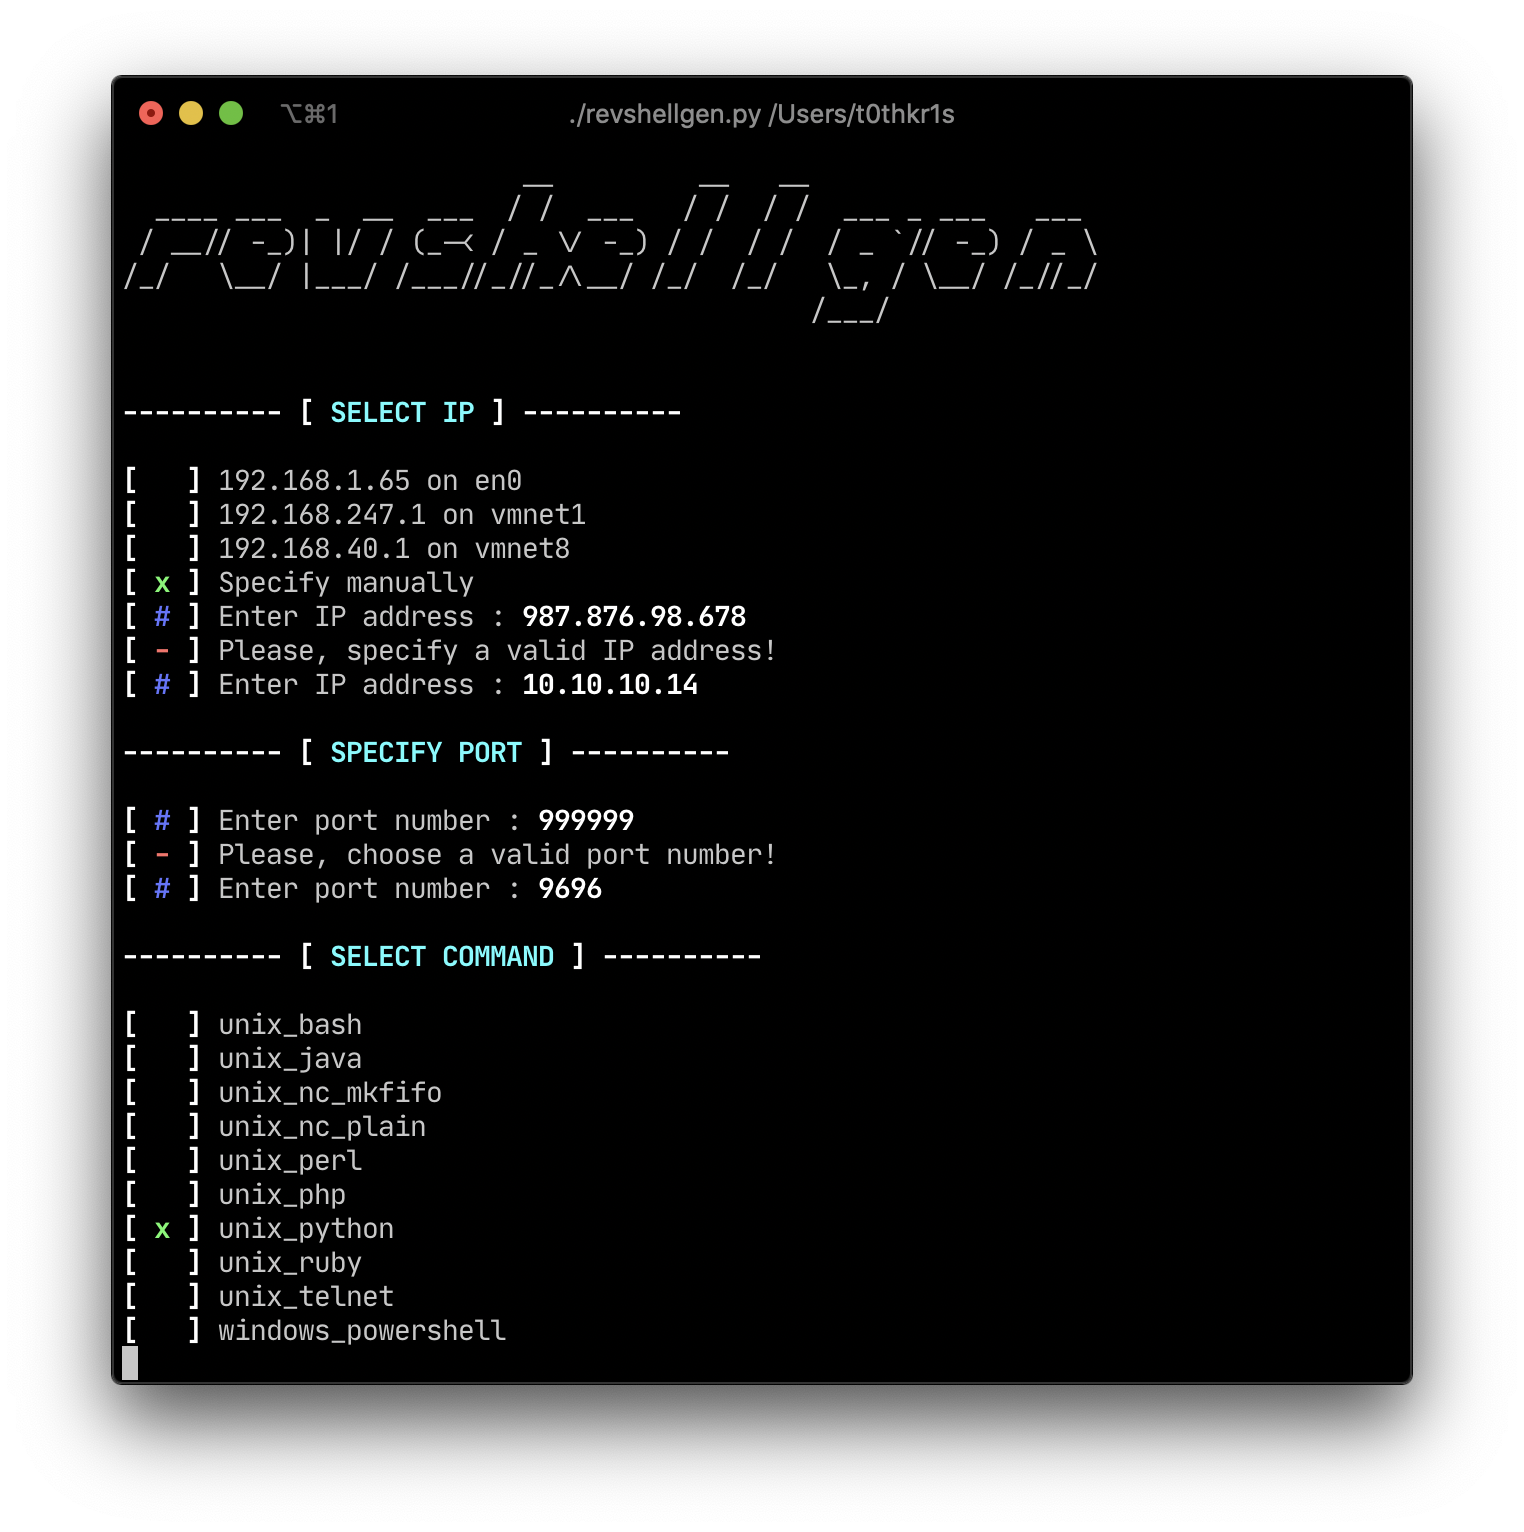 t0thkr1s/revshellgen
Reverse shell generator written in Python 3.