
cve-2021-31290
 qaisarafridi/cve-2021-31290
Proof-of-concept exploit for CVE-2021-31290, demonstrating a specific vulnerability in a web application. Intended for security testing and…
exploitationvulnerability-analysisweb-application-exploitation
qaisarafridi/cve-2021-31290Proof-of-concept exploit for CVE-2021-31290, demonstrating a specific vulnerability in a web application. Intended for security testing and…
 xmr110/cve-2022-1040
Proof-of-concept exploit for CVE-2022-1040, demonstrating exploitation of a web application vulnerability for security testing and research.
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 digininja/dvwa
Intentionally vulnerable PHP/MariaDB web application for practicing common web security vulnerabilities across multiple difficulty levels in a legal,…
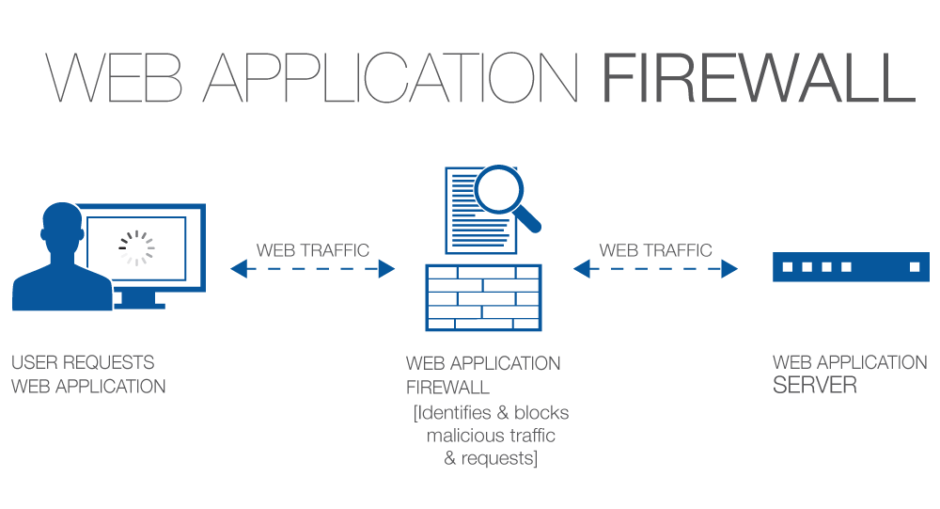 0xinfection/awesome-waf
Everything about Web Application Firewalls (WAFs) from Security Standpoint! 🔥

 mbrandner-group/webgoat.net
Deliberately vulnerable .NET web application for learning common web security flaws through hands-on exercises covering XSS, SQL injection, and other…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 g01d3nw01f/cve-2023-27372
Proof-of-concept exploit for CVE-2023-27372, demonstrating a remote code execution vulnerability in a web application. Intended for educational…
 xmohamed0/cve-2021-21315-poc
Proof-of-concept exploit for CVE-2021-21315, demonstrating remote code execution in a web application framework. Intended for security testing and…
 z3n70/cve-2023-23752
simple program for joomla CVE-2023-23752 scanner for pentesting and educational purpose
 artemcyberlab/project-project-chimera-exploiting-a-modern-wordpress-xxe-to-pillage-secrets-
The objective is to conduct a full-scale security assessment of a WordPress-based web application, culminating in a complete server compromise. The…
 shahibakes/cve-2023-34804
Exploit for CVE-2023-34804, a vulnerability in a web application, providing proof-of-concept code for security testing.
 iamarit/cve-2024-10858
Proof-of-concept exploit for CVE-2024-10858 targeting a vulnerable WordPress Jetpack plugin. Demonstrates exploitation of a security flaw in a…
 rampanic/cve-2019-19609-exploit
Exploit for CVE-2019-19609, a remote code execution vulnerability in a web application, providing proof-of-concept code for security testing.
 mr-n0b3dy/cve-2023-42362
Proof-of-concept exploit for CVE-2023-42362: unrestricted file upload leading to stored XSS and admin account takeover in NCR Teller web app 4.4.0.