

TokenStealer
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
impersonation-toolspost-exploitationprivilege-escalation+1
165
decoder-it/tokenstealerWindows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 artusec/pivotool
Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 zimedev/certipy-merged
Tool for Active Directory Certificate Services enumeration and abuse
 v-byte-cpu/sx
:vulcan_salute: Fast, modern, easy-to-use network scanner
 ttpreport/ligolo-mp
Multiplayer pivoting solution
 rek7/patchy
Automated Persistence and Lateral Movement using GCP Patch Management
 reverseclabs/sharpgpoabuse
SharpGPOAbuse is a .NET application written in C# that can be used to take advantage of a user's edit rights on a Group Policy Object (GPO) in order…
 med0x2e/gadgettojscript
A tool for generating .NET serialized gadgets that can trigger .NET assembly load/execution when deserialized using BinaryFormatter from JS/VBS/VBA…
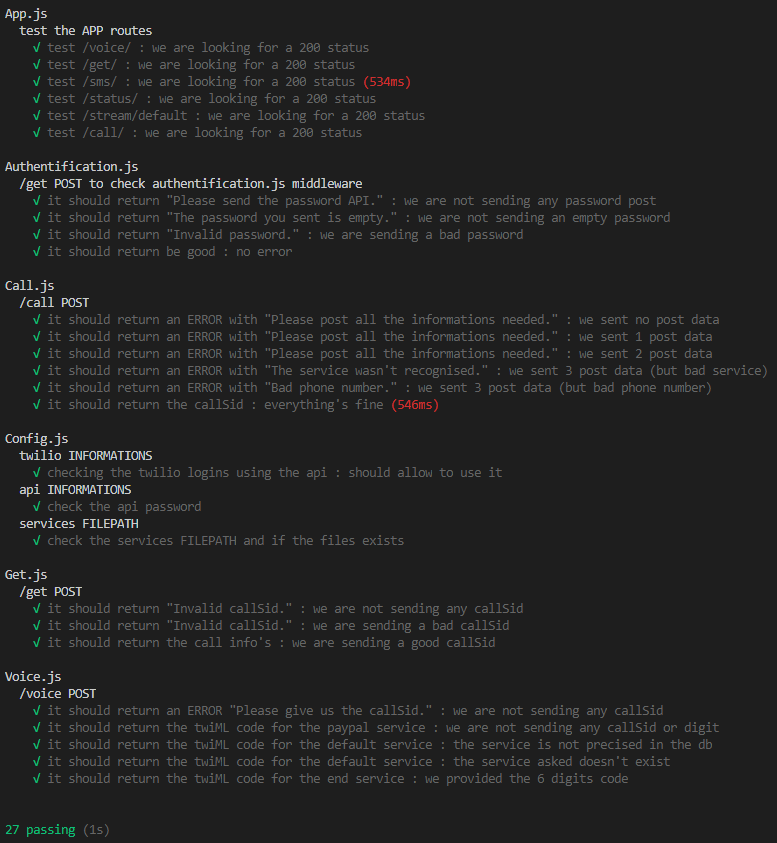 oriyomi12/otp-bot
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…
 blackarrowsec/mssqlproxy
mssqlproxy is a toolkit aimed to perform lateral movement in restricted environments through a compromised Microsoft SQL Server via socket reuse
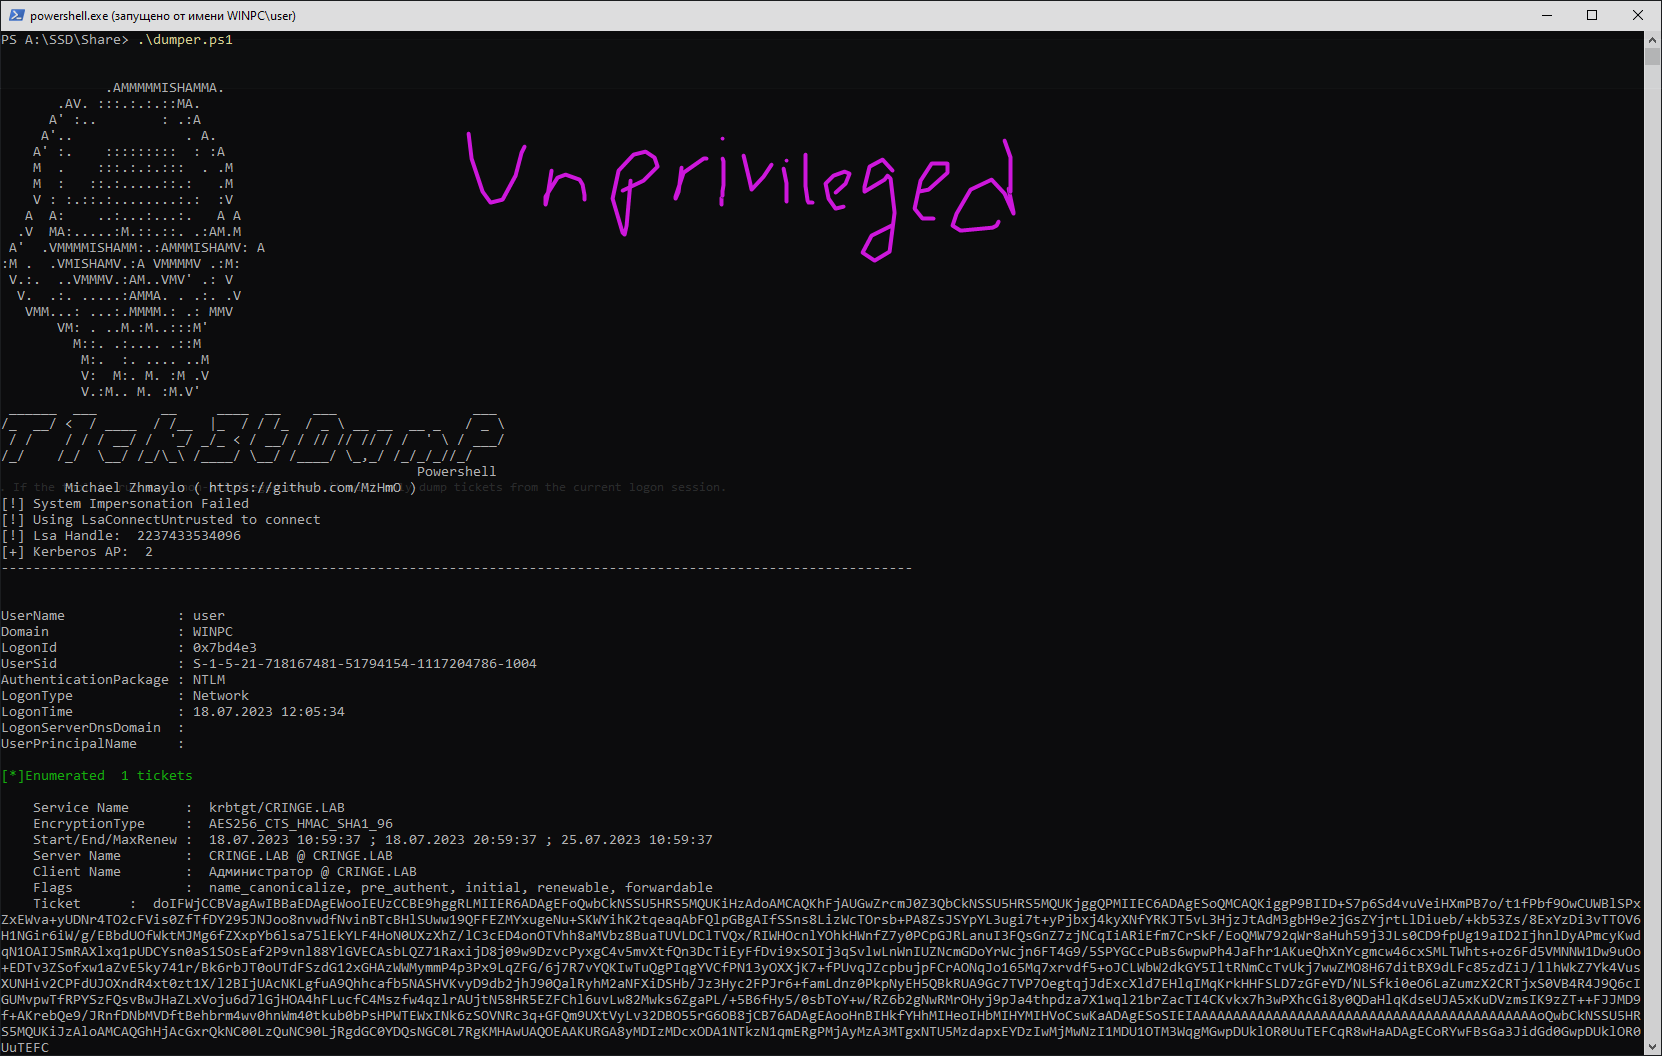 mzhmo/powershellkerberos
Some scripts to abuse kerberos using Powershell
 infamoussyn/rogue
An extensible toolkit providing penetration testers an easy-to-use platform to deploy Access Points during penetration testing and red team…
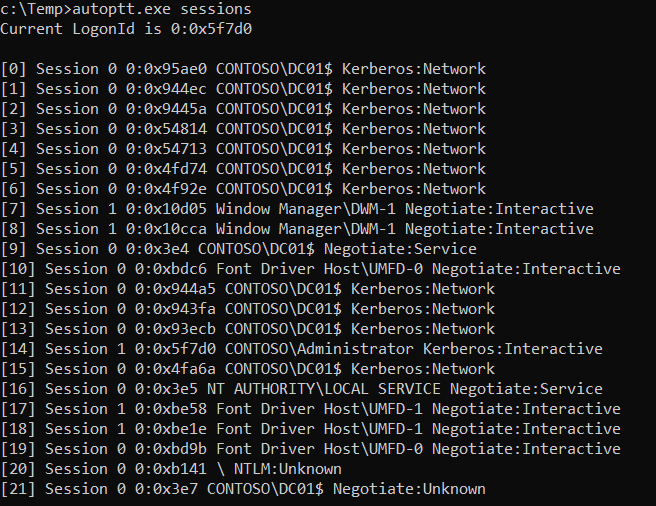 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.