
spring4shell-local-verification-lab
 meng-security/spring4shell-local-verification-lab
Spring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
code-analysiseducationexploitation+3
meng-security/spring4shell-local-verification-labSpring Framework CVE-2022-22965 本地影响条件验证、版本升级修复与复测项目
 erroristotle/dvdr_llm
Ensemble framework for software vulnerability detection and repair using multiple large language models, with consensus analysis and evaluation tools…
 nightfullstar/openclaw-defender
Multi-layer security framework for AI agent ecosystems. Provides pre-installation skill auditing, file integrity monitoring, runtime protection, and…
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
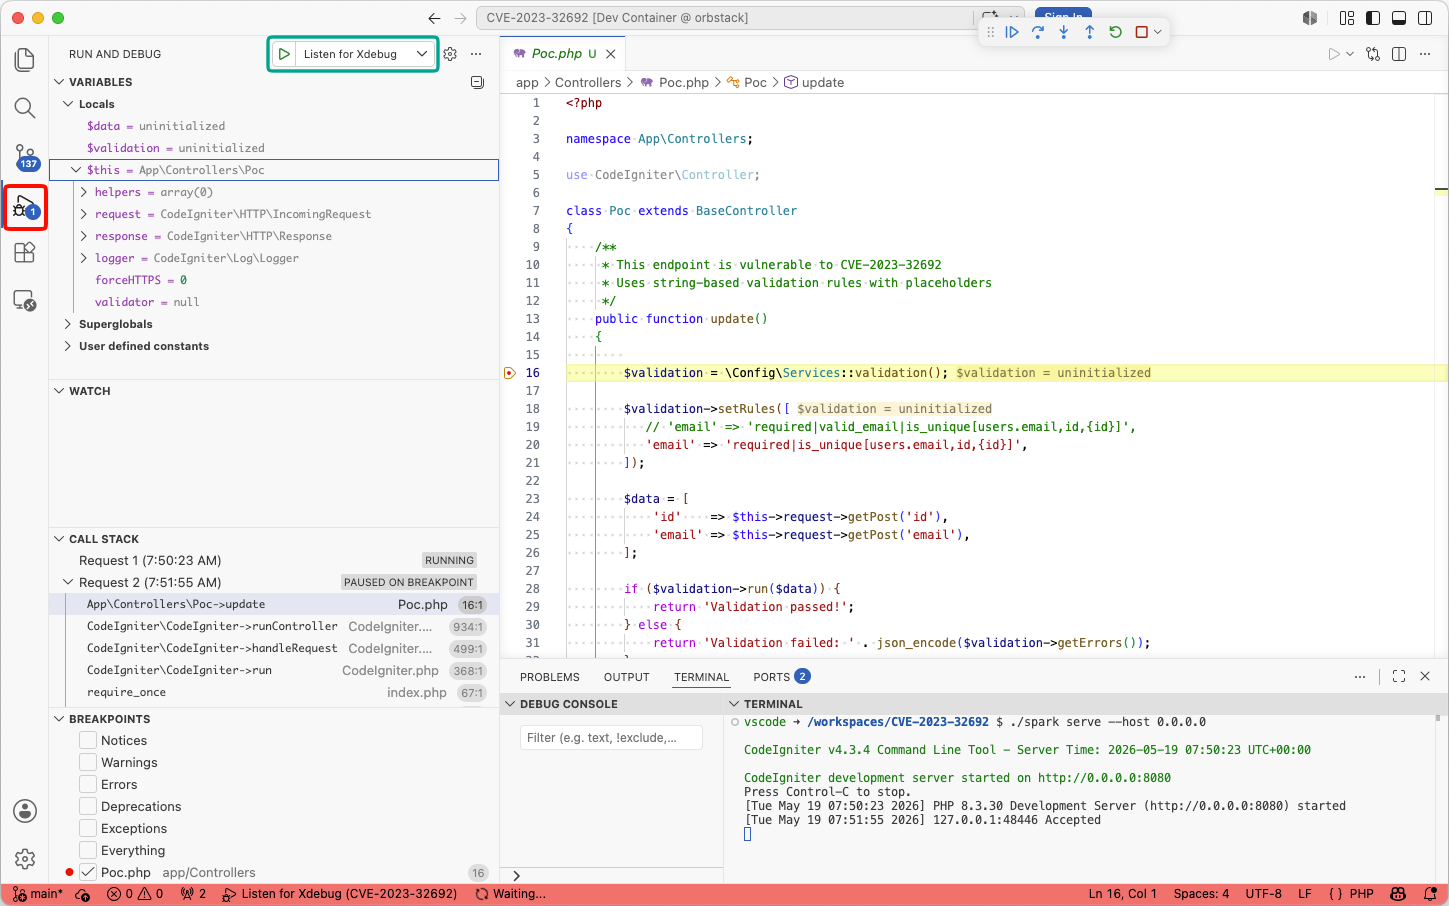 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 renweimeng/vlun-agent-x
VulnAgent-X: A Layered Agentic Framework for Repository-Level Vulnerability Detection
 roninforge/roninforge-hono
Cursor plugin for Hono v4 (TypeScript edge web framework). 59 LLM regressions with BAD/CORRECT pairs. Pinned to hono ^4.12.19 (>= 4.9.7 for…
 helsecert/cve-2022-22965
Detection scripts and guidance for CVE-2022-22965 (Spring4Shell) vulnerability in Spring Framework, including PowerShell and Bash scanners for…
 raptor-audit/raptor
Framework for auditing blockchain ecosystems, identifying smart contract vulnerabilities, and generating structured findings with multi-platform…
 c4mx/cve-2022-22965_poc
Proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) targeting Java Spring Framework applications via crafted HTTP requests.
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
 uthrasri/frame_cve-2023-40133_136_137
Exploit for CVE-2023-40133, a vulnerability in Android's Framework component, enabling code execution analysis and security testing.
 luoqianlin/cve-2022-22965
Spring Framework RCE exploit (CVE-2022-22965) with analysis code and educational walkthrough for understanding the vulnerability and exploitation…
 snicoll-scratches/spring-boot-cve-2022-22965
Showcase of overridding the Spring Framework version in older Spring Boot versions
 funcid/cve-2024-38828
PoC and fix for CVE-2024-38828: Spring Framework DoS via Content-Length manipulation in ByteArrayHttpMessageConverter. Includes load testing,…
 epicosy/vul4j-23
Curated Java web framework vulnerability (CVE-2016-5394) for Apache Sling, designed for security testing, exploitation practice, and vulnerability…
 shoucheng3/testng-team__testng_cve-2022-4065_7-5
Java testing framework for unit, integration, and end-to-end tests with annotations, data-driven testing, and parallel execution support.