
CVE-2023-27524-POC
 maanvader/cve-2023-27524-poc
A POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.
authentication-authorizationeducationexploitation+3
maanvader/cve-2023-27524-pocA POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.
 jet-pentest/cve-2020-29666
Proof-of-concept for CVE-2020-29666: directory listing vulnerability in Lan ATMService M3 ATM Monitoring System 6.1.0 that exposes log files…
 guy2610/tough-cookie-patch-cve-2023-26136
RFC6265-compliant cookie parsing and CookieJar management library for Node.js, with CVE-2023-26136 security patch. Supports cookie creation,…
 anestisb/webacoo
Web Backdoor Cookie Script-Kit
 0xr2r/cve-2024-3400-palo-alto-os-command-injection
Proof-of-concept exploitation steps for CVE-2024-3400, demonstrating unauthenticated command injection in Palo Alto GlobalProtect via crafted cookie…
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 ekkoo-z/cve-2019-18935-bypasswaf
Exploit for CVE-2019-18935 (Telerik UI) with WAF bypass via encrypted cookie payload injection and custom memory shell deployment.
 baktistr/cve-2026-23550-poc
Bash-based proof-of-concept tester for CVE-2026-23550. Checks WordPress modular connector login endpoints for admin cookie issuance and verifies…
 0xzerosec/cve-2025-55888
Proof-of-concept exploit demonstrating an XSS vulnerability in ARD's Ajax transaction manager endpoint through unsanitized accountName input,…
 randomrobbiebf/cve-2023-6700
Cookie Information | Free GDPR Consent Solution <= 2.0.22 - Authenticated (Subscriber+) Arbitrary Options Update
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 87achrafg-stack/cve-2026-5513
CVE-2026-5513 — Bookly ≤ 27.2 Stored XSS via Cookie
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
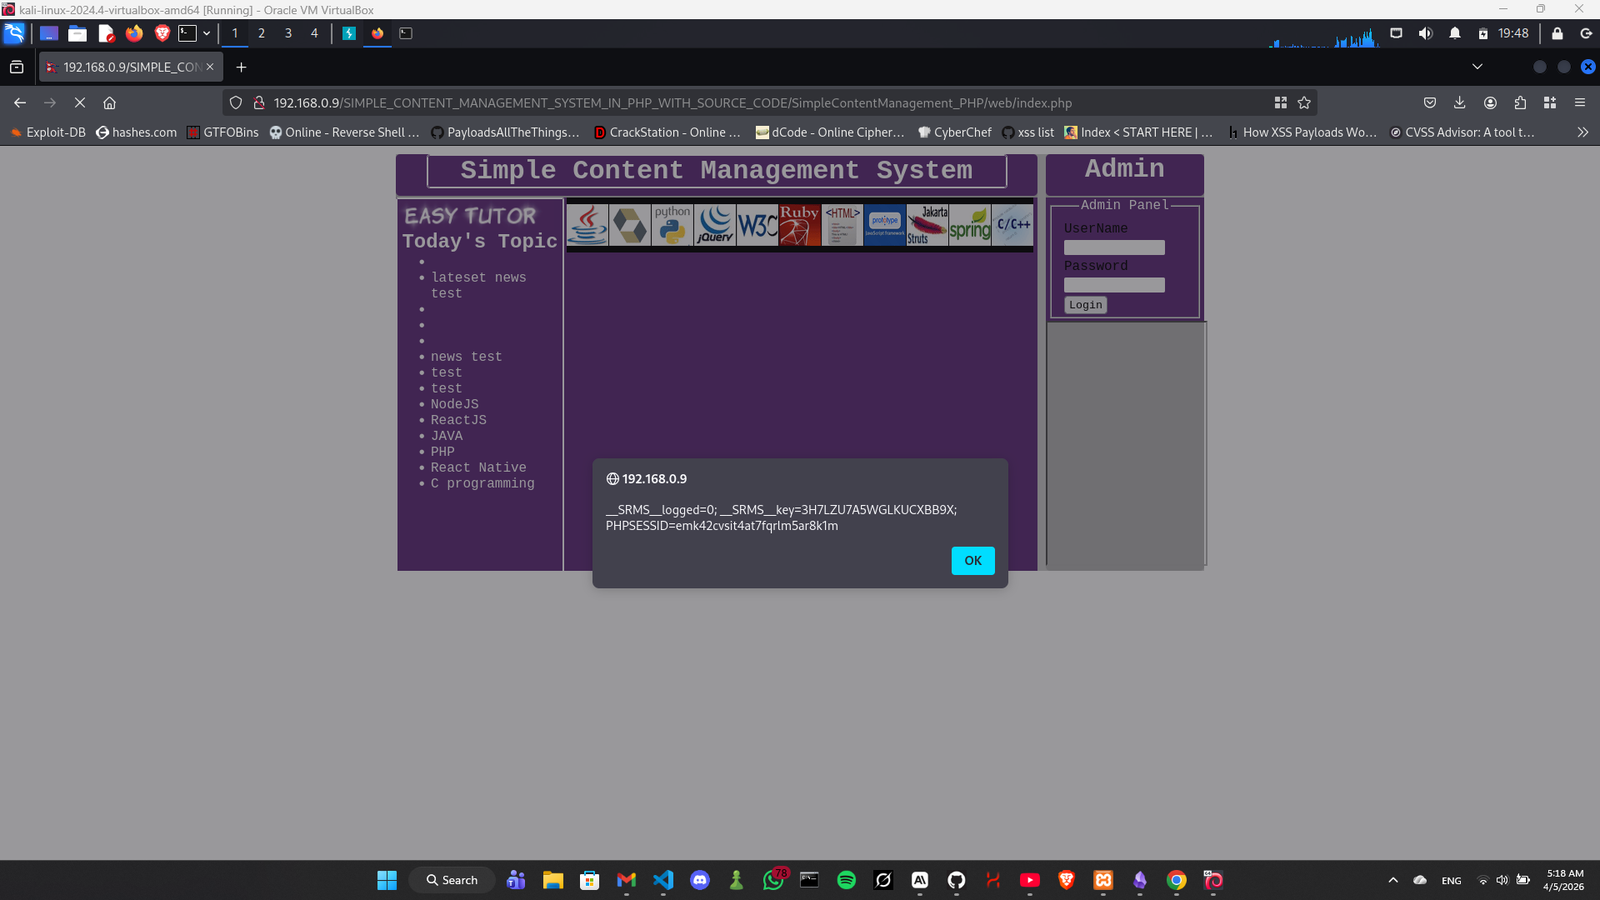 xmyronn/cve-2026-6184-stored-xss
Proof-of-concept for a stored XSS vulnerability in Simple Content Management System PHP, demonstrating session cookie theft via unsanitized News…
 calfcrusher/cve-2023-31853
Proof-of-concept for reflected XSS in Cudy LT400 web interface, demonstrating session cookie theft and admin takeover via crafted requests.
 dylandavis1/cve-2025-63708
Proof-of-concept exploit for CVE-2025-63708, a stored XSS vulnerability in AI Font Matcher. Demonstrates session cookie theft via unsanitized font…
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…