

ecapture
 gojue/ecapture
Capture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
android-securitydatabase-securitydynamic-analysis-sandboxing+3
gojue/ecaptureCapture SSL/TLS plaintext with eBPF—no MITM proxy or custom CA installation. Supports Linux and Android on x86_64 and arm64.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 hhhrrrttt222111/ethical-hacking-tools
Complete Listing and Usage of Tools used for Ethical Hacking
 crazy-max/windowsspyblocker
Block spying and tracking on Windows
 pentesteracademy/patoolkit
PA Toolkit is a collection of traffic analysis plugins focused on security
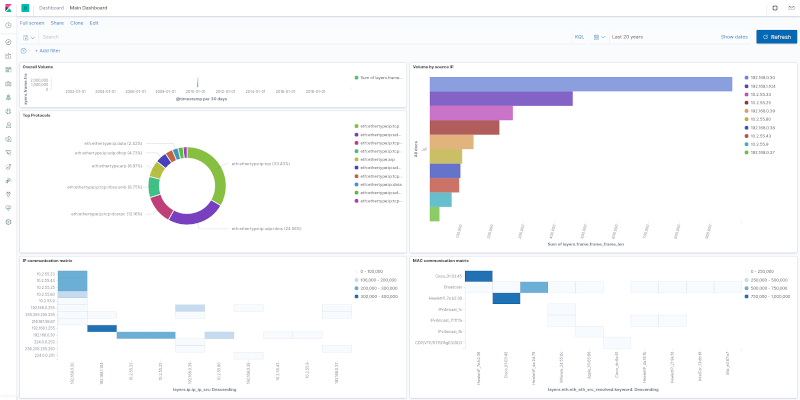 h21lab/tsharkvm
tshark + ELK analytics virtual machine
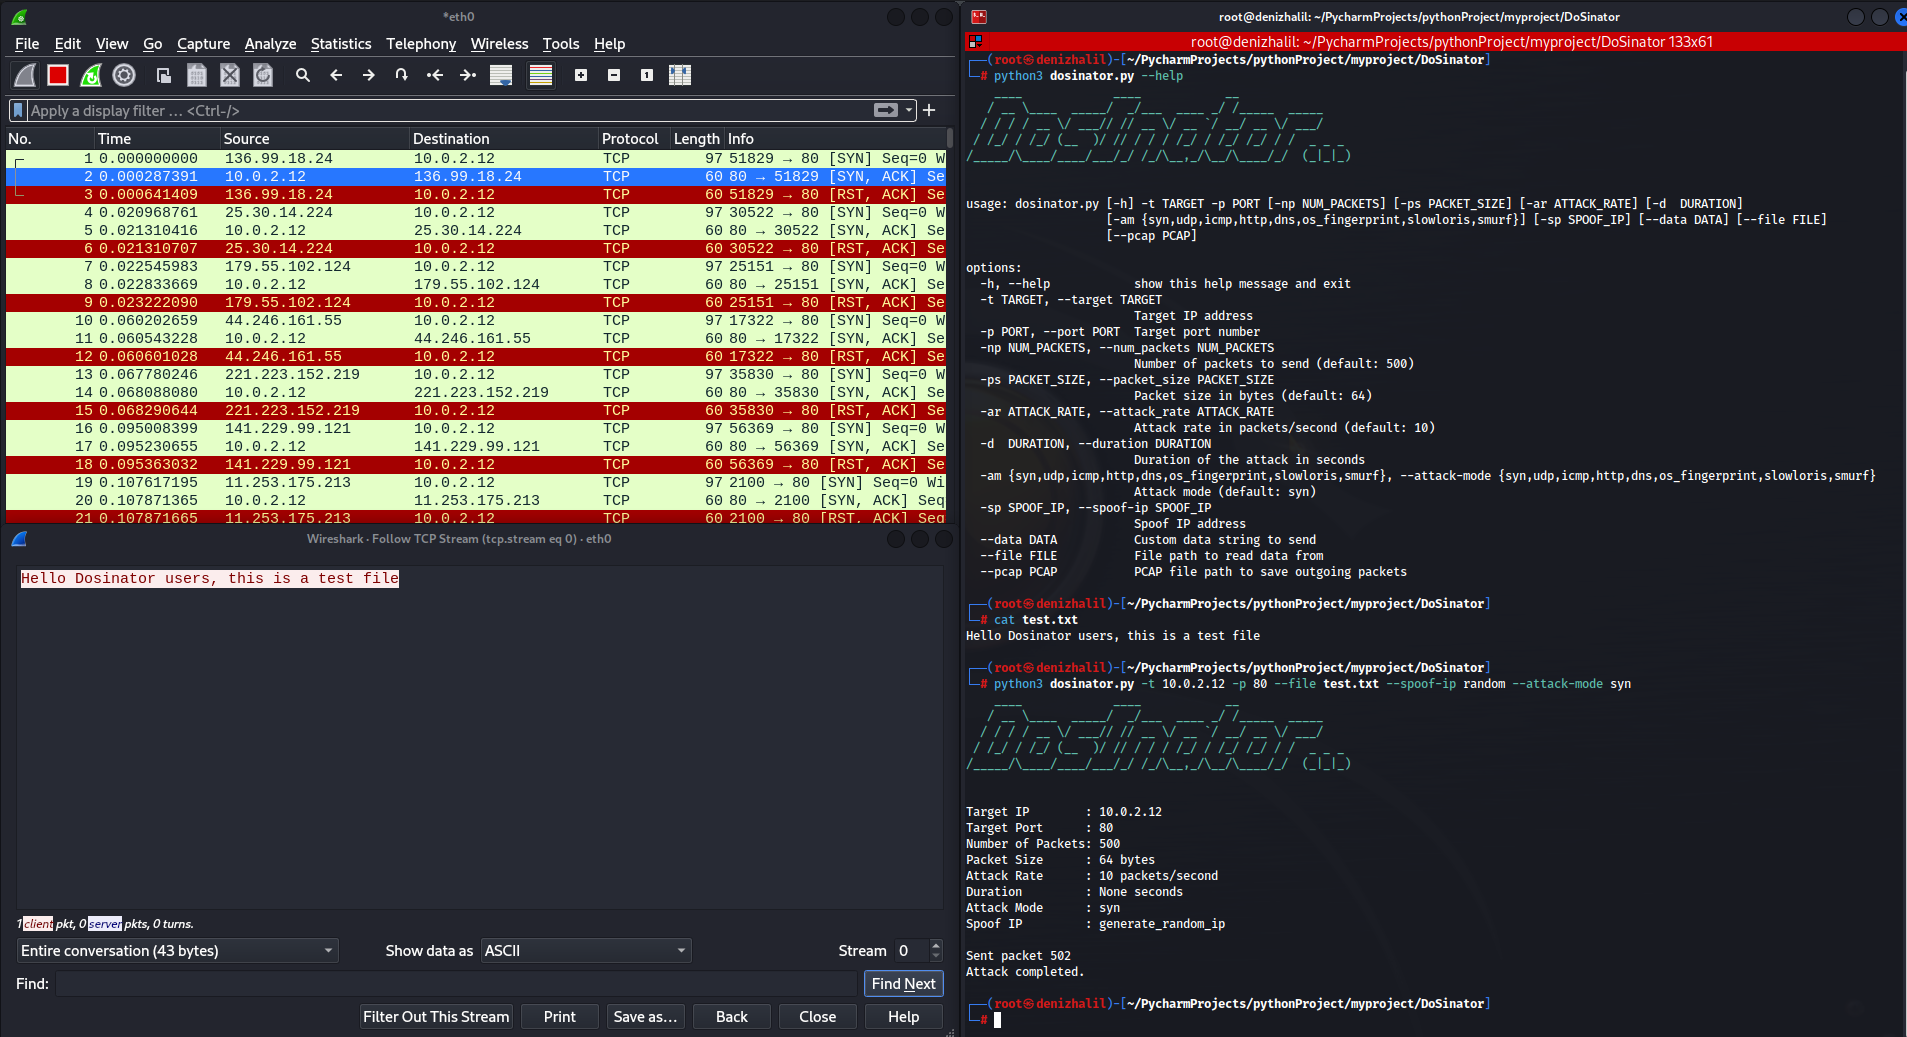 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 emrekybs/bluefish
Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
 0x0allenace/windows-malware-behavioral-analysis
Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…
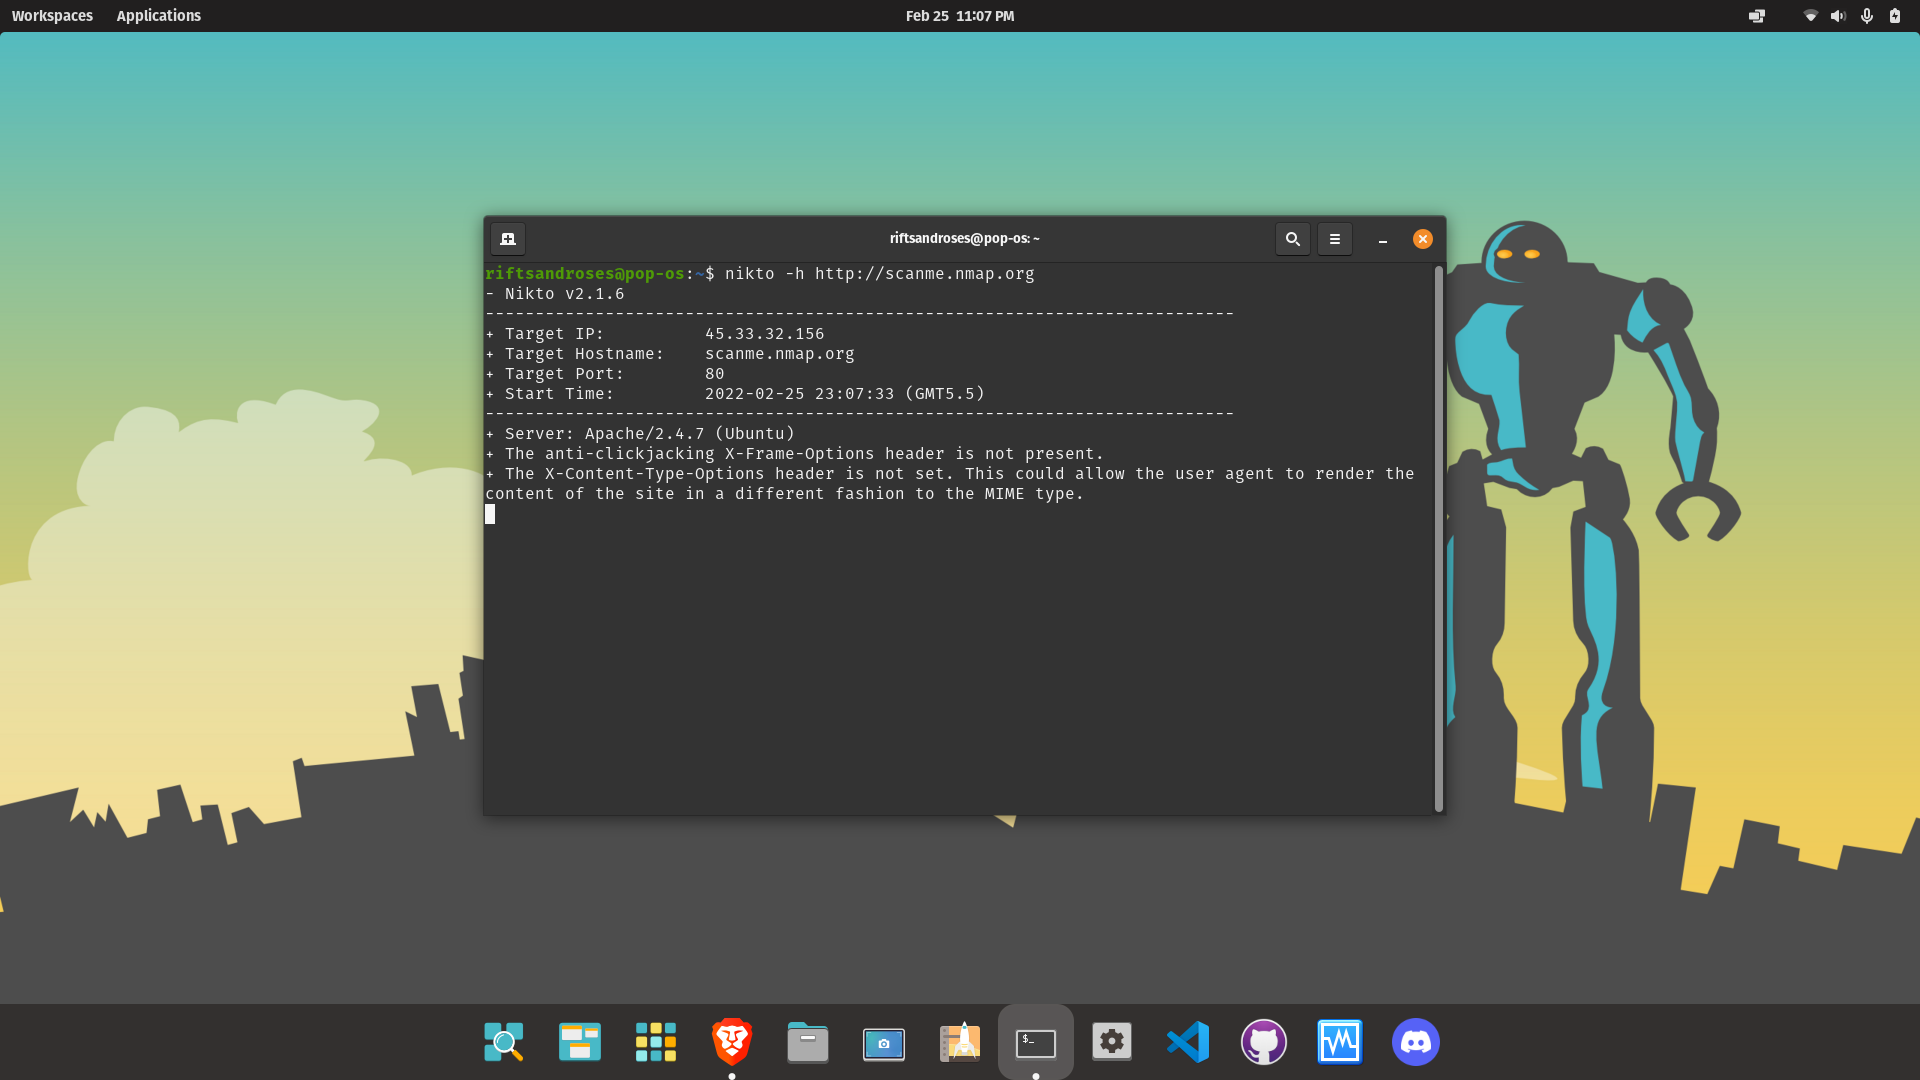
 ilk-toolkit/ilk-toolkit
A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".