
exploits
 xiphosresearch/exploits
Miscellaneous exploit code
exploitationpayload-developmentpenetration-testing+3
1.6k
xiphosresearch/exploitsMiscellaneous exploit code
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
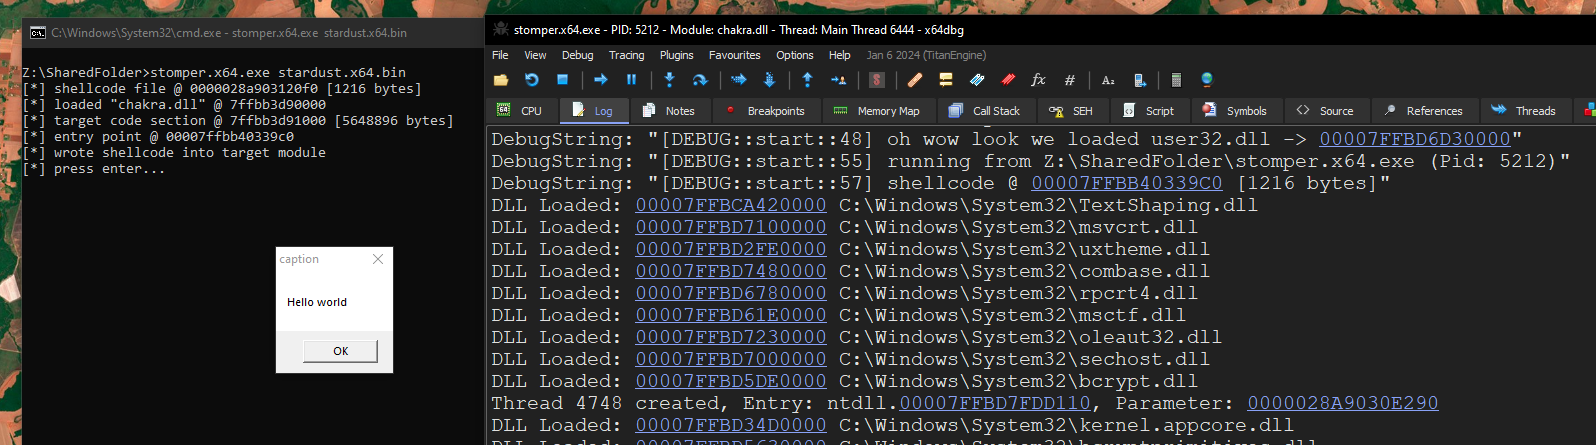 cracked5pider/stardust
A modern 32/64-bit position independent implant template
 hakluke/weaponised-xss-payloads
XSS payloads designed to turn alert(1) into P1
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 ne0nd0g/go-shellcode
A repository of Windows Shellcode runners and supporting utilities. The applications load and execute Shellcode using various API calls or techniques.
 r00t-3xp10it/fakeimageexploiter
Use a Fake image.jpg to exploit targets (hide known file extensions)
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
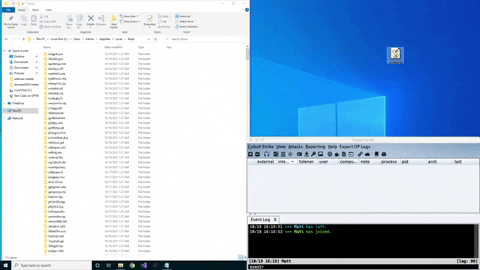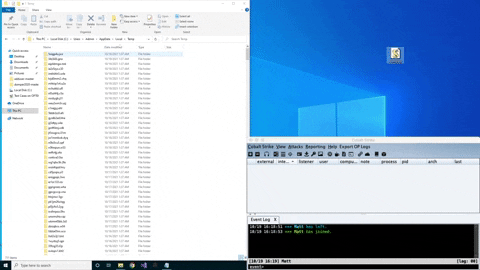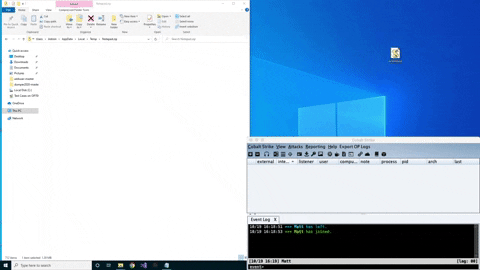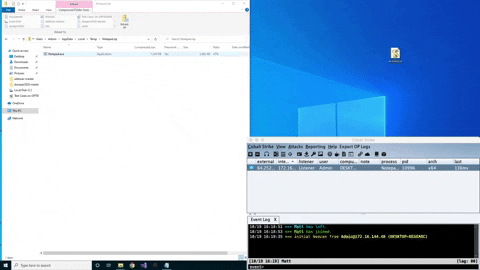 tylous/zipexec
A unique technique to execute binaries from a password protected zip
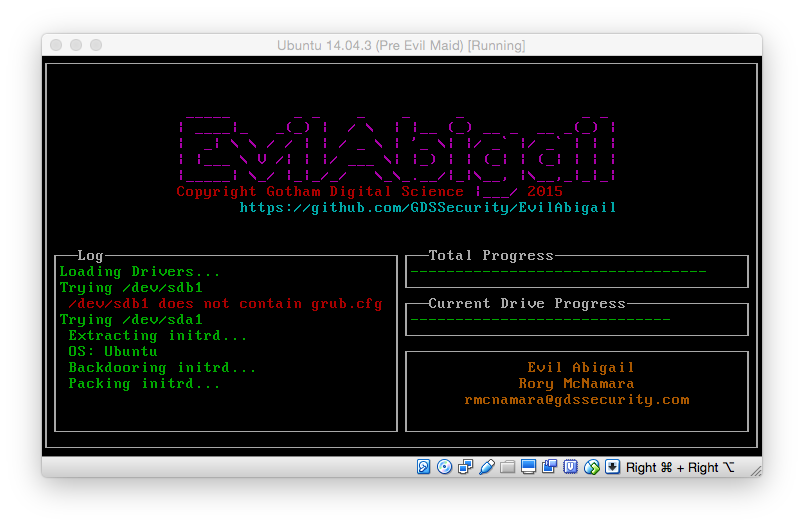 strozfriedberg/evilabigail
Automated Linux evil maid attack
 khr0x40sh/macroshop
Collection of scripts to aid in delivering payloads via Office Macros. Most are python. See http://khr0x40sh.wordpress.com for details.
 danielbohannon/invoke-cradlecrafter
PowerShell Remote Download Cradle Generator & Obfuscator
 sighook/pixload
Image Payload Creating/Injecting tools
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…
 safebreach-labs/poolparty
A set of fully-undetectable process injection techniques abusing Windows Thread Pools
 sin5678/gh0st
a open source remote administrator tool