
CVE-2024-5243-pwn2own-toronto-2023
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
binary-exploitationeducationexploitation+4
redpack-kr/cve-2024-5243-pwn2own-toronto-2023Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
 trinadh465/platform_system_netd_aosp10_r33_cve-2023-40084
Android netd vulnerability analysis and exploitation research for CVE-2023-40084, focusing on the platform's network daemon.
 lcartey/proftpd-cve-2019-12815
Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 zecure/shadowd
The Shadow Daemon web application firewall server
 thinkst/opencanary
Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
 nlnetlabs/nsd
High-performance authoritative DNS server with DNSSEC support, delivering RFC-compliant name resolution for secure and reliable production…
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
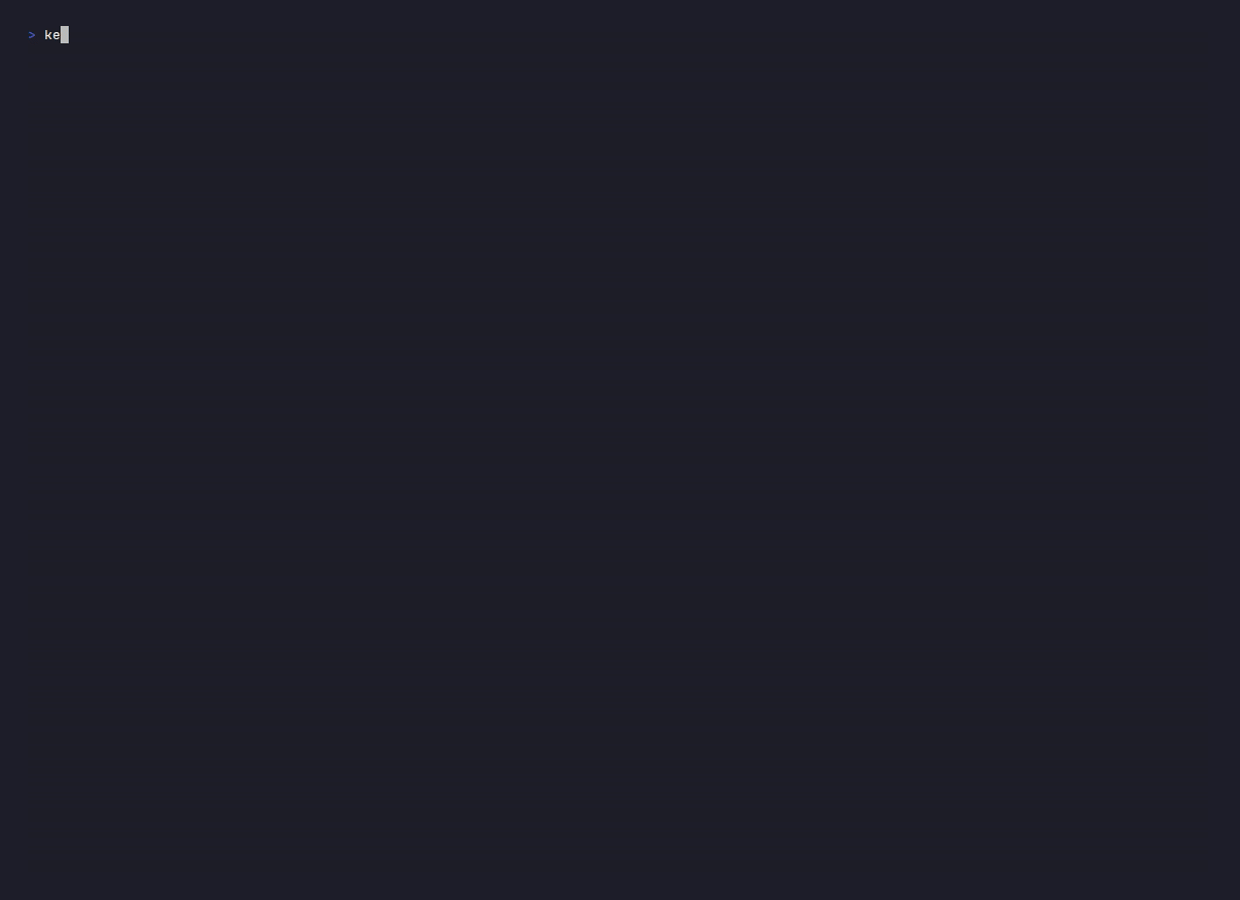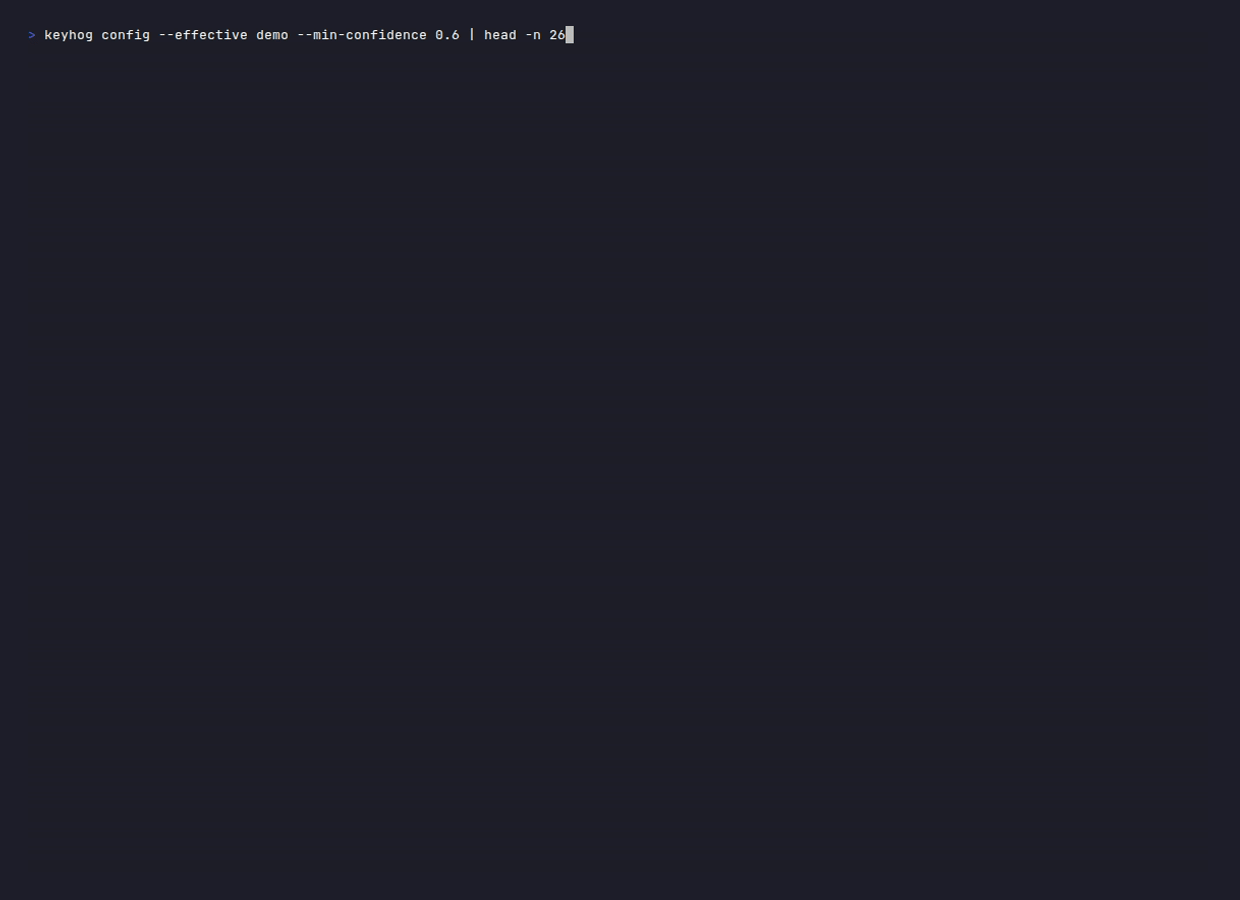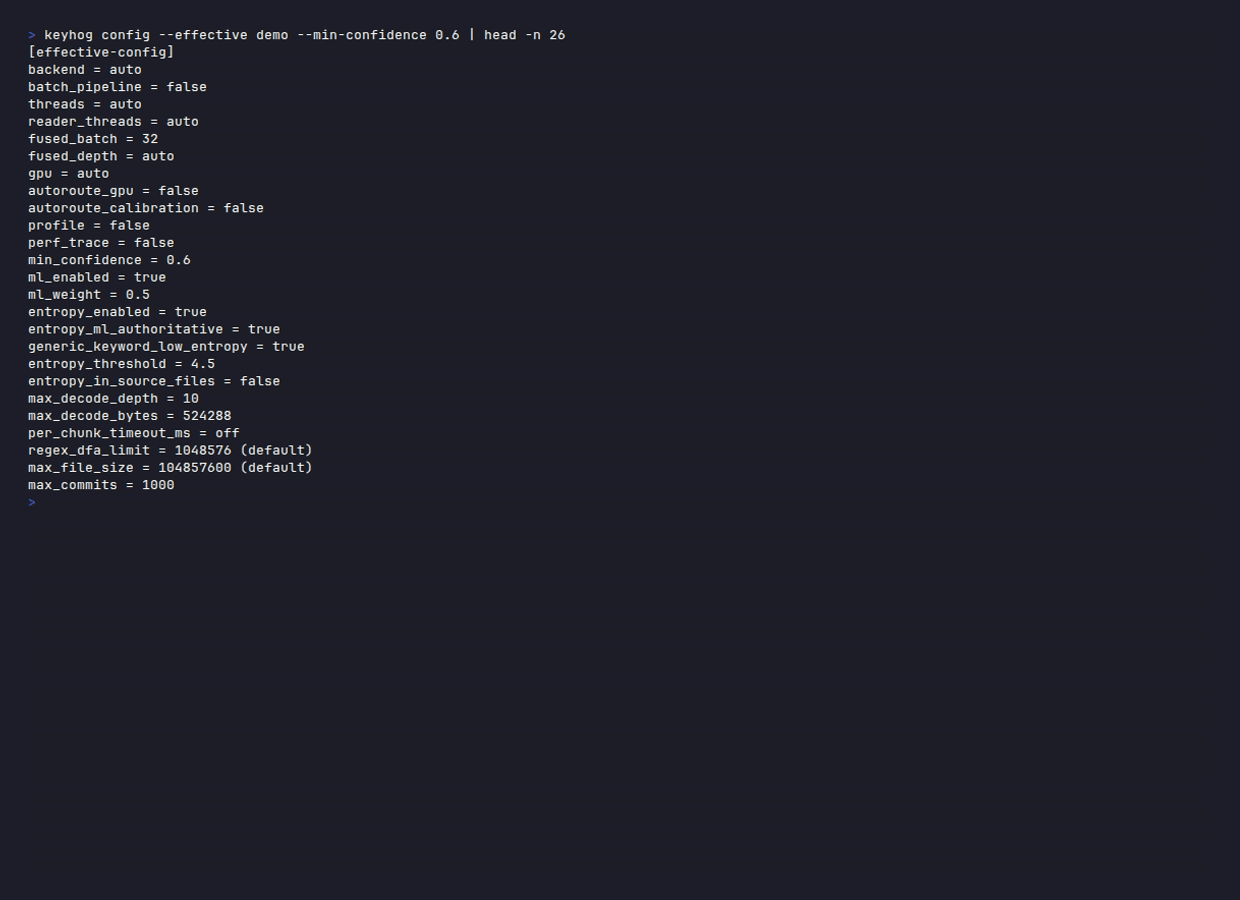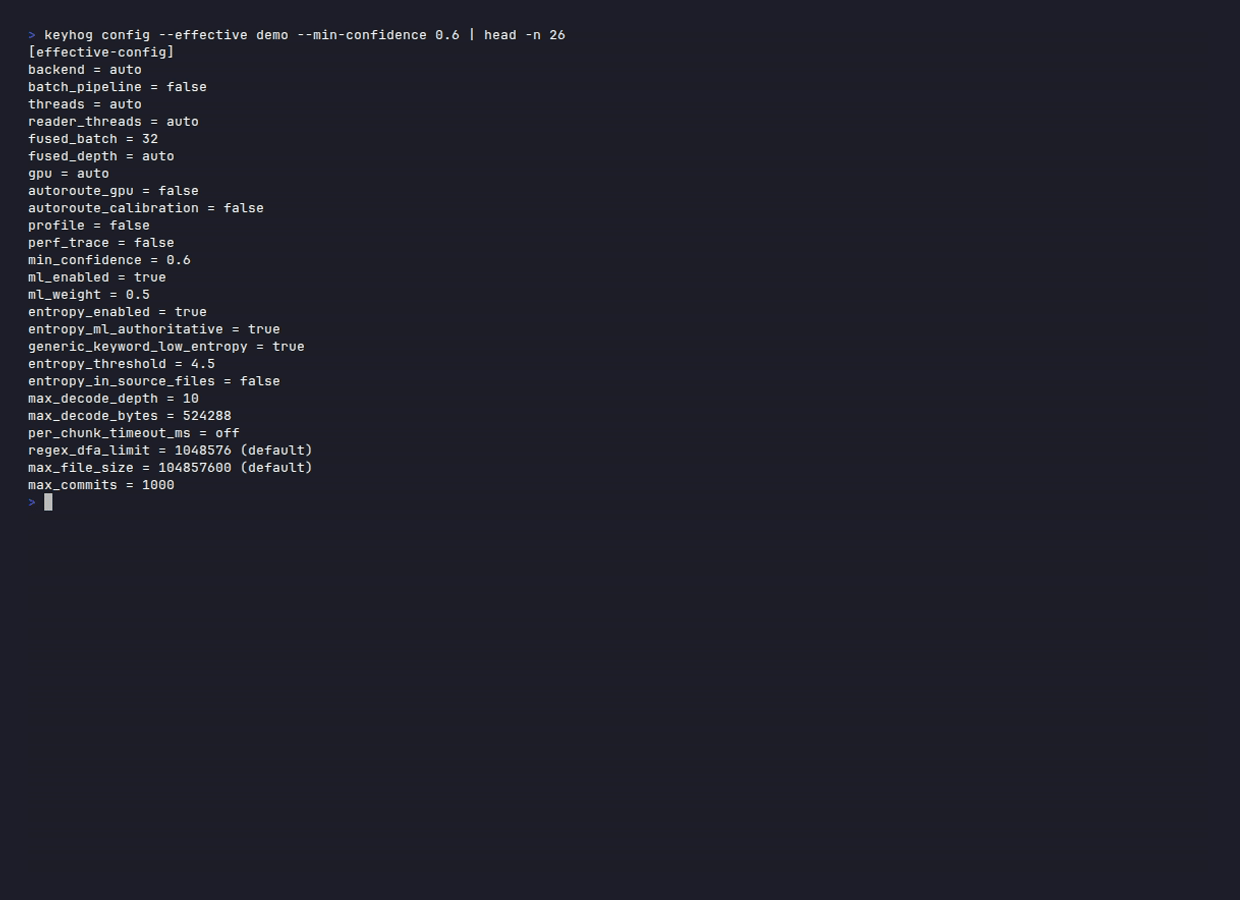 santhreal/keyhog
Open-source secret scanner in Rust
 mellow-hype/cve-2024-20017
exploits for CVE-2024-20017
 vozec/cve-2026-41651
Exploits a TOCTOU race in PackageKit's transaction handler to install arbitrary packages as root, achieving local privilege escalation and a SUID…

 bazad/launchd-portrep
CVE-2018-4280: Mach port replacement vulnerability in launchd on macOS 10.13.5 leading to local privilege escalation and SIP bypass.
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
