
Archived
Source
 librewolf-community/browser/source
Development has moved to https://codeberg.org/librewolf/source
educationprivacyscripting-automation+2
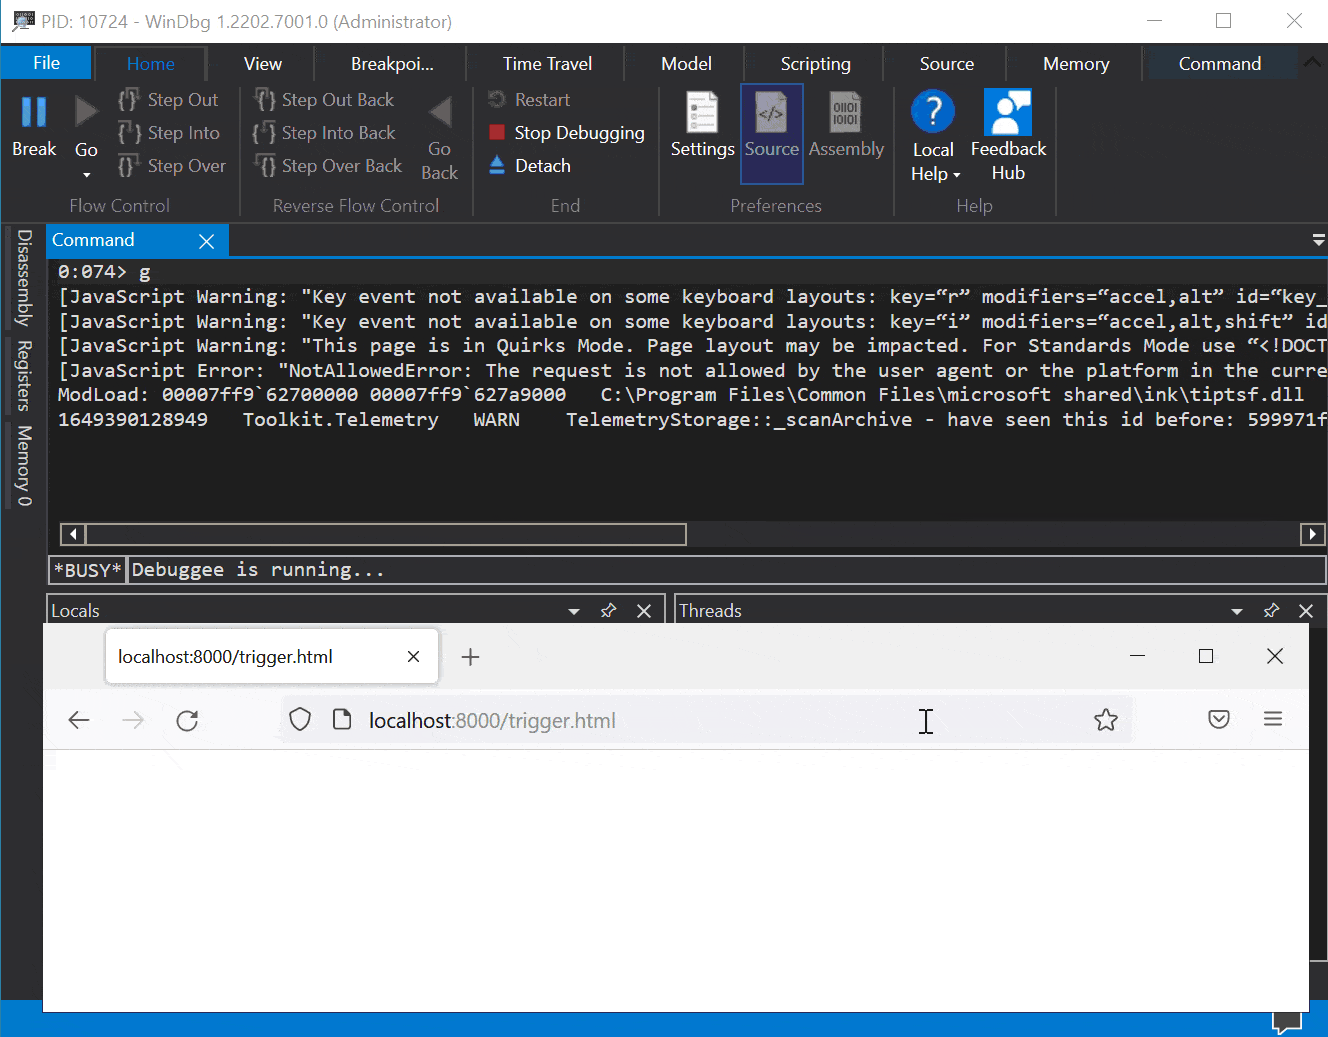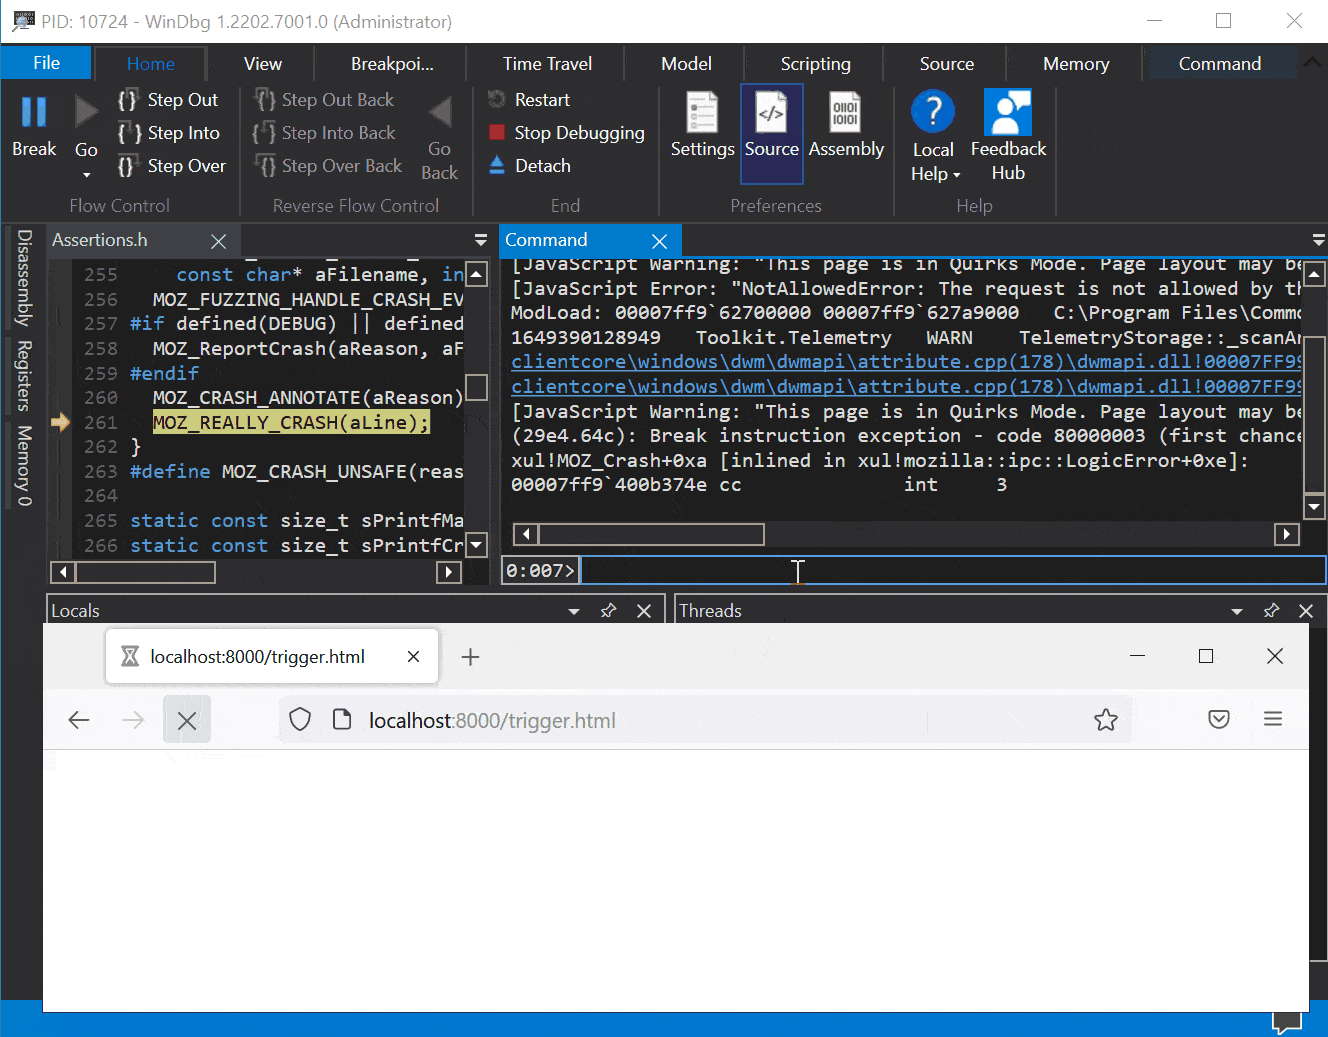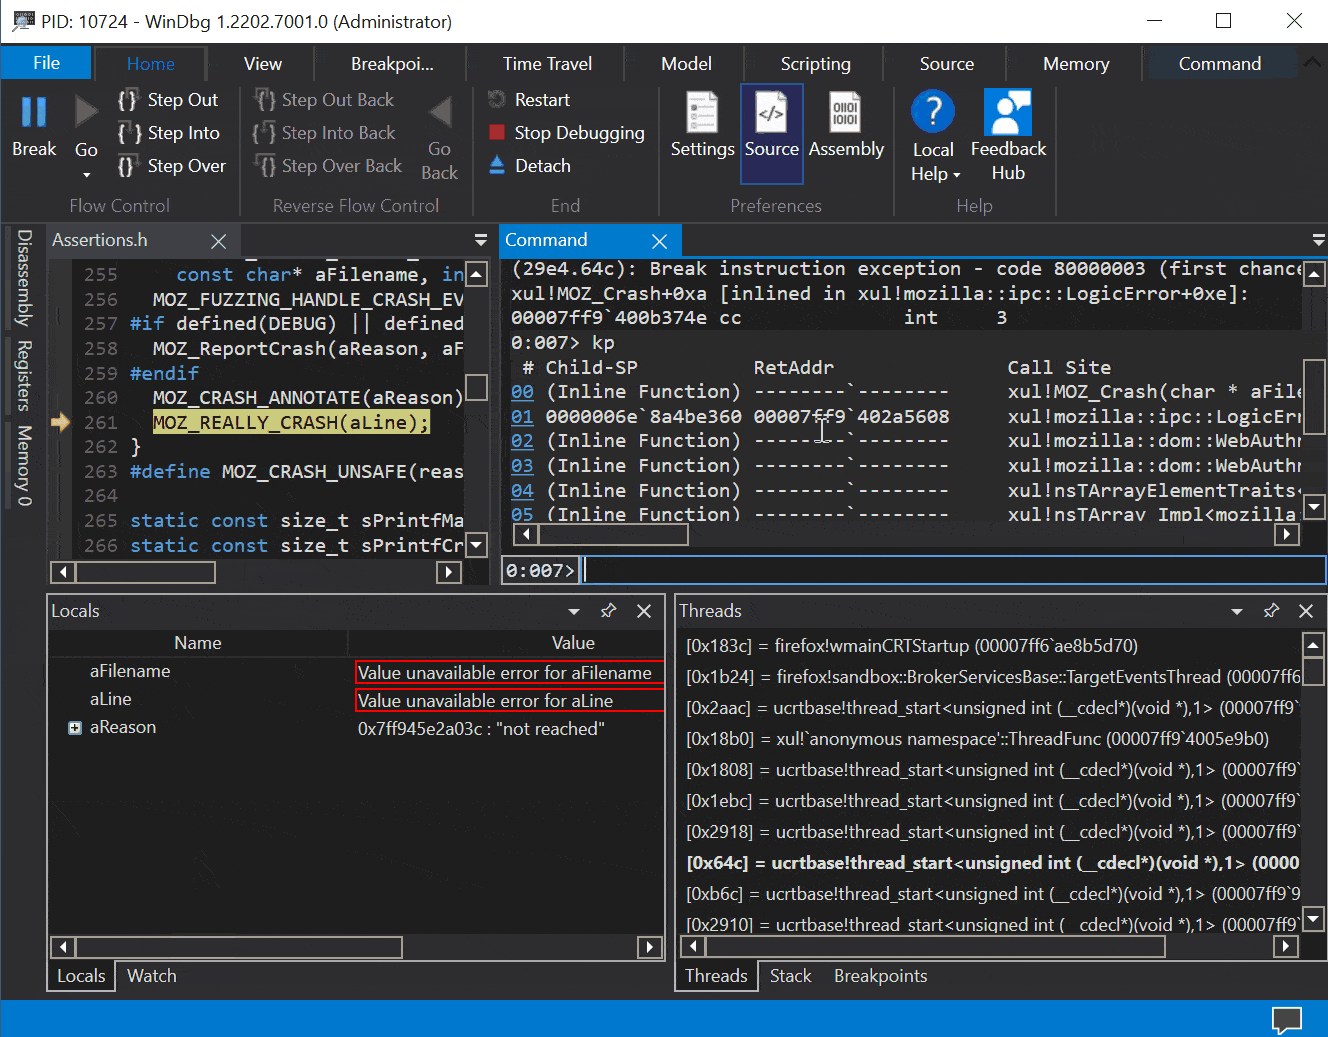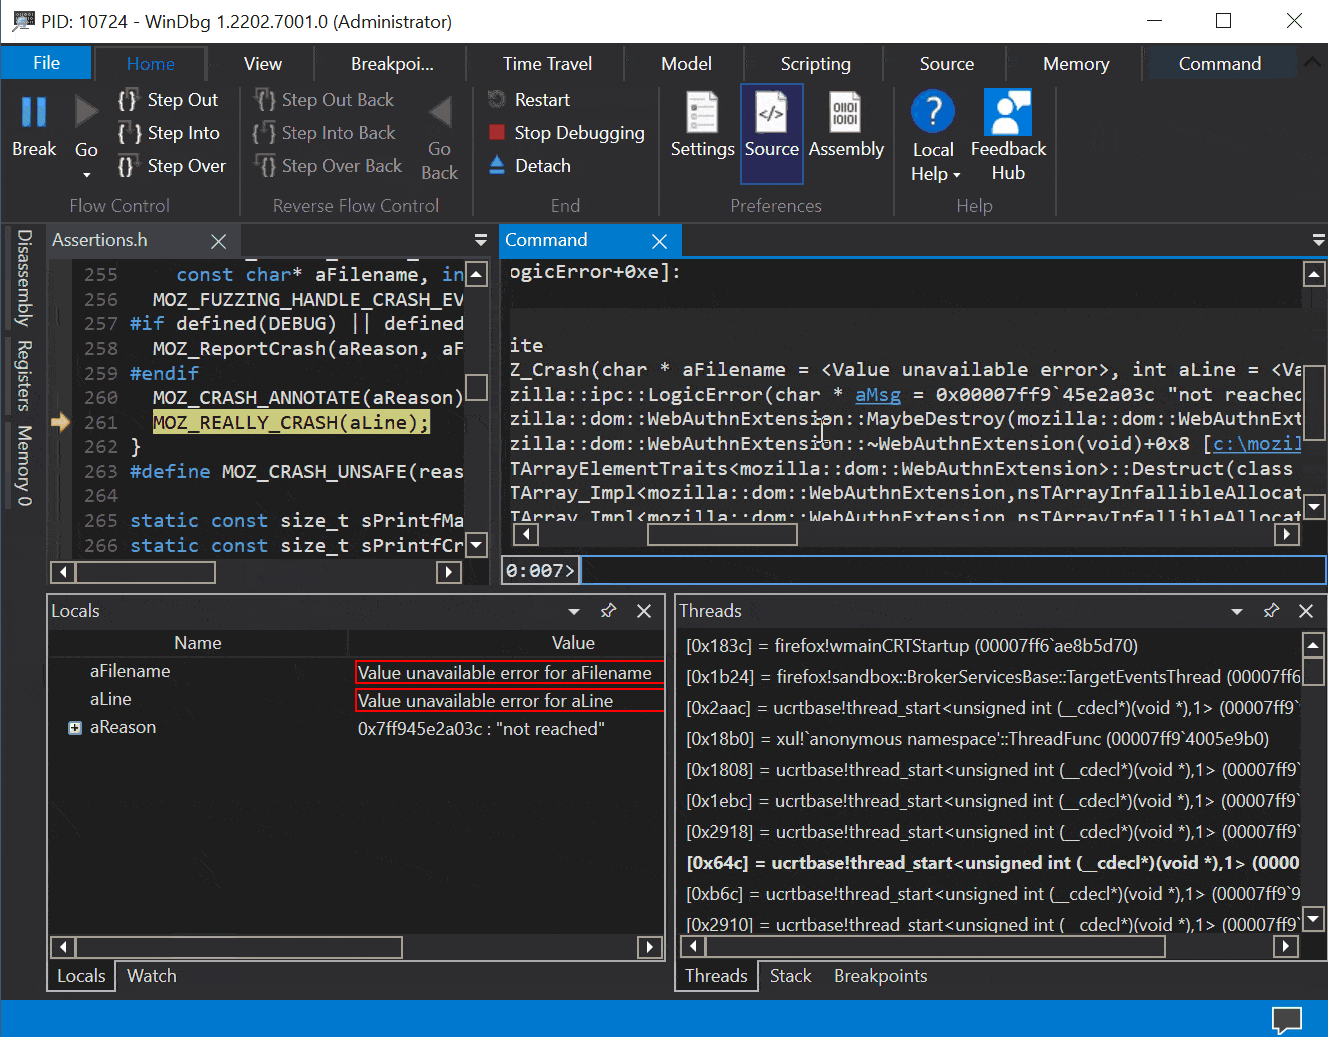
 0vercl0k/cve-2022-28281
PoC for CVE-2022-28281 a Mozilla Firefox Out of bounds write.
 moond4rk/hackbrowserdata
Extract and decrypt browser data, supporting multiple data types, runnable on various operating systems (macOS, Windows, Linux).
 ironfox-oss/ironfox
Hardened Android web browser forked from Mull/Firefox with privacy-focused patches, anti-fingerprinting, telemetry removal, and secure defaults for…
 bitwarden/clients
Bitwarden client apps (web, browser extension, desktop, and cli).
 saelo/foxpwn
Exploit code for CVE-2016-9066
 forrest-orr/exploits
A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…
 forrest-orr/doublestar
A personalized/enhanced re-creation of the Darkhotel "Double Star" APT exploit chain with a focus on Windows 8.1 and mixed with some of my own…
 mistymntncop/cve-2022-1802
Proof-of-concept exploit code for Firefox CVEs (2022-1802, 1529, 2200) targeting version 100.0.1 on Windows, demonstrating browser vulnerability…
 vigneshsrao/cve-2019-11707
Exploit code for CVE-2019-11707 on Firefox 66.0.3 running on Ubuntu
 federicochieregato/darkfox
Remote access trojan created using WinRar with firefox installer and python Reverse Shell embedded.
 mistymntncop/cve-2022-26485
Proof-of-concept exploit for CVE-2022-26485 targeting Firefox 78.0 on Windows, demonstrating a remote code execution vulnerability in the browser's…
 zombie-kaiser/cve-2024-4367-poc-fixed
PDF.js是由Mozilla维护的基于JavaScript的PDF查看器。此漏洞允许攻击者在打开恶意 PDF 文件后立即执行任意 JavaScript 代码。这会影响所有 Firefox 用户 (<126),因为 Firefox 使用 PDF.js 来显示 PDF 文件,但也严重影响了许多基于…
 aleksejspopovs/cve-2020-16012
PoC for CVE-2020-16012, a timing side channel in drawImage in Firefox & Chrome
 dangokyo/cve-2016-9079
Proof-of-concept exploit for CVE-2016-9079 targeting Firefox on Ubuntu x64, demonstrating a use-after-free vulnerability in the SVG animation…
 defineid/revenant
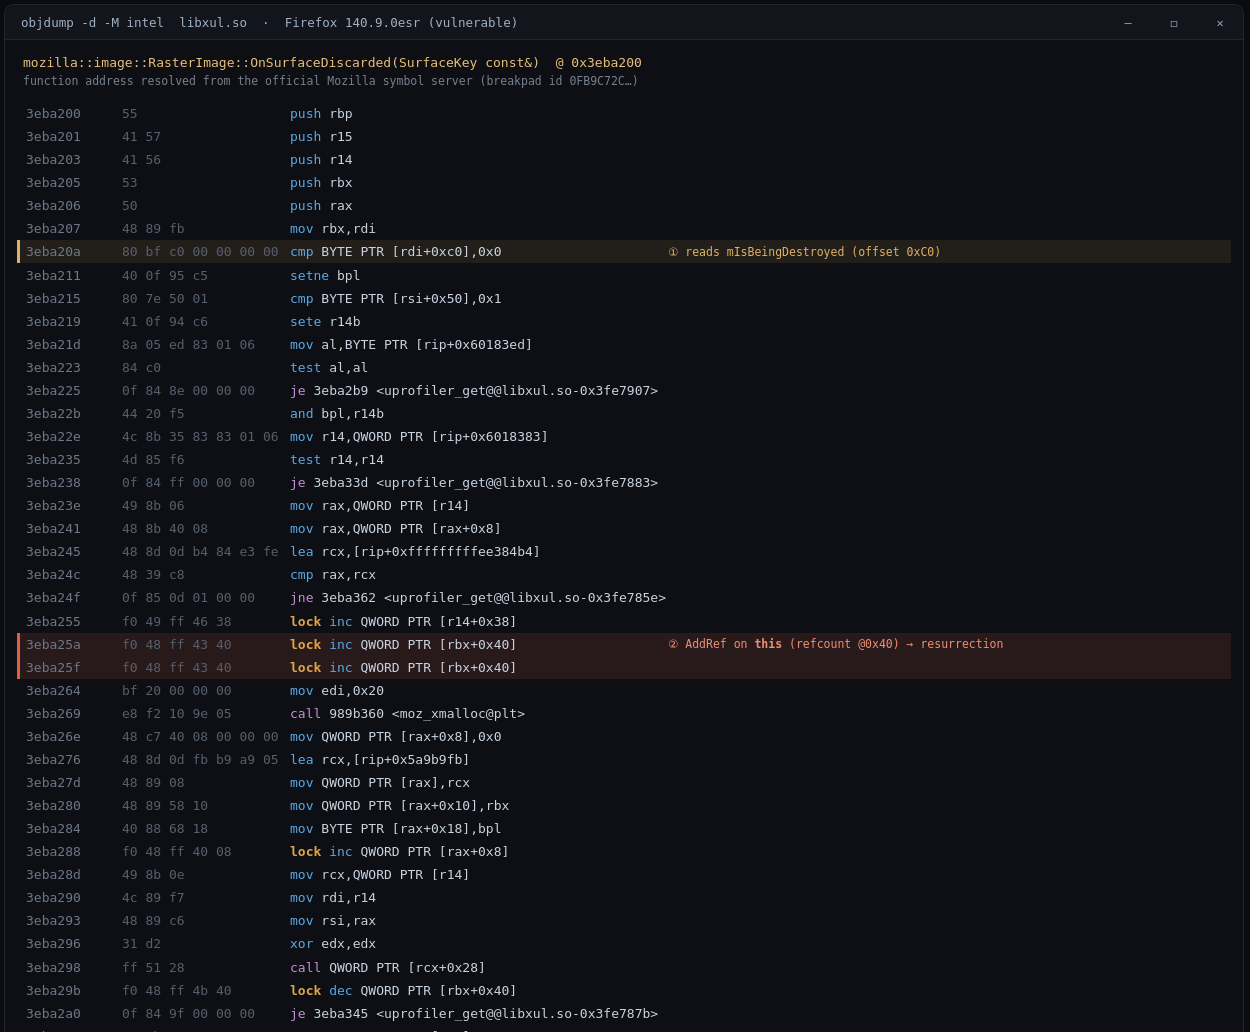
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
 defineid/trespasser
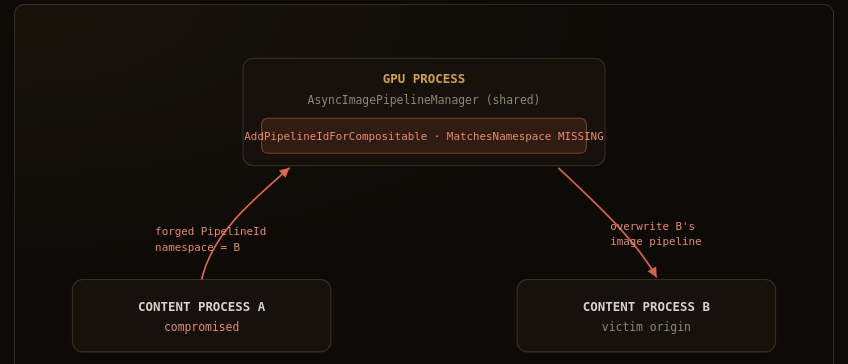
CVE-2026-74970, Fission site isolation bypass in Firefox WebRender
 sneakynachos/cve-2026-12295-uxxs-in-my-wasm
Firefox content->parent srcdoc forge (N-day, bug 2040160): forged PDocumentChannel with SrcdocData on a non-about:srcdoc URI -> attacker HTML served…