system_bt_A10-r33_CVE-2021-0474

Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…

Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…

Proof-of-concept for CVE-2024-53027, a Wi-Fi beacon Country IE denial-of-service vulnerability affecting Qualcomm WLAN chipsets. Includes educational…

Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.

Software tools for Nordic Semiconductor nRF24-based devices like wireless keyboards, mice, and presenters

PoC tool to demonstrate vulnerabilities in wireless input devices

A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…

Records calls from a Trunked Radio System (P25 & SmartNet)

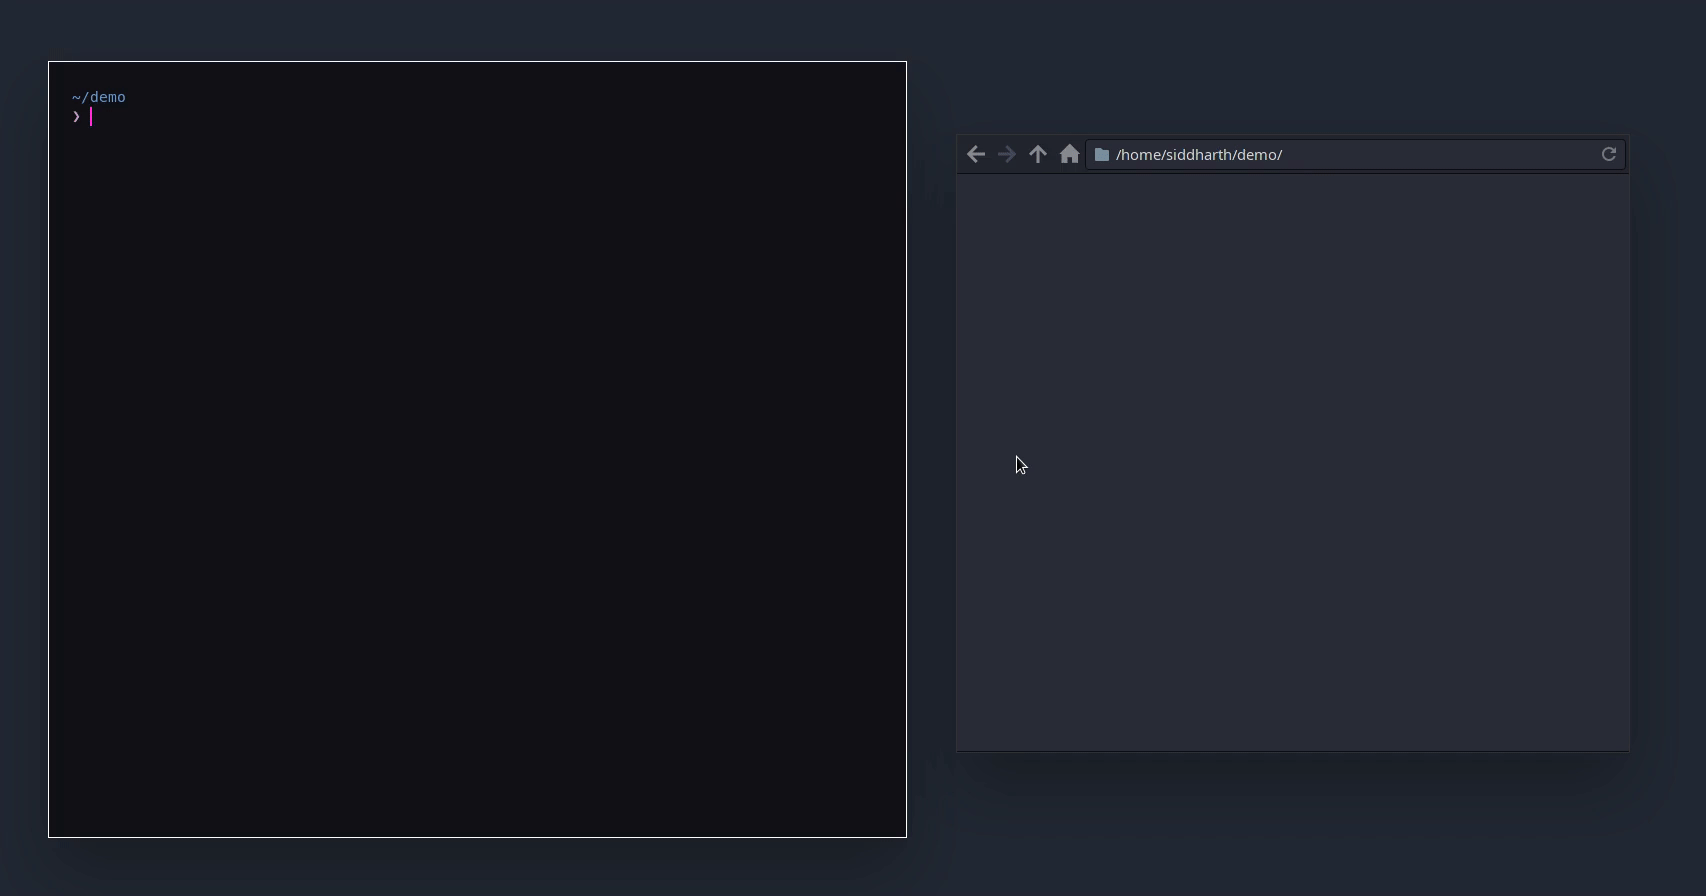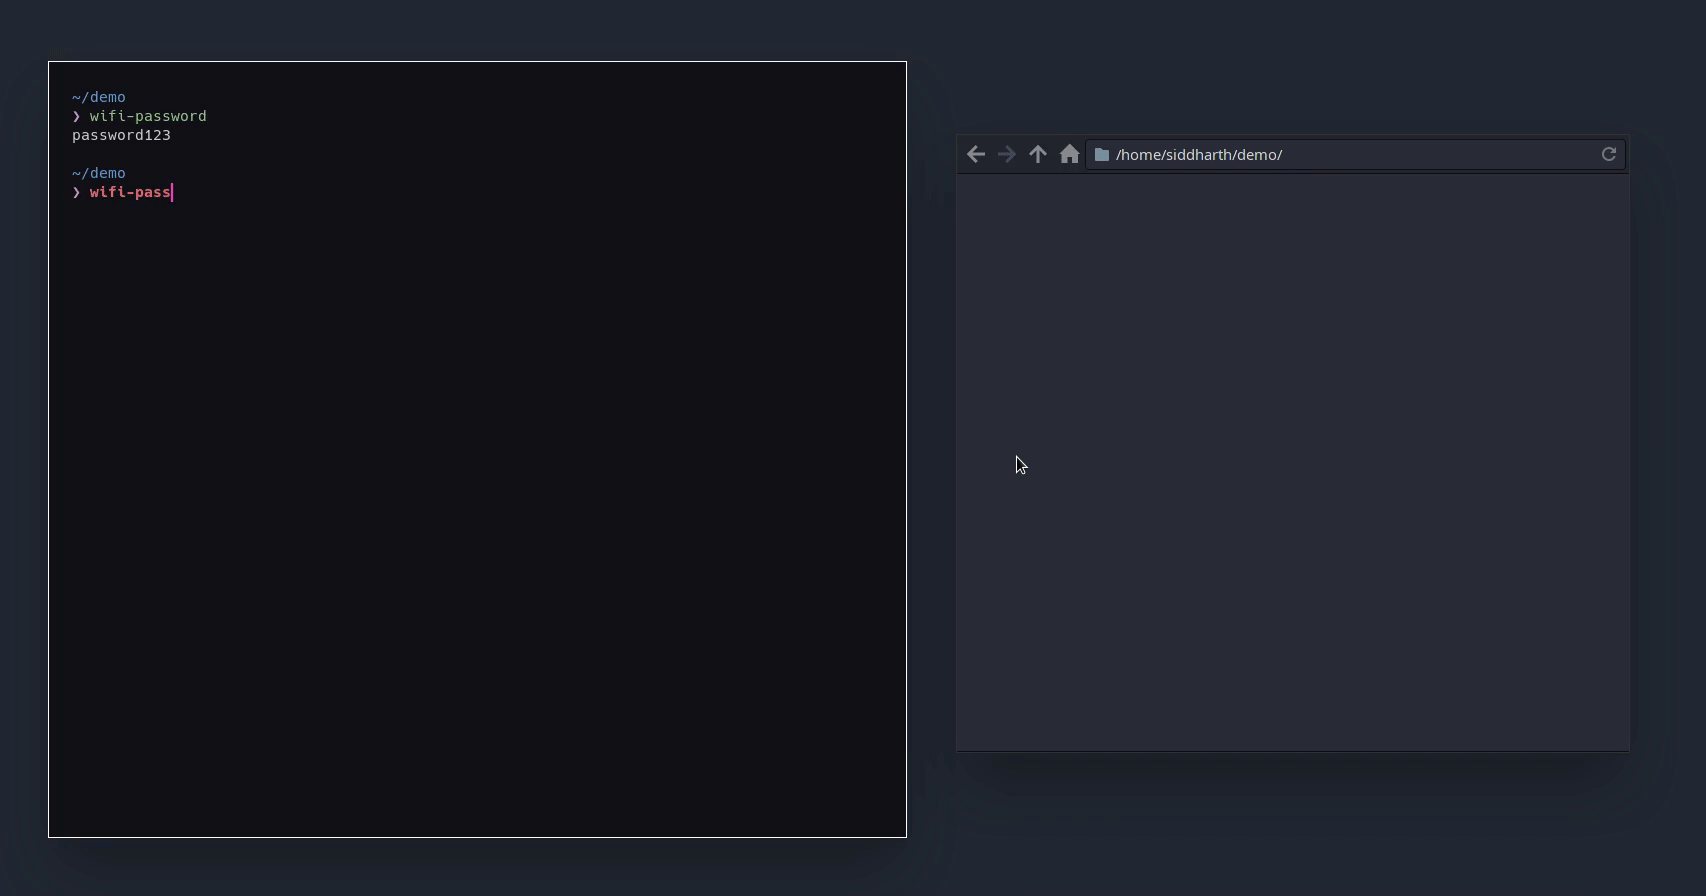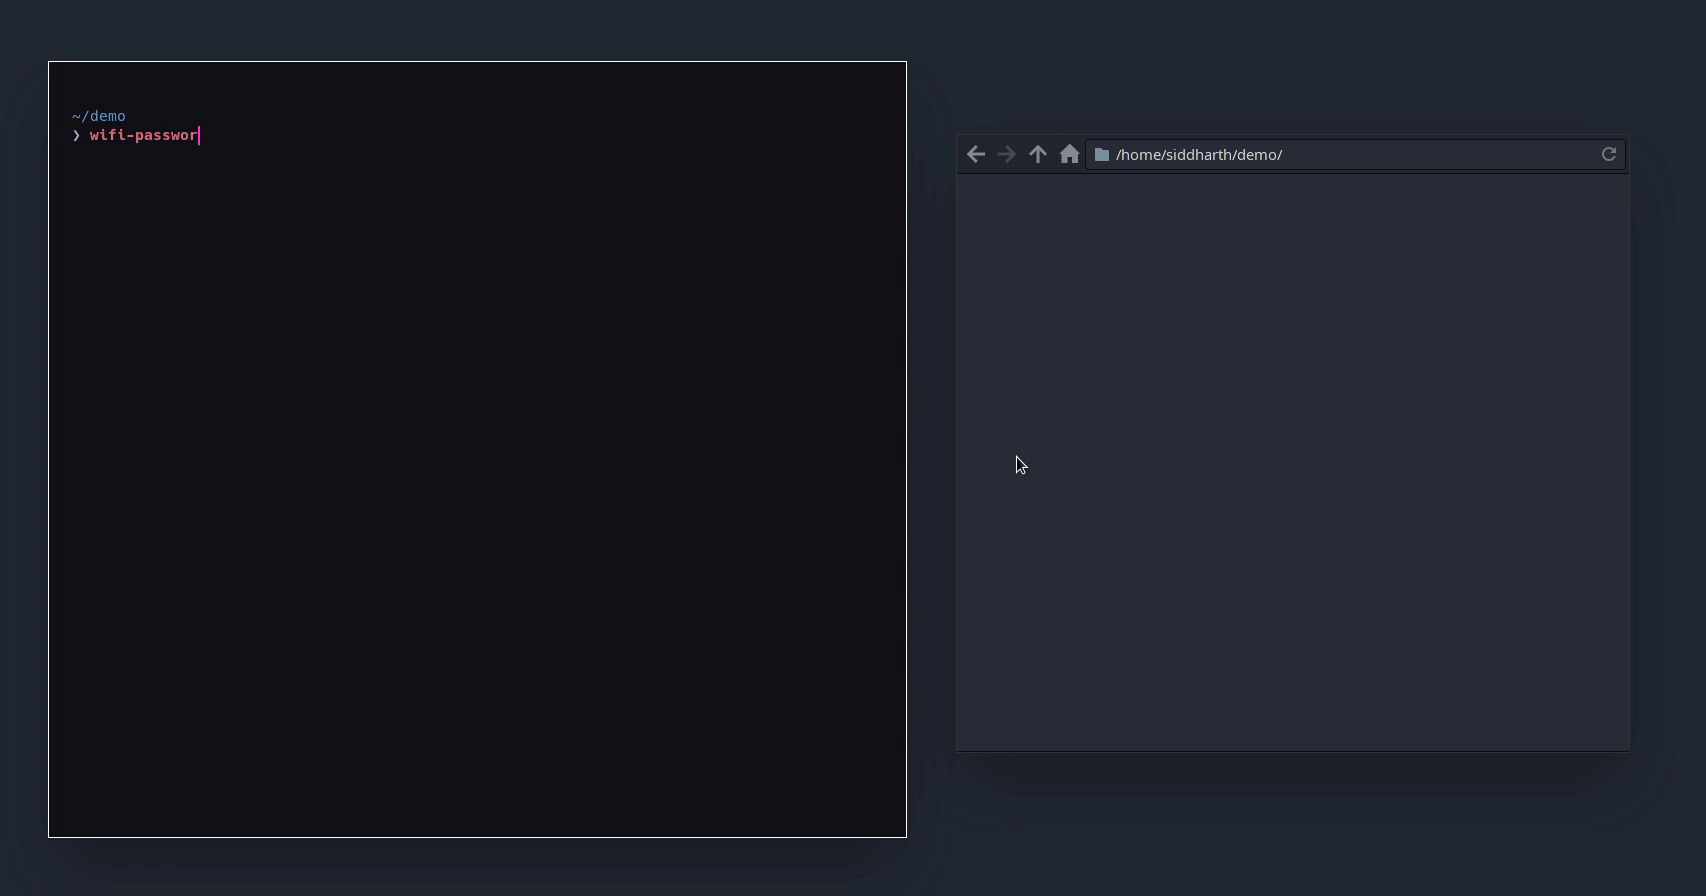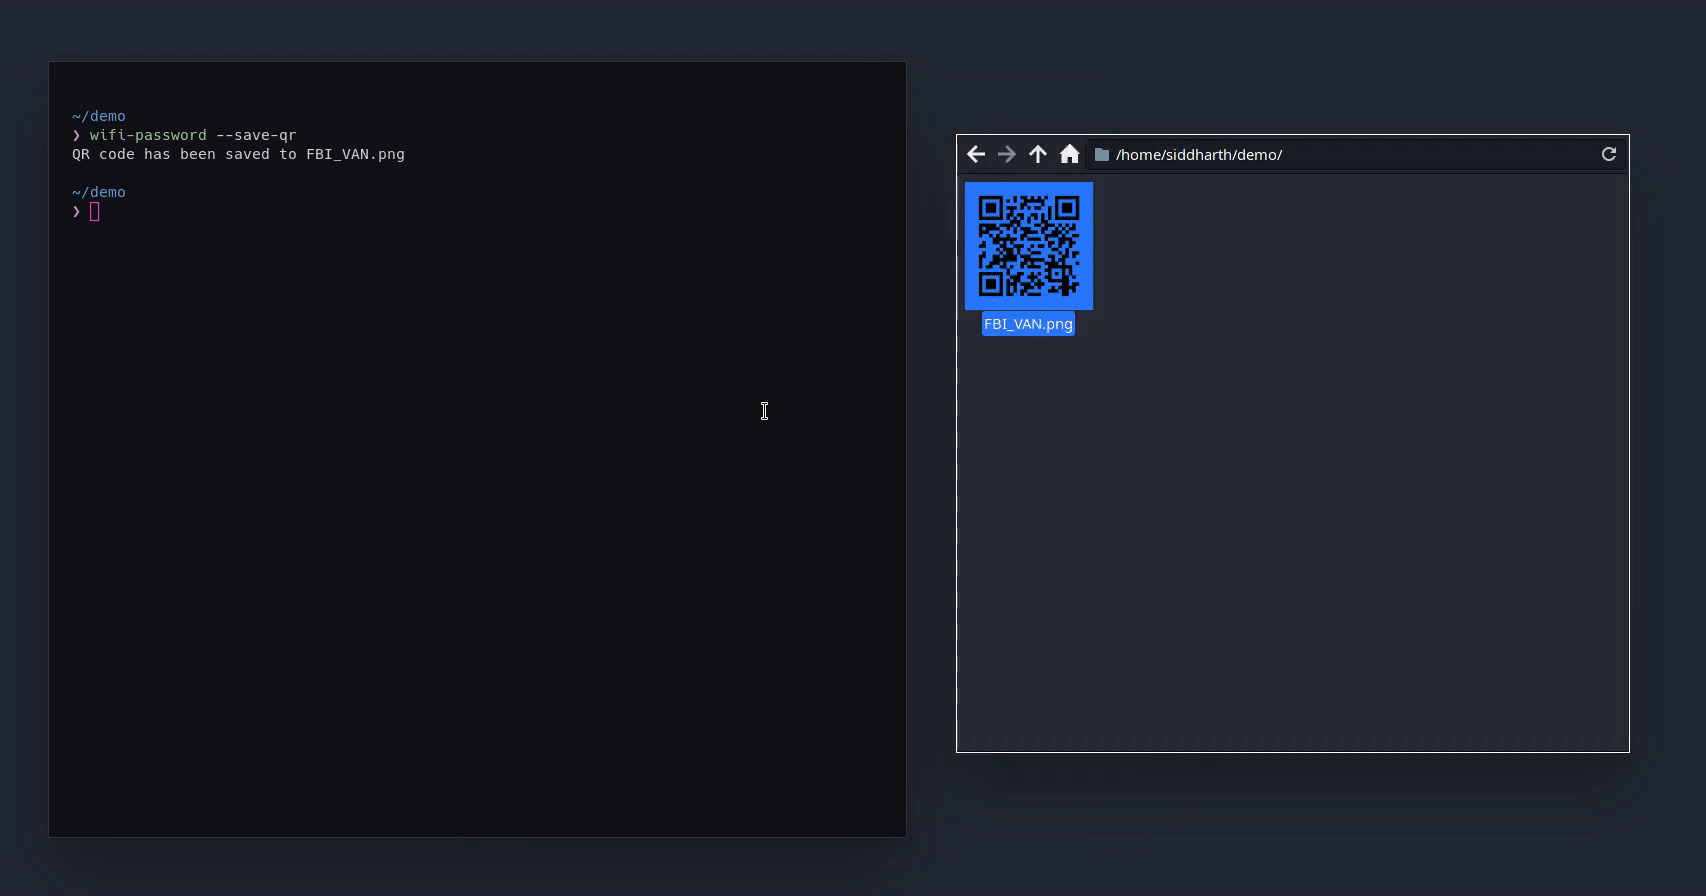
Quickly fetch your WiFi password and if needed, generate a QR code of your WiFi to allow phones to easily connect

A tool set for sniffing devices and launching attacks with Crazyradio

Nortel Wireless LAN Access Point 2200 Series - Denial of Service

Cisco IOS XE Software for Catalyst 9800 Series Wireless Controllers IPv6 Denial of Service Vulnerability

Exploit for CVE-2020-0022, an Android Bluetooth RCE vulnerability. Provides proof-of-concept code for testing and understanding the memory corruption…

Android Bluetooth package with a patch for CVE-2022-20126, addressing a security vulnerability in AOSP 10.

WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…

Android Bluetooth stack (Fluoride) with a specific patch for CVE-2022-20229, providing a vulnerable version for security research and exploit…

Android Bluetooth stack (Fluoride) with a proof-of-concept exploit for CVE-2020-0471, enabling vulnerability analysis and exploitation testing on…

AOSP Bluetooth stack with a patch for CVE-2021-0589, providing a vulnerable version for security research and exploit development.

"A single malicious packet can own your device." — Android Security Team, Nov 2025