

Struts2-045-Exp
 flyteas/struts2-045-exp
Struts2 S2-045(CVE-2017-5638)Exp with GUI
educationexploitationpayload-generation+3
flyteas/struts2-045-expStruts2 S2-045(CVE-2017-5638)Exp with GUI
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
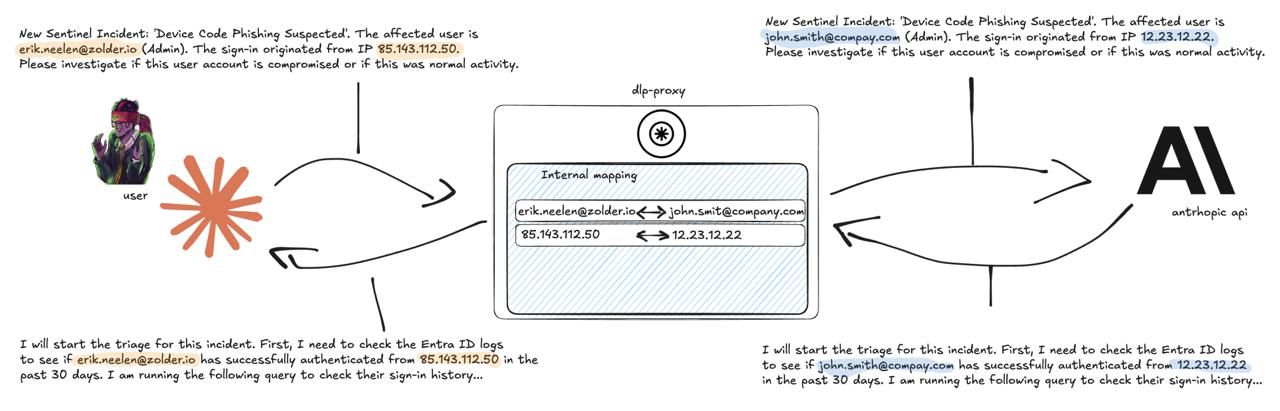 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…

 malwaretech/phasehack
Phase C&C Blind SQL Injection
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 ynsmroztas/wpsniper
CVE-2026-87902 detector. WordPress get_page_template LFI class. Detect-only. Authorized lab.
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 al1ex/cve-2021-4034
Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 george0papasotiriou/cve-2026-22013-hardware-wallet-usb-descriptor-buffer-overflow
Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 digamma-ai/cve-2020-8835-verification
Coq-based formal verification of a Linux kernel eBPF verifier vulnerability (CVE-2020-8835) with reproducible build environment and proof artifacts.
 zzzz0317/log4j2-vulnerable-spring-app
CVE-2021-44228